
本教程适用于以下操作系统版本
- Ubuntu 22.04 (Jammy Jellyfish)
- Ubuntu 20.04 (Focal Fossa)
本页内容
- 先决条件
- 安装 Apache、MariaDB 和 PHP
- 为 FileRun 创建数据库
- 下载 FileRun
- 为 FileRun 创建 Apache 虚拟主机
- 访问 FileRun Web UI
- 使用 Let's Encrypt SSL 保护 FileRun
- 结论
FileRun 是一款开源、基于 Web 的文件共享应用程序,适用于 Linux 操作系统。它与 Google Drive、iCloud 和 DropBox 非常相似,允许用户通过互联网共享和同步文件。它可以通过移动应用、WebDAV 和 Web 浏览器进行访问。它允许您在云端托管自己的文件共享方案,并通过安全的云存储随时随地访问您的所有文件。
本文将演示如何在 Ubuntu 22.04 上通过 Apache 和 Let's Encrypt SSL 安装 FileRun。
先决条件
- 一台运行 Ubuntu 22.04 的服务器。
- 一个指向您服务器 IP 的有效域名。
- 服务器上已配置 root 密码。
安装 Apache、MariaDB 和 PHP
FileRun 使用 PHP 编写,并使用 MariaDB 作为数据库后端。因此,您需要在服务器上安装 Apache、MariaDB、PHP 及其他软件包。首先,使用以下命令安装 Apache 和 MariaDB 软件包:
apt-get install apache2 mariadb-server mariadb-client安装完这两个软件包后,您需要在服务器上安装 php7.2-php7.4 版本的 PHP。然而,Ubuntu 22.04 默认仓库中自带的是 PHP 8.1 版本。因此,您需要在服务器上添加 PHP Ondrej 仓库。
首先,使用以下命令安装所有必需的依赖项:
apt install software-properties-common ca-certificates lsb-release apt-transport-https -y接下来,使用以下命令添加 PHP 仓库:
add-apt-repository ppa:ondrej/php接下来,使用以下命令更新仓库缓存并安装 PHP 及其他必需的扩展:
apt update
apt install php7.4 libapache2-mod-php7.4 imagemagick ffmpeg php7.4-imagick php7.4-mysql php7.4-fpm php7.4-common php7.4-gd php7.4-json php7.4-curl php7.4-zip php7.4-xml php7.4-mbstring php7.4-bz2 php7.4-intl unzip -y
所有软件包安装完成后,您还需要在系统上安装 IonCube loader。
首先,使用以下命令下载 IonCube loader:
wget https://downloads.ioncube.com/loader_downloads/ioncube_loaders_lin_x86-64.tar.gz接下来,使用以下命令解压下载的文件:
tar -xzf ioncube_loaders_lin_x86-64.tar.gz -C /usr/lib/php接下来,创建一个 ioncube 配置文件并定义 IonCube 源的路径:
nano /etc/php/7.4/apache2/conf.d/00-ioncube.ini添加以下行:
zend_extension = /usr/lib/php/ioncube/ioncube_loader_lin_7.4.so
保存并关闭文件,然后为 FileRun 创建一个 PHP 配置文件:
nano /etc/php/7.4/apache2/conf.d/filerun.ini添加以下设置:
expose_php = Off
error_reporting = E_ALL & ~E_NOTICE
display_errors = Off
display_startup_errors = Off
log_errors = On
ignore_repeated_errors = Off
allow_url_fopen = On
allow_url_include = Off
variables_order = "GPCS"
allow_webdav_methods = On
memory_limit = 128M
max_execution_time = 300
output_buffering = Off
output_handler = ""
zlib.output_compression = Off
zlib.output_handler = ""
safe_mode = Off
register_globals = Off
magic_quotes_gpc = Off
upload_max_filesize = 20M
post_max_size = 20M
enable_dl = Off
disable_functions = ""
disable_classes = ""
session.save_handler = files
session.use_cookies = 1
session.use_only_cookies = 1
session.auto_start = 0
session.cookie_lifetime = 0
session.cookie_httponly = 1
date.timezone = "UTC"
保存并关闭文件,然后重启 Apache 服务以使更改生效:
systemctl reload apache2为 FileRun 创建数据库
首先,使用以下命令加固 MariaDB 安装并设置 root 密码:
mysql_secure_installation按如下所示回答所有问题:
Enter current password for root (enter for none):  PRESS ENTER
Set root password? [Y/n] Y
New password:
Re-enter new password:
Remove anonymous users? [Y/n] Y
Disallow root login remotely? [Y/n] Y
Remove test database and access to it? [Y/n]  Y
Reload privilege tables now? [Y/n] Y
接下来,使用以下命令登录到 MariaDB shell:
mysql -u root -p登录后,使用以下命令创建一个数据库和用户:
MariaDB [(none)]> CREATE DATABASE filerun;
MariaDB [(none)]> CREATE USER 'filerun'@'localhost' IDENTIFIED BY 'password';
接下来,使用以下命令向 FileRun 数据库授予所有权限:
MariaDB [(none)]> GRANT ALL PRIVILEGES ON filerun.* TO 'filerun'@'localhost';接下来,使用以下命令刷新权限并退出 MariaDB:
MariaDB [(none)]> FLUSH PRIVILEGES;
MariaDB [(none)]> EXIT;
完成后,您可以继续下一步。
下载 FileRun
首先,使用以下命令从其官方网站下载最新版本的 FileRun:
wget -O FileRun.zip https://filerun.com/download-latestFileRun 下载完成后,使用以下命令解压下载的文件:
unzip FileRun.zip -d /var/www/html/filerun/接下来,使用以下命令设置正确的权限和所有权:
chown -R www-data:www-data /var/www/html/filerun
chmod -R 755 /var/www/html/filerun
完成后,您可以继续下一步。
为 FileRun 创建 Apache 虚拟主机
接下来,您需要为 FileRun 创建一个 Apache 虚拟主机配置文件。您可以使用以下命令创建它:
nano /etc/apache2/sites-available/filerun.conf添加以下行:
<VirtualHost *:80>
        ServerName filerun.example.com

        DocumentRoot /var/www/html/filerun

        <Directory "/var/www/html/filerun">
                Options Indexes FollowSymLinks
                AllowOverride All
                Require all granted
        </Directory>

        ErrorLog ${APACHE_LOG_DIR}/filerun.error.log
        CustomLog ${APACHE_LOG_DIR}/filerun.access.log combined
</VirtualHost>
保存并关闭文件,然后使用以下命令激活 Apache 虚拟主机并启用 Apache rewrite 模块:
a2ensite filerun.conf
a2enmod rewrite
接下来,重启 Apache 服务以使更改生效:
systemctl restart apache2您也可以使用以下命令检查 Apache 状态:
systemctl status apache2您应该会看到以下输出:
? apache2.service - The Apache HTTP Server
     Loaded: loaded (/lib/systemd/system/apache2.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2022-08-06 09:26:00 UTC; 7s ago
       Docs: https://httpd.apache.org/docs/2.4/
    Process: 21189 ExecStart=/usr/sbin/apachectl start (code=exited, status=0/SUCCESS)
   Main PID: 21193 (apache2)
      Tasks: 6 (limit: 2242)
     Memory: 14.6M
        CPU: 112ms
     CGroup: /system.slice/apache2.service
             ??21193 /usr/sbin/apache2 -k start
             ??21194 /usr/sbin/apache2 -k start
             ??21195 /usr/sbin/apache2 -k start
             ??21196 /usr/sbin/apache2 -k start
             ??21197 /usr/sbin/apache2 -k start
             ??21198 /usr/sbin/apache2 -k start

Aug 06 09:26:00 ubuntu2204 systemd[1]: Starting The Apache HTTP Server...
完成后,您可以继续下一步。
访问 FileRun Web UI
现在,打开您的 Web 浏览器,使用 URL http://filerun.example.com 访问 FileRun Web UI。您将被重定向到以下页面:
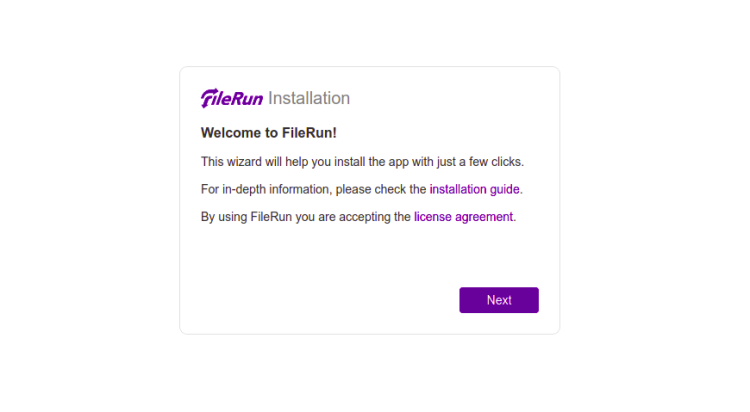
点击 Next 按钮。您应该会看到服务器要求检查页面:
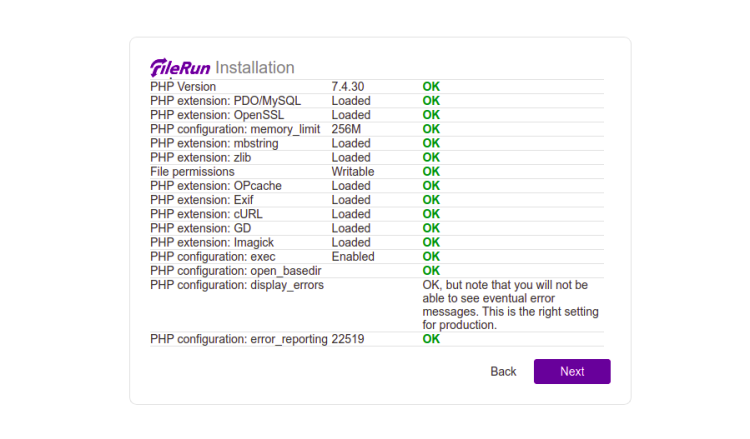
点击 Next 按钮。您应该会看到数据库配置页面:
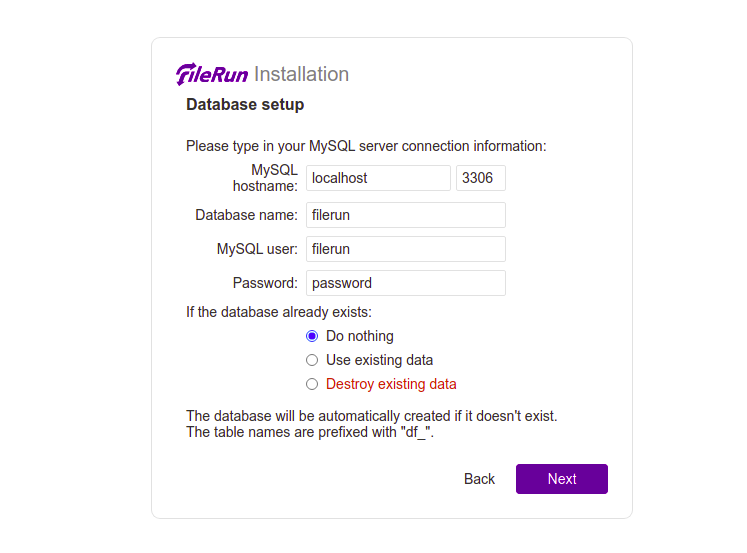
点击 Next 按钮。安装完成后,您应该会看到以下页面:
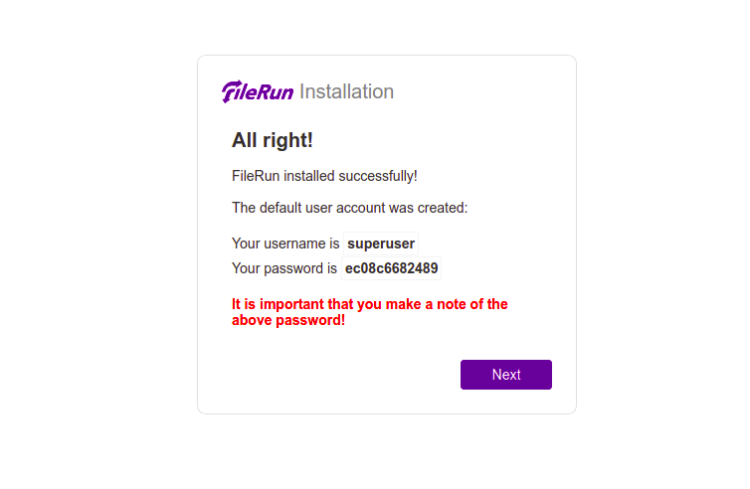
点击 Next 按钮。您应该会看到 FileRun 登录页面:
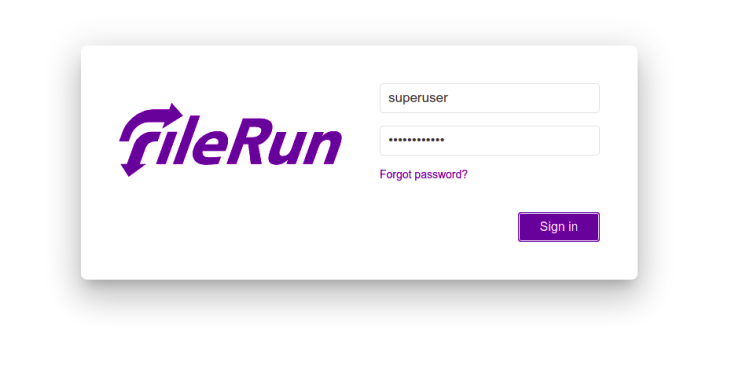
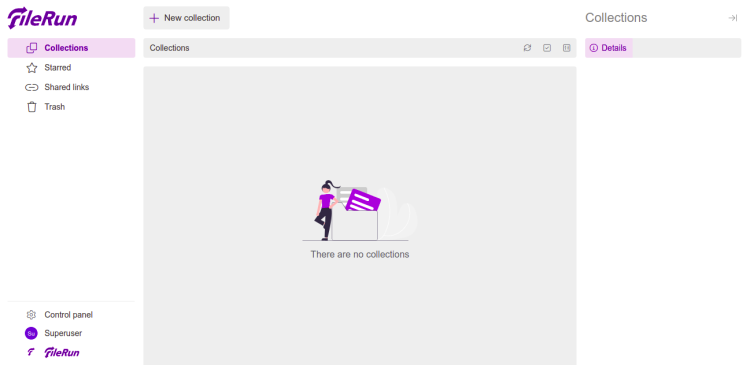
输入您的管理员用户名和密码,然后点击 Sign in 按钮。您应该会在以下页面看到 FileRun 仪表板:
使用 Let's Encrypt SSL 保护 FileRun
还建议使用 Let's Encrypt SSL 保护您的网站。首先,您需要在服务器上安装 Certbot 客户端。您可以使用以下命令进行安装:
apt-get install python3-certbot-apache -yCertbot 安装完成后,运行以下命令以 Let's Encrypt SSL 保护您的网站:
certbot --apache -d filerun.example.com系统将要求您提供电子邮件并接受服务条款,如下所示:
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator standalone, Installer None
Enter email address (used for urgent renewal and security notices) (Enter 'c' to
cancel):
[email protected]


- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at
https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf. You must
agree in order to register with the ACME server at
https://acme-v02.api.letsencrypt.org/directory
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(A)gree/(C)ancel: A

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing to share your email address with the Electronic Frontier
Foundation, a founding partner of the Let's Encrypt project and the non-profit
organization that develops Certbot? We'd like to send you email about our work
encrypting the web, EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: Y
Plugins selected: Authenticator apache, Installer apache
Obtaining a new certificate
Performing the following challenges:
http-01 challenge for filerun.example.com
Enabled Apache rewrite module
Waiting for verification...
Cleaning up challenges
Created an SSL vhost at /etc/apache2/sites-available/filerun-le-ssl.conf
Enabled Apache socache_shmcb module
Enabled Apache ssl module
Deploying Certificate to VirtualHost /etc/apache2/sites-available/filerun-le-ssl.conf
Enabling available site: /etc/apache2/sites-available/filerun-le-ssl.conf
Next, select whether or not to redirect HTTP traffic to HTTPS as shown below:
请选择是否将 HTTP 流量重定向到 HTTPS,从而移除 HTTP 访问。
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
1: No redirect - Make no further changes to the webserver configuration.
2: Redirect - Make all requests redirect to secure HTTPS access. Choose this for
new sites, or if you're confident your site works on HTTPS. You can undo this
change by editing your web server's configuration.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Select the appropriate number [1-2] then [enter] (press 'c' to cancel): 2
输入 2 并按 Enter 为您的网站安装 Let's Encrypt SSL:
Enabled Apache rewrite module
Redirecting vhost in /etc/apache2/sites-enabled/filerun.conf to ssl vhost in /etc/apache2/sites-available/filerun-le-ssl.conf

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations! You have successfully enabled https://filerun.example.com

You should test your configuration at:
https://www.ssllabs.com/ssltest/analyze.html?d=filerun.example.com
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/filerun.example.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/filerun.example.com/privkey.pem
   Your cert will expire on 2022-4-29. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot again
   with the "certonly" option. To non-interactively renew *all* of
   your certificates, run "certbot renew"
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le
结论
恭喜!您已成功在 Ubuntu 22.04 上通过 Apache 和 Let's Encrypt SSL 安装了 FileRun。现在您可以在云端托管自己的 FileRun 服务器,并开始与您的朋友和家人共享和同步您的文件、音乐和照片。