
本页内容
- 准备工作
- 安装 Grafana
- 配置 Grafana
- 配置 Nginx 作为反向代理
- 安装 Prometheus 与 Node Exporter
- 配置 Prometheus 与 Node Exporter 为 Prometheus 启用 basic_auth 与 HTTPS/SSL 为目标机器设置 scrape_config
- 将 Prometheus 添加为 Grafana 的数据源
- 配置仪表盘监控
- 总结
- 为 Prometheus 启用 basic_auth 与 HTTPS/SSL
- 为目标机器设置 scrape_config
Grafana 是由 Grafana Labs 开发的开源、多平台数据可视化平台。Grafana 提供了一个交互式的数据可视化 Web 应用程序,包含图表、图形和告警功能。借助 Grafana,你可以查询、可视化、设置告警,并探索 TSDB 的指标、日志和链路追踪。它是一款强大的工具,能够将时序数据库(TSDB)的数据转换为富有洞察力的图形和可视化界面。
在 Grafana 中,你可以通过“数据源(Data Source)”添加时序数据库数据。Grafana 支持多种数据源,例如 Prometheus、InfluxDB、PostgreSQL、Loki、Jaeger、Graphite、Google Cloud Monitoring、AWS CloudWatch、Azure Monitor 等等。
在本教程中,我将安装 Grafana 开源分析与可视化 Web 应用程序,并使用 Nginx 作为反向代理。接着,我将安装并配置 Prometheus 开源系统监控以及 Node Exporter 来收集系统指标。最后,你将为 Grafana 添加 Prometheus 作为数据源,并搭建一个用于系统监控的仪表盘。
在本指南中,你将在 Rocky Linux 9 服务器上安装上述所有组件。
准备工作
首先,你需要满足以下要求才能完成本指南:
- 一台 Rocky Linux 9 服务器——你可以使用多台服务器或单台服务器进行实验。以下是你必须了解的几种安装类型:单台服务器:grafana、prometheus 和 node_exporter 都安装在同一台服务器上。两台服务器:grafana 安装在 server1,prometheus 和 node_exporter 安装在 server3。三台服务器:grafana 安装在 server1,prometheus 安装在 server2,node_exporter 安装在 server3。
- 一个具有 sudo/root 管理员权限的非 root 用户。
安装 Grafana
Grafana 是一款多平台应用程序,可安装在 Windows、Linux 和 macOS 等多种操作系统上。对于 Linux 系统,Grafana 同时提供了面向 Debian 系操作系统(Debian 和 Ubuntu)以及 RHEL 系操作系统(RHEL、CentOS、Fedora、RockyLinux、AlmaLinux)的软件仓库。
在此步骤中,你将配置 Grafana 软件仓库,并在 Rocky Linux 9 服务器上安装 Grafana 9.3。
在配置 Grafana 软件仓库之前,请运行以下命令将默认加密策略后端设置为“SHA1”,并重启服务器使更改生效。
sudo update-crypto-policies --set DEFAULT:SHA1
sudo reboot
重新登录后,使用以下 nano 编辑器命令创建新的仓库文件“/etc/yum.repos.d/grafana.repo”。
sudo nano /etc/yum.repos.d/grafana.repo将以下 Grafana 仓库内容添加到该文件中。
[grafana]
name=grafana
baseurl=https://rpm.grafana.com
repo_gpgcheck=1
enabled=1
gpgcheck=1
gpgkey=https://rpm.grafana.com/gpg.key
sslverify=1
sslcacert=/etc/pki/tls/certs/ca-bundle.crt
保存文件并退出编辑器。
现在运行以下命令来验证系统中的仓库列表。你应该能看到 Grafana 仓库已被添加。
sudo dnf repolist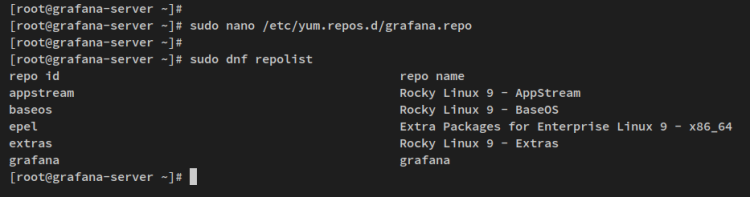
添加 Grafana 仓库后,你现在可以通过下面的 dnf 命令安装 Grafana 软件包。
sudo dnf install grafana当提示出现时,输入 y 确认安装并按 ENTER。
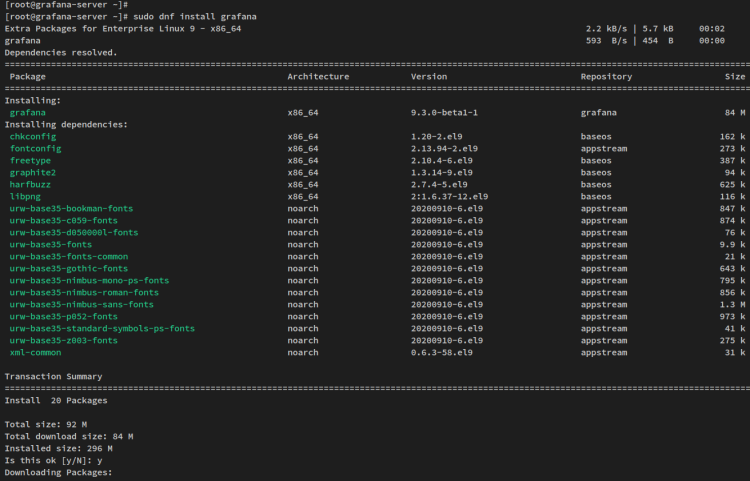
你还会被提示确认 Grafana 仓库的 gpg 密钥。输入 y 并按 ENTER 将该 gpg 密钥添加到系统中。
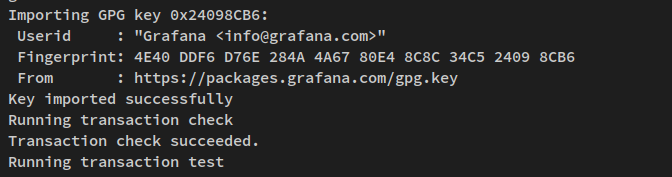
Grafana 安装完成后,运行以下 systemctl 命令重新加载 systemd 配置。
sudo systemctl daemon-reload然后,启动并启用 Grafana 服务“grafana-server”。此时 Grafana 服务应该已被启用并正在运行。
sudo systemctl start grafana-server
sudo systemctl enable grafana-server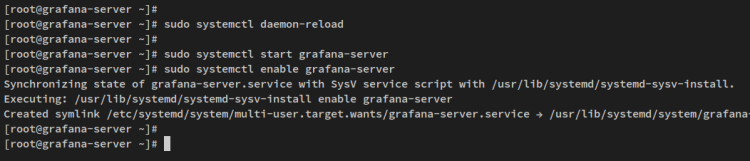
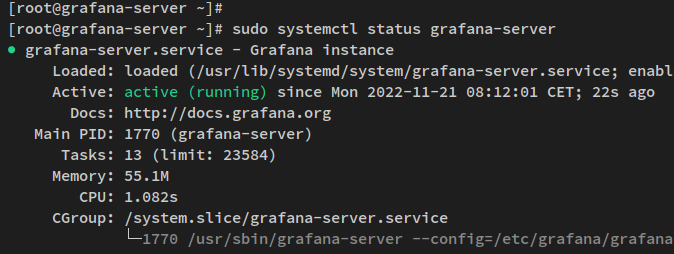
通过以下命令验证“grafana-server”服务,确保服务正在运行。
sudo systemctl status grafana-server以下输出确认 grafana-server 已启用并正在运行。grafana-server 现在应该会在系统启动时自动运行。
配置 Grafana
既然 Grafana 服务器已经安装并运行,你将通过配置文件“/etc/grafana/grafana.ini”来设置 Grafana 的运行方式。在本示例中,你仅在本地主机(localhost)上运行 grafana,并使用本地域名 grafana.howtoforge.local。
使用以下 nano 编辑器命令打开 Grafana 配置文件“/etc/grafana/grafana.ini”。
sudo nano /etc/grafana/grafana.ini取消注释以下部分行,并按如下方式修改默认值。
[server]
# The IP address to bind to, empty will bind to all interfaces
http_addr = localhost
# The http port  to use
http_port = 3000
# The public facing domain name used to access grafana from a browser
domain = grafana.howtoforge.local
通过此配置,你将 Grafana 设置为仅在本地主机运行,使用默认的 TCP 端口 3000。你将使用本地域名 grafana.howtoforge.local 运行 Grafana,该域名由反向代理处理。
完成后保存文件并关闭编辑器。
现在通过 systemctl 命令重启“grafana-server”服务以使新更改生效。
sudo systemctl restart grafana-serverGrafana 已配置完成并正在运行。接下来你将安装并配置 Nginx 作为 Grafana 服务器的反向代理。
配置 Nginx 作为反向代理
在此步骤中,你将安装 Nginx Web 服务器并将其配置为 Grafana 服务器的反向代理。在安装 Nginx 之前,请确保已有一个解析到你的服务器的域名或本地域名,并已生成 SSL 证书。
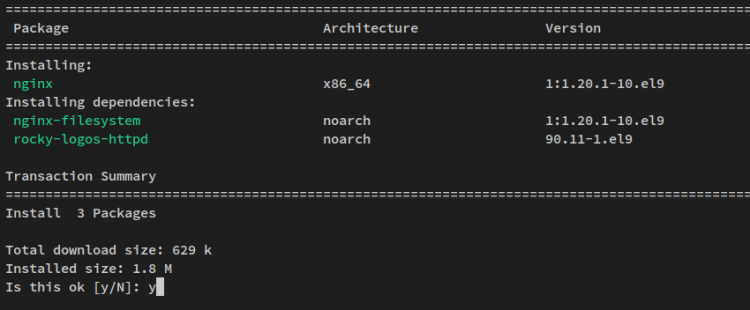
运行以下 dnf 命令将 Nginx Web 服务器安装到系统中。
sudo dnf install nginx当提示确认时输入 y 并按 ENTER 继续。
安装 Nginx 后,使用以下 nano 编辑器命令创建新的 Nginx 服务器块文件“/etc/nginx/conf.d/grafana.conf”。
sudo nano /etc/nginx/conf.d/grafana.conf将以下行添加到文件中,并修改域名和 SSL 证书路径的详细信息。
# this is required to proxy Grafana Live WebSocket connections.
map $http_upgrade $connection_upgrade {
  default upgrade;
  '' close;
}
server {
    listen      80;
    server_name grafana.howtoforge.local;
    rewrite     ^   https://$server_name$request_uri? permanent;
}
server {
  listen      443 ssl http2;
  server_name grafana.howtoforge.local;
  root /usr/share/nginx/html;
  index index.html index.htm;
  ssl_certificate /etc/letsencrypt/live/grafana.howtoforge.local/fullchain.pem;
  ssl_certificate_key /etc/letsencrypt/live/grafana.howtoforge.local/privkey.pem;
  access_log /var/log/nginx/grafana-access.log;
  error_log /var/log/nginx/grafana-error.log;
  location / {
    proxy_set_header Host $http_host;
    proxy_pass http://localhost:3000/;
  }
  # Proxy Grafana Live WebSocket connections.
  location /api/live {
    rewrite  ^/(.*)  /$1 break;
    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection $connection_upgrade;
    proxy_set_header Host $http_host;
    proxy_pass http://localhost:3000/;
  }
}
通过此配置,你将 Nginx 作为运行在 localhost:3000 上的 grafana 服务器的反向代理。你还将通过安全的 SSL/HTTPS 连接保护 grafana。同时,你将为 grafana 的 WebSocket 连接设置反向代理。
完成后保存文件并退出编辑器。
接下来,运行以下命令验证 Nginx 配置,确保配置正确无误。
sudo nginx -t如果配置正确,你应该会看到类似“test successful - syntax ok”的输出信息。
现在运行以下 systemctl 命令启动并启用 Nginx。
sudo systemctl start nginx
sudo systemctl enable nginx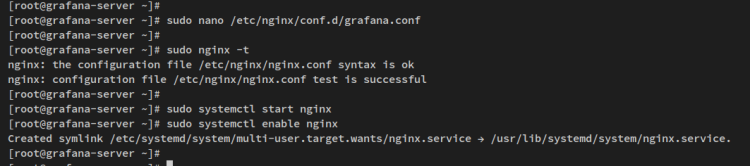
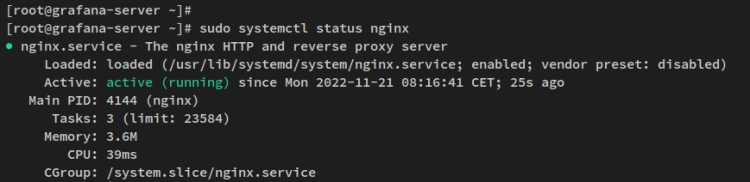
Nginx 服务现在应该正在运行并已被启用。通过以下 systemctl 命令验证 Nginx 服务。
sudo systemctl status nginx以下输出确认 Nginx 服务正在运行且已启用。Nginx 服务应该在系统启动时自动运行。
Nginx 服务已在 HTTP 和 HTTPS 两种协议上正常运行,接下来你将配置 firewalld 以开放这两个服务。
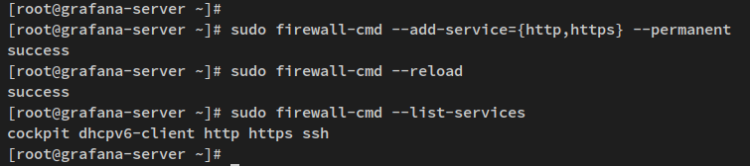
运行以下 firewall-cmd 命令将 HTTP 和 HTTPS 服务添加到 firewalld。
sudo firewall-cmd --add-service={http,https} --permanent之后,重新加载 firewalld 使更改生效,并验证 firewalld 上已启用的服务列表。
sudo firewall-cmd --reload
sudo firewall-cmd --list-services
你应该会收到以下输出——HTTP 和 HTTPS 服务已添加到 firewalld。
配置好 firewalld 后,你将能够访问你的 grafana 以及 Nginx 反向代理安装。
打开 Web 浏览器并访问你的 grafana 安装对应的域名(例如:https://grafana.howtoforge.local/),你应该会看到 grafana 登录页面。
使用默认的用户名/密码“admin”登录。
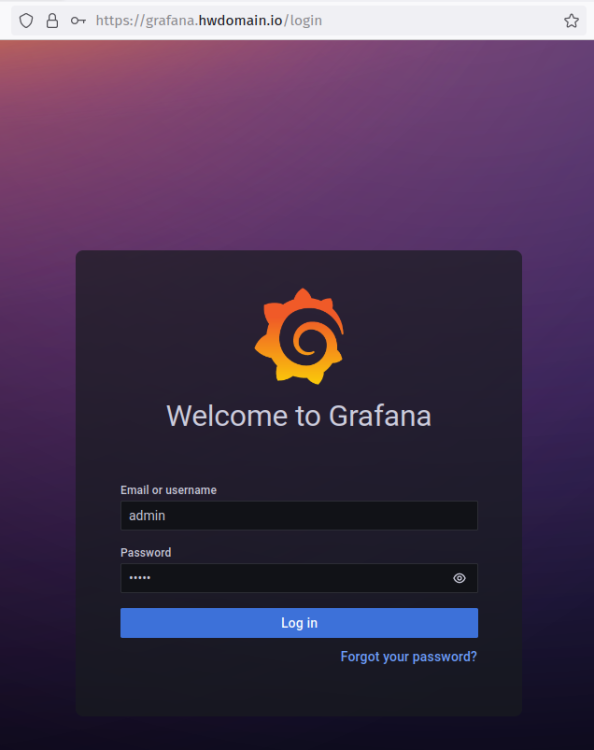
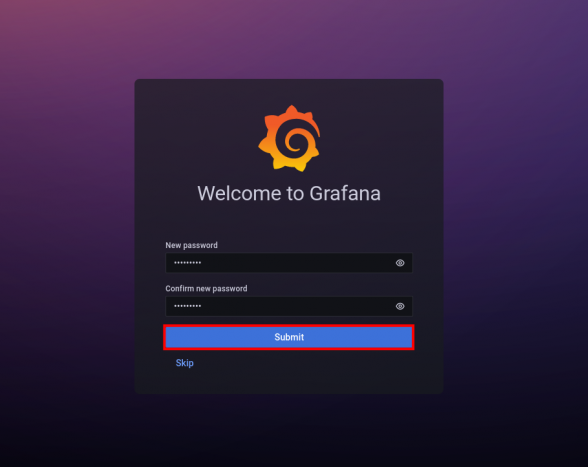
登录后,系统会要求你修改默认密码。输入你的 grafana 安装的新密码,并点击“Submit”确认。
现在你应该会看到如下截图所示的 grafana 仪表盘。
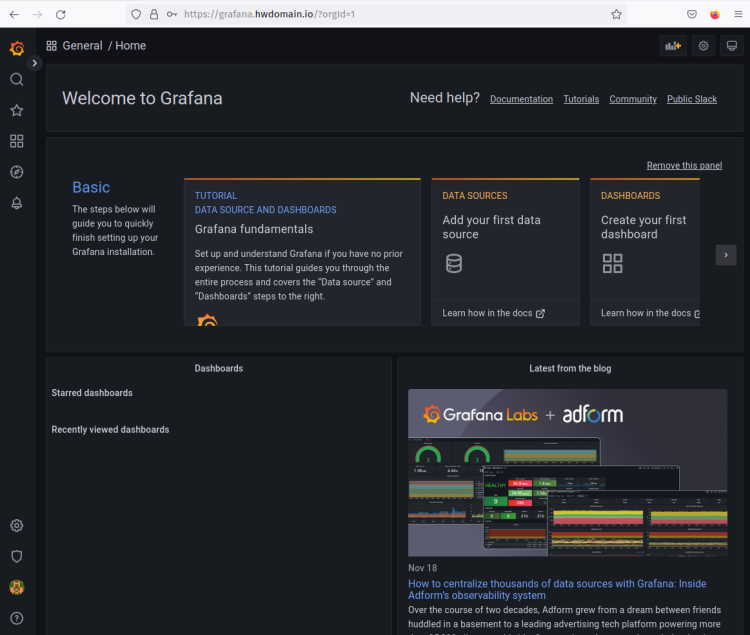
至此,你已完成在 Rocky Linux 9 服务器上的 grafana 安装与配置。你还通过 Nginx 反向代理运行 grafana,并通过 HTTPS 保护了 grafana 安装,同时修改了 grafana 的默认 admin 用户。
接下来,你将安装并配置 Prometheus 和 node_exporter 来收集系统指标,并将 Prometheus 添加为你的 grafana 的数据源。
安装 Prometheus 与 Node Exporter
Prometheus 是一个开源的系统监控与告警工具集。它是收集和查询指标数据的强大工具。Prometheus 通过定期向指标端点发送 HTTP 请求,从应用服务和主机上拉取(scraping)实时指标,然后将其压缩并存储在时序数据库中。
node_exporter 是最受欢迎的 prometheus 抓取器之一,用于拉取操作系统的指标。node_exporter 专为监控主机系统而设计,它暴露了种类繁多的硬件和内核相关指标。
现在你将在 Rocky Linux 9 服务器上安装 prometheus 和 node_exporter。
使用以下 nano 编辑器命令创建新的仓库文件“/etc/yum.repos.d/prometheus.repo”。
sudo nano /etc/yum.repos.d/prometheus.repo将以下行添加到文件中,这是 Packagecloud.io 提供的 prometheus 仓库。
[prometheus]
name=prometheus
baseurl=https://packagecloud.io/prometheus-rpm/release/el/$releasever/$basearch
repo_gpgcheck=1
enabled=1
gpgkey=https://packagecloud.io/prometheus-rpm/release/gpgkey
       https://raw.githubusercontent.com/lest/prometheus-rpm/master/RPM-GPG-KEY-prometheus-rpm
gpgcheck=1
metadata_expire=300
完成后保存并关闭文件。
现在你可以通过以下 dnf 命令验证系统中可用的仓库列表。
sudo dnf repolist在以下输出中确认 prometheus 仓库已添加到你的系统。
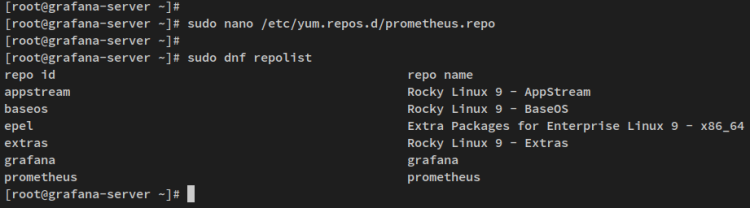
现在通过以下 dnf 命令安装 prometheus 和 node_exporter 软件包。
sudo dnf install prometheus2 node_exporter当提示出现时,输入 y 确认并按 ENTER。随后 prometheus 和 node_exporter 的安装将开始。
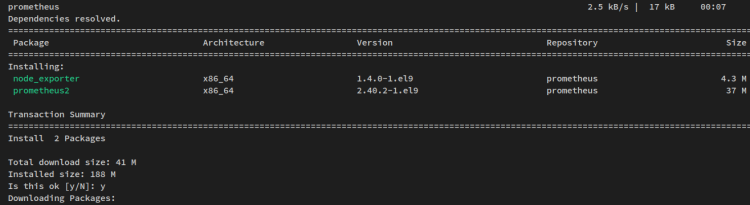
同样,当提示添加 GPG 密钥时,输入 y 确认。
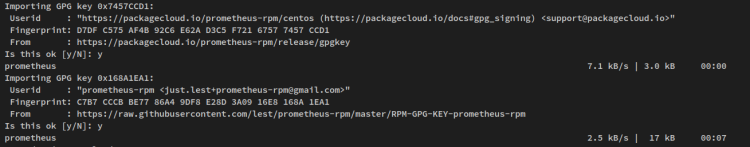
prometheus 和 node_exporter 安装完成后,运行以下 systemctl 命令启动并启用这两个服务,即 prometheus 和 node_exporter 服务。
sudo systemctl start prometheus node_exporter
sudo systemctl enable prometheus node_exporter
现在使用以下命令验证 prometheus 和 node_exporter 服务。
sudo systemctl status prometheus node_exporter在以下输出中确认 prometheus 和 node_exporter 服务正在运行且已启用。这两个服务都会在系统启动时自动运行。
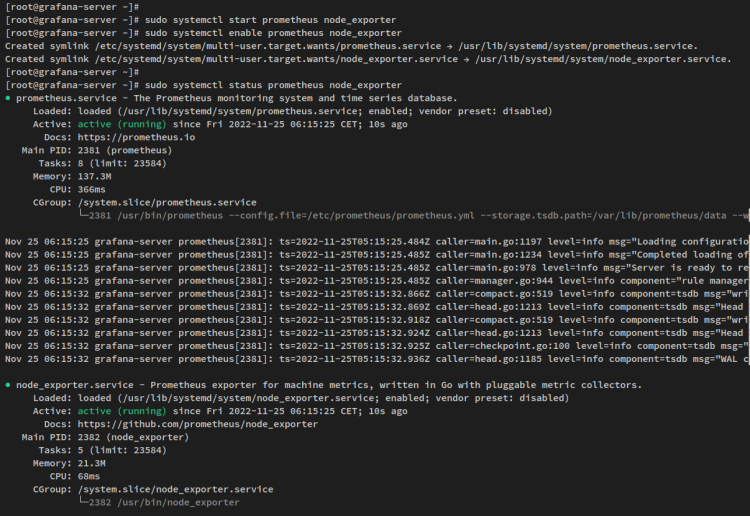
prometheus 默认运行在 9090 端口,而 node-exporter 默认运行在 9100 端口。你现在将把 9090 和 9100 这两个端口添加到 firewalld。
运行以下 firewall-cmd 命令将 prometheus 和 node_exporter 端口添加到 firewalld。然后重新加载 firewalld 使新更改生效。
sudo firewall-cmd --add-port={9090/tcp,9100/tcp} --permanent
sudo firewall-cmd --reload
配置好 firewalld 后,你可以访问 prometheus 和 node_exporter 安装。但接下来你将更进一步,对 prometheus 和 node_exporter 进行配置。
配置 Prometheus 与 Node Exporter
prometheus 和 node_exporter 安装完成后,你将使用以下配置来设置这两个服务:
- 为 prometheus 启用基本身份验证。
- 在 prometheus Web 界面上启用 HTTPS/SSL。
- 为目标机器设置 scrape_config。
为 Prometheus 启用 basic_auth 与 HTTPS/SSL
在默认安装中,prometheus 不带密码身份验证,并运行在 HTTP 协议上。为了加固安装,你将在 prometheus 安装上配置 basic_auth 并启用 HTTPS。
在为 prometheus 配置 basic_auth 之前,运行以下 dnf 命令安装“httpd-tools”软件包。该软件包提供了“htpasswd”命令,可用于生成 bcrypt 密码。
sudo dnf install httpd-tools -y接下来,运行以下命令为你的 prometheus 安装生成密码。在本示例中,你将使用用户“promadmin”作为 prometheus basic_auth 的默认用户。
htpasswd -nB promadmin当提示出现时,输入将用于 prometheus basic_auth 的密码,并重复输入该密码。
在以下输出中,你可以看到生成的 bcrypt 密码。复制用户名和生成的密码。
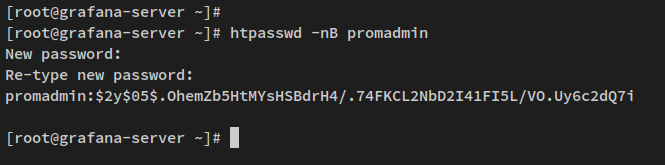
现在使用以下 nano 编辑器命令创建新的 prometheus 配置文件“/etc/prometheus/web.yml”。该配置将在你的 Prometheus 安装上启用 HTTPS/SSL 和 basic_auth。
sudo nano /etc/prometheus/web.yml将以下行添加到文件中,并务必修改 SSL 证书路径以及将用于你 prometheus 的用户名和密码。
# tls certificates
tls_server_config:
  cert_file: fullchain.pem
  key_file: privkey.pem
# basic_auth
basic_auth_users:
  promadmin: $2y$05$.OhemZb5HtMYsHSBdrH4/.74FKCL2NbD2I41FI5L/VO.Uy6c2dQ7i
“tls_server_config”部分允许你启用安全的 HTTPS/SSL 连接,而“basic_auth_users”将启用 prometheus 安装上的基本密码身份验证。
完成后保存文件并退出编辑器。
接下来,使用以下 nano 编辑器命令打开文件“/etc/default/prometheus”。
sudo nano /etc/default/prometheus将以下行添加到“PROMETHEUS_OPTS”部分。
--web.config.file=/etc/prometheus/web.yml
选项“--web.config.file”将指定 prometheus Web 界面的配置文件。在本示例中,配置为“/etc/prometheus/web.yml”。
完成后保存文件并退出编辑器。
为目标机器设置 scrape_config
在启用 prometheus basic_auth 和 HTTPS/SSL 之后,接下来你将把目标机器添加到 prometheus 的“scrape_config”部分。
使用以下 nano 编辑器命令打开 prometheus 配置文件“/etc/prometheus/prometheus.yml”。
sudo nano /etc/prometheus/prometheus.yml在 scrape_config 部分,使用以下行替换默认配置。
scrape_configs:
  # The job name is added as a label `job=<job_name>` to any timeseries scraped from this config.
  - job_name: "prometheus"
    # metrics_path defaults to '/metrics'
    # scheme defaults to 'http'.
    # add settings for certificate and authentication
    scheme: https
    tls_config:
      cert_file: /etc/prometheus/server.crt
      key_file: /etc/prometheus/server.key
      # if using self-signed certificate, set [true]
      insecure_skip_verify: true
    basic_auth:
      username: 'promadmin'
      password: 'password'
    static_configs:
      # if using a valid certificate, set the same hostname in the certificate
      - targets: ["localhost:9090"]
  - job_name: "node_exporter"
    static_configs:
      - targets: ["192.168.5.120:9100"]
通过此配置,你将设置两个名为“prometheus”和“node_exporter”的任务。并务必修改“prometheus”任务中的 basic_auth 部分。
- 在“prometheus”任务中,你将启用 HTTPS 安全连接,并启用“basic_auth”进行身份验证。在“prometheus”任务中,目标主机为“localhost:9090”,即 prometheus 服务器。
- 在“node_exporter”任务中,目标是 node_exporter 服务本身,它运行在端口“9100”上。
现在运行以下 systemctl 命令重启 prometheus 和 node_exporter 两个服务,使新更改生效。
sudo systemctl restart prometheus node_exporter至此,你已通过启用基本身份验证和 SSL/HTTPS 加密,将 prometheus 提升到了更高安全级别。你还添加了两个用于收集指标的抓取任务,即“prometheus”和“node_exporter”。
要验证你的安装,请打开 Web 浏览器并访问服务器 IP 地址加上端口“9090”(例如:https://192.168.5.120:9090/)。
现在系统会提示你进行基本身份验证,输入用户“promadmin”和你创建的密码。
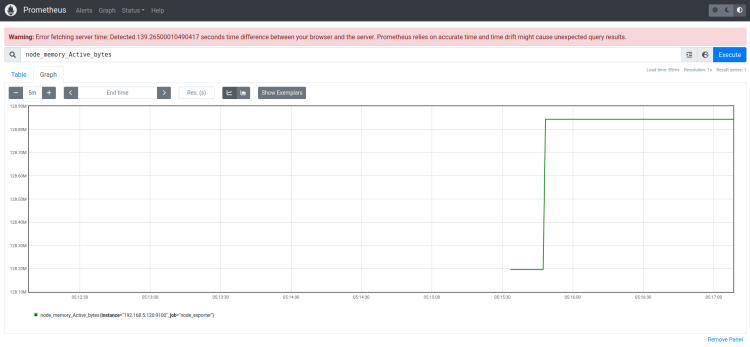
登录后,你应该会看到 prometheus 仪表盘。输入诸如“node_memory_Active_bytes”的查询并点击“Execute”。你应该会获得已执行查询对应的指标。
查询“node_memory_Active_bytes”由“node_exporter”提供,用于检查活动内存。
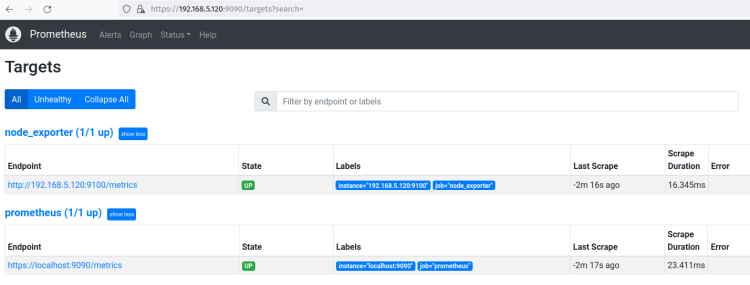
接下来,点击“Status”菜单并选择“Target”。你应该会看到你创建的两个不同任务,即“prometheus”和“node_exporter”。这两个任务的状态均为 up(正常运行)。
prometheus 和 node_exporter 配置完成后,接下来你将把 prometheus 添加为 grafana 的数据源。
将 Prometheus 添加为 Grafana 的数据源
Grafana 支持多种数据源,例如 MySQL、PostgreSQL、Influxdb、Graphite、Prometheus 等等。在此步骤中,你将把 prometheus 添加为 grafana 的数据源。
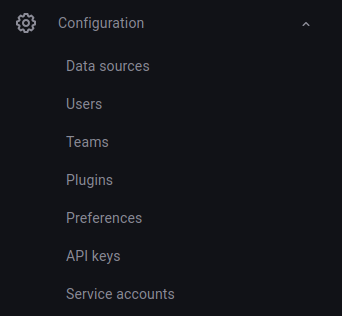
在 grafana 仪表盘上,点击“Configuration”菜单并选择“Data Sources”。
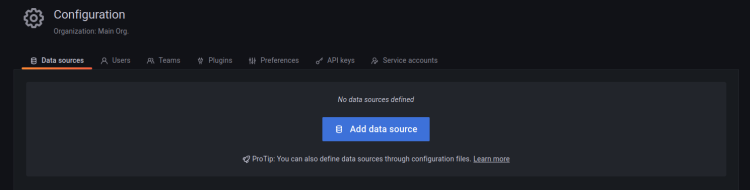
现在点击“Add data source”以添加新的数据源。
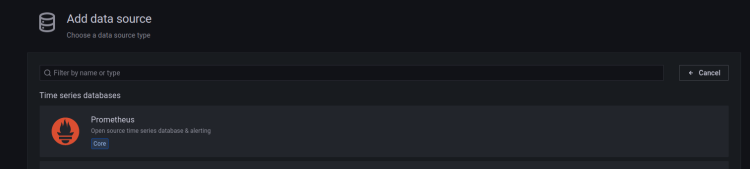
选择你要添加的数据源类型。本示例为“Prometheus”。
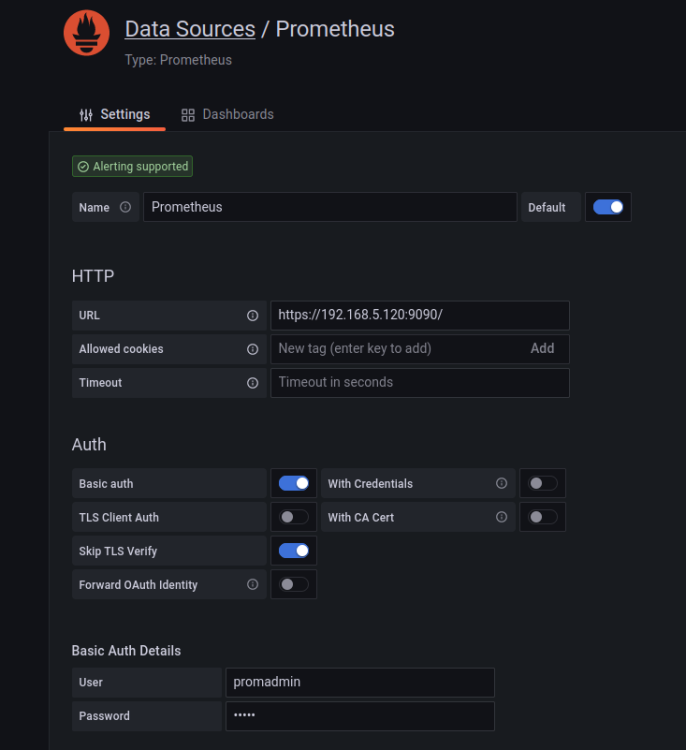
现在输入 prometheus 配置的详细信息——即“prometheus”的 scrape_config。务必启用“Basic auth”和“Skip TLS Verify”(如果你使用的是自签名证书)。
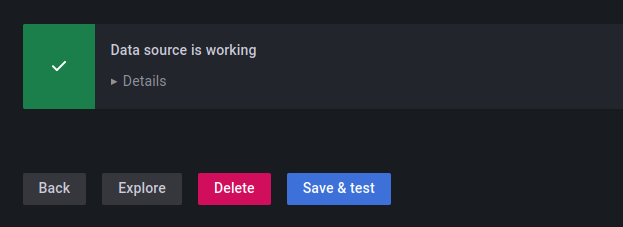
向下滚动到页面底部,点击“Save & test”进行确认。如果你看到类似“Data source is working”的输出信息,那么你已经成功将 prometheus 数据源添加到 grafana。
配置仪表盘监控
将 Prometheus 作为数据源添加到 Grafana 后,你可以创建新的仪表盘来监控系统。你可以手动为每个单元格创建仪表盘,也可以从 Grafana 仪表盘仓库导入一些 Grafana 仪表盘示例。
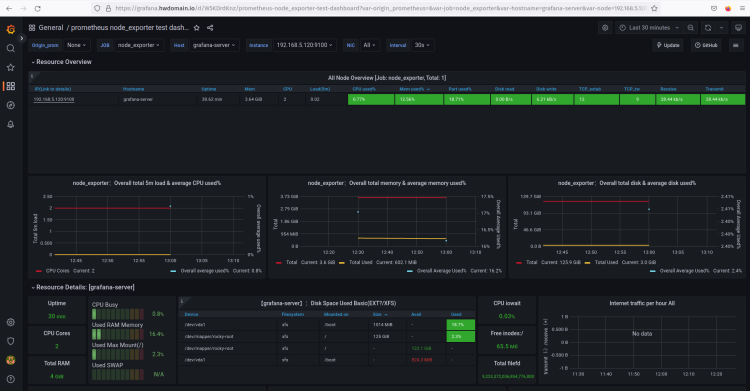
在此步骤中,你将通过在线导入可用的仪表盘到 Grafana 来设置 Grafana 仪表盘。
点击“Dashboard”菜单并选择“Import”。
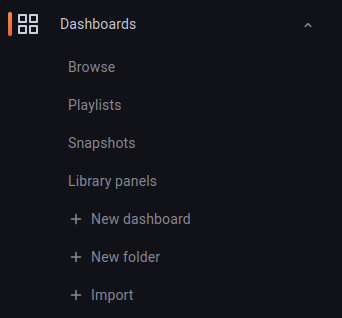
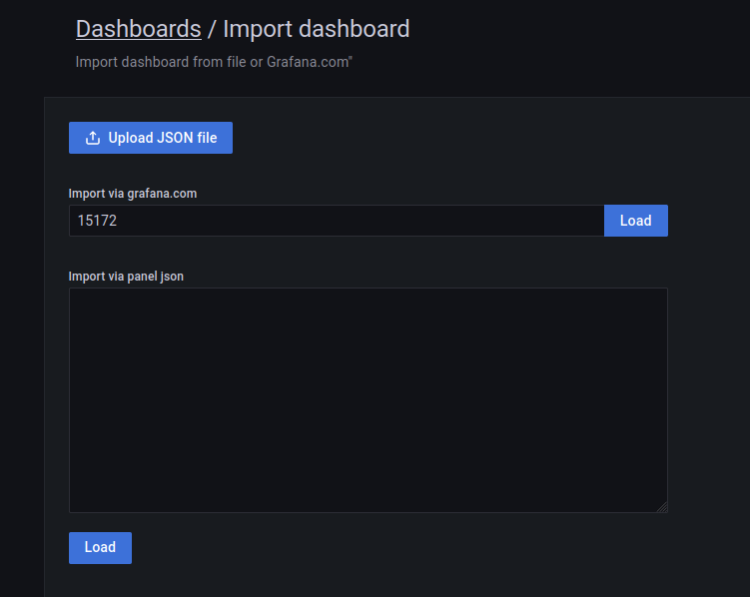
现在你可以从 Grafana 仪表盘仓库中找到仪表盘示例。本示例使用 ID 为“15172”的 Grafana 仪表盘。
输入你要导入的仪表盘 ID“15172”,然后点击“Load”。
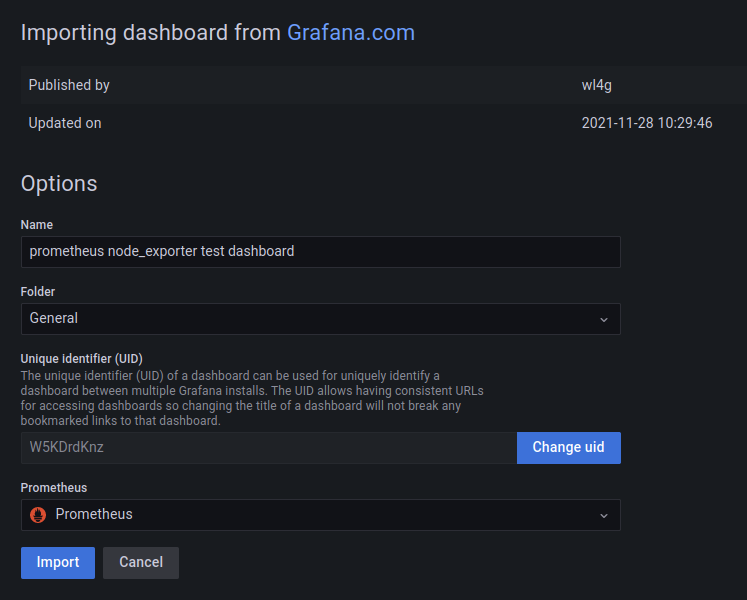
现在,输入新仪表盘的名称,并选择“Prometheus”作为数据源。点击“Import”确认。
在以下截图中确认,已创建用于监控系统、以 prometheus 为数据源的新 grafana 仪表盘。
总结
在本教程中,你在 Rocky Linux 9 服务器上安装了用于数据可视化的 Grafana,并使用 Nginx 作为反向代理。你还随 Grafana 一起安装了 Prometheus 和 node_exporter。
Prometheus 在启用了 SSL/TLS 连接、启用 basic_auth 模块进行用户身份验证的情况下运行,并配置了两个抓取任务,分别通过 Prometheus 自身和 node_exporter 来收集系统指标。
最后,你将 Prometheus 添加为 Grafana 的数据源,并导入了一个仪表盘,用于可视化由 Prometheus 和 node_exporter 收集的数据。
在此基础上,你可以为你的应用向 Prometheus 添加另一个 exporter,并通过 Grafana 数据可视化仪表盘查看所有指标。