
本教程适用于以下操作系统版本
- Ubuntu 22.04(Jammy Jellyfish)
- Ubuntu 20.04(Focal Fossa)
本页内容
- 准备工作
- 安装 Apache、PHP 和 MariaDB
- 配置 MariaDB 数据库
- 下载 ElkArte
- 为 ElkArte 配置 Apache
- 访问 ElkArte Web 界面
- 使用 Let's Encrypt SSL 保护 ElkArte
- 总结
ElkArte 是一款使用 PHP 语言编写的免费开源论坛软件。它基于 Simple Machines Forum(简单机器论坛),可帮助你轻松创建社区论坛。它已发展成为一个现代化、功能丰富的论坛套件,能够满足当今论坛用户的需求。它提供了由社区创建的丰富主题(Themes)和插件(Addons),可帮助你扩展 ElkArte 的功能。
本教程将向你展示如何在 Ubuntu 22.04 上安装 ElkArte,并配置 Let's Encrypt SSL。
准备工作
- 一台运行 Ubuntu 22.04 的服务器。
- 一个已指向你服务器的有效域名。
- 服务器上已配置 root 密码。
安装 Apache、PHP 和 MariaDB
ElkArte 运行在基于 PHP 的 Web 服务器上,并使用 MariaDB 作为数据库后端。因此,你需要在服务器上安装 Apache、MariaDB、PHP 以及其他 PHP 扩展。
首先,使用以下命令安装 Apache 和 MariaDB 服务器:
apt install apache2 mariadb-server接下来,你需要在服务器上安装 PHP 7.4 版本及其他所需扩展。默认情况下,Ubuntu 22.04 默认软件源中自带的是 PHP 8.1 版本。因此,你需要在服务器上添加 Ondrej PHP 软件源。
apt install software-properties-common -y
add-apt-repository ppa:ondrej/php -y
将 PHP 软件源添加到服务器后,你可以使用以下命令安装 PHP:
apt install php7.4 libapache2-mod-php7.4 php7.4-common php7.4-curl php7.4-intl php7.4-mbstring php7.4-xmlrpc php7.4-mysql php7.4-gd php7.4-pgsql php7.4-xml php7.4-cli php7.4-imagick php7.4-bcmath php7.4-gmp php7.4-zip unzip -y所有软件包安装完成后,打开 php.ini 文件并修改默认设置:
nano /etc/php/7.4/apache2/php.ini修改以下行:
Change the following lines:
memory_limit = 256M
upload_max_filesize = 100M
max_execution_time = 360
date.timezone = Asia/Kolkata
保存并关闭文件,然后重启 Apache 服务以使更改生效:
systemctl restart apache2配置 MariaDB 数据库
首先,使用以下命令加固 MariaDB 安装并设置 MariaDB root 密码:
mysql_secure_installation按下图所示回答所有问题:
Enter current password for root (enter for none):
Set root password? [Y/n] Y
New password:
Re-enter new password:
Remove anonymous users? [Y/n] Y
Disallow root login remotely? [Y/n] Y
Remove test database and access to it? [Y/n] Y
Reload privilege tables now? [Y/n] Y
接下来,使用以下命令登录到 MariaDB 命令行:
mysql -u root -p登录后,为 ElkArte 创建一个数据库和用户:
MariaDB [(none)]> CREATE DATABASE elkdb;
MariaDB [(none)]> CREATE USER 'elk'@'localhost' IDENTIFIED BY 'password';
接下来,使用以下命令为 elkdb 授予所有权限:
MariaDB [(none)]> GRANT ALL ON elkdb.* TO 'elk'@'localhost' WITH GRANT OPTION;接下来,使用以下命令刷新权限并退出 MariaDB 命令行:
MariaDB [(none)]> FLUSH PRIVILEGES;
MariaDB [(none)]> EXIT;
数据库配置完成后,你可以进入下一步。
下载 ElkArte
首先,使用以下命令从 Git 仓库下载 ElkArte 的最新版本:
wget https://github.com/elkarte/Elkarte/releases/download/v1.1.8/ElkArte_v1-1-8_install.zip下载完成后,使用以下命令将下载的文件解压到 Apache 的 Web 根目录:
unzip ElkArte_v1-1-8_install.zip -d /var/www/html/elkarte接下来,使用以下命令为 elkarte 目录设置正确的权限:
chown -R www-data:www-data /var/www/html/elkarte/
chmod -R 755 /var/www/html/elkarte/
完成后,你可以进入下一步。
为 ElkArte 配置 Apache
接下来,为 ElkArte 创建一个新的 Apache 虚拟主机配置文件。
nano /etc/apache2/sites-available/elkarte.conf添加以下行:
<VirtualHost *:80>
     ServerAdmin
[email protected]

     ServerName elk.linuxbuz.com
     DocumentRoot /var/www/html/elkarte

     <Directory /var/www/html/elkarte/>
          Options FollowSymlinks
          AllowOverride All
          Require all granted
     </Directory>

     ErrorLog ${APACHE_LOG_DIR}/error.log
     CustomLog ${APACHE_LOG_DIR}/access.log combined

</VirtualHost>
完成后保存并关闭文件。然后,使用以下命令启用 Apache 虚拟主机和重写模块:
a2ensite elkarte.conf
a2enmod rewrite
最后,重启 Apache 服务以使更改生效。
systemctl restart apache2你也可以使用该命令查看 Apache 的状态:
systemctl status apache2你将看到类似以下的输出:
? apache2.service - The Apache HTTP Server
     Loaded: loaded (/lib/systemd/system/apache2.service; enabled; vendor preset: enabled)
     Active: active (running) since Sun 2022-09-11 13:35:46 UTC; 9s ago
       Docs: https://httpd.apache.org/docs/2.4/
    Process: 30485 ExecStart=/usr/sbin/apachectl start (code=exited, status=0/SUCCESS)
   Main PID: 30490 (apache2)
      Tasks: 6 (limit: 4579)
     Memory: 14.9M
        CPU: 90ms
     CGroup: /system.slice/apache2.service
             ??30490 /usr/sbin/apache2 -k start
             ??30549 /usr/sbin/apache2 -k start
             ??30550 /usr/sbin/apache2 -k start
             ??30551 /usr/sbin/apache2 -k start
             ??30552 /usr/sbin/apache2 -k start
             ??30553 /usr/sbin/apache2 -k start

Sep 11 13:35:46 ubuntu2204 systemd[1]: Starting The Apache HTTP Server...
访问 ElkArte Web 界面
现在,打开你的 Web 浏览器并访问 URL https://elk.linuxbuz.com。你将被重定向到 ElkArte 欢迎页面:
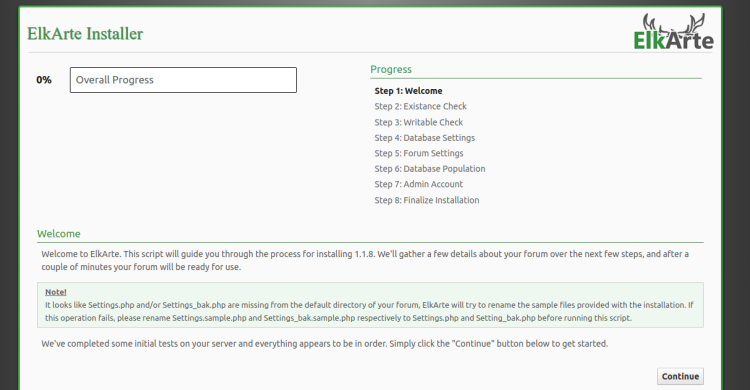
点击 Continue(继续)按钮。你应该会看到数据库服务器设置页面:
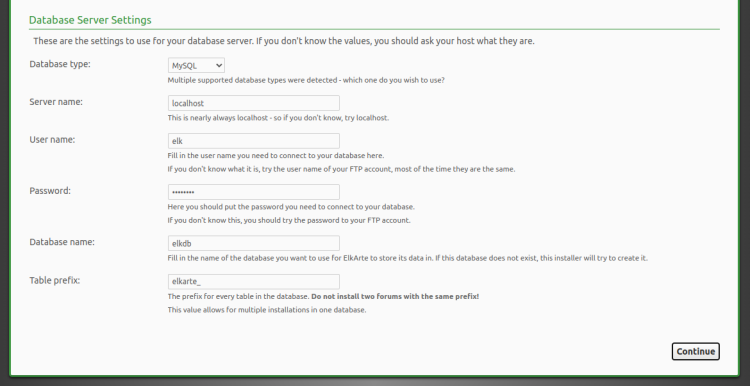
填写你的数据库信息并点击 Continue(继续)按钮。你应该会看到论坛设置页面:
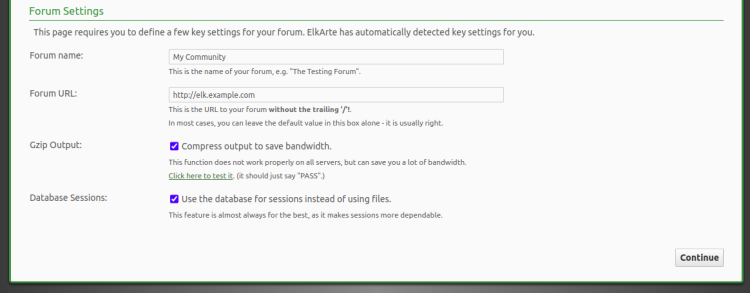
填写你的论坛 URL 和论坛名称,并点击 Continue(继续)按钮。你应该会看到如下页面:
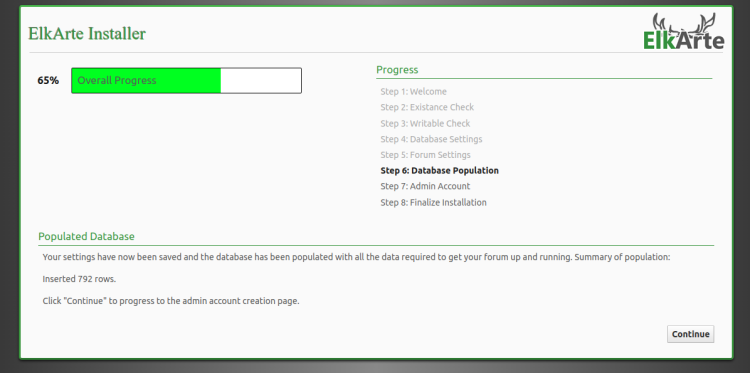
点击 Continue(继续)按钮。你应该会看到管理员账户创建页面:
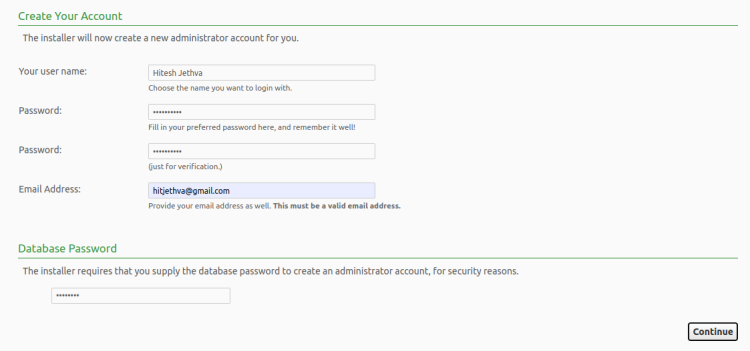
填写你的管理员用户名、密码、邮箱,并点击 Continue(继续)按钮。安装完成后,你应该会看到如下页面:
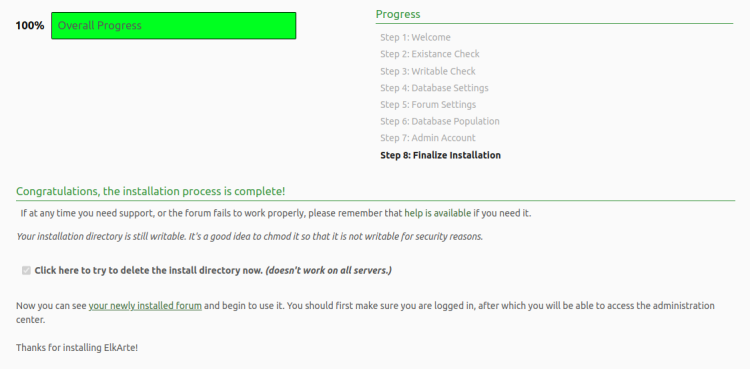
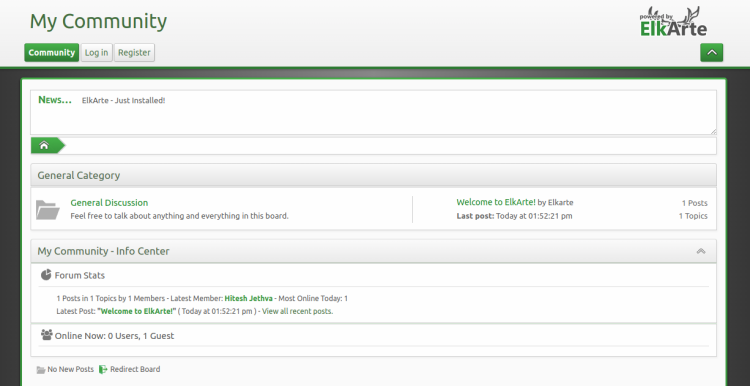
点击你新安装的论坛。你应该在如下页面看到 ElkArte 仪表盘:
使用 Let's Encrypt SSL 保护 ElkArte
首先,安装 Certbot Let's Encrypt 客户端以管理你网站的 SSL:
apt-get install certbot python3-certbot-apache -yCertbot 安装完成后,运行以下命令为你的网站下载并安装 Let's Encrypt SSL:
certbot --apache -d elk.linuxbuz.com系统会要求你提供电子邮件地址并接受服务条款,如下图所示:
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator apache, Installer apache
Enter email address (used for urgent renewal and security notices) (Enter 'c' to
cancel):
[email protected]


- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at
https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf. You must
agree in order to register with the ACME server at
https://acme-v02.api.letsencrypt.org/directory
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(A)gree/(C)ancel: A

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing to share your email address with the Electronic Frontier
Foundation, a founding partner of the Let's Encrypt project and the non-profit
organization that develops Certbot? We'd like to send you email about our work
encrypting the web, EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: Y

Obtaining a new certificate
Performing the following challenges:
http-01 challenge for elk.linuxbuz.com
Enabled Apache rewrite module
Waiting for verification...
Cleaning up challenges
Created an SSL vhost at /etc/apache2/sites-available/elk-le-ssl.conf
Enabled Apache socache_shmcb module
Enabled Apache ssl module
Deploying Certificate to VirtualHost /etc/apache2/sites-available/elk-le-ssl.conf
Enabling available site: /etc/apache2/sites-available/elk-le-ssl.conf
接下来,选择是否将 HTTP 流量重定向到 HTTPS,如下图所示:
Please choose whether or not to redirect HTTP traffic to HTTPS, removing HTTP access.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
1: No redirect - Make no further changes to the webserver configuration.
2: Redirect - Make all requests redirect to secure HTTPS access. Choose this for
new sites, or if you're confident your site works on HTTPS. You can undo this
change by editing your web server's configuration.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Select the appropriate number [1-2] then [enter] (press 'c' to cancel): 2
输入 2 并按回车键完成安装,如下图所示。
Redirecting vhost in /etc/apache2/sites-enabled/elk.conf to ssl vhost in /etc/apache2/sites-available/elk-le-ssl.conf

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations! You have successfully enabled https://elk.linuxbuz.com

You should test your configuration at:
https://www.ssllabs.com/ssltest/analyze.html?d=elk.linuxbuz.com
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/elk.linuxbuz.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/elk.linuxbuz.com/privkey.pem
   Your cert will expire on 2020-08-19. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot again
   with the "certonly" option. To non-interactively renew *all* of
   your certificates, run "certbot renew"
 - Your account credentials have been saved in your Certbot
   configuration directory at /etc/letsencrypt. You should make a
   secure backup of this folder now. This configuration directory will
   also contain certificates and private keys obtained by Certbot so
   making regular backups of this folder is ideal.
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le

 - We were unable to subscribe you the EFF mailing list because your
   e-mail address appears to be invalid. You can try again later by
   visiting https://act.eff.org.
至此,你的 ElkArte 已通过 Let's Encrypt SSL 得到保护。
总结
恭喜!你已成功在 Ubuntu 22.04 上安装了带 Let's Encrypt SSL 的 ElkArte。现在你可以轻松地使用 ElkArte 托管自己的社区论坛。如果你有任何疑问,欢迎随时向我提问。