
本页内容
- 准备工作
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Nginx
- 步骤 3 - 安装 Git
- 步骤 4 - 安装 Hugo
- 步骤 5 - 创建新的 Hugo 站点
- 步骤 6 - 安装 Hugo 主题 方法 1 - 克隆 Hugo 主题 方法 2 - 从压缩包安装主题 方法 3 - 以 Git 子模块方式安装主题 配置 Hugo
- 步骤 7 - 创建文章和页面 配置主题
- 步骤 8 - 发布 Hugo 站点
- 步骤 9 - 安装 SSL
- 步骤 10 - 配置 Nginx
- 步骤 11 - 配置 SELinux
- 步骤 12 - 运行站点
- 步骤 13 - 更新 Hugo
- 步骤 14 - 备份与恢复 Hugo
- 总结
- 方法 1 - 克隆 Hugo 主题
- 方法 2 - 从压缩包安装主题
- 方法 3 - 以 Git 子模块方式安装主题
- 配置 Hugo
- 配置主题
静态站点由静态内容页面或纯 HTML、JavaScript 或 CSS 代码构建。其内容并非动态生成,不涉及任何数据库或服务器端处理。这类站点速度极快,且不会受到依赖动态代码或 SQL 的漏洞攻击。
Hugo 是一个用 Go 编写的开源静态站点生成器。它通过将用 markdown 语言编写的文章转换为 HTML 来生成内容。Hugo 还内置了一个服务器,用于托管其生成的站点。你也可以将 Hugo 网站托管在 Amazon S3、GitHub pages、Google Cloud、Netlify、Vercel 等平台上。
在本教程中,我们将探讨如何在运行 Rocky Linux 9 的服务器上安装 Hugo 以创建一个静态网站。我们将使用 Nginx 服务器来托管站点,并使用 Let's Encrypt SSL 证书来保护我们的安装。
准备工作
- 一台运行 Rocky Linux 9 的服务器。
- 一个具有 sudo 权限的非 root 用户。
- 一个指向你服务器的完全限定域名(FQDN)。在本教程中,我们将使用 hugo.example.com 作为域名。
- 确保所有内容都已更新。$ sudo dnf update
- 安装基础工具包。其中部分可能已安装。$ sudo dnf install wget curl nano unzip yum-utils tree -y
一台运行 Rocky Linux 9 的服务器。
一个具有 sudo 权限的非 root 用户。
一个指向你服务器的完全限定域名(FQDN)。在本教程中,我们将使用 hugo.example.com 作为域名。
确保所有内容都已更新。
$ sudo dnf update
安装基础工具包。其中部分可能已安装。
$ sudo dnf install wget curl nano unzip yum-utils tree -y
步骤 1 - 配置防火墙
第一步是配置防火墙。Rocky Linux 使用 Firewalld 防火墙。检查防火墙的状态。
$ sudo firewall-cmd --state
running
防火墙使用不同的区域(zone),public 区域是我们将使用的默认区域。列出防火墙上所有处于活动状态的服务和端口。
$ sudo firewall-cmd --permanent --list-services
它应该显示以下输出。
cockpit dhcpv6-client ssh
Wiki.js 需要 HTTP 和 HTTPS 端口才能运行。开放这些端口。
$ sudo firewall-cmd --add-service=http --permanent
$ sudo firewall-cmd --add-service=https --permanent
重新加载防火墙以应用更改。
$ sudo firewall-cmd --reload
步骤 2 - 安装 Nginx
Rocky Linux 9 自带较旧版本的 Nginx。你需要下载官方的 Nginx 仓库来安装最新版本。
创建并打开 /etc/yum.repos.d/nginx.repo 文件以创建官方的 Nginx 仓库。
$ sudo nano /etc/yum.repos.d/nginx.repo
将以下代码粘贴到其中。
[nginx-stable]
name=nginx stable repo
baseurl=http://nginx.org/packages/centos/$releasever/$basearch/
gpgcheck=1
enabled=1
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true

[nginx-mainline]
name=nginx mainline repo
baseurl=http://nginx.org/packages/mainline/centos/$releasever/$basearch/
gpgcheck=1
enabled=0
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true
按 Ctrl + X 保存文件,并在提示时输入 Y。
安装 Nginx 服务器。
$ sudo dnf install nginx -y
验证安装。
$ nginx -v
nginx version: nginx/1.24.0
启用并启动 Nginx 服务器。
$ sudo systemctl enable nginx --now
检查服务器状态。
$ sudo systemctl status nginx
? nginx.service - nginx - high performance web server
     Loaded: loaded (/usr/lib/systemd/system/nginx.service; enabled; preset: disabled)
     Active: active (running) since Mon 2023-10-30 08:24:05 UTC; 7s ago
       Docs: http://nginx.org/en/docs/
    Process: 4265 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 4266 (nginx)
      Tasks: 2 (limit: 4402)
     Memory: 1.9M
        CPU: 7ms
     CGroup: /system.slice/nginx.service
             ??4266 "nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf"
             ??4267 "nginx: worker process"

Oct 30 08:24:05 hugo.example.com systemd[1]: Starting nginx - high performance web server...
步骤 3 - 安装 Git
Hugo 需要 Git 才能工作。运行以下命令来安装 Git
$ sudo dnf install git -y
验证 Git 安装。
$ git --version
git version 2.39.3
步骤 4 - 安装 Hugo
由于 Hugo 是使用 Go 语言构建的,安装它相当容易,因为它不需要任何依赖项,可以独立运行。
下载 Hugo。在本教程中,我们将安装 Hugo 的 extended 版本。extended 版本在处理图片时可以将图片编码为 Webp 格式。如果你希望 Hugo 即时为你转换图片并减小其体积,这会很有用。extended 版本还包含了一个 SASS 编译器,在你有需要的情况下会很有用。
为 Hugo 创建一个目录。
$ sudo mkdir /var/www/html/hugo -p
切换到新创建的目录。
$ cd /var/www/html/hugo
从 GitHub 的 releases 页面下载 Hugo。在撰写本教程时,v0.119.0 是最新版本,我们也将下载该版本。
$ sudo wget https://github.com/gohugoio/hugo/releases/download/v0.119.0/hugo_extended_0.119.0_linux-amd64.tar.gz
从压缩包中提取文件。
$ sudo tar -xzf hugo_extended_0.119.0_linux-amd64.tar.gz
你会在目录中看到以下三个文件。
$ ls
hugo  hugo_extended_0.119.0_linux-amd64.tar.gz  LICENSE  README.md
将 hugo 二进制文件移动到 /usr/bin 目录。
$ sudo mv hugo /usr/bin/hugo
该文件已经设置了可执行权限,因此你无需再设置。
确认安装。
$ hugo version
hugo v0.119.0-b84644c008e0dc2c4b67bd69cccf87a41a03937e+extended linux/amd64 BuildDate=2023-09-24T15:20:17Z VendorInfo=gohugoio
你也可以通过使用 --help 标志来查看所有可用的选项。
$ hugo --help
你将得到以下输出。
hugo is the main command, used to build your Hugo site.

Hugo is a Fast and Flexible Static Site Generator
built with love by spf13 and friends in Go.

Complete documentation is available at https://gohugo.io/.

Usage:
  hugo [flags]
  hugo [command]

Available Commands:
  completion  Generate the autocompletion script for the specified shell
  config      Print the site configuration
  convert     Convert your content to different formats
  deploy      Deploy your site to a Cloud provider.
  env         Print Hugo version and environment info
  gen         A collection of several useful generators.
  help        Help about any command
  import      Import your site from others.
  list        Listing out various types of content
  mod         Various Hugo Modules helpers.
  new         Create new content for your site
  server      A high performance webserver
  version     Print Hugo version and environment info

Flags:
  -b, --baseURL string             hostname (and path) to the root, e.g. https://spf13.com/
  -D, --buildDrafts                include content marked as draft
  -E, --buildExpired               include expired content
  -F, --buildFuture                include content with publishdate in the future
      --cacheDir string            filesystem path to cache directory
      --cleanDestinationDir        remove files from destination not found in static directories
      --clock string               set the clock used by Hugo, e.g. --clock 2021-11-06T22:30:00.00+09:00
      --config string              config file (default is hugo.yaml|json|toml)
      --configDir string           config dir (default "config")
  -c, --contentDir string          filesystem path to content directory
      --debug                      debug output
  -d, --destination string         filesystem path to write files to
      --disableKinds strings       disable different kind of pages (home, RSS etc.)
      --enableGitInfo              add Git revision, date, author, and CODEOWNERS info to the pages
  -e, --environment string         build environment
      --forceSyncStatic            copy all files when static is changed.
      --gc                         enable to run some cleanup tasks (remove unused cache files) after the build
  -h, --help                       help for hugo
      --ignoreCache                ignores the cache directory
      --ignoreVendorPaths string   ignores any _vendor for module paths matching the given Glob pattern
  -l, --layoutDir string           filesystem path to layout directory
      --logLevel string            log level (debug|info|warn|error)
      --minify                     minify any supported output format (HTML, XML etc.)
      --noBuildLock                don't create .hugo_build.lock file
      --noChmod                    don't sync permission mode of files
      --noTimes                    don't sync modification time of files
      --panicOnWarning             panic on first WARNING log
      --poll string                set this to a poll interval, e.g --poll 700ms, to use a poll based approach to watch for file system changes
      --printI18nWarnings          print missing translations
      --printMemoryUsage           print memory usage to screen at intervals
      --printPathWarnings          print warnings on duplicate target paths etc.
      --printUnusedTemplates       print warnings on unused templates.
      --quiet                      build in quiet mode
      --renderToMemory             render to memory (only useful for benchmark testing)
  -s, --source string              filesystem path to read files relative from
      --templateMetrics            display metrics about template executions
      --templateMetricsHints       calculate some improvement hints when combined with --templateMetrics
  -t, --theme strings              themes to use (located in /themes/THEMENAME/)
      --themesDir string           filesystem path to themes directory
      --trace file                 write trace to file (not useful in general)
  -v, --verbose                    verbose output
  -w, --watch                      watch filesystem for changes and recreate as needed

Use "hugo [command] --help" for more information about a command.
删除文件夹中所有剩余的文件,因为它们不再需要。
$ sudo rm -rf *.*
步骤 5 - 创建新的 Hugo 站点
执行以下命令来创建一个新的 Hugo 网站。
$ sudo hugo new site howtoforge
你将得到以下输出。
Congratulations! Your new Hugo site was created in /home/navjot/hugo/howtoforge.

Just a few more steps...

1. Change the current directory to /home/navjot/hugo/howtoforge.
2. Create or install a theme:
   - Create a new theme with the command "hugo new theme <THEMENAME>"
   - Install a theme from https://themes.gohugo.io/
3. Edit hugo.toml, setting the "theme" property to the theme name.
4. Create new content with the command "hugo new content <SECTIONNAME>/<FILENAME>.<FORMAT>".
5. Start the embedded web server with the command "hugo server --buildDrafts".

See documentation at https://gohugo.io/.
运行 tree 命令来检查站点的结构。
$ tree howtoforge/
你将得到以下输出。
howtoforge/
??? archetypes
?   ??? default.md
??? assets
??? content
??? data
??? hugo.toml
??? i18n
??? layouts
??? static
??? themes

8 directories, 2 files
切换到 Hugo 目录。
$ cd howtoforge
步骤 6 - 安装 Hugo 主题
下一步是安装一个 Hugo 主题。这有两种方法,且两种方法都需要 Git。第一种方法简单直接,即克隆主题的 GitHub 仓库。这在大多数情况下都很有用,也是最简便的方法。通过这种方法更新很容易,不过这种方法确实会下载很多你并不需要的多余内容。有些主题,尤其是付费主题,并没有可供获取的 GitHub 仓库。这类主题通常以压缩包的形式提供。在这种情况下,你需要手动解压压缩包并保持主题手动更新。第三种方法是将主题作为 Git 子模块获取。这要求你将 Hugo 目录初始化为一个 Git 仓库。这是推荐的方法,并且在你想将站点部署到 GitHub、Netlify 或任何其他托管服务时很有用。将你的 Hugo 站点推送到 GitHub 还能确保自动备份,且无需额外操作。
我们将介绍全部三种方法。还有另一种使用 Hugo Go modules 安装 Hugo 主题的方法。这种方法只有在主题以 Hugo 模块形式提供时才有效。不过,由于超出了本文的范围,我们将不涉及它。
方法 1 - 克隆 Hugo 主题
这是最常用的安装 Hugo 主题的方法。在本教程中,我们将安装 Paper 主题。切换到 Hugo 目录。
$ cd /var/www/html/hugo/howtoforge
运行以下命令来克隆主题的 GitHub 仓库。--depth=1 标志只会获取最新的提交。
$ sudo git clone https://github.com/nanxiaobei/hugo-paper themes/Paper --depth=1
要更新通过此方法下载的主题,请运行以下命令。
$ cd ~/hugo/howtoforge/themes/Paper
$ sudo git pull
方法 2 - 从压缩包安装主题
这是所有方法中最简单的一种。获取主题文件的压缩包。Paper 主题没有 releases 部分,因此你无法下载特定版本。因此,我们将下载 GitHub 的 master 压缩包。你可以从其 GitHub 仓库页面获取链接。
$ cd ~
$ wget https://github.com/nanxiaobei/hugo-paper/archive/refs/heads/main.zip
将压缩包解压到 themes 目录。-q 标志会抑制输出,-d 标志指定输出目录。
$ sudo unzip -q main.zip -d /var/www/html/hugo/howtoforge/themes/
要更新主题,你需要下载最新的压缩包并再次解压。请确保备份你所修改过的所有文件。
后两种方法只有在你的 Hugo 站点作为 Git 项目托管时才有效。否则,你无需使用以下方法。
方法 3 - 以 Git 子模块方式安装主题
切换到 Hugo 文件夹。
$ cd /var/www/html/hugo/howtoforge
将 Hugo 文件夹初始化为一个 Git 仓库。这是重要的一步。这可以让你将 Hugo 站点推送到 GitHub,以便日后用于通过 Netlify、AWS、Vercel 等托管。
$ sudo git init
运行以下命令,将主题添加为 Git 子模块。
$ sudo git submodule add https://github.com/nanxiaobei/hugo-paper themes/paper
要更新以子模块方式添加的主题,请从 Hugo 文件夹运行以下命令。
$ sudo git submodule update --remote --merge
配置 Hugo
使用你选择的方法安装主题后,打开 Hugo 根目录中的 hugo.toml 文件。从 Hugo v0.110.0 开始,默认配置文件名为 hugo.toml。如果你使用的是较旧版本的 Hugo,则会在 Hugo 目录中找到 config.toml 文件。
$ sudo nano hugo.toml
将以下行添加到文件中。其值应与主题目录相匹配。对于 paper 主题,如果你使用的是压缩包安装方式,则为 hugo-paper-theme 目录;如果你使用的是上述 Git 克隆或子模块方式,则为 Paper。
theme = 'hugo-paper-main'
同时,将变量 baseURL 的值更改为你站点的域名。并更改你网站的标题。
你的配置文件应如下所示。
baseURL = 'https://hugo.example.com/'
languageCode = 'en-us'
title = 'Howtoforge Hugo Demo'
theme = 'hugo-paper-main'
完成后,按 Ctrl + X 保存文件,并在提示时输入 Y。
步骤 7 - 创建文章和页面
要创建一篇新文章,请执行以下命令。
$ sudo hugo new post/first-post.md
这将在 content/post 文件夹中创建一个名为 first-post.md、标题为 First Post 的新 markdown 文件。在你喜欢的编辑器中打开该文件,编辑其中的细节,并为你的第一篇文章写些内容。
+++
title = 'First Post'
date = 2023-10-30T03:32:38Z
draft = true
+++
## Introduction

This is **bold** text, and this is *emphasized* text.

Visit the [Howtoforge](https://www.howtoforge.com) website!
完成文章撰写后,删除 draft = true。按 Ctrl + X 保存文件,并在提示时输入 Y。
要创建一个新页面,请执行以下命令。
$ sudo hugo new about.md
这将在 content 文件夹中创建一个名为 About 的新页面。打开它,并以与文章相同的方式对其进行编辑。
配置主题
在发布之前,我们需要对主题进行一些更改以显示菜单栏。这些更改将在 Hugo 的配置文件中完成,而不是在主题的配置文件中。
切换到 Hugo 目录。
$ cd /var/www/html/hugo/howtoforge
打开 hugo.toml 文件进行编辑。
$ sudo nano hugo.toml
将以下代码粘贴到文件末尾。
author = "Navjot Singh"
copyright = "Copyright © 2023, Navjot Singh; all rights reserved."
paginate = 3
enableInlineShortcodes = true
# needed to  render raw HTML (e.g. <sub>, <sup>, <kbd>, <mark>)
[markup]
  [markup.goldmark]
    [markup.goldmark.renderer]
      unsafe = true

[menu]
  [[menu.main]]
    identifier = "about"
    name = "About"
    url = "/about/"
    weight = 10

[taxonomies]
category = "categories"
tag = "tags"
series = "series"
按 Ctrl + X 保存文件,并在提示时输入 Y。
这些是使站点正常运行的一些基本设置。在这里,我们将站点配置为每页显示 3 篇文章,将 About 页面显示为菜单项,并设置了分类、标签和文章系列。我们还启用了 Hugo 的内联 shortcodes,并为 Goldmark Markdown 渲染启用了原始 HTML。如果你不希望在文章中嵌入原始 HTML,可以禁用它。
步骤 8 - 发布 Hugo 站点
要构建并发布站点,只需运行以下命令。
$ sudo hugo
你将得到类似的输出。
Start building sites …
hugo v0.119.0-b84644c008e0dc2c4b67bd69cccf87a41a03937e+extended linux/amd64 BuildDate=2023-09-24T15:20:17Z VendorInfo=gohugoio


                   | EN
-------------------+-----
  Pages            |  7
  Paginator pages  |  0
  Non-page files   |  0
  Static files     | 11
  Processed images |  0
  Aliases          |  3
  Sitemaps         |  1
  Cleaned          |  0

Total in 46 ms
这会在 public 文件夹中创建并发布静态 Hugo 网站。这些就是我们需要在 Nginx 配置中指定以使站点正常运行的文件。在做出任何更改后再次运行该命令,你的网站就会立即更新。
步骤 9 - 安装 SSL
在继续之前,我们需要安装 Certbot 工具,并为我们的域名安装 SSL 证书。
为了安装 Certbot,我们将使用 Snapd 软件包安装器。Snapd 始终携带最新稳定版的 Certbot,你应该使用它。
Snapd 工具需要 Epel 仓库才能工作。
$ sudo dnf install epel-release -y
我们将使用 Snapd 来安装 Certbot。安装 Snapd。
$ sudo dnf install snapd -y
启用并启动 Snap 服务。
$ sudo systemctl enable snapd.socket --now
创建 Snapd 工作所需的必要链接。
$ sudo ln -s /var/lib/snapd/snap /snap
$ echo 'export PATH=$PATH:/var/lib/snapd/snap/bin' | sudo tee -a /etc/profile.d/snapd.sh
确保你的 snapd 版本是最新的。在发出以下命令之前,请等待几秒钟。
$ sudo snap install core
$ sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可以运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
验证安装。
$ certbot --version
certbot 2.7.3
生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d hugo.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/hugo.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
你会发现 snap.certbot.renew.service 是计划运行的服务之一。
NEXT                        LEFT          LAST                        PASSED    UNIT                         ACTIVATES
Wed 2023-10-29 10:00:17 UTC 57min left    Wed 2023-10-18 08:49:39 UTC 12min ago dnf-makecache.timer          dnf-makecache.service
Wed 2023-10-29 12:18:00 UTC 3h 15min left -                           -         snap.certbot.renew.timer     snap.certbot.renew.service
Thu 2023-10-30 00:00:00 UTC 14h left      Wed 2023-10-18 08:10:08 UTC 52min ago logrotate.timer              logrotate.service
对该过程进行一次空运行(dry run),以检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果你没有看到错误,说明一切就绪。你的证书将自动续期。
步骤 10 - 配置 Nginx
创建并打开文件 /etc/nginx/conf.d/hugo.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/hugo.conf
将以下代码粘贴到 hugo.conf 文件中。将所有 hugo.example.com 替换为你自己的域名。
## enforce HTTPS
server {
  listen 80;
  listen [::]:80;
  server_name hugo.example.com;
  return 301 https://$server_name$request_uri;
}

server {
  listen 443 ssl http2;
  listen [::]:443 ssl http2;
  server_name hugo.example.com;

  root /home/navjot/hugo/howtoforge/public;
  index index.html

  access_log /var/log/nginx/hugo.access.log;
  error_log /var/log/nginx/hugo.error.log;
  client_max_body_size 20m;
  gzip on;

  http2_push_preload on; # Enable HTTP/2 Server Push

  ssl_certificate     /etc/letsencrypt/live/hugo.example.com/fullchain.pem;
  ssl_certificate_key /etc/letsencrypt/live/hugo.example.com/privkey.pem;
  ssl_trusted_certificate /etc/letsencrypt/live/hugo.example.com/chain.pem;
  ssl_session_timeout 1d;

  # Enable TLS versions (TLSv1.3 is required upcoming HTTP/3 QUIC).
  ssl_protocols TLSv1.2 TLSv1.3;

  # Enable TLSv1.3's 0-RTT. Use $ssl_early_data when reverse proxying to
  # prevent replay attacks.
  #
  # @see: https://nginx.org/en/docs/http/ngx_http_ssl_module.html#ssl_early_data
  ssl_early_data on;

  ssl_ciphers 'ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA384';
  ssl_prefer_server_ciphers on;
  ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
  ssl_session_cache shared:SSL:50m;
  ssl_session_tickets off;

  # OCSP Stapling ---
  # fetch OCSP records from URL in ssl_certificate and cache them
  ssl_stapling on;
  ssl_stapling_verify on;
  ssl_dhparam /etc/ssl/certs/dhparam.pem;

  add_header X-Early-Data $tls1_3_early_data;

  location / {
      try_files $uri $uri/ =404;
  }

  # Media
  location ~* \.(?:jpg|jpeg|gif|png|ico|cur|gz|svg|mp4|ogg|ogv|webm|htc)$ {
      expires 30d;
  }

  # CSS and Js
  location ~* \.(css|js)$ {
      expires 7d;
  }
}

# This block is useful for debugging TLS v1.3. Please feel free to remove this
# and use the `$ssl_early_data` variable exposed by NGINX directly should you
# wish to do so.
map $ssl_early_data $tls1_3_early_data {
  "~." $ssl_early_data;
  default "";
}
上述配置会将所有 HTTP 请求重定向到 HTTPS,并作为 Hugo 服务的代理,通过你的域名来提供服务。
按 Ctrl + X 保存文件,并在提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
验证你的 Nginx 配置。
$ sudo nginx -t
如果你没有看到错误,说明一切就绪。重新加载 Nginx 服务器。
$ sudo systemctl reload nginx
步骤 11 - 配置 SELinux
更改 OpenEMR 的文件安全上下文。
$ sudo semanage fcontext -a -t httpd_sys_rw_content_t "/var/www/html/hugo/howtoforge/public(/.*)?"
应用策略。
$ sudo restorecon -Rv /var/www/html/hugo/howtoforge/public/
允许 Nginx 连接网络。
$ sudo setsebool -P httpd_can_network_connect 1
步骤 12 - 运行站点
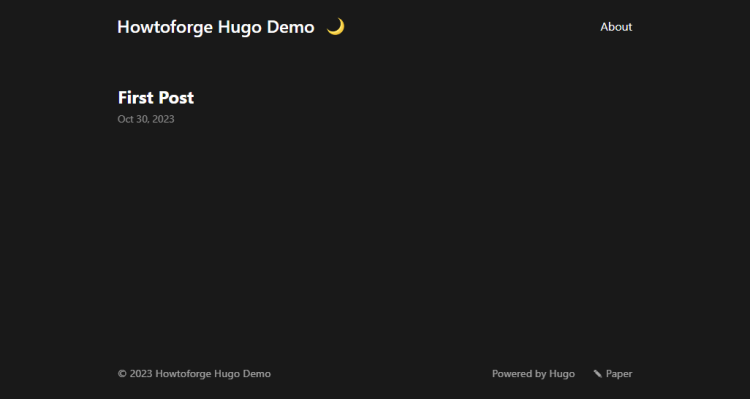
现在,你可以通过在网页浏览器中打开 https://hugo.example.com 来验证安装。你将看到以下页面,表明安装成功。
步骤 13 - 更新 Hugo
更新 Hugo 非常简单。从 Hugo 的 GitHub 页面下载最新版本。
$ cd /var/www/html/hugo
$ sudo wget https://github.com/gohugoio/hugo/releases/download/v0.119.0/hugo_extended_0.119.0_linux-amd64.tar.gz
解压压缩包。
$ sudo tar -xzf hugo_extended_0.119.0_linux-amd64.tar.gz
并用最新版本替换 Hugo 二进制文件。-f 标志会在不提示的情况下覆盖二进制文件。如果你希望在覆盖前进行提示,可以改用 -i 标志。
$ sudo mv -f hugo /usr/bin/hugo
就是这样。更新 Hugo 就像替换二进制文件一样简单。
步骤 14 - 备份与恢复 Hugo
要进行备份,请创建整个 Hugo 文件夹的压缩包。
$ cd /var/www/html/hugo
$ sudo tar -czvf howtoforge.tar.gz howtoforge/
要在新服务器上恢复,只需解压压缩包并安装二进制文件,即可大功告成。
$ cd /var/www/html/hugo
$ sudo tar -xzf howtoforge.tar.gz
总结
至此,我们关于如何在运行 Rocky Linux 9 的服务器上使用 Nginx 搭建 Hugo 静态站点生成器的教程就结束了。如果你有任何问题或反馈,请在下方评论中分享。