
本教程适用于以下操作系统版本
- Debian 12 (Bookworm)
- Debian 11 (Bullseye)
- Debian 10 (Buster)
本页内容
- 先决条件
- 安装 Jellyfin
- 将 Nginx 配置为 Jellyfin 的反向代理
- 访问 Jellyfin Web 界面
- 使用 Let's Encrypt 保护 Jellyfin
- 结语
Jellyfin 是一款免费开源的媒体串流应用,可对数字媒体文件进行整理、管理并共享给联网设备。它允许你将上传的媒体文件串流到你的 PC、笔记本、手机和 Roku 设备。它提供交互式 Web 界面来管理你所有的照片、视频和音乐。如果你正在寻找 Plex 和 Netflix 的替代方案,Jellyfin 是最佳选择。
功能特性
- 免费、开源且跨平台
- 支持使用 FFMpeg 对视频编解码进行硬件加速
- 允许从 TheTVDB 和 TheMovieDB 获取元数据
- 移动端应用无播放限制
本文将介绍如何在 Debian 11 上安装 Jellyfin 媒体串流应用,并配合 Nginx 与 Let's Encrypt SSL 使用。
先决条件
- 一台运行 Debian 11 的服务器。
- 一个已指向你服务器 IP 的有效域名。
- 服务器上已配置 root 密码。
安装 Jellyfin
在开始之前,你需要将 Jellyfin 仓库添加到 APT。为此,首先使用以下命令安装所需的依赖项:
apt-get install apt-transport-https ca-certificates gnupg2 curl git -y所有依赖安装完成后,使用以下命令添加 GPG 密钥与仓库:
wget -O - https://repo.jellyfin.org/jellyfin_team.gpg.key | apt-key add -
echo "deb [arch=$( dpkg --print-architecture )] https://repo.jellyfin.org/debian bullseye main" | tee /etc/apt/sources.list.d/jellyfin.list
接下来,更新仓库并安装 Jellyfin,使用以下命令:
apt-get update -y
apt-get install jellyfin -y
Jellyfin 安装完成后,你可以使用以下命令查看其运行状态:
systemctl status jellyfin你将看到如下输出:
? jellyfin.service - Jellyfin Media Server
     Loaded: loaded (/lib/systemd/system/jellyfin.service; enabled; vendor preset: enabled)
    Drop-In: /etc/systemd/system/jellyfin.service.d
             ??jellyfin.service.conf
     Active: active (running) since Fri 2022-02-04 03:48:50 UTC; 9s ago
   Main PID: 4989 (jellyfin)
      Tasks: 19 (limit: 2341)
     Memory: 85.0M
        CPU: 4.069s
     CGroup: /system.slice/jellyfin.service
             ??4989 /usr/bin/jellyfin --webdir=/usr/share/jellyfin/web --restartpath=/usr/lib/jellyfin/restart.sh --ffmpeg=/usr/lib/jellyfin->

Feb 04 03:48:56 debian11 jellyfin[4989]: [03:48:56] [INF] ServerId: 809b343f6da845699dd6447e1bb4f061
Feb 04 03:48:56 debian11 jellyfin[4989]: [03:48:56] [INF] Registering publisher for urn:schemas-upnp-org:device:MediaServer:1 on 127.0.0.1/32
Feb 04 03:48:56 debian11 jellyfin[4989]: [03:48:56] [WRN] 127.0.0.1/32: GetBindInterface: Loopback 127.0.0.1 returned.
Feb 04 03:48:56 debian11 jellyfin[4989]: [03:48:56] [INF] Executed all pre-startup entry points in 0:00:00.2808517
Feb 04 03:48:56 debian11 jellyfin[4989]: [03:48:56] [INF] Core startup complete
Feb 04 03:48:57 debian11 jellyfin[4989]: [03:48:57] [INF] Executed all post-startup entry points in 0:00:00.2169291
Feb 04 03:48:57 debian11 jellyfin[4989]: [03:48:57] [INF] Startup complete 0:00:06.7385186
Feb 04 03:48:59 debian11 jellyfin[4989]: [03:48:59] [INF] StartupTrigger fired for task: Update Plugins
Feb 04 03:48:59 debian11 jellyfin[4989]: [03:48:59] [INF] Queuing task PluginUpdateTask
Feb 04 03:48:59 debian11 jellyfin[4989]: [03:48:59] [INF] Executing Update Plugins
默认情况下,Jellyfin 监听 8096 端口。你可以使用以下命令进行查看:
ss -antpl | grep 8096你将看到如下输出:
LISTEN 0 512 0.0.0.0:8096 0.0.0.0:* users:(("jellyfin",pid=4989,fd=289))
将 Nginx 配置为 Jellyfin 的反向代理
接下来,你需要安装并配置 Nginx 作为 Jellyfin 的反向代理。首先,使用以下命令安装 Nginx:
apt-get install nginx -y接下来,使用以下命令创建 Nginx 虚拟主机配置文件:
nano /etc/nginx/conf.d/jellyfin.conf添加以下内容:
server {
      listen 80;
      server_name jellyfin.example.com;

      access_log /var/log/nginx/jellyfin.access;
      error_log /var/log/nginx/jellyfin.error;

    resolver 127.0.0.1 valid=30;

    # Security / XSS Mitigation Headers
    add_header X-Frame-Options "SAMEORIGIN";
    add_header X-XSS-Protection "1; mode=block";
    add_header X-Content-Type-Options "nosniff";


    location / {
        # Proxy main Jellyfin traffic
        proxy_pass http://localhost:8096;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header X-Forwarded-Protocol $scheme;
        proxy_set_header X-Forwarded-Host $http_host;

        # Disable buffering when the nginx proxy gets very resource heavy upon streaming
        proxy_buffering off;
    }

    # location block for /web - This is purely for aesthetics so /web/#!/ works instead of having to go to /web/index.html/#!/
    location = /web/ {
        # Proxy main Jellyfin traffic
        proxy_pass http://localhost:8096/web/index.html;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header X-Forwarded-Protocol $scheme;
        proxy_set_header X-Forwarded-Host $http_host;
    }

    location /socket {
        # Proxy Jellyfin Websockets traffic
        proxy_pass http://localhost:8096/socket;
        proxy_http_version 1.1;
        proxy_set_header Upgrade $http_upgrade;
        proxy_set_header Connection "upgrade";
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header X-Forwarded-Protocol $scheme;
        proxy_set_header X-Forwarded-Host $http_host;
    }
}
保存并关闭文件,然后检查 Nginx 是否存在语法错误。
nginx -t你将看到如下输出:
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
最后,重启 Nginx 使配置生效:
systemctl reload nginx使用以下命令查看 Nginx 的状态:
systemctl status nginx你应该看到如下输出:
? nginx.service - A high performance web server and a reverse proxy server
     Loaded: loaded (/lib/systemd/system/nginx.service; enabled; vendor preset: enabled)
     Active: active (running) since Fri 2022-02-04 03:49:27 UTC; 55s ago
       Docs: man:nginx(8)
    Process: 6314 ExecStartPre=/usr/sbin/nginx -t -q -g daemon on; master_process on; (code=exited, status=0/SUCCESS)
    Process: 6315 ExecStart=/usr/sbin/nginx -g daemon on; master_process on; (code=exited, status=0/SUCCESS)
    Process: 6454 ExecReload=/usr/sbin/nginx -g daemon on; master_process on; -s reload (code=exited, status=0/SUCCESS)
   Main PID: 6395 (nginx)
      Tasks: 2 (limit: 2341)
     Memory: 2.8M
        CPU: 66ms
     CGroup: /system.slice/nginx.service
             ??6395 nginx: master process /usr/sbin/nginx -g daemon on; master_process on;
             ??6455 nginx: worker process

Feb 04 03:49:27 debian11 systemd[1]: Starting A high performance web server and a reverse proxy server...
Feb 04 03:49:27 debian11 systemd[1]: nginx.service: Failed to parse PID from file /run/nginx.pid: Invalid argument
Feb 04 03:49:27 debian11 systemd[1]: Started A high performance web server and a reverse proxy server.
Feb 04 03:50:17 debian11 systemd[1]: Reloading A high performance web server and a reverse proxy server.
Feb 04 03:50:17 debian11 systemd[1]: Reloaded A high performance web server and a reverse proxy server.
访问 Jellyfin Web 界面
现在,打开你的 Web 浏览器,通过 URL http://jellyfin.example.com 访问 Jellyfin Web 界面。你将被重定向到如下页面:
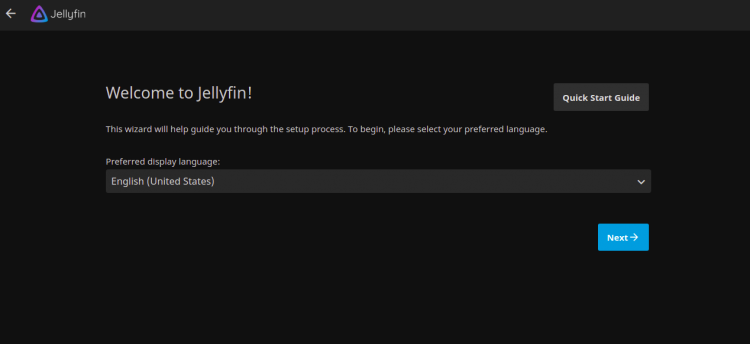
选择你的语言,然后点击 Next 按钮。你将看到如下页面:
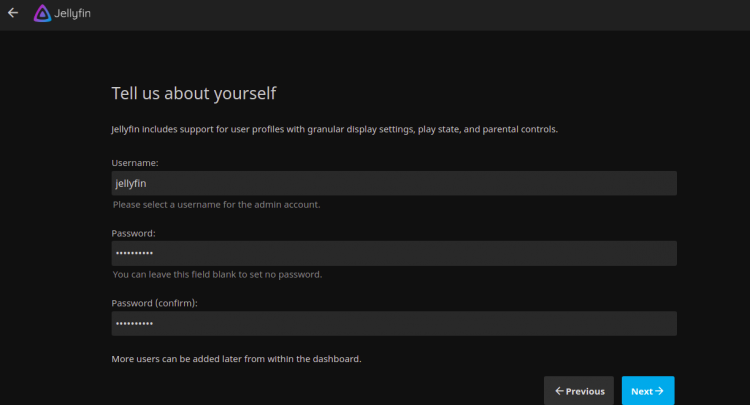
输入管理员用户名和密码,然后点击 Next 按钮。你将看到如下页面:
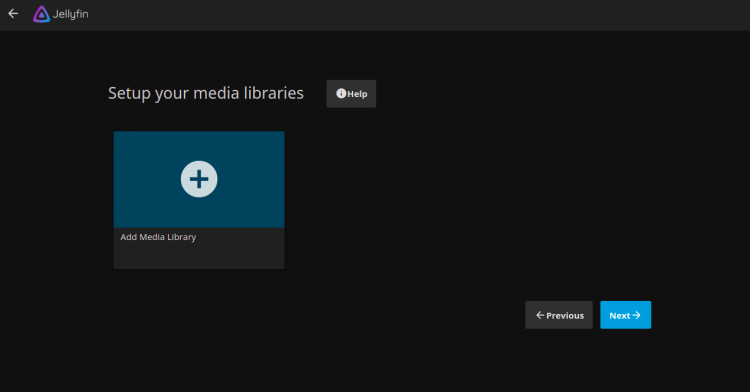
点击 Next 按钮。你将看到如下页面:
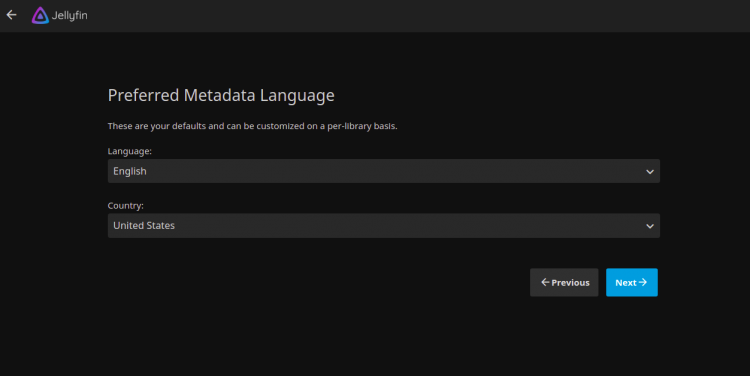
选择你的元数据语言,然后点击 Next 按钮。你将看到如下页面:
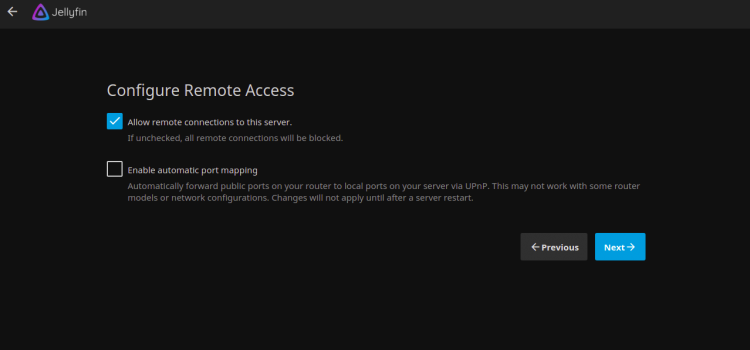
选择你偏好的选项,然后点击 Next 按钮。Jellyfin 安装完成后,你将看到如下页面:
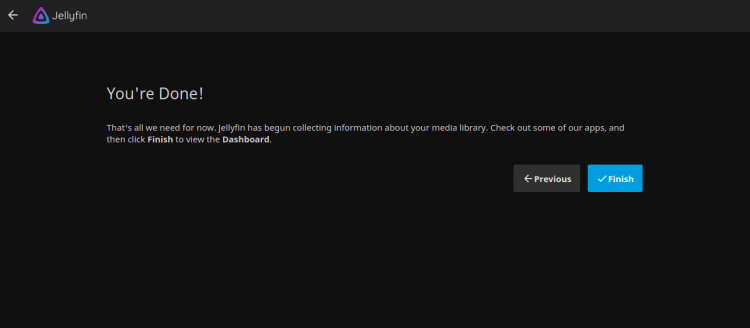
点击 Finish 按钮。你将被重定向到 Jellyfin 登录页面:
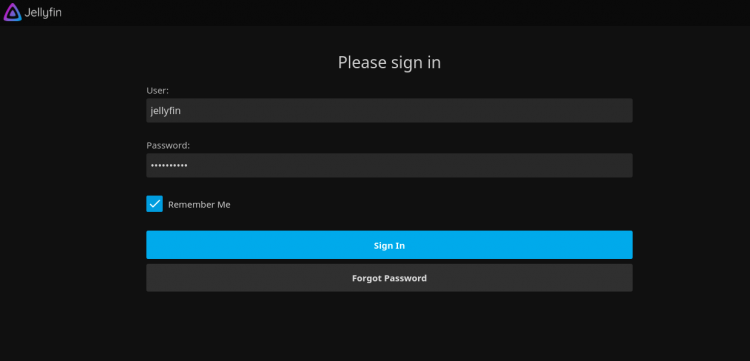
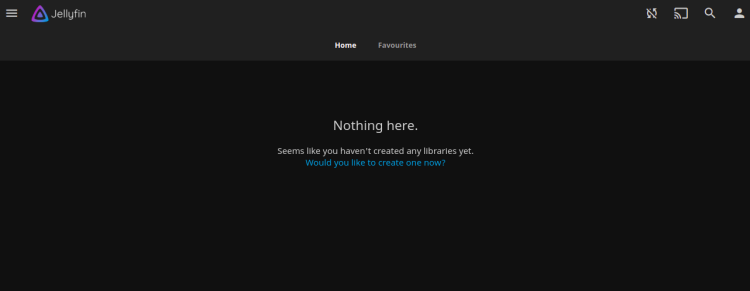
输入管理员用户名和密码,然后点击 Sign In 按钮。你将在下一页面看到 Jellyfin 仪表盘:
使用 Let's Encrypt 保护 Jellyfin
接下来,你需要安装 Certbot 客户端软件包,以便安装和管理 Let's Encrypt SSL。
首先,使用以下命令安装 Certbot:
apt-get install certbot python3-certbot-nginx -y安装完成后,运行以下命令为你的网站安装 Let's Encrypt SSL:
certbot --nginx -d jellyfin.example.com系统会要求你提供有效的电子邮件地址并接受服务条款,如下所示:
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator nginx, Installer nginx
Enter email address (used for urgent renewal and security notices) (Enter 'c' to
cancel):
[email protected]


- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at
https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf. You must
agree in order to register with the ACME server at
https://acme-v02.api.letsencrypt.org/directory
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(A)gree/(C)ancel: A

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing to share your email address with the Electronic Frontier
Foundation, a founding partner of the Let's Encrypt project and the non-profit
organization that develops Certbot? We'd like to send you email about our work
encrypting the web, EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: Y
Obtaining a new certificate
Performing the following challenges:
http-01 challenge for jellyfin.example.com
Waiting for verification...
Cleaning up challenges
Deploying Certificate to VirtualHost /etc/nginx/conf.d/jellyfin.conf
接下来,选择是否将 HTTP 流量重定向到 HTTPS,如下所示:
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
1: No redirect - Make no further changes to the webserver configuration.
2: Redirect - Make all requests redirect to secure HTTPS access. Choose this for
new sites, or if you're confident your site works on HTTPS. You can undo this
change by editing your web server's configuration.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Select the appropriate number [1-2] then [enter] (press 'c' to cancel): 2
输入 2 并按 Enter 键完成安装。你应该看到如下输出:
Redirecting all traffic on port 80 to ssl in /etc/nginx/conf.d/jellyfin.conf

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations! You have successfully enabled https://jellyfin.example.com

You should test your configuration at:
https://www.ssllabs.com/ssltest/analyze.html?d=jellyfin.example.com
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/jellyfin.example.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/jellyfin.example.com/privkey.pem
   Your cert will expire on 2022-05-07. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot again
   with the "certonly" option. To non-interactively renew *all* of
   your certificates, run "certbot renew"
 - Your account credentials have been saved in your Certbot
   configuration directory at /etc/letsencrypt. You should make a
   secure backup of this folder now. This configuration directory will
   also contain certificates and private keys obtained by Certbot so
   making regular backups of this folder is ideal.
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le

 - We were unable to subscribe you the EFF mailing list because your
   e-mail address appears to be invalid. You can try again later by
   visiting https://act.eff.org.
结语
恭喜!你已成功在 Debian 11 上安装了 Jellyfin,并配合 Nginx 与 Let's Encrypt SSL 使用。现在你可以开始上传媒体文件,并从移动设备串流播放了。