
本页内容
- 前置条件
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Nginx
- 步骤 3 - 安装 MariaDB
- 步骤 4 - 配置 MariaDB
- 步骤 5 - 安装 PHP 及其扩展
- 步骤 6 - 安装 SSL
- 步骤 7 - 下载 OpenEMR
- 步骤 8 - 安装 phpMyAdmin
- 步骤 9 - 配置 phpMyAdmin
- 步骤 10 - 配置 PHP-FPM
- 步骤 11 - 配置 Nginx
- 步骤 12 - 安装 OpenEMR
- 结语
OpenEMR 是一款开源的电子健康记录(EHR)和医疗诊所管理工具。它通过了国家卫生信息技术协调办公室(ONC)认证,具备集成健康记录、诊所管理、排程、电子账单、国际化、免费支持等诸多功能。它可以跟踪患者人口统计信息、安排患者就诊、维护包含实验室检查报告、用药和诊疗操作的详尽健康记录、跟踪处方、协助医疗账单处理、生成详细报告,并支持多语言。
在本教程中,你将学习如何在运行 Debian 12 的服务器上安装 OpenEMR 软件。
前置条件
- 一台运行 Debian 12 的服务器。
- 一个非 root 的 sudo 用户。
- 一个完整域名(FQDN),例如 openemr.example.com 。
- 确保所有内容都已更新。$ sudo apt update $ sudo apt upgrade
- 系统所需的一些软件包。$ sudo apt install wget curl nano ufw software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release debian-archive-keyring unzip -y 其中部分软件包可能已安装在你的系统上。
一台运行 Debian 12 的服务器。
一个非 root 的 sudo 用户。
一个完整域名(FQDN),例如 openemr.example.com 。
确保所有内容都已更新。
$ sudo apt update
$ sudo apt upgrade
系统所需的一些软件包。
$ sudo apt install wget curl nano ufw software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release debian-archive-keyring unzip -y
其中部分软件包可能已安装在你的系统上。
步骤 1 - 配置防火墙
第一步是配置防火墙。Debian 默认附带了 ufw(Uncomplicated Firewall,简易防火墙)。
检查防火墙是否正在运行。
$ sudo ufw status
你将看到如下输出。
Status: inactive
放行 SSH 端口,以免启用防火墙时断开当前连接。
$ sudo ufw allow OpenSSH
同时放行 HTTP 和 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
启用防火墙
$ sudo ufw enable
Command may disrupt existing ssh connections. Proceed with operation (y|n)? y
Firewall is active and enabled on system startup
再次检查防火墙状态。
$ sudo ufw status
你应该会看到类似的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
步骤 2 - 安装 Nginx
Debian 12 自带较旧版本的 Nginx。要安装最新版本,你需要添加官方的 Nginx 仓库。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
    | sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
添加 Nginx 稳定版仓库。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg] \
http://nginx.org/packages/debian `lsb_release -cs` nginx" \
    | sudo tee /etc/apt/sources.list.d/nginx.list
更新系统仓库。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。在 Debian 系统上,以下命令需要配合 sudo 才能运行。
$ sudo nginx -v
nginx version: nginx/1.24.0
启动 Nginx 服务。
$ sudo systemctl start nginx
检查服务状态。
? nginx.service - nginx - high performance web server
     Loaded: loaded (/lib/systemd/system/nginx.service; enabled; preset: enabled)
     Active: active (running) since Tue 2023-08-08 02:03:03 UTC; 5s ago
       Docs: https://nginx.org/en/docs/
    Process: 4929 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 4930 (nginx)
      Tasks: 2 (limit: 2315)
     Memory: 1.8M
        CPU: 12ms
     CGroup: /system.slice/nginx.service
             ??4930 "nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf"
             ??4931 "nginx: worker process"
步骤 3 - 安装 MariaDB
Debian 12 默认不附带 MySQL,且官方也尚未发布对应的软件包。因此,我们将使用 MariaDB 作为替代。MariaDB 同样没有针对 Debian 12 的官方软件包,但 Debian 自带该软件。因此,请使用以下命令进行安装。
$ sudo apt install mariadb-server
检查 MySQL 的版本。
$ mysql --version
mysql  Ver 15.1 Distrib 10.11.3-MariaDB, for debian-linux-gnu (x86_64) using  EditLine wrapper
运行 MariaDB 安全安装脚本。
$ sudo mysql_secure_installation
系统会提示输入 root 密码。直接按回车键,因为我们尚未为其设置任何密码。
NOTE: RUNNING ALL PARTS OF THIS SCRIPT IS RECOMMENDED FOR ALL MariaDB
      SERVERS IN PRODUCTION USE!  PLEASE READ EACH STEP CAREFULLY!

In order to log into MariaDB to secure it, we'll need the current
password for the root user. If you've just installed MariaDB, and
haven't set the root password yet, you should just press enter here.

Enter current password for root (enter for none):
接下来,系统会询问是否切换到 Unix socket 认证方式。unix_socket 插件允许你使用操作系统的凭据连接 MariaDB 服务器。由于你已拥有一个受保护的 root 账户,请输入 n 继续。
OK, successfully used password, moving on...

Setting the root password or using the unix_socket ensures that nobody
can log into the MariaDB root user without the proper authorisation.

You already have your root account protected, so you can safely answer 'n'.

Switch to unix_socket authentication [Y/n] n
接下来,系统会询问是否要更改 root 密码。在 Debian 12 中,root 密码与自动化系统维护紧密关联,因此不应修改。输入 n 继续。
 ... skipping.

You already have your root account protected, so you can safely answer 'n'.

Change the root password? [Y/n] n
接下来,系统会提出一些问题以增强 MariaDB 的安全性。输入 Y 以删除匿名用户、禁止 root 远程登录、移除测试数据库并重新加载权限表。
 ... skipping.

By default, a MariaDB installation has an anonymous user, allowing anyone
to log into MariaDB without having to have a user account created for
them.  This is intended only for testing, and to make the installation
go a bit smoother.  You should remove them before moving into a
production environment.

Remove anonymous users? [Y/n] y
 ... Success!

Normally, root should only be allowed to connect from 'localhost'.  This
ensures that someone cannot guess at the root password from the network.

Disallow root login remotely? [Y/n] y
 ... Success!

By default, MariaDB comes with a database named 'test' that anyone can
access.  This is also intended only for testing, and should be removed
before moving into a production environment.

Remove test database and access to it? [Y/n] y
 - Dropping test database...
 ... Success!
 - Removing privileges on test database...
 ... Success!

Reloading the privilege tables will ensure that all changes made so far
will take effect immediately.

Reload privilege tables now? [Y/n] y
 ... Success!

Cleaning up...

All done!  If you've completed all of the above steps, your MariaDB
installation should now be secure.

Thanks for using MariaDB!
你可以在命令行中输入 sudo mysql 或 sudo mariadb 进入 MariaDB shell。
步骤 4 - 配置 MariaDB
登录到 MariaDB shell。
$ sudo mysql
创建 OpenEMR 数据库。
mysql> CREATE DATABASE openemr;
创建 OpenEMR 用户账户。
mysql> CREATE USER 'openemruser'@'localhost' IDENTIFIED BY 'Your_password2!';
将该数据库的所有权限授予该用户。
mysql> GRANT ALL PRIVILEGES ON openemr.* TO 'openemruser'@'localhost';
由于我们不会修改 root 用户,你应该创建另一个使用密码认证、用于执行管理任务的 SQL 用户。请为其设置一个强密码。
MariaDB> GRANT ALL ON *.* TO 'navjot'@'localhost' IDENTIFIED BY 'Yourpassword32!' WITH GRANT OPTION;
刷新用户权限。
mysql> FLUSH PRIVILEGES;
退出 shell。
mysql> exit
步骤 5 - 安装 PHP 及其扩展
Debian 12 默认自带 PHP 8.2。你可以通过运行以下命令进行安装。
$ sudo apt install php-fpm php-mysql php-bcmath php-xml php-zip php-curl php-mbstring php-gd php-tidy php-intl php-cli php-soap imagemagick libtiff-tools php-ldap
若想始终使用最新版本的 PHP,或需要安装多个 PHP 版本,请添加 Ondrej 的 PHP 仓库。
首先,导入 Sury 仓库的 PHP GPG 密钥。
$ sudo curl -sSLo /usr/share/keyrings/deb.sury.org-php.gpg https://packages.sury.org/php/apt.gpg
添加 Ondrej Sury 的 PHP 仓库。
$ sudo sh -c 'echo "deb [signed-by=/usr/share/keyrings/deb.sury.org-php.gpg] https://packages.sury.org/php/ $(lsb_release -sc) main" > /etc/apt/sources.list.d/php.list'
更新系统仓库列表。
$ sudo apt update
接下来,安装 OpenEMR 所需的 PHP 及其扩展。
$ sudo apt install php8.2-fpm php8.2-mysql php8.2-bcmath php8.2-xml php8.2-zip php8.2-curl php8.2-mbstring php8.2-gd php8.2-tidy php8.2-intl php8.2-cli php8.2-soap imagemagick libtiff-tools php8.2-ldap
验证安装。
$ php --version
PHP 8.2.8 (cli) (built: Jul 16 2023 11:00:43) (NTS)
Copyright (c) The PHP Group
Zend Engine v4.2.8, Copyright (c) Zend Technologies
    with Zend OPcache v8.2.8, Copyright (c), by Zend Technologies
步骤 6 - 安装 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Debian 自带的仓库安装 Certbot,也可以通过 Snapd 工具获取最新版本。本教程将使用 Snapd 版本。
Debian 12 默认未安装 Snapd。请安装 Snapd 软件包。
$ sudo apt install snapd
运行以下命令,确保你的 Snapd 版本是最新的。
$ sudo snap install core && sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可被直接执行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
验证 Certbot 是否正常工作。
$ certbot --version
certbot 2.6.0
运行以下命令生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d openemr.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/openemr.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
你会发现 snap.certbot.renew.service 是已计划运行的服务之一。
NEXT                        LEFT          LAST                        PASSED    UNIT                      ACTIVATES
.....
Tue 2023-08-08 03:09:00 UTC 23min left    Tue 2023-08-08 02:39:00 UTC 6min ago  phpsessionclean.timer        phpsessionclean.service
Tue 2023-08-08 04:21:00 UTC 1h 35min left -                           -         snap.certbot.renew.timer     snap.certbot.renew.service
Tue 2023-08-08 06:25:00 UTC 3h 39min left Mon 2023-08-07 13:54:08 UTC 12h ago   ntpsec-rotate-stats.timer    ntpsec-rotate-stats.service
对该过程进行一次空运行,检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果未出现错误,说明一切就绪。你的证书将自动续期。
步骤 7 - 下载 OpenEMR
访问 OpenEMR 下载页面,获取最新版本 OpenEMR 的下载链接。将 OpenEMR 下载到服务器。
$ wget https://sourceforge.net/projects/openemr/files/OpenEMR%20Current/7.0.1/openemr-7.0.1.tar.gz
解压文件。
$ tar -pxzf openemr-7.0.1.tar.gz
创建 /var/www/html 目录。
$ sudo mkdir /var/www/html -p
将解压后的文件移动到 Web 目录。
$ sudo mv openemr-7.0.1 /var/www/html/openemr
将 Web 根目录的权限授予 Nginx 用户。
$ sudo chown -R nginx:nginx /var/www/html/openemr
步骤 8 - 安装 phpMyAdmin
在配置 PHP-FPM 之前,我们先安装 phpMyAdmin,你可以用它来浏览和编辑数据库。
下载英文版的 phpMyAdmin 压缩包。从 phpMyAdmin 下载页面获取最新版本的链接。
$ wget https://files.phpmyadmin.net/phpMyAdmin/5.2.1/phpMyAdmin-5.2.1-english.tar.gz
将压缩包解压到公共目录。
$ sudo tar -xzf phpMyAdmin-5.2.1-english.tar.gz -C /var/www/html/openemr
切换到公共目录。
$ cd /var/www/html/openemr
将解压后的目录重命名为一个不易猜到的名称,以提高安全性。
$ sudo mv phpMyAdmin-5.2.1-english sm175
步骤 9 - 配置 phpMyAdmin
复制示例配置文件。
$ sudo cp sm175/config.sample.inc.php sm175/config.inc.php
打开配置文件进行编辑。
$ sudo nano sm175/config.inc.php
找到 $cfg['blowfish_secret'] = ''; 这一行,并填入一个 32 位的随机字符串,用于基于 Cookie 的认证。
你可以使用 phpSolved 的在线 blowfish 生成器,或者通过命令行来完成。
复制该值,并按示例粘贴。
$cfg['blowfish_secret'] = 'Tc/HfLPBOAPxJ-rhQP}HJoZEK69c3j:m';
按下 Ctrl + X 保存文件,并在提示时输入 Y。
将 phpMyAdmin 目录的所有权更改为 Nginx 服务。
$ sudo chown -R nginx:nginx /var/www/html/openemr/sm175
删除 phpMyAdmin 安装目录。
$ sudo rm -rf /var/www/html/openemr/sm175/setup
步骤 10 - 配置 PHP-FPM
打开文件 /etc/php/8.2/fpm/pool.d/www.conf 。
$ sudo nano /etc/php/8.2/fpm/pool.d/www.conf
我们需要将 PHP 进程的 Unix 用户/组设置为 nginx 。找到文件中的 user=www-data 和 group=www-data 行,并将它们改为 nginx 。
; Unix user/group of the child processes. This can be used only if the master
; process running user is root. It is set after the child process is created.
; The user and group can be specified either by their name or by their numeric
; IDs.
; Note: If the user is root, the executable needs to be started with
;       --allow-to-run-as-root option to work.
; Default Values: The user is set to master process running user by default.
;                 If the group is not set, the user's group is used.
user = nginx
group = nginx
...
找到文件中的 listen.owner = www-data 和 listen.group = www-data 行,并将它们改为 nginx 。
; Set permissions for unix socket, if one is used. In Linux, read/write
; permissions must be set in order to allow connections from a web server. Many
; BSD-derived systems allow connections regardless of permissions. The owner
; and group can be specified either by name or by their numeric IDs.
; Default Values: Owner is set to the master process running user. If the group
;                 is not set, the owner's group is used. Mode is set to 0660.
listen.owner = nginx
listen.group = nginx
按下 Ctrl + X 保存文件,并在提示时输入 Y。
将 PHP-FPM 和 PHP-CLI 的执行时间延长至 60 秒。
$ sudo sed -i 's/max_execution_time = 30/max_execution_time = 60/' /etc/php/8.2/fpm/php.ini
将变量 max_input_time 的值设置为 1 。
$ sudo sed -i 's/max_input_time = 60/max_input_time = -1/' /etc/php/8.2/fpm/php.ini
将 PHP-FPM 的内存限制从 128MB 提高到 512MB。
$ sudo sed -i 's/memory_limit = 128M/memory_limit = 512M/' /etc/php/8.2/fpm/php.ini
将文件上传大小上限提高到 30MB。
$ sudo sed -i 's/post_max_size = 8M/post_max_size = 30M/' /etc/php/8.2/fpm/php.ini
$ sudo sed -i 's/upload_max_filesize = 2M/upload_max_filesize = 30M/' /etc/php/8.2/fpm/php.ini
将最大输入变量数量提高到 3000。
$ sudo sed -i 's/;max_input_vars = 1000/max_input_vars = 3000/g' /etc/php/8.2/fpm/php.ini
允许从 PHP 的角度,通过 LOAD DATA 语句访问本地文件。
$ sudo sed -i 's/;mysqli.allow_local_infile = On/mysqli.allow_local_infile = On/g' /etc/php/8.2/fpm/php.ini
重启 PHP-FPM 服务。
$ sudo systemctl restart php8.2-fpm
将 PHP 会话目录的所属组更改为 Nginx。
$ sudo chgrp -R nginx /var/lib/php/sessions
步骤 11 - 配置 Nginx
创建并打开文件 /etc/nginx/conf.d/openemr.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/openemr.conf
在其中粘贴以下代码。
server {
    listen       443 ssl http2;
    listen       [::]:443 ssl http2;
    server_name  openemr.example.com;

    access_log  /var/log/nginx/openemr.access.log;
    error_log   /var/log/nginx/openemr.error.log;

    # SSL
    ssl_certificate         /etc/letsencrypt/live/openemr.example.com/fullchain.pem;
    ssl_certificate_key     /etc/letsencrypt/live/openemr.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/openemr.example.com/chain.pem;
    ssl_session_timeout  1d;
    ssl_session_cache shared:SSL:50m;
    ssl_session_tickets off;
    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;
    # use https://blog.cloudflare.com/announcing-1111 Cloudfare+Apnic labs, It is free and secure
    resolver 1.1.1.1 1.0.0.1 [2606:4700:4700::1111] [2606:4700:4700::1001] valid=300s;

    root /var/www/html/openemr;

    index index.php;

    location / {
        try_files $uri $uri/ /index.php;
    }

    # Pass PHP Scripts To FastCGI Server
    location ~* \.php$ {
        try_files $uri =404;
        fastcgi_index  index.php;
        fastcgi_pass unix:/run/php-fpm/www.sock; # Depends On The PHP Version
        fastcgi_param SCRIPT_FILENAME  $realpath_root$fastcgi_script_name;
        fastcgi_param DOCUMENT_ROOT $realpath_root;
        include fastcgi_params;
    }

    # deny access to writable files/directories
    location ~* ^/sites/*/(documents|edi|era) {
        deny all;
        return 404;
    }

    # deny access to certain directories
    location ~* ^/(contrib|tests) {
	    deny all;
        return 404;
    }

    # Alternatively all access to these files can be denied
    location ~* ^/(admin|setup|acl_setup|acl_upgrade|sl_convert|sql_upgrade|gacl/setup|ippf_upgrade|sql_patch)\.php {
        deny all;
        return 404;
    }

    location = /favicon.ico {
        log_not_found off;
        access_log off;
    }

    location = /robots.txt  {
        log_not_found off;
        access_log off;
    }

    location ~ /\. {
        deny all;
    }
}

# enforce HTTPS
server {
    listen       80;
    listen       [::]:80;
    server_name  openemr.example.com;
    return 301   https://$host$request_uri;
}
注意,Nginx 配置中使用的根目录是 /var/www/html/wallabag/public/ 。
完成后按下 Ctrl + X 保存文件,并在提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下内容。
server_names_hash_bucket_size 64;
按下 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
步骤 12 - 安装 OpenEMR
在浏览器中打开 URL https://openemr.example.com ,你将看到如下安装设置界面。
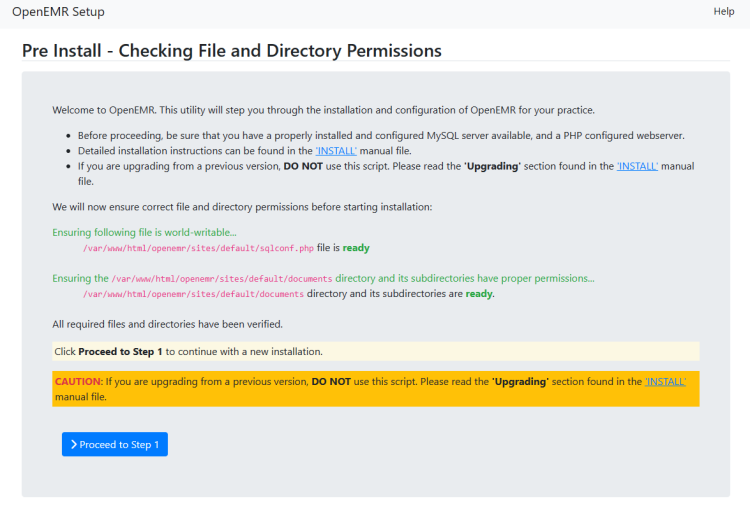
此步骤会检查文件权限,并确认你是否可以继续进行第 1 步。如果看到绿色的 ready 字样,说明可以继续。点击蓝色按钮进入第 1 步。
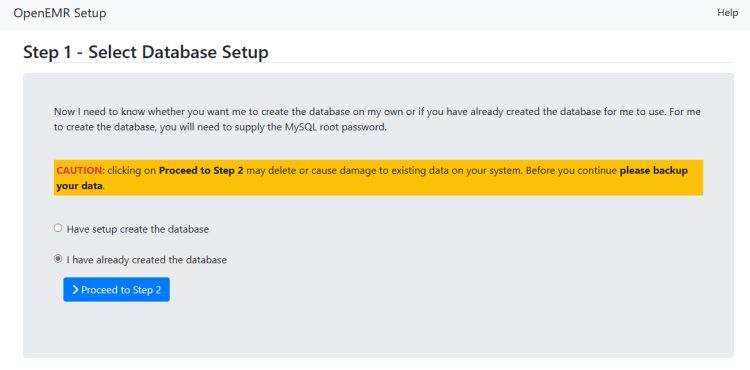
在下一页,系统会询问是由安装程序创建数据库,还是使用已创建的数据库。选择「I have already created the database(我已创建数据库)」选项,然后点击按钮进入第 2 步。
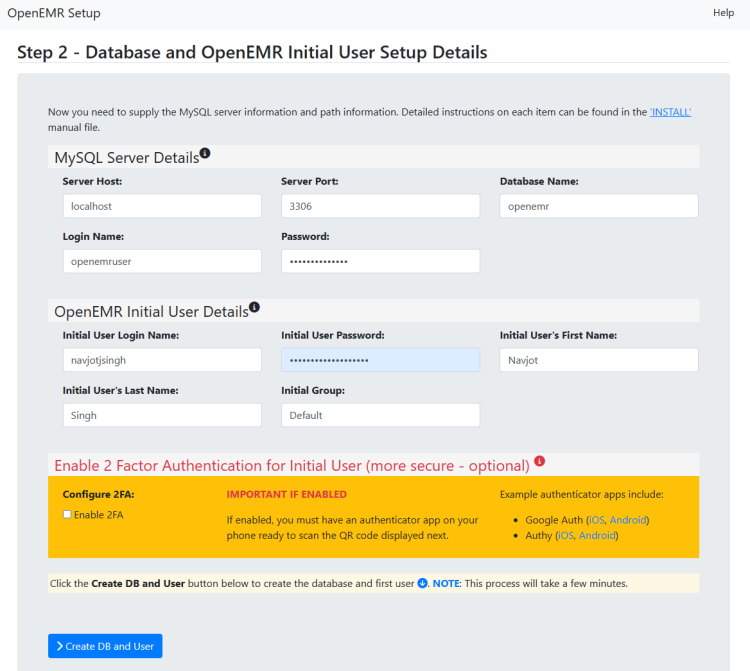
在下一页,填写你在第 4 步中配置的数据库凭据。同时,输入你的管理员账户凭据。请确保用户名长度不少于 12 个字符,否则会出现错误。你可以在此处启用双因素认证(2FA),但建议安装完成后再进行配置。点击按钮以创建数据库和用户账户。
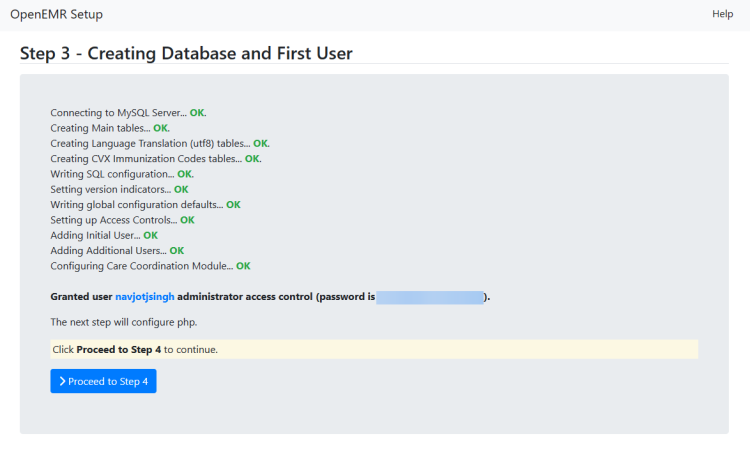
下一页将显示安装状态,并展示用户名和密码。点击按钮进入第 4 步。
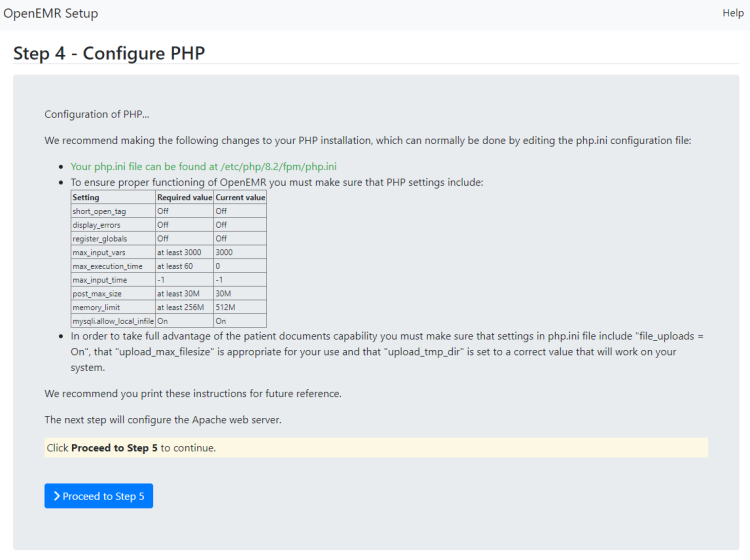
下一页会列出 php.ini 文件中的推荐值和当前值。请确保当前值满足要求。由于某些原因,即使你已正确设置,安装程序对变量 max_execution_time 仍可能显示错误的值,你可以忽略这一点。你可以使用以下命令验证当前值。

确认无误后,点击按钮进入第 5 步。
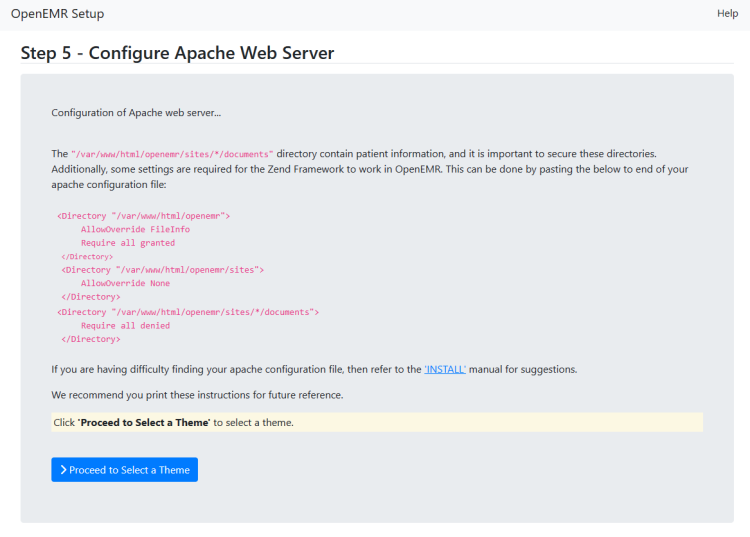
下一步列出的是 Apache 服务器设置,由于我们使用的是 Nginx 服务器,可以忽略。点击按钮进入下一页。
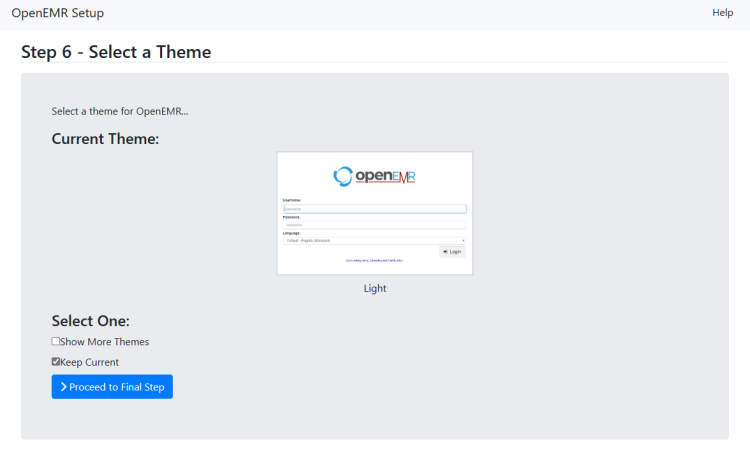
此处会要求你为管理面板选择主题。选择「Keep Current(保持当前)」选项并点击按钮继续。你可以稍后在管理面板中更改主题,但届时无法预览其外观。如果从安装程序页面选择,你可以在选定前先预览效果。我们将沿用默认主题。
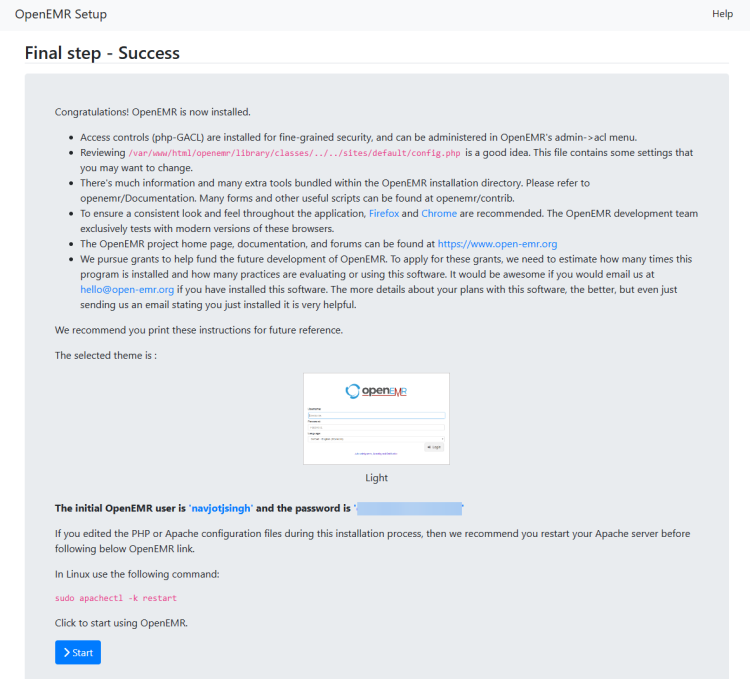
最后一页列出了一些关于软件和账户凭据的最终说明。点击 Start 按钮打开登录页面。
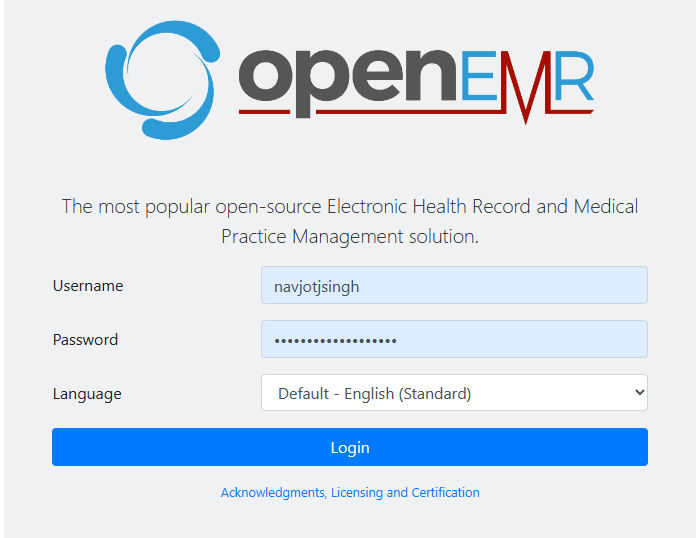
你会看到一个 OpenEMR 注册弹窗,用于接收其网站的公告。你可以忽略它,直接输入凭据并点击 Login 按钮进入仪表盘。
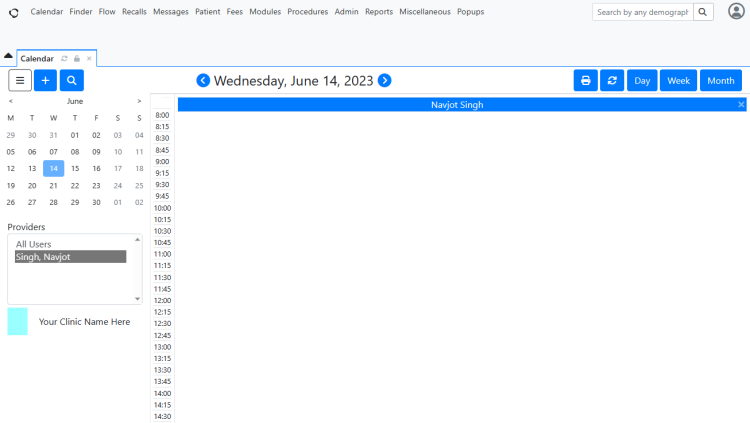
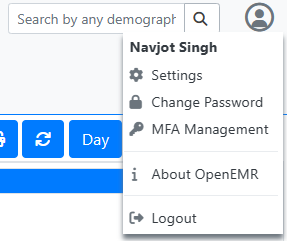
如果你在安装过程中未配置双因素认证,可以点击右上角的头像图标,并选择 MFA Management(多因素认证管理)选项进行设置。
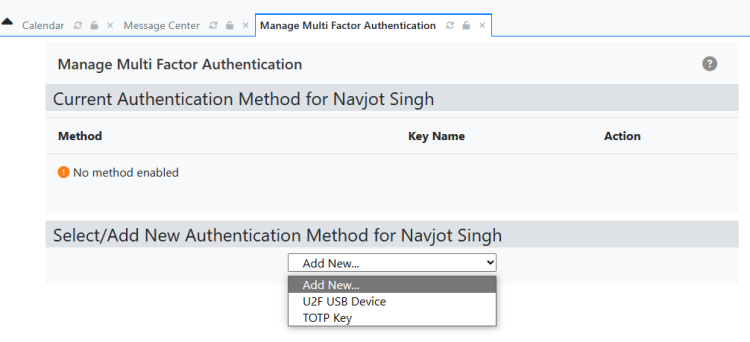
在下一页,从下拉菜单中选择认证方式并开始配置。
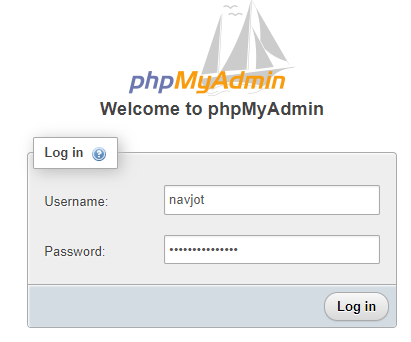
从此刻起,你就可以开始使用 OpenEMR 来管理你的医疗业务了。要访问 phpMyAdmin,请在浏览器中打开 URL https://openemr.example.com/sm175/ 。你可以使用 OpenEMR 数据库凭据,或第 4 步中创建的具有 root 权限的用户登录 phpMyAdmin。
结语
至此,关于在 Debian 12 服务器上安装 OpenEMR 的教程就结束了。如果你有任何问题,请在下方评论区留言。