
本页内容
- 准备工作
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Nginx
- 步骤 3 - 安装 PHP 及其扩展
- 步骤 4 - 安装 MySQL
- 步骤 5 - 配置 MySQL
- 步骤 6 - 安装 SSL
- 步骤 7 - 下载 SuiteCRM
- 步骤 8 - 配置 SELinux
- 步骤 9 - 配置 Nginx 和 PHP / 配置 PHP-FPM / 配置 Nginx
- 步骤 10 - 安装并访问 SuiteCRM / 方法 1 - Web 向导 / 方法 2 - SuiteCRM 命令控制台
- 步骤 11 - 配置 Cron 任务
- 总结
- 配置 PHP-FPM
- 配置 Nginx
- 方法 1 - Web 向导
- 方法 2 - SuiteCRM 命令控制台
SuiteCRM 是一款使用 PHP 编写的开源客户关系管理(CRM)解决方案。它是在 SugarCRM 停止发布社区版之后,由流行的 SugarCRM 软件分叉(fork)而来。它用于创建所有客户数据的中央存储库,以获取可用于增强和维系业务关系的洞察。
其部分功能包括文档存储、电子邮件营销、日历、社交媒体集成、区域管理、细分、营销自动化、销售线索资格审核、内部聊天集成、客户支持、社交 CRM、销售队伍自动化、营销活动、移动 CRM 和报表。它可以与 Mandrill、SendGrid、Amazon SES 等第三方 SMTP 中继服务集成。您可以安装插件来扩展 SuiteCRM 的功能。它还可以与 Mautic、Facebook、Twitter、MailChimp、Zoom、Quickbooks、DocuSign 等第三方应用集成。
在本文中,您将学习如何在 Rocky Linux 9 服务器上使用 Nginx Web 服务器和 Let's Encrypt SSL 安装 SuiteCRM。
准备工作
- 一台运行 Rocky Linux 9 的服务器。
- 一个拥有 sudo 权限的非 root 用户。
- 一个完整的域名(FQDN),例如 suitecrm.example.com 。
- 确保系统已更新。$ sudo dnf update
- 系统所需的少量软件包。$ sudo dnf install wget curl nano unzip yum-utils policycoreutils-python-utils -y 其中部分软件包可能已经安装在您的系统上。
一台运行 Rocky Linux 9 的服务器。
一个拥有 sudo 权限的非 root 用户。
一个完整的域名(FQDN),例如 suitecrm.example.com 。
确保系统已更新。
$ sudo dnf update
系统所需的少量软件包。
$ sudo dnf install wget curl nano unzip yum-utils policycoreutils-python-utils -y
其中部分软件包可能已经安装在您的系统上。
步骤 1 - 配置防火墙
第一步是配置防火墙。Rocky Linux 使用 Firewalld 防火墙。请检查防火墙的状态。
$ sudo firewall-cmd --state
running
防火墙使用不同的区域(zone)工作,public 区域是我们将使用的默认区域。列出防火墙上所有已激活的服务和端口。
$ sudo firewall-cmd --permanent --list-services
它应显示如下输出。
cockpit dhcpv6-client ssh
SuiteCRM 需要 HTTP 和 HTTPS 端口才能运行。请开放这些端口。
$ sudo firewall-cmd --permanent --add-service=http
$ sudo firewall-cmd --permanent --add-service=https
重新加载防火墙以应用更改。
$ sudo firewall-cmd --reload
再次列出所有服务。
$ sudo firewall-cmd --permanent --list-services
您应得到如下输出。
cockpit dhcpv6-client http https ssh
步骤 2 - 安装 Nginx
Rocky Linux 9 自带较旧版本的 Nginx。您需要下载官方 Nginx 软件仓库以安装最新版本。
创建并打开 /etc/yum.repos.d/nginx.repo 文件以创建官方 Nginx 软件仓库。
$ sudo nano /etc/yum.repos.d/nginx.repo
将以下代码粘贴到其中。
[nginx-stable]
name=nginx stable repo
baseurl=http://nginx.org/packages/centos/$releasever/$basearch/
gpgcheck=1
enabled=1
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true

[nginx-mainline]
name=nginx mainline repo
baseurl=http://nginx.org/packages/mainline/centos/$releasever/$basearch/
gpgcheck=1
enabled=0
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true
按下 Ctrl + X 保存文件,并在提示时输入 Y。
安装 Nginx 服务器。
$ sudo dnf install -y nginx
验证安装。
$ nginx -v
nginx version: nginx/1.24.0
启用并启动 Nginx 服务器。
$ sudo systemctl enable nginx --now
检查服务器的状态。
$ sudo systemctl status nginx
? nginx.service - nginx - high performance web server
     Loaded: loaded (/usr/lib/systemd/system/nginx.service; enabled; preset: disabled)
    Drop-In: /usr/lib/systemd/system/nginx.service.d
             ??php-fpm.conf
     Active: active (running) since Thu 2023-05-18 22:32:50 UTC; 4s ago
       Docs: http://nginx.org/en/docs/
    Process: 3955 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 3957 (nginx)
      Tasks: 2 (limit: 5922)
     Memory: 2.1M
        CPU: 6ms
     CGroup: /system.slice/nginx.service
             ??3957 "nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf"
             ??3958 "nginx: worker process"
步骤 3 - 安装 PHP 及其扩展
我们需要安装 PHP 8.1 以使 SuiteCRM 正常运行。第一步是获取 Epel 软件仓库。
$ sudo dnf install epel-release -y
接下来,安装 Remi 软件仓库。
$ sudo dnf install https://rpms.remirepo.net/enterprise/remi-release-9.rpm
检查可用的 PHP 软件流(stream)。
$ dnf module list php -y
Name                                   Stream                   Profiles                                        Summary
php                                    8.1                      common [d], devel, minimal                      PHP scripting language

Remi's Modular repository for Enterprise Linux 9 - x86_64
Name                                   Stream                   Profiles                                        Summary
php                                    remi-7.4                 common [d], devel, minimal                      PHP scripting language
php                                    remi-8.0                 common [d], devel, minimal                      PHP scripting language
php                                    remi-8.1                 common [d], devel, minimal                      PHP scripting language
php                                    remi-8.2                 common [d], devel, minimal                      PHP scripting language

Hint: [d]efault, [e]nabled, [x]disabled, [i]nstalled
默认版本是 8.1。启用 Remi 的 PHP 8.1 软件仓库。
$ sudo dnf module reset php -y
$ sudo dnf module enable php:remi-8.1
安装 SuiteCRM 所需的 PHP 及必需扩展。
$ sudo dnf install -y php-fpm php-mysql php-bcmath php-xml php-zip php-curl php-mbstring php-gd php-tidy php-intl php-cli php-opcache php-soap php-imap php-ldap
验证安装。
$ php --version
PHP 8.1.19 (cli) (built: May 10 2023 13:43:03) (NTS gcc x86_64)
Copyright (c) The PHP Group
Zend Engine v4.1.19, Copyright (c) Zend Technologies
    with Zend OPcache v8.1.19, Copyright (c), by Zend Technologies
启用并启动 PHP-FPM 服务。
$ sudo systemctl enable php-fpm --now
步骤 4 - 安装 MySQL
Rocky Linux 9 自带最新版本的 MySQL。您可以使用一条命令安装它。
$ sudo dnf install mysql-server
检查 MySQL 的版本。
$ mysql --version
mysql  Ver 8.0.32 for Linux on x86_64 (Source distribution)
启用并启动 MySQL 服务。
$ sudo systemctl enable mysqld --now
运行 MySQL 安全安装脚本。
$ sudo mysql_secure_installation
系统会询问您是否安装 Validate Password Component(密码验证组件)。它用于检查 MySQL 中所用密码的强度。按下 Y 进行安装。接下来,系统会询问您设置密码验证策略的级别。选择 2,因为它是最严格的级别。
Securing the MySQL server deployment.

Connecting to MySQL using a blank password.

VALIDATE PASSWORD COMPONENT can be used to test passwords
and improve security. It checks the strength of password
and allows the users to set only those passwords which are
secure enough. Would you like to setup VALIDATE PASSWORD component?

Press y|Y for Yes, any other key for No: Y

There are three levels of password validation policy:

LOW    Length >= 8
MEDIUM Length >= 8, numeric, mixed case, and special characters
STRONG Length >= 8, numeric, mixed case, special characters and dictionary                  file

Please enter 0 = LOW, 1 = MEDIUM and 2 = STRONG: 2
接下来,系统会要求您设置一个新的 root 密码。请根据上述要求输入密码。在提示时输入 Y 以继续使用所选的 root 密码。
Please set the password for root here.

New password:

Re-enter new password:

Estimated strength of the password: 100
Do you wish to continue with the password provided?(Press y|Y for Yes, any other key for No) : Y
接下来,输入 Y 以删除匿名用户、禁止 root 远程登录、删除测试数据库并重新加载权限表。
By default, a MySQL installation has an anonymous user,
allowing anyone to log into MySQL without having to have
a user account created for them. This is intended only for
testing, and to make the installation go a bit smoother.
You should remove them before moving into a production
environment.

Remove anonymous users? (Press y|Y for Yes, any other key for No) : Y
Success.


Normally, root should only be allowed to connect from
'localhost'. This ensures that someone cannot guess at
the root password from the network.

Disallow root login remotely? (Press y|Y for Yes, any other key for No) : Y
Success.

By default, MySQL comes with a database named 'test' that
anyone can access. This is also intended only for testing,
and should be removed before moving into a production
environment.


Remove test database and access to it? (Press y|Y for Yes, any other key for No) : Y
 - Dropping test database...
Success.

 - Removing privileges on test database...
Success.

Reloading the privilege tables will ensure that all changes
made so far will take effect immediately.

Reload privilege tables now? (Press y|Y for Yes, any other key for No) : Y
Success.

All done!
步骤 5 - 配置 MySQL
登录到 MySQL shell。在提示时输入您的 root 密码。
$ sudo mysql -u root -p
创建一个示例数据库。
mysql> CREATE DATABASE suitecrm;
创建一个 SQL 用户账户。
mysql> CREATE USER 'suiteuser'@'localhost' IDENTIFIED BY 'Your_password2';
将该数据库的所有权限授予该用户。
mysql> GRANT ALL PRIVILEGES ON suitecrm.* TO 'suiteuser'@'localhost';
刷新用户权限。
mysql> FLUSH PRIVILEGES;
退出 shell。
mysql> exit
步骤 6 - 安装 SSL
我们需要安装 Certbot 以生成 SSL 证书。
为此我们将使用 Snapd 软件包安装器。由于 Rocky Linux 默认未附带它,请安装 Snapd 安装器。它需要 EPEL 软件仓库才能工作,而我们在安装 PHP 之前已经安装了该仓库,因此可以跳过这一步。
安装 Snapd。
$ sudo dnf install -y snapd
启用并启动 Snap 服务。
$ sudo systemctl enable snapd --now
安装 Snap core 软件包,并确保您的 Snapd 版本是最新的。
$ sudo snap install core && sudo snap refresh core
为 Snapd 创建必要的链接。
$ sudo ln -s /var/lib/snapd/snap /snap
$ echo 'export PATH=$PATH:/var/lib/snapd/snap/bin' | sudo tee -a /etc/profile.d/snapd.sh
执行以下命令以安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保可以运行 Certbot 命令。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
验证安装。
$ certbot --version
certbot 2.6.0
运行以下命令以生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d suitecrm.example.com
上述命令会将证书下载到您服务器上的 /etc/letsencrypt/live/suitecrm.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
您会发现 snap.certbot.renew.service 是计划运行的服务之一。
NEXT                        LEFT          LAST                        PASSED        UNIT                      ACTIVATES
.....
Sun 2023-05-21 06:32:00 UTC 9h left       Sat 2023-05-21 18:04:05 UTC 2h 59min ago  snap.certbot.renew.timer  snap.certbot.renew.service
Sun 2023-05-21 06:43:20 UTC 9h left       Sat 2023-05-21 10:49:23 UTC 10h ago       apt-daily-upgrade.timer   apt-daily-upgrade.service
Sun 2023-05-21 09:00:06 UTC 11h left      Sat 2023-05-21 20:58:06 UTC 5min ago      apt-daily.timer           apt-daily.service
进行一次试运行,检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果没有看到错误,说明一切就绪。您的证书将自动续期。
步骤 7 - 下载 SuiteCRM
为 SuiteCRM 创建 Web 根目录。
$ sudo mkdir /var/www/html/suitecrm -p
切换到 Web 根目录。
$ cd /var/www/html/suitecrm
下载 SuiteCRM 8.x 版本。请从 SuiteCRM 下载页面获取最新版本的链接 。
$ sudo wget https://suitecrm.com/download/140/suite83/562304/suitecrm-8-3-0.zip
解压归档文件中的内容。
$ sudo unzip -q suitecrm*.*
删除 zip 文件。
$ sudo rm suitecrm-8-3-0.zip
将正确的文件权限和所有者设置为 Nginx 用户。同时,将 bin/console 文件设置为可执行,以便运行 SuiteCRM 控制台。
$ sudo find . -type d -not -perm 2755 -exec chmod 2755 {} \;
$ sudo find . -type f -not -perm 0644 -exec chmod 0644 {} \;
$ sudo find . ! -user nginx -exec chown nginx:nginx {} \;
$ sudo chmod +x bin/console
步骤 8 - 配置 SELinux
更改 SuiteCRM 的文件安全上下文。
$ sudo semanage fcontext -a -t httpd_sys_rw_content_t "/var/www/html/suitecrm(/.*)?"
应用该策略。
$ sudo restorecon -Rv /var/www/html/suitecrm/
应用该策略以允许 Nginx 访问 MySQL。
$ sudo setsebool -P httpd_can_network_connect_db 1
应用该策略以允许与外部主机建立连接。发送电子邮件需要此项设置。
$ sudo setsebool -P httpd_can_network_connect 1
步骤 9 - 配置 Nginx 和 PHP
配置 PHP-FPM
打开文件 /etc/php-fpm.d/www.conf 。
$ sudo nano /etc/php-fpm.d/www.conf
我们需要将 PHP 进程的 Unix 用户/组设置为 nginx 。在文件中找到 user=www-data 和 group=www-data 两行,并将其改为 nginx 。
...
; Unix user/group of processes
; Note: The user is mandatory. If the group is not set, the default user's group
;       will be used.
; RPM: apache user chosen to provide access to the same directories as httpd
user = nginx
; RPM: Keep a group allowed to write in log dir.
group = nginx
...
接下来,取消注释 socket 文件所有者、组以及默认权限那一行,并按如下所示进行修改。
; Set permissions for unix socket, if one is used. In Linux, read/write
; permissions must be set in order to allow connections from a web server.
; Default Values: user and group are set as the running user
;                 mode is set to 0660
listen.owner = nginx
listen.group = nginx
listen.mode = 0660
接下来,在该行前面加上分号将其注释掉,如下所示。
;listen.acl_users = apache,nginx
按下 Ctrl + X 保存文件,并在提示时输入 Y。
将 PHP-FPM 和 PHP-CLI 的执行时间延长至 60 秒。
$ sudo sed -i 's/max_execution_time = 30/max_execution_time = 60/' /etc/php.ini
将 PHP-FPM 的内存限制从 128 MB 提高到 256 MB。
$ sudo sed -i 's/memory_limit = 128M/memory_limit = 256M/' /etc/php.ini
PHP 默认将媒体库的文件大小限制设为 2MB。运行以下命令将文件大小限制提高到 25MB。
$ sudo sed -i 's/upload_max_filesize = 2M/upload_max_filesize = 25M/g' /etc/php.ini
$ sudo sed -i 's/post_max_size = 8M/post_max_size = 25M/g' /etc/php.ini
重启 PHP-FPM 服务。
$ sudo systemctl restart php-fpm
将 PHP 会话目录的组更改为 Nginx。
$ sudo chgrp -R nginx /var/lib/php/session
配置 Nginx
创建并打开文件 /etc/nginx/conf.d/suitecrm.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/suitecrm.conf
将以下代码粘贴到其中。
server {
    listen 443 ssl http2;
    listen [::]:443 ssl http2;
    server_name suitecrm.example.com;

    root /var/www/html/suitecrm/public;
    error_log /var/log/nginx/suitecrm.error.log;
    access_log /var/log/nginx/suitecrm.access.log;
    client_max_body_size 25M;

    index index.php index.html index.htm;

    ssl_certificate      /etc/letsencrypt/live/suitecrm.example.com/fullchain.pem;
    ssl_certificate_key  /etc/letsencrypt/live/suitecrm.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/suitecrm.example.com/chain.pem;

    ssl_session_timeout  5m;
    ssl_session_cache shared:MozSSL:10m;
    ssl_session_tickets off;

    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;

    location / {
        try_files $uri /index.php;
    }

    location ~ \.php$ {
        try_files $uri =404;
        fastcgi_pass unix:/run/php-fpm/www.sock;
        fastcgi_index index.php;
        fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
        include fastcgi_params;

        fastcgi_buffer_size 128k;
        fastcgi_buffers 256 16k;
        fastcgi_busy_buffers_size 256k;
        fastcgi_temp_file_write_size 256k;
    }

    # Don't log favicon
    location = /favicon.ico {
        log_not_found off;
        access_log off;
    }

    # Deny all attempts to access hidden files/folders such as .htaccess, .htpasswd, .DS_Store (Mac), etc...
    location ~ /\. {
        deny all;
    }

    # A long browser cache lifetime can speed up repeat visits to your page
    location ~* \.(jpg|jpeg|gif|png|webp|svg|woff|woff2|ttf|css|js|ico|xml)$ {
        expires           360d;
    }
}

# enforce HTTPS
server {
    listen       80;
    listen       [::]:80;
    server_name  suitecrm.example.com;
    return 301   https://$host$request_uri;
}
请注意,Nginx 配置中使用的根目录是 /var/www/html/suitecrm/public 。在早期的 SuiteCRM 版本(7.x)中,该目录为 /var/www/html/suitecrm 。public 目录是在 SuiteCRM 8.x 版本中引入的。
完成后按下 Ctrl + X 保存文件,并在提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按下 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
步骤 10 - 安装并访问 SuiteCRM
安装 SuiteCRM 有两种方式。第一种方法是使用 Web 安装程序,第二种方法是使用 SuiteCRM 控制台命令行。
方法 1 - Web 向导
在浏览器中打开 URL https://suitecrm.example.com,您将看到安装向导。
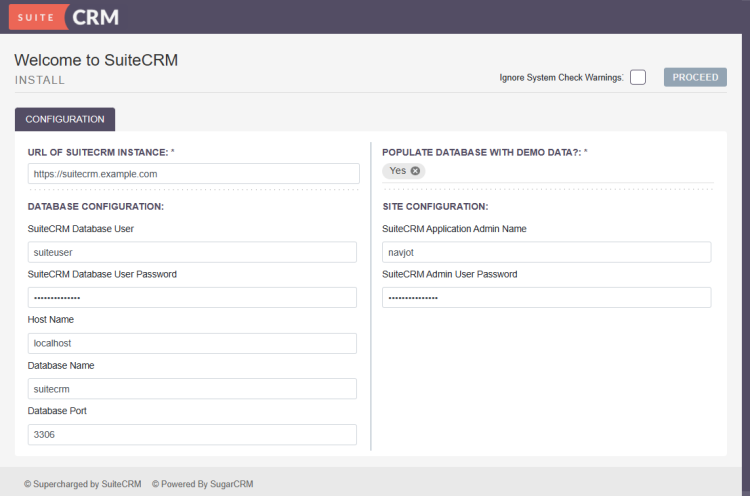
填写 URL、数据库凭据以及您的管理员账户登录信息。输入 localhost 作为主机名,3306 作为数据库端口。点击 Proceed 按钮打开登录页面。
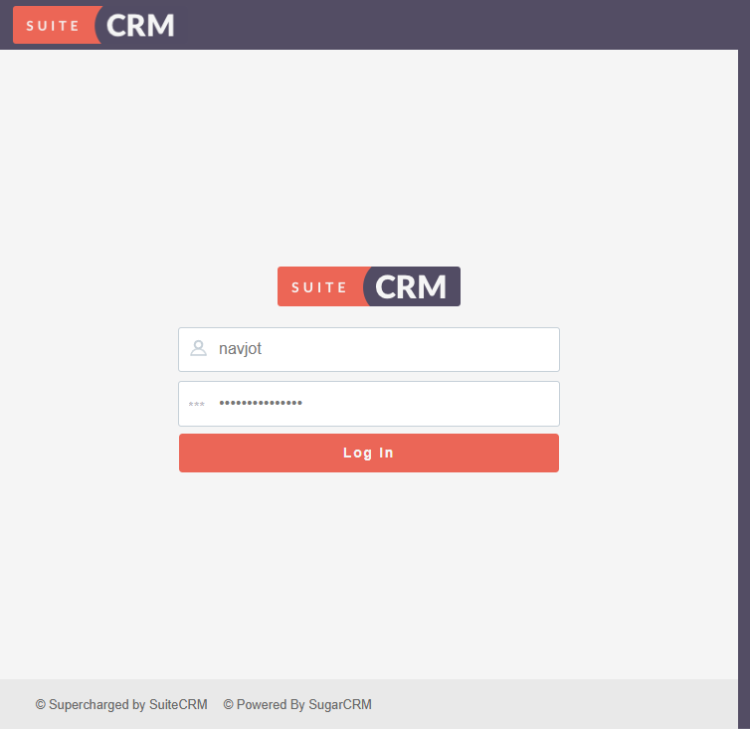
输入您的账户信息并点击 Log in 按钮以打开 SuiteCRM 仪表盘。
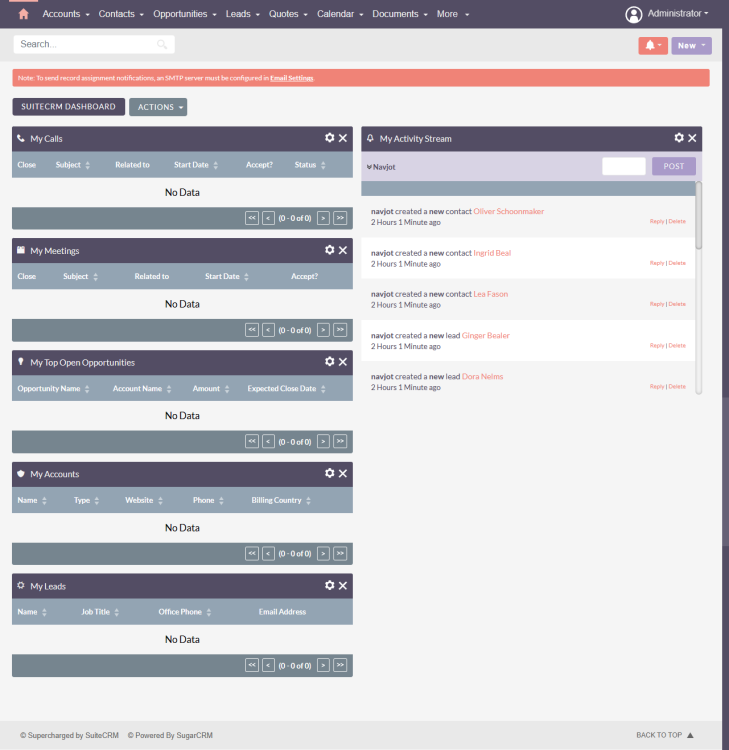
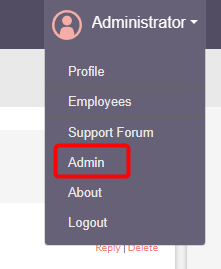
早期版本的 SuiteCRM 在安装过程中提供了配置电子邮件提供商的选项。现在已不再如此。要配置电子邮件提供商,请点击右上角的 Administrator 下拉菜单,并点击 Admin 选项。
您将被带到如下的 SuiteCRM 管理面板(Admin Panel)。
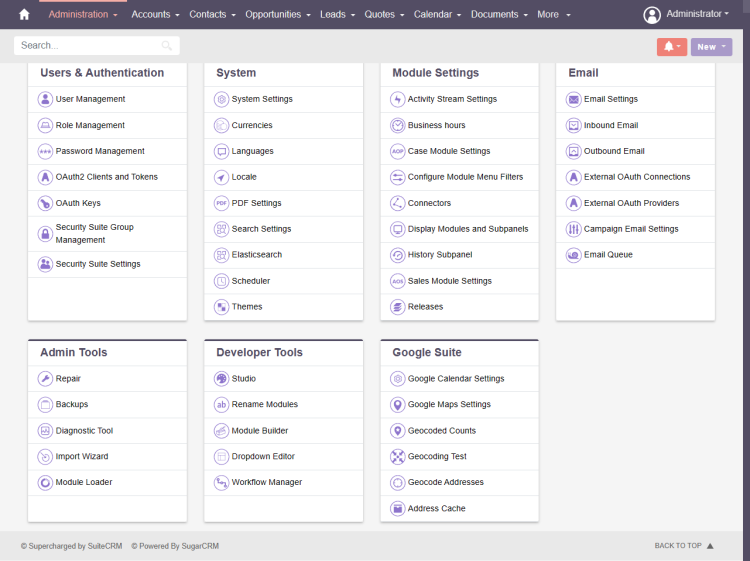
点击 Email Settings 链接以打开电子邮件提供商页面。
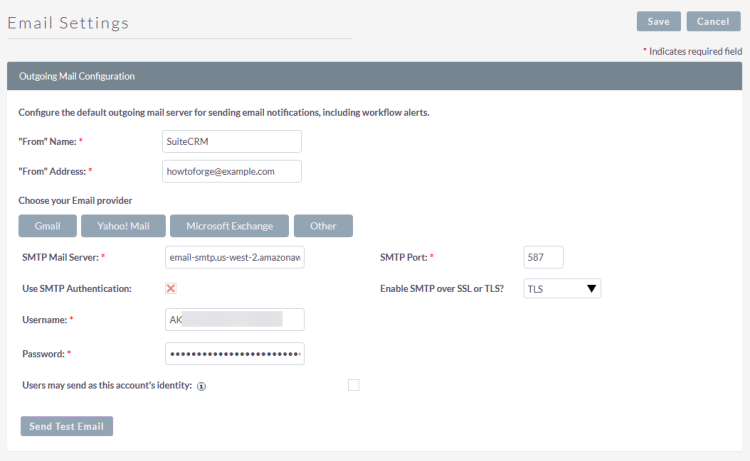
如果您使用的是 Gmail 或 Microsoft Exchange,可以使用专用按钮进行配置。在本教程中,我们使用的是 Amazon SES。如果您希望用户使用您的 SMTP 设置,可以启用相应选项。点击 Send Test Email 按钮打开如下弹窗,并填写您希望接收测试邮件的邮箱地址。
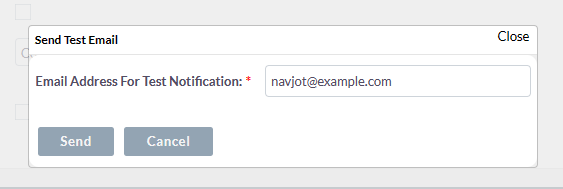
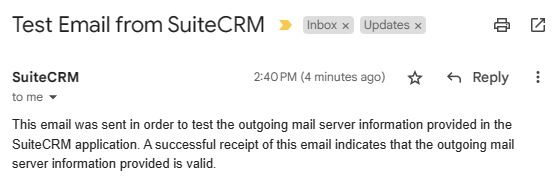
点击 Send 按钮发送测试邮件。如果您收到如下邮件,说明您的设置已正常工作。
点击电子邮件设置页面顶部的 Save 按钮以保存您的设置。现在您可以开始使用 SuiteCRM 来管理客户和业务了。
方法 2 - SuiteCRM 命令控制台
切换到 SuiteCRM 目录。
$ cd /var/www/html/suitecrm
运行以下命令以安装 SuiteCRM。
$ sudo ./bin/console suitecrm:app:install -u "admin_username" -p "admin_password" -U "db_user" -P "db_password" -H "localhost" -N "dbname" -S "https://suitecrm.example.com" -d "yes" -Z "3306"
如果您不需要演示数据,可以省略上述命令中的 -d "yes" 标志。
您甚至可以在不提供任何变量的情况下运行安装程序。在这种情况下,它会向您询问相关信息。
$ sudo ./bin/console suitecrm:app:install
在浏览器中打开 URL https://suitecrm.example.com,打开登录页面并从此处继续。
步骤 11 - 配置 Cron 任务
SuiteCRM 需要 cron 任务才能正常运行。请编辑 nginx 用户的 crontab 文件。Rocky Linux 默认使用 Vim 编辑器。以下命令将在更易使用的 Nano 编辑器中打开 crontab。
$ sudo EDITOR=nano crontab -e -u nginx
在文件末尾添加以下行。
* * * * * cd /var/www/html/suitecrm/public/legacy; php -f cron.php > /dev/null 2>&1
完成后按下 Ctrl + X 保存并关闭文件,并在提示时输入 Y。
总结
本教程到此结束,您已了解如何在 Rocky Linux 9 机器上使用 Nginx 服务器和 Let's Encrypt SSL 安装 SuiteCRM。如果您有任何问题,请在下方的评论中留言。