
本教程适用于以下操作系统版本
- Debian 11 (Bullseye)
- Debian 7 (Wheezy)
本页内容
- 前置条件
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Apache 服务器
- 步骤 3 - 安装并配置 MySQL 服务器
- 步骤 4 - 安装 Ruby 及其他依赖
- 步骤 5 - 安装 Redmine
- 步骤 6 - 安装 Phusion Passenger
- 步骤 7 - 配置 Apache 服务器
- 步骤 8 - 安装 Nginx 更改 Apache 监听端口
- 步骤 9 - 安装 SSL
- 步骤 10 - 配置 Nginx 作为反向代理
- 结论
- 更改 Apache 监听端口
Redmine 是一款免费开源的项目管理软件与问题追踪工具。它基于 Ruby on Rails 框架编写,并可集成多种版本控制系统。它内置仓库浏览器和差异查看器。它可以用于管理项目的特性、各项目独立的 wiki 和论坛、时间跟踪,以及基于角色的访问控制。它是跨平台、跨数据库的,并支持 49 种语言。
在本教程中,你将学习如何在 Debian 11 服务器上安装 Redmine。
前置条件
- 一台运行 Debian 11 的服务器。
- 一个具有 root 权限的非 sudo 用户。
- Uncomplicated Firewall(UFW)已启用并正在运行。
- 系统所需的少数几个软件包。 $ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release unzip debian-archive-keyring -y 其中部分软件包可能已经在你的系统上安装。
- 确保一切都已更新。 $ sudo apt update && sudo apt upgrade
一台运行 Debian 11 的服务器。
一个具有 root 权限的非 sudo 用户。
Uncomplicated Firewall(UFW)已启用并正在运行。
系统所需的少数几个软件包。
$ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release unzip debian-archive-keyring -y
其中部分软件包可能已经在你的系统上安装。
确保一切都已更新。
$ sudo apt update && sudo apt upgrade
步骤 1 - 配置防火墙
在安装任何软件包之前的第一步是配置防火墙,以允许 HTTP 和 HTTPS 连接。
检查防火墙状态。
$ sudo ufw status
你应该会看到类似以下的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
放行 HTTP 和 HTTPS 端口。同时,为 Redmine 开放 3000 端口。
$ sudo ufw allow http
$ sudo ufw allow https
$ sudo ufw allow 3000
再次检查状态以确认。
$ sudo ufw status
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
3000                       ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
3000 (v6)                  ALLOW       Anywhere (v6)
步骤 2 - 安装 Apache 服务器
我们将使用 Apache Web 服务器来部署 Redmine。使用以下命令安装 Apache。
$ sudo apt install apache2
检查 Apache 服务的状态。
$ sudo systemctl status apache2
? apache2.service - The Apache HTTP Server
     Loaded: loaded (/lib/systemd/system/apache2.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2023-03-04 13:28:57 UTC; 41s ago
       Docs: https://httpd.apache.org/docs/2.4/
   Main PID: 3478 (apache2)
      Tasks: 55 (limit: 1129)
     Memory: 9.7M
        CPU: 27ms
     CGroup: /system.slice/apache2.service
             ??3478 /usr/sbin/apache2 -k start
             ??3481 /usr/sbin/apache2 -k start
             ??3482 /usr/sbin/apache2 -k start

Mar 04 13:28:56 redmine systemd[1]: Starting The Apache HTTP Server...
Mar 04 13:28:57 redmine systemd[1]: Started The Apache HTTP Server.
步骤 3 - 安装并配置 MySQL 服务器
我们将使用 MySQL 数据库来存储数据。Debian 的软件仓库中已不再包含 MySQL。因此我们将使用官方的 MySQL 仓库进行安装。
导入 MySQL 的 GPG 密钥。
$ curl https://repo.mysql.com/RPM-GPG-KEY-mysql-2022 | gpg --dearmor | sudo tee /usr/share/keyrings/mysql.gpg >/dev/null
创建 MySQL 仓库文件。
$ echo "deb [signed-by=/usr/share/keyrings/mysql.gpg arch=amd64] http://repo.mysql.com/apt/debian/ `lsb_release -cs` mysql-8.0" | sudo tee /etc/apt/sources.list.d/mysql.list
更新系统仓库列表。
$ sudo apt update
安装 MySQL。
$ sudo apt install mysql-server
系统会提示你设置一个 root 密码。请选择一个强密码。接下来,会提示你在较新的 MySQL caching_sha2_password 加密方式与较旧的 mysql_native_password 加密方式之间进行选择。请选择较新的方式,因为 Redmine 支持它。选择 OK 继续并完成安装。
检查 MySQL 服务的状态。
$ sudo systemctl status mysql
? mysql.service - MySQL Community Server
     Loaded: loaded (/lib/systemd/system/mysql.service; enabled; vendor preset: enabled)
     Active: active (running) since Sun 2023-03-05 08:18:15 UTC; 4h 14min ago
       Docs: man:mysqld(8)
             http://dev.mysql.com/doc/refman/en/using-systemd.html
   Main PID: 10500 (mysqld)
     Status: "Server is operational"
      Tasks: 38 (limit: 1129)
     Memory: 391.5M
        CPU: 1min 49.904s
     CGroup: /system.slice/mysql.service
             ??10500 /usr/sbin/mysqld

Mar 05 08:18:14 redmine systemd[1]: Starting MySQL Community Server...
Mar 05 08:18:15 redmine systemd[1]: Started MySQL Community Server.
加固 MySQL 安装。
$ sudo mysql_secure_installation
首先,会要求你输入 root 密码。请输入安装时设置的密码。接下来,会询问你是否要安装 Validate Password 插件,该插件可用于测试你的 MySQL 密码强度。输入 Y 继续。下一步会要求你选择密码校验级别。请选择 2,这是最强级别,要求密码至少 8 个字符,并包含大小写字母、数字和特殊字符的组合。
Securing the MySQL server deployment.

Enter password for user root:

VALIDATE PASSWORD COMPONENT can be used to test passwords
and improve security. It checks the strength of password
and allows the users to set only those passwords which are
secure enough. Would you like to setup VALIDATE PASSWORD component?

Press y|Y for Yes, any other key for No: Y

There are three levels of password validation policy:

LOW    Length >= 8
MEDIUM Length >= 8, numeric, mixed case, and special characters
STRONG Length >= 8, numeric, mixed case, special characters and dictionary                  file

Please enter 0 = LOW, 1 = MEDIUM and 2 = STRONG: 2
系统会显示你 root 密码的强度,并询问你是否要更改它。如果你不想更改,输入 N 并继续。如果你想更改,现在可以输入 Y 并选择一个满足上述要求的密码。
Using existing password for root.

Estimated strength of the password: 100
Change the password for root ? ((Press y|Y for Yes, any other key for No) : N

 ... skipping.
对后续所有提示按 Y 然后按 ENTER 键,以删除匿名用户和测试数据库、禁用 root 远程登录并加载新设置的规则。
By default, a MySQL installation has an anonymous user,
allowing anyone to log into MySQL without having to have
a user account created for them. This is intended only for
testing, and to make the installation go a bit smoother.
You should remove them before moving into a production
environment.

Remove anonymous users? (Press y|Y for Yes, any other key for No) : Y
Success.


Normally, root should only be allowed to connect from
'localhost'. This ensures that someone cannot guess at
the root password from the network.

Disallow root login remotely? (Press y|Y for Yes, any other key for No) : Y
Success.

By default, MySQL comes with a database named 'test' that
anyone can access. This is also intended only for testing,
and should be removed before moving into a production
environment.


Remove test database and access to it? (Press y|Y for Yes, any other key for No) : Y
 - Dropping test database...
Success.

 - Removing privileges on test database...
Success.

Reloading the privilege tables will ensure that all changes
made so far will take effect immediately.

Reload privilege tables now? (Press y|Y for Yes, any other key for No) : Y
Success.

All done!
进入 MySQL 命令行。输入你的 root 密码以继续。
$ mysql -u root -p
创建 redmine 用户。确保密码满足之前设置的要求。
mysql> CREATE USER 'redmine'@'localhost' IDENTIFIED BY 'Your_password2';
创建 redmine 数据库。
mysql> CREATE DATABASE redmine CHARACTER SET utf8mb4;
授予该用户对 redmine 数据库的权限。
mysql> GRANT ALL PRIVILEGES ON redmine.* TO 'redmine'@'localhost';
退出命令行。
mysql> exit
步骤 4 - 安装 Ruby 及其他依赖
Redmine 的最新版本兼容 Ruby 3.1。Debian 自带的是 Ruby 2.7,因此我们需要使用 Ruby Version Manager(RVM)来安装最新版本。
安装 RVM 的 GPG 密钥。
$ gpg2 --keyserver keyserver.ubuntu.com --recv-keys 409B6B1796C275462A1703113804BB82D39DC0E3 7D2BAF1CF37B13E2069D6956105BD0E739499BDB
安装 RVM。
$ \curl -sSL https://get.rvm.io | bash -s stable
加载 RVM 脚本。
$ source ~/.rvm/scripts/rvm
安装 Ruby。你可以从 Ruby 官网查看最新版本。在撰写本教程时,Ruby 3.1.3 是该系列中的最新版本。
$ rvm install ruby-3.1.3
验证安装。
$ ruby -v
ruby 3.1.3p185 (2022-11-24 revision 1a6b16756e) [x86_64-linux]
安装 Redmine 所需的其余所有软件包。
$ sudo apt install libxml2-dev libxslt1-dev zlib1g-dev imagemagick libmagickwand-dev libmysqlclient-dev apache2-dev build-essential libcurl4-openssl-dev
步骤 5 - 安装 Redmine
访问 Redmine 下载页面,查看可用的最新稳定版本。在撰写本教程时,最新的可用版本是 5.0.5。
使用 wget 下载 Redmine。
$ wget https://www.redmine.org/releases/redmine-5.0.5.tar.gz
在下载该归档文件时,你可能会遇到以下错误,原因是该网站的一个根证书已过期。
WARNING: The certificate of ‘www.redmine.org’ is not trusted.
WARNING: The certificate of ‘www.redmine.org’ doesn't have a known issuer.
WARNING: The certificate of ‘www.redmine.org’ has expired.
如果你遇到此错误,请改用以下命令进行下载。
$ wget https://www.redmine.org/releases/redmine-5.0.5.tar.gz --no-check-certificate
解压并将文件移动到 /var/www/redmine 目录。
$ tar xfz redmine-5.0.5.tar.gz
$ sudo mv redmine-5.0.5 /var/www/redmine
切换到 /var/www/redmine 目录。
$ cd /var/www/redmine
你会看到以下输出以及一条关于 Ruby 版本的警告。你可以放心忽略它。
RVM used your Gemfile for selecting Ruby, it is all fine - Heroku does that too,
you can ignore these warnings with 'rvm rvmrc warning ignore /var/www/redmine/Gemfile'.
To ignore the warning for all files run 'rvm rvmrc warning ignore allGemfiles'.

Unknown ruby interpreter version (do not know how to handle): >=2.5.0,<3.2.0.
使用提供的示例文件创建 Redmine 配置文件。
$ cp config/configuration.yml.example config/configuration.yml
$ cp config/database.yml.example config/database.yml
$ cp public/dispatch.fcgi.example public/dispatch.fcgi
打开 database.yml 文件进行编辑。
$ nano config/database.yml
在以下小节中找到并配置你的数据库设置。
production:
  adapter: mysql2
  database: redmine
  host: localhost
  username: redmine
  password: "Your_password2"
  # Use "utf8" instead of "utfmb4" for MySQL prior to 5.7.7
  encoding: utf8mb4
按 Ctrl + X 保存文件,并在提示时输入 Y。
安装 bundler 以管理 Ruby gem 依赖。
$ gem install bundler
设置用于安装 gem 依赖的环境。
$ bundle config set --local without 'development test'
安装 gem 依赖。
$ bundle install
如果你遇到 gem 版本相关的问题,请使用以下命令进行恢复。
$ gem pristine --all
添加 webrick 依赖。
$ bundle add webrick
生成一个随机密钥,以防止篡改用于存储会话数据的 Cookie。
$ bundle exec rake generate_secret_token
创建数据库结构。
$ RAILS_ENV=production bundle exec rake db:migrate
将数据插入 MySQL 数据库。
$ RAILS_ENV=production REDMINE_LANG=en bundle exec rake redmine:load_default_data
创建必要的目录并设置文件权限。
$ mkdir -p tmp/pdf
$ mkdir -p public/plugin_assets
$ chown -R $USER:$USER files log tmp public/plugin_assets
$ chmod -R 755 /var/www/redmine/
运行以下命令以启动一个 Rails 服务器实例。
$ bundle exec rails server -u webrick -e production
=> Booting WEBrick
=> Rails 6.1.7.2 application starting in production http://0.0.0.0:3000
=> Run `bin/rails server --help` for more startup options
[2023-03-06 09:12:11] INFO  WEBrick 1.7.0
[2023-03-06 09:12:11] INFO  ruby 3.1.3 (2022-11-24) [x86_64-linux]
[2023-03-06 09:12:11] INFO  WEBrick::HTTPServer#start: pid=34652 port=3000
打开 URL http://<你的服务器IP>:3000/login 以进入 Redmine 登录界面。
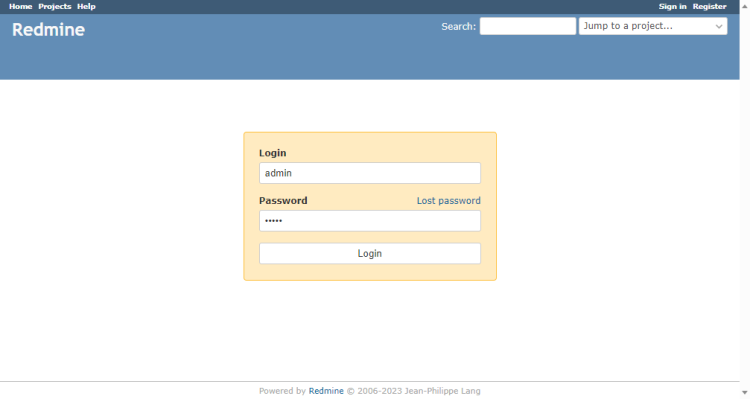
输入默认凭据(admin/admin)进行登录。系统会要求你更改密码。
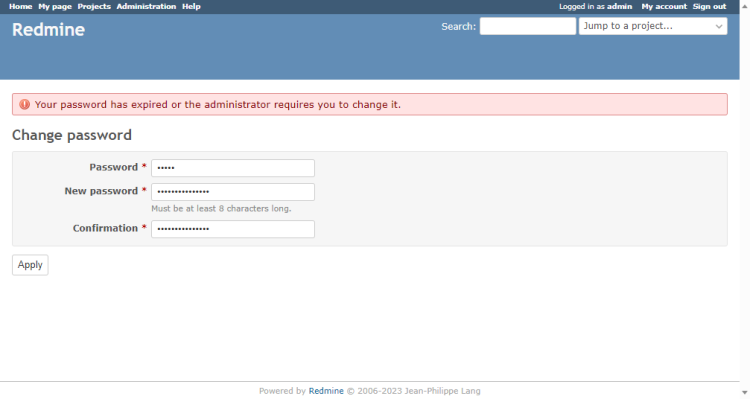
接下来,你将被重定向到「我的账户」页面。
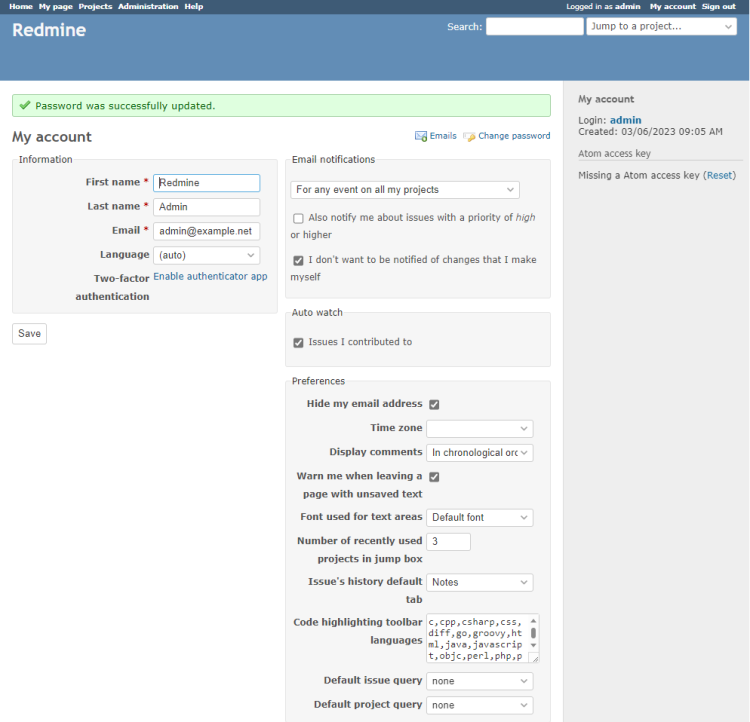
Redmine 已成功安装。
接下来,在终端中按 CTRL+C 停止服务器。
步骤 6 - 安装 Phusion Passenger
Phusion Passenger 是一个 Ruby 应用服务器,允许我们通过第三方服务器来提供 Redmine 服务。在本例中,我们将使用 Apache。
安装 Passenger。
$ gem install passenger
为 Apache 服务器安装 Passenger 模块。
$ passenger-install-apache2-module
你会看到一条欢迎信息。按 Enter 继续。
Welcome to the Phusion Passenger Apache 2 module installer, v6.0.17.

This installer will guide you through the entire installation process. It
shouldn't take more than 3 minutes in total.

Here's what you can expect from the installation process:

 1. The Apache 2 module will be installed for you.
 2. You'll learn how to configure Apache.
 3. You'll learn how to deploy a Ruby on Rails application.

Don't worry if anything goes wrong. This installer will advise you on how to
solve any problems.

Press Enter to continue, or Ctrl-C to abort.
--------------------------------------------
接下来,会询问你选择语言。Ruby 为默认选中,因此直接按 Enter 继续即可。
Which languages are you interested in?

Use <space> to select.
If the menu doesn't display correctly, press '!'

 ? ?  Ruby
   ?  Python
   ?  Node.js
   ?  Meteor
--------------------------------------------
整个过程大约需要 10-15 分钟完成。如果你遇到类似以下的错误,很可能是内存(RAM)不足。你应该增加服务器内存或安装交换空间(swap)。
c++: fatal error: Killed signal terminated program cc1plus
compilation terminated.
rake aborted!
一旦过程完成,你会看到以下信息。
--------------------------------------------
Almost there!

Please edit your Apache configuration file, and add these lines:

   LoadModule passenger_module /home/navjot/.rvm/gems/ruby-3.1.3/gems/passenger-6.0.17/buildout/apache2/mod_passenger.so
   <IfModule mod_passenger.c>
     PassengerRoot /home/navjot/.rvm/gems/ruby-3.1.3/gems/passenger-6.0.17
     PassengerDefaultRuby /home/navjot/.rvm/gems/ruby-3.1.3/wrappers/ruby
   </IfModule>

After you restart Apache, you are ready to deploy any number of web
applications on Apache, with a minimum amount of configuration!

Press ENTER when you are done editing.
先不要按 Enter。以当前用户身份在服务器上打开一个新会话,并执行以下配置。
步骤 7 - 配置 Apache 服务器
为 Phusion Passenger 创建一个 Apache 模块配置文件。
$ sudo nano /etc/apache2/conf-available/00-passenger.conf
粘贴你在 Passenger 安装结束时获得的那段代码。
 LoadModule passenger_module /home/navjot/.rvm/gems/ruby-3.1.3/gems/passenger-6.0.17/buildout/apache2/mod_passenger.so
   <IfModule mod_passenger.c>
     PassengerRoot /home/navjot/.rvm/gems/ruby-3.1.3/gems/passenger-6.0.17
     PassengerDefaultRuby /home/navjot /.rvm/gems/ruby-3.1.3/wrappers/ruby
   </IfModule>
按 Ctrl + X 保存文件,并在提示时输入 Y。
为 Redmine 站点创建另一个 Apache 配置文件。
$ sudo nano /etc/apache2/sites-available/redmine.conf
在其中粘贴以下代码。
Listen 3000
<IfModule mod_passenger.c>
  PassengerRoot /home/navjot/.rvm/gems/ruby-3.1.3/gems/passenger-6.0.17
  PassengerDefaultRuby /home/navjot/.rvm/gems/ruby-3.1.3/wrappers/ruby
</IfModule>
<VirtualHost *:3000>
    ServerName redmine.example.com
    DocumentRoot "/var/www/redmine/public"

    CustomLog ${APACHE_LOG_DIR}/redmine_access.log combined
    ErrorLog ${APACHE_LOG_DIR}/redmine_error.log
    LogLevel warn

    <Directory "/var/www/redmine/public">
        Options Indexes ExecCGI FollowSymLinks
        Require all granted
        AllowOverride all
    </Directory>
</VirtualHost>
按 Ctrl + X 保存文件,并在提示时输入 Y。
打开 Apache 主配置文件 /etc/httpd/conf/httpd.conf 进行编辑。
$ sudo nano /etc/httpd/conf/httpd.conf
找到 ServerName 变量,去掉其前面的井号(#)以取消注释,并将其值设置如下。
ServerName localhost
按 Ctrl + X 保存文件,并在提示时输入 Y。
启用 Redmine 站点和 Phusion Passenger 配置。
$ sudo a2ensite redmine.conf
$ sudo a2enconf 00-passenger.conf
验证你的 Apache 配置。
$ sudo apachectl configtest
Syntax OK
返回并按 Enter 继续你的 Passenger 安装。它会执行一些检查,成功后你应该会看到以下信息。
Deploying a web application

To learn how to deploy a web app on Passenger, please follow the deployment
guide:

  https://www.phusionpassenger.com/library/deploy/apache/deploy/

Enjoy Phusion Passenger, a product of Phusion® (www.phusion.nl) :-)
https://www.phusionpassenger.com

Passenger® is a registered trademark of Phusion Holding B.V.
重启你的 Apache 服务器。
$ sudo systemctl restart apache2
你的网站应该可以通过 http://redmine.example.com:3000 访问。
这不是访问 Redmine 的理想方式。它仍然通过不安全的 HTTP 协议并使用了端口号来提供服务。我们将安装 Nginx 作为反向代理,并使用 HTTPS 协议来提供 Redmine 服务,以改善这一点。在继续进行 Nginx 的安装和配置之前,我们需要先配置 SSL 证书。
步骤 8 - 安装 Nginx
Debian 11 自带的是较旧版本的 Nginx。要安装最新版本,你需要下载官方的 Nginx 仓库。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
    | sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
为 Nginx 的稳定版本添加仓库。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg] \
http://nginx.org/packages/debian `lsb_release -cs` nginx" \
    | sudo tee /etc/apt/sources.list.d/nginx.list
更新系统仓库。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。Debian 要求使用 sudo 来运行以下命令。
$ sudo nginx -v
nginx version: nginx/1.22.1
更改 Apache 监听端口
为避免与 Nginx 冲突,我们需要更改 Apache 监听的默认端口。打开 /etc/apache2/ports.conf 文件进行编辑。
$ sudo nano /etc/apache2/ports.conf
将端口从 80 改为 8080,如下所示。
Listen 8080
按 Ctrl + X 保存文件,并在提示时输入 Y。
禁用默认站点配置。
$ sudo a2dissite 000-default.conf
重启 Apache。
$ sudo systemctl restart apache2
启动 Nginx 服务器。
$ sudo systemctl start nginx
检查 Nginx 服务器状态。
$ sudo systemctl status nginx
? nginx.service - nginx - high performance web server
     Loaded: loaded (/lib/systemd/system/nginx.service; enabled; vendor preset: enabled)
     Active: active (running) since Mon 2023-03-06 10:29:44 UTC; 6s ago
       Docs: https://nginx.org/en/docs/
    Process: 53531 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 53532 (nginx)
      Tasks: 2 (limit: 1129)
     Memory: 1.7M
        CPU: 8ms
     CGroup: /system.slice/nginx.service
             ??53532 nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf
             ??53533 nginx: worker process
步骤 9 - 安装 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Debian 的仓库安装 Certbot,或者通过 Snapd 工具获取最新版本。我们将使用 Snapd 版本。
Debian 默认没有安装 Snapd。因此,请安装 Snapd。
$ sudo apt install snapd
运行以下命令以确保你的 Snapd 版本是最新的。
$ sudo snap install core && sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可以被运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d redmine.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/redmine.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
你会发现 snap.certbot.renew.service 是计划运行的服务之一。
NEXT                        LEFT         LAST                        PASSED       UNIT                         ACTIVATES
Mon 2023-03-06 11:37:00 UTC 1h 2min left n/a                         n/a          snap.certbot.renew.timer     snap.certbot.renew.service
Mon 2023-03-06 13:37:15 UTC 3h 2min left Sun 2023-03-05 13:37:15 UTC 20h ago      systemd-tmpfiles-clean.timer systemd-tmpfiles-clean.service
Tue 2023-03-07 00:00:00 UTC 13h left     Mon 2023-03-06 00:00:15 UTC 10h ago      logrotate.timer              logrotate.service
对该过程进行一次空运行(dry run),以检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果没有看到错误,你就大功告成了。你的证书将自动续期。
步骤 10 - 配置 Nginx 作为反向代理
创建并打开文件 /etc/nginx/conf.d/redmine.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/redmine.conf
在其中粘贴以下代码。
# Redirect all non-encrypted to encrypted
server {
    listen 80;
    server_name redmine.example.com;
    return 301 https://$host$request_uri;
}

server {
    listen 443 ssl http2;

    server_name redmine.example.com;

    ssl_certificate     /etc/letsencrypt/live/redmine.example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/redmine.example.com/privkey.pem;
	ssl_trusted_certificate /etc/letsencrypt/live/redmine.example.com/chain.pem;

	ssl_session_timeout  5m;
    ssl_session_cache shared:MozSSL:10m;
    ssl_session_tickets off;

    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;
    resolver 8.8.8.8;

    access_log /var/log/nginx/redmine.access.log main;
    error_log  /var/log/nginx/redmine.error.log;

	location / {
        proxy_pass          http://localhost:3000;
        proxy_redirect      off;
        proxy_buffering     off;
        proxy_set_header    Host $host;
        proxy_set_header    X-Real-IP $remote_addr;
        proxy_set_header    X-Forwarded-For $proxy_add_x_forwarded_for;
    }
}
完成后按 Ctrl + X 保存文件,并在提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下一行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务以使新配置生效。
$ sudo systemctl restart nginx
你的 Redmine 应用应该可以通过 https://redmine.example.com 访问。
你应该在防火墙中删除 3000 端口的条目,因为已经不再需要它了。
$ sudo ufw delete allow 3000
结论
本教程到此结束,你学习了如何在 Debian 11 服务器上安装 Redmine 项目管理器。你还学习了如何通过 Nginx 使用 HTTPS 协议来提供 Redmine 应用服务。如果你有任何问题,请在下方评论中留言。