
本页内容
- 先决条件
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装并配置 PostgreSQL
- 第 3 步 - 安装 Node.js
- 第 4 步 - 安装 Strapi
- 第 5 步 - 安装并配置 PM2
- 第 6 步 - 安装 Nginx
- 第 7 步 - 安装 SSL
- 第 8 步 - 配置 Nginx
- 第 9 步 - 升级 Strapi
- 结论
Strapi 是一个使用 JavaScript 构建的开源无头内容管理系统(CMS)。与其他无头 CMS 一样,Strapi 开箱即用时并不附带前端。它通过 API 提供前端,使你能使用 React 和 Next.js 等流行框架来构建网站。Strapi 基于插件系统,是一个灵活的 CMS,其管理面板和 API 均可扩展,且每个部分都可定制以适配任何使用场景。Strapi 还内置了用户系统,用于详细管理管理员和最终用户所能访问的权限。
在本教程中,你将学习如何在 Ubuntu 22.04 服务器上安装社区版的 Strapi CMS,并使用 Nginx 作为反向代理服务器。
先决条件
- 一台运行 Ubuntu 22.04 的服务器。
- 一个具有 sudo 权限的非 root 用户。
- 一个完全限定域名(FQDN),例如 strapi.example.com 。
- 确保系统已更新至最新。 $ sudo apt update $ sudo apt upgrade
- 系统所需的一些软件包。 $ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y 其中部分软件包可能已安装在你的系统上。
一台运行 Ubuntu 22.04 的服务器。
一个具有 sudo 权限的非 root 用户。
一个完全限定域名(FQDN),例如 strapi.example.com 。
确保系统已更新至最新。
$ sudo apt update
$ sudo apt upgrade
系统所需的一些软件包。
$ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y
其中部分软件包可能已安装在你的系统上。
第 1 步 - 配置防火墙
第一步是配置防火墙。Ubuntu 默认自带 ufw(Uncomplicated Firewall,简易防火墙)。
检查防火墙是否正在运行。
$ sudo ufw status
你应该会看到如下输出。
Status: inactive
放行 SSH 端口,以免启用防火墙时中断当前连接。
$ sudo ufw allow OpenSSH
同时放行 HTTP 和 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
启用防火墙
$ sudo ufw enable
Command may disrupt existing ssh connections. Proceed with operation (y|n)? y
Firewall is active and enabled on system startup
再次检查防火墙的状态。
$ sudo ufw status
你应该会看到类似的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
第 2 步 - 安装并配置 PostgreSQL
Strapi 兼容 PostgreSQL 11 及以上版本。Ubuntu 22.04 默认附带 PostgreSQL 14。本教程中将使用 PostgreSQL 15。
运行以下命令以添加 PostgreSQL 的 GPG 密钥。
$ curl https://www.postgresql.org/media/keys/ACCC4CF8.asc | gpg --dearmor | sudo tee /usr/share/keyrings/postgresql-key.gpg >/dev/null
将 APT 仓库添加到你的软件源列表。
$ sudo sh -c 'echo "deb [signed-by=/usr/share/keyrings/postgresql-key.gpg arch=amd64] http://apt.postgresql.org/pub/repos/apt $(lsb_release -cs)-pgdg main" > /etc/apt/sources.list.d/pgdg.list'
更新系统软件源。
$ sudo apt update
现在,你可以使用以下命令安装 PostgreSQL。
$ sudo apt install postgresql postgresql-contrib
postgresql-contrib 软件包包含一些额外的工具。
检查 PostgreSQL 服务的状态。
$ sudo systemctl status postgresql
? postgresql.service - PostgreSQL RDBMS
     Loaded: loaded (/lib/systemd/system/postgresql.service; enabled; vendor preset: enabled)
     Active: active (exited) since Wed 2022-12-28 18:03:03 UTC; 17s ago
   Main PID: 4119 (code=exited, status=0/SUCCESS)
        CPU: 2ms

Dec 28 18:03:03 strapi systemd[1]: Starting PostgreSQL RDBMS...
Dec 28 18:03:03 strapi systemd[1]: Finished PostgreSQL RDBMS.
你可以看到该服务默认已启用并正在运行。
进入 PostgreSQL 命令行终端。
$ sudo -i -u postgres psql
创建 Strapi 数据库。
postgres=# CREATE DATABASE strapidb;
创建 Strapi 用户并设置一个强密码。
postgres-# CREATE USER strapiuser WITH PASSWORD 'Your_Password';
将数据库所有者更改为 Strapi 用户。
postgres-# ALTER DATABASE strapidb OWNER TO strapiuser;
退出终端。
postgres-# \q
验证你的凭据是否有效。
$ psql --username strapiuser --password --host localhost strapidb
Password:
psql (15.1 (Ubuntu 15.1-1.pgdg22.04+1))
SSL connection (protocol: TLSv1.3, cipher: TLS_AES_256_GCM_SHA384, bits: 256, compression: off)
Type "help" for help.

strapidb=>
输入 \q 退出终端。
第 3 步 - 安装 Node.js
Ubuntu 22.04 自带的 Node v12 已经过时。我们将安装最新的 Node LTS 版本,在撰写本教程时该版本为 v18。
从 Nodesource 获取 Node v18 安装脚本。
$ curl -sL https://deb.nodesource.com/setup_18.x -o nodesource_setup.sh
运行安装脚本。
$ sudo bash nodesource_setup.sh
安装 Node.js。
$ sudo apt install nodejs
验证 Node.js 版本。
$ node -v
v18.12.1
删除安装脚本文件。
$ rm nodesource_setup.sh
第 4 步 - 安装 Strapi
运行以下命令以安装 Strapi。
$ npx create-strapi-app@latest howtoforge-project
Need to install the following packages:

[email protected]

Ok to proceed? (y) y
输入 y 以继续安装。接下来会要求你选择安装类型。选择 Custom(自定义)以继续,并按如下回答相关问题。
? Choose your installation type Custom (manual settings)
? Choose your preferred language JavaScript
? Choose your default database client postgres
? Database name: strapidb
? Host: 127.0.0.1
? Port: 5432
? Username: strapiuser
? Password: Your_Password
? Enable SSL connection: No
根据你的需求,可以选择 Typescript 或 JavaScript 作为 Strapi 的开发语言。
安装完成后,你就可以构建自己的 Strapi 项目了。
切换到项目目录。
$ cd howtoforge-project
运行以下命令构建项目(包括 Strapi 管理界面)。
$ NODE_ENV=production npm run build
使用以下命令启动 Strapi 服务器。
$ node ~/howtoforge-project/node_modules/.bin/strapi start
你的应用应当可以通过 URL http://
$ sudo ufw allow 1337
打开该 URL 后,你应该会看到以下界面。
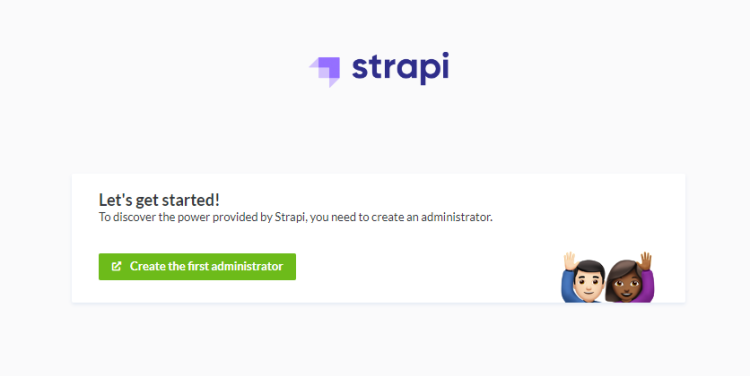
在终端中按 Ctrl + C 停止服务器。你应当删除该防火墙规则,因为我们不再需要它。
$ sudo ufw delete allow 1337
第 5 步 - 安装并配置 PM2
我们可以借助 PM2(Process Manager 2,进程管理器 2)来管理进程并为其创建 systemd 服务,而无需手动启动服务器。
切换到主目录。
$ cd ~
安装 PM2。
$ sudo npm install pm2@latest -g
创建并打开 PM2 配置文件进行编辑。
$ sudo nano ecosystem.config.js
将以下内容粘贴到文件中。请确保填写正确的目录名称以及 Postgres 凭据。
module.exports = {
  apps: [
    {
      name: 'strapi',
      cwd: '/home/navjot/my-project',
      script: 'npm',
      args: 'start',
      env: {
        NODE_ENV: 'production',
        DATABASE_HOST: 'localhost',
        DATABASE_PORT: '5432',
        DATABASE_NAME: 'strapidb',
        DATABASE_USERNAME: 'strapiuser',
        DATABASE_PASSWORD: 'Your_Password',
      },
    },
  ],
};
完成后按 Ctrl + X 保存文件,并在提示时输入 Y。
使用 PM2 在后台运行你的 Strapi 实例。
$ pm2 start ecosystem.config.js
你将看到如下输出。
                        -------------

__/\\\\\\\\\\\\\____/\\\\____________/\\\\____/\\\\\\\\\_____
 _\/\\\/////////\\\_\/\\\\\\________/\\\\\\__/\\\///////\\\___
  _\/\\\_______\/\\\_\/\\\//\\\____/\\\//\\\_\///______\//\\\__
   _\/\\\\\\\\\\\\\/__\/\\\\///\\\/\\\/_\/\\\___________/\\\/___
    _\/\\\/////////____\/\\\__\///\\\/___\/\\\________/\\\//_____
     _\/\\\_____________\/\\\____\///_____\/\\\_____/\\\//________
      _\/\\\_____________\/\\\_____________\/\\\___/\\\/___________
       _\/\\\_____________\/\\\_____________\/\\\__/\\\\\\\\\\\\\\\_
        _\///______________\///______________\///__\///////////////__


                          Runtime Edition

        PM2 is a Production Process Manager for Node.js applications
                     with a built-in Load Balancer.

                Start and Daemonize any application:
                $ pm2 start app.js

                Load Balance 4 instances of api.js:
                $ pm2 start api.js -i 4

                Monitor in production:
                $ pm2 monitor

                Make pm2 auto-boot at server restart:
                $ pm2 startup

                To go further checkout:
                http://pm2.io/


                        -------------

[PM2] Spawning PM2 daemon with pm2_home=/home/navjot/.pm2
[PM2] PM2 Successfully daemonized
[PM2][WARN] Applications strapi not running, starting...
[PM2] App [strapi] launched (1 instances)
????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????
? id  ? name      ? namespace   ? version ? mode    ? pid      ? uptime ? ?    ? status    ? cpu      ? mem      ? user
    ? watching ?
????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????
? 0   ? strapi    ? default     ? N/A     ? fork    ? 4824     ? 0s     ? 0    ? online    ? 0%       ? 31.9mb   ? navjot   ? disabled ?
????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????????
在 PM2 下运行的应用在崩溃或被终止时会自动重启。
使用以下命令创建开机启动的 systemd 脚本。
$ pm2 startup
你将看到如下输出。
[PM2] Init System found: systemd
[PM2] To setup the Startup Script, copy/paste the following command:
sudo env PATH=$PATH:/usr/bin /usr/lib/node_modules/pm2/bin/pm2 startup systemd -u navjot --hp /home/navjot
复制上面输出中的命令并运行它。
$ sudo env PATH=$PATH:/usr/bin /usr/lib/node_modules/pm2/bin/pm2 startup systemd -u navjot --hp /home/navjot
保存 PM2 进程列表。
$ pm2 save
你的 Strapi 服务现在正以生产模式在后台运行。
第 6 步 - 安装 Nginx
Ubuntu 22.04 自带的是较旧版本的 Nginx。要安装最新版本,你需要下载官方的 Nginx 仓库。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
	| sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
添加 Nginx 稳定版的仓库。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg arch=amd64] \
http://nginx.org/packages/ubuntu `lsb_release -cs` nginx" \
    | sudo tee /etc/apt/sources.list.d/nginx.list
更新系统软件源。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.22.1
启动 Nginx 服务器。
$ sudo systemctl start nginx
第 7 步 - 安装 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Ubuntu 的仓库安装 Certbot,也可以通过 Snapd 工具获取最新版本。本教程将使用 Snapd 版本。
Ubuntu 22.04 默认已安装 Snapd。运行以下命令以确保你的 Snapd 版本是最新的。请确保你的 Snapd 版本是最新的。
$ sudo snap install core
$ sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令创建指向 /usr/bin 目录的符号链接,以确保 certbot 命令可正常运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
运行以下命令生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d strapi.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/strapi.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
对流程进行一次试运行,检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果未出现错误,说明一切就绪。你的证书将自动续期。
第 8 步 - 配置 Nginx
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
创建并打开文件 /etc/nginx/conf.d/strapi.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/strapi.conf
将以下代码粘贴到其中。
server {
  # Redirect any http requests to https
  listen         80;
  listen         [::]:80;
  server_name    strapi.example.com;
  return 301     https://$host$request_uri;
}

server {
  listen                    443 ssl http2;
  listen                    [::]:443 ssl http2;
  server_name               strapi.example.com;

  access_log                /var/log/nginx/strapi.access.log;
  error_log                 /var/log/nginx/strapi.error.log;

  # TLS configuration
  ssl_certificate           /etc/letsencrypt/live/strapi.example.com/fullchain.pem;
  ssl_certificate_key       /etc/letsencrypt/live/strapi.example.com/privkey.pem;
  ssl_trusted_certificate   /etc/letsencrypt/live/strapi.example.com/chain.pem;
  ssl_protocols             TLSv1.2 TLSv1.3;

  ssl_ciphers 'ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA384';
  ssl_prefer_server_ciphers on;
  ssl_session_cache         shared:SSL:50m;
  ssl_session_timeout       1d;

  # OCSP Stapling ---
  # fetch OCSP records from URL in ssl_certificate and cache them
  ssl_stapling on;
  ssl_stapling_verify on;
  ssl_dhparam /etc/ssl/certs/dhparam.pem;

  location / {
    proxy_set_header        X-Real-IP $remote_addr;
    proxy_set_header        X-Forwarded-Proto $scheme;
    proxy_set_header	    X-Forwarded-Host $http_host;
    proxy_set_header        X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_pass              http://127.0.0.1:1337;
  }
}
完成后按 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
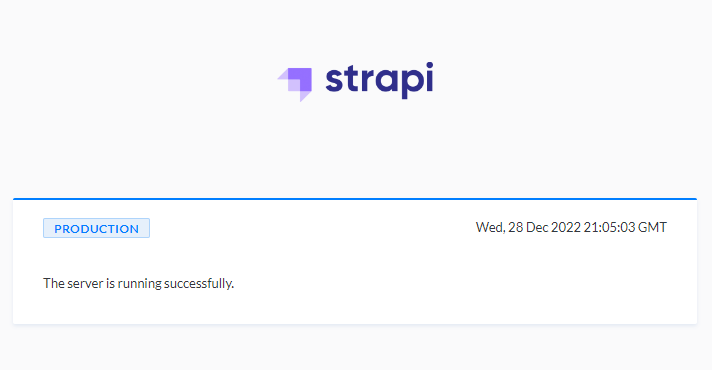
现在你可以通过 URL https://strapi.example.com 访问 Strapi CMS。你将看到以下页面,表明 Strapi 正在以生产模式运行。
访问 https://strapi.example.com/admin 以创建一个管理员用户。
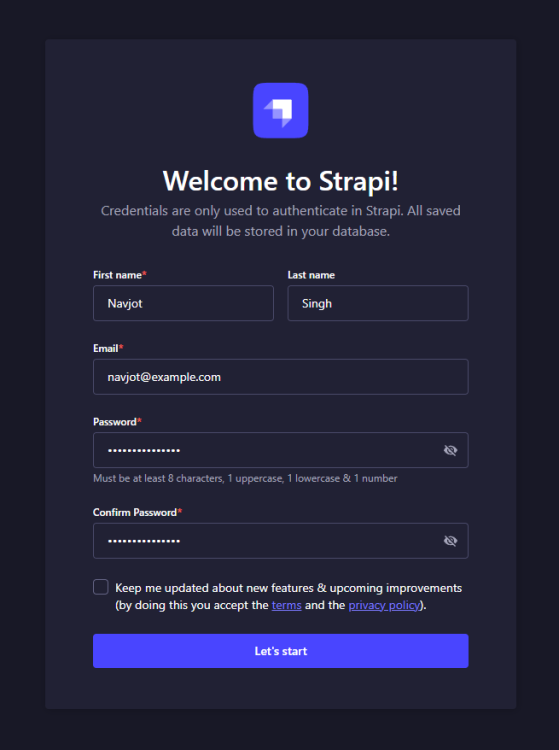
填写管理员信息,并点击 Let's start(开始)按钮,进入管理员仪表板界面。
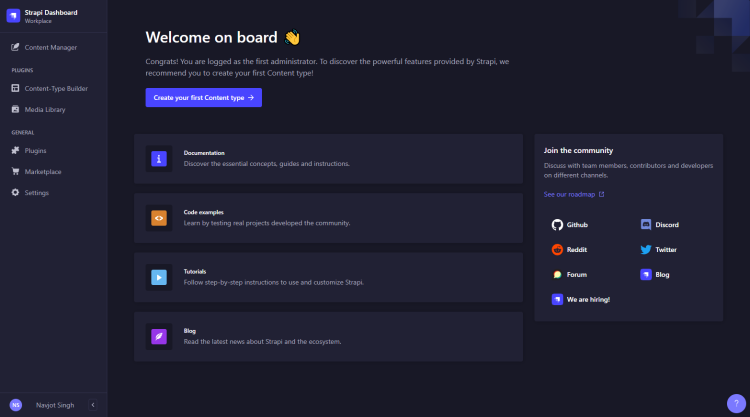
此后,你就可以开始在 Strapi 上创建内容了。
第 9 步 - 升级 Strapi
升级 Strapi 的第一步是停止服务器。
$ cd ~
$ pm2 stop ecosystem.config.js
切换到项目目录并打开 package.json 文件进行编辑。
$ cd howtoforge-project
$ nano package.json
将所有 Strapi 软件包的版本号升级到最新的稳定版 Strapi。你可以从 Strapi 的 GitHub releases 页面获取最新可用版本。
"devDependencies": {},
  "dependencies": {
    "@strapi/strapi": "4.5.5",
    "@strapi/plugin-users-permissions": "4.5.5",
    "@strapi/plugin-i18n": "4.5.5",
    "pg": "8.6.0"
  },
这里你需要将 4.5.5 改为最新的稳定版本。完成后按 Ctrl + X 保存文件,并在提示时输入 Y。
安装升级后的版本。
$ npm install
重新构建管理面板。
$ NODE_ENV=production npm run build
再次启动服务器。
$ cd ~
$ pm2 start ecosystem.config.js
你的 Strapi 安装现已升级并正在运行。
结论
至此,本教程关于在 Ubuntu 22.04 服务器上安装 Strapi CMS 并使用 Nginx 作为反向代理服务器的内容就结束了。如果你有任何问题,请在下方评论区留言。