
本教程适用于以下操作系统版本
- Debian 12 (Bookworm)
- Debian 11 (Bullseye)
- Debian 10 (Buster)
- Debian 9 (Stretch)
- Debian 8 (Jessie)
- Debian 7 (Wheezy)
本页目录
- 1 环境要求
- 2 前置说明
- 3 Debian 基础系统
- 4 安装 SSH 服务器(可选)
- 5 安装 shell 编辑器(可选)
- 6 配置网络
- 7 更新 Debian 安装
- 8 Debian 11 VMWare 服务器镜像
- 9 相关链接
本教程通过大量截图详细演示如何安装 Debian 11(Bullseye)最小化服务器。本指南的目的是提供一个最小化系统配置,可作为 howtoforge.com 上我们其他 Debian 11 教程的基础。
1 环境要求
要安装 Debian 11 服务器系统,你需要准备以下内容:
- Debian Buster 网络安装光盘可在此获取:64 位:https://cdimage.debian.org/debian-cd/current/amd64/iso-cd/debian-11.5.0-amd64-netinst.iso (x86_64 / amd64)
- 一条高速的 Internet 连接。
我将使用 Debian 11.3 64 位(amd64)安装介质。
Debian 下载链接会定期变更。如果上述链接已失效,请前往此处获取最新的 Debian netinst 镜像:https://cdimage.debian.org/debian-cd/current/amd64/iso-cd/ 。
2 前置说明
在本教程中,我将使用主机名 server1.example.com,IP 地址为 192.168.0.100,网关为 192.168.0.1。这些设置可能与你的情况不同,因此你需根据实际情况进行替换。
3 Debian 基础系统
将你的 Debian 11(Bullseye)网络安装光盘插入系统(或插入已写入 iso 文件的 U 盘),并从中启动。当你使用 VMware 或 Virtualbox 等虚拟化软件时,请将 Debian 11 minimal iso 文件选为虚拟机 DVD 光驱的源文件。你无需先将其刻录到 CD 或 DVD。
选择 Install(这将启动文本安装程序——如果你更喜欢图形化安装程序,请选择 Graphical install):
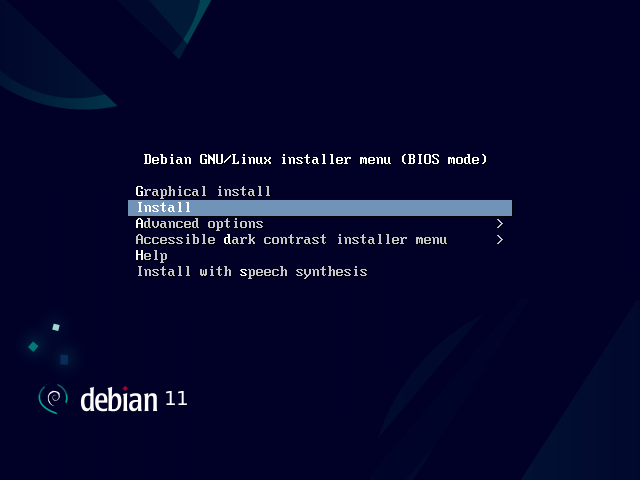
选择你的语言:
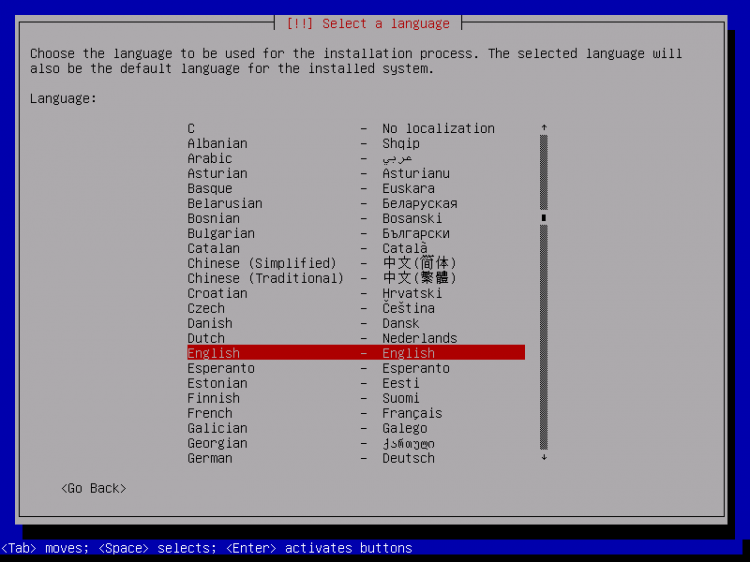
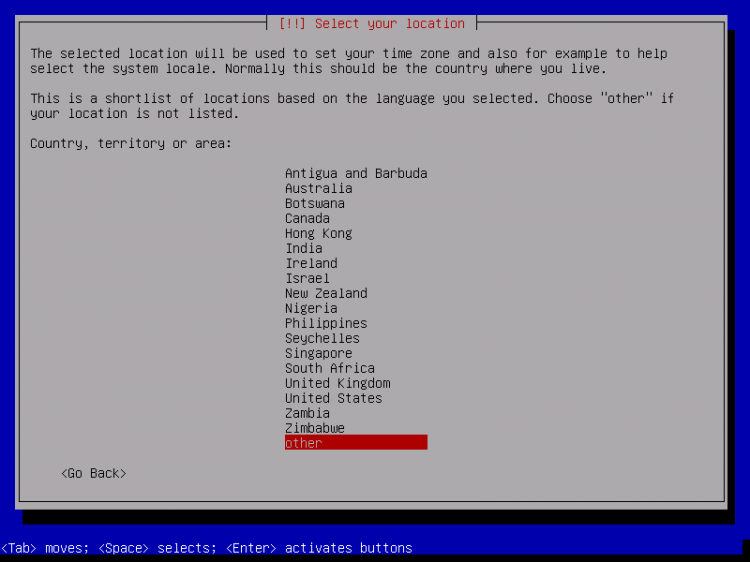
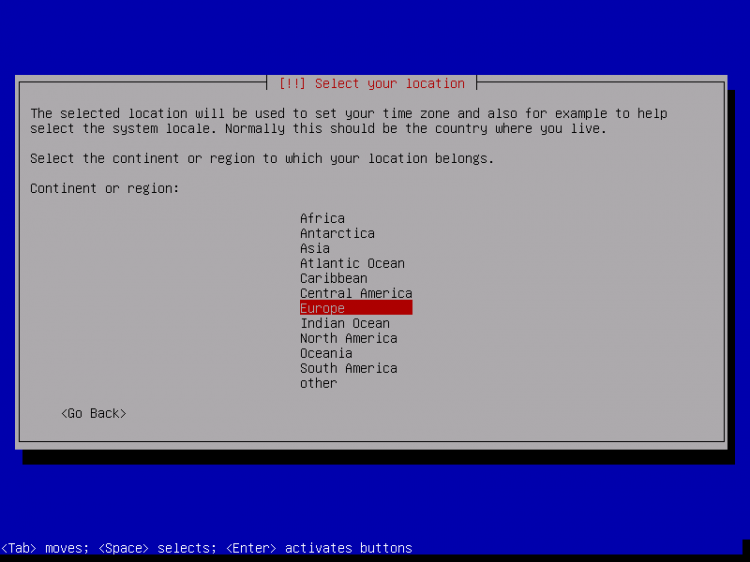
然后选择你的所在位置并选择键盘布局。后续界面会根据你的选择有所不同。只需选择适合你的国家和键盘布局,因为它们决定了 Debian 系统在 shell 中使用的语言以及所使用的键盘布局。就我而言,我会使用德语键盘布局,但希望 shell 中的语言为英语。
选择国家、地区或区域:
再次选择你的位置、地区,以及区域设置和键盘:
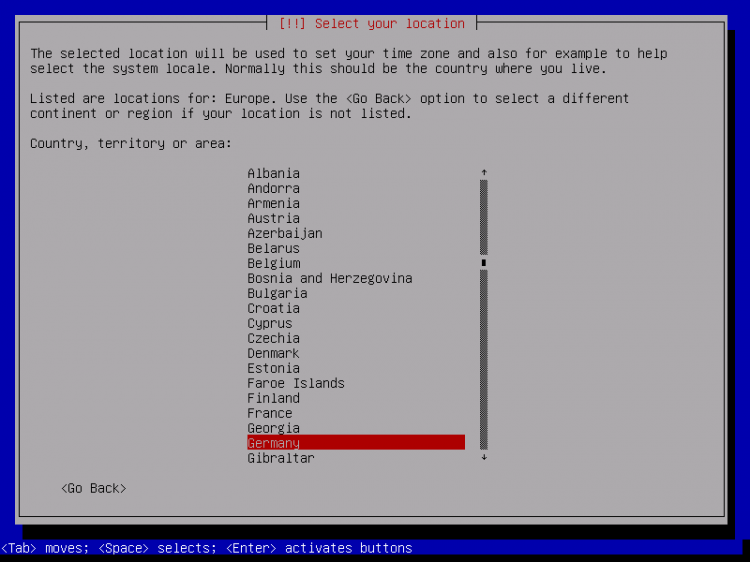
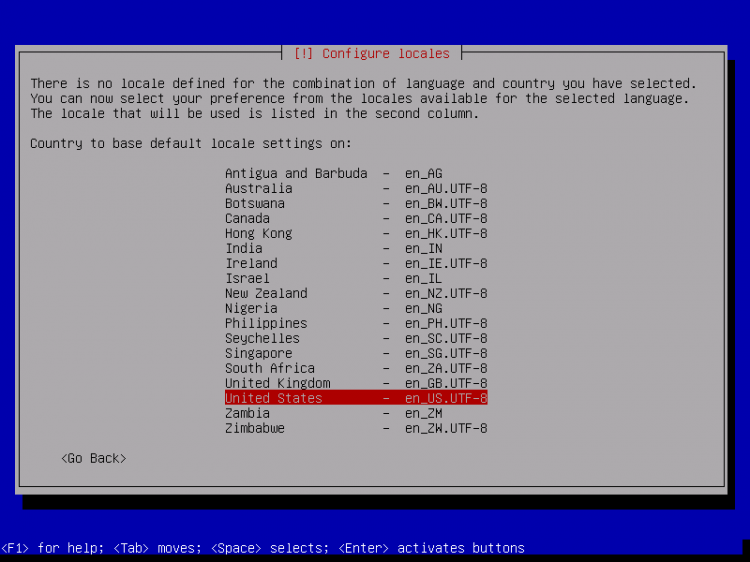
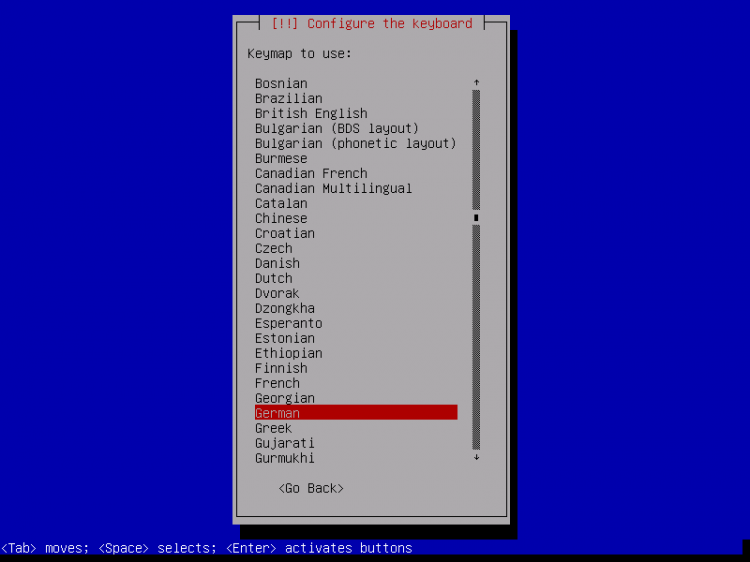
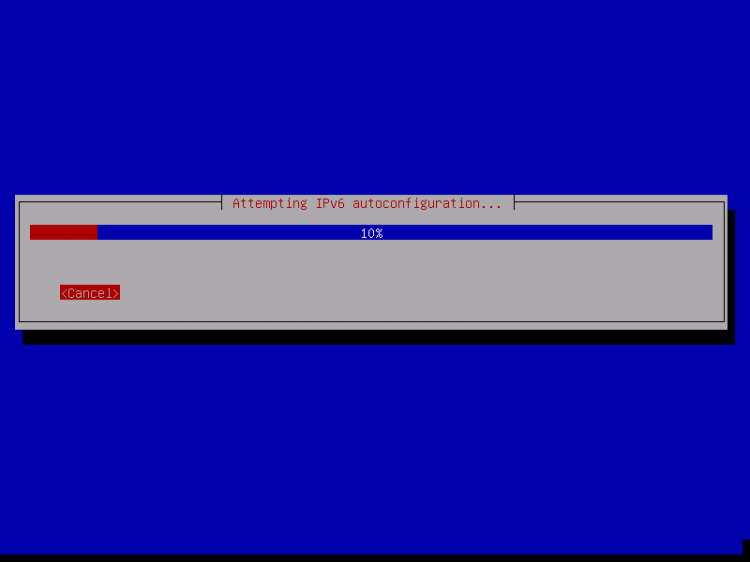
安装程序会检查安装光盘和你的硬件,并在网络中存在 DHCP 服务器时通过 DHCP 配置网络:
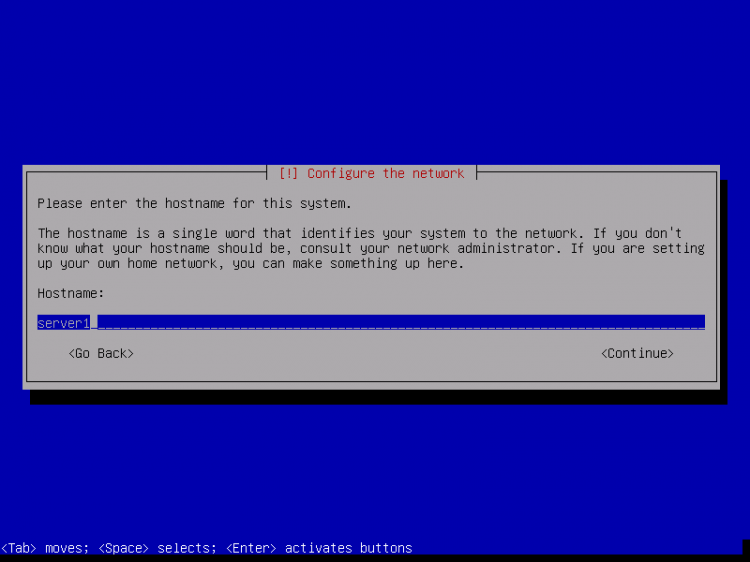
输入主机名。在本例中,我的系统名为 server1.example.com,因此我输入 server1:
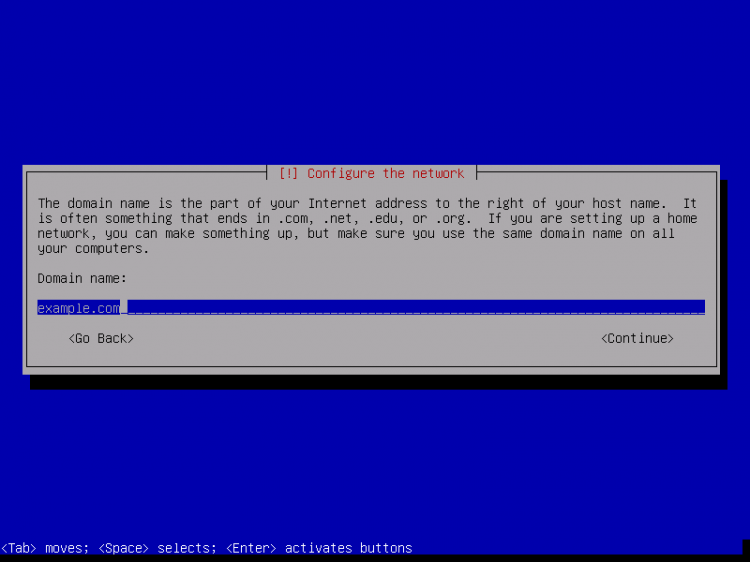
输入你的域名。在本例中,域名为 example.com:
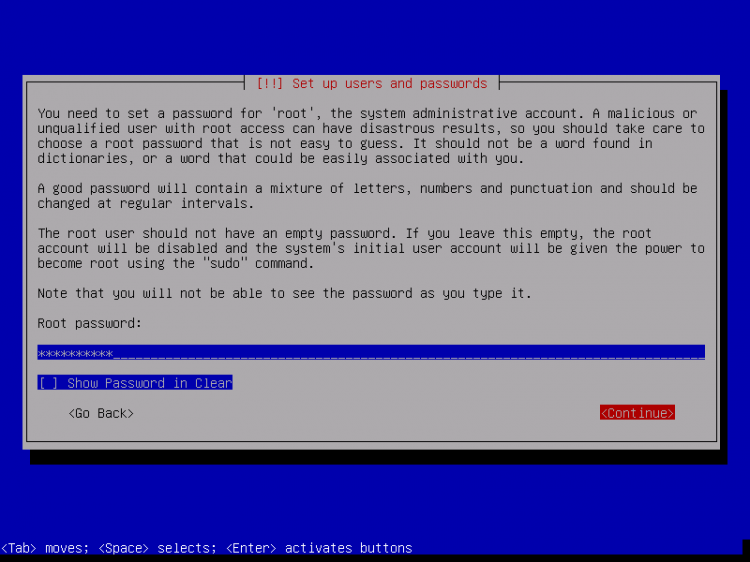
接着,为 root 用户设置一个密码:
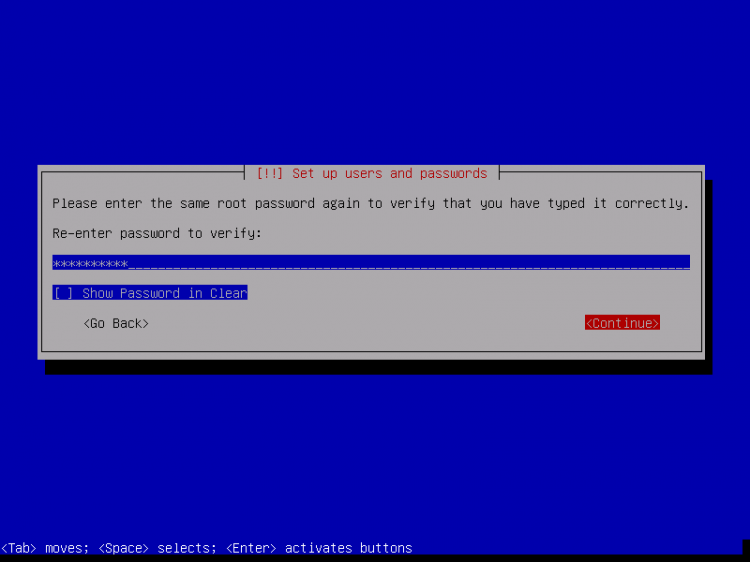
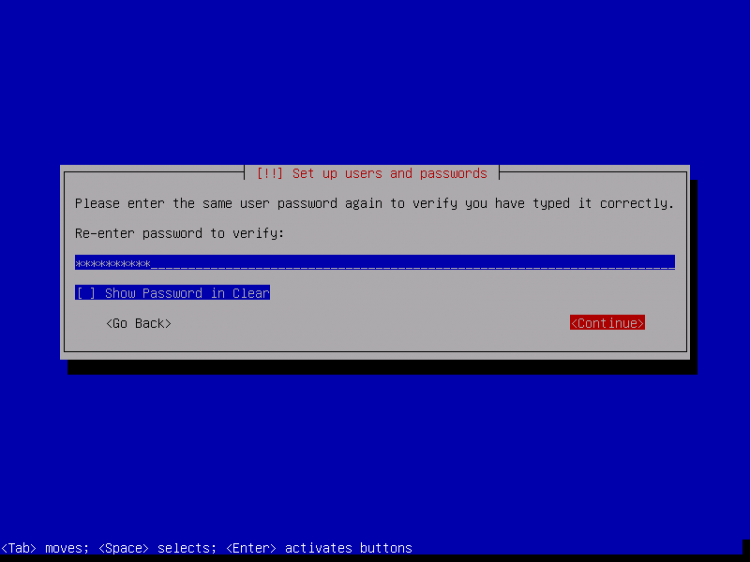
再次确认该密码以避免输入错误:
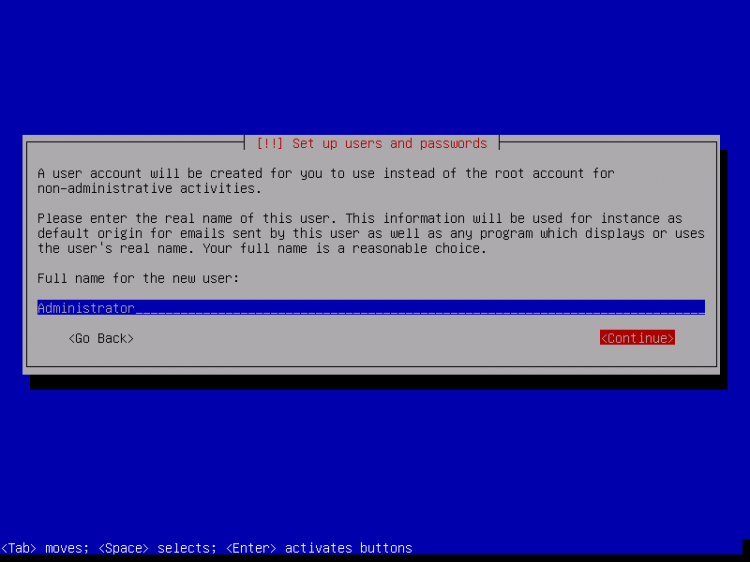
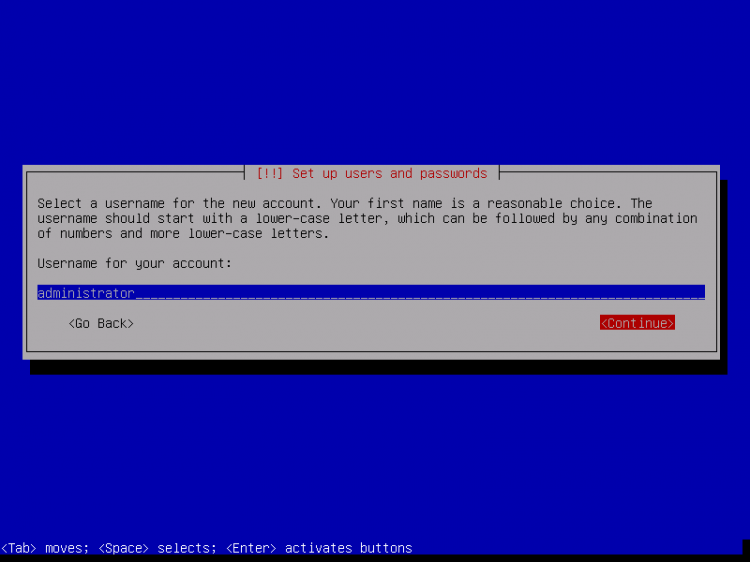
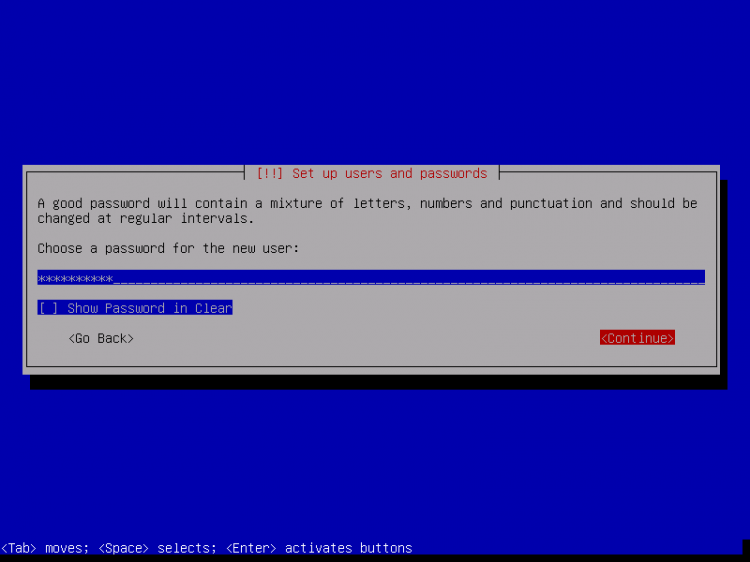
创建一个 Linux 用户账户,例如使用你的姓名或昵称。在本示例安装中,我将使用「administrator」作为用户名,全名为「administrator」(请勿使用 admin 作为用户名,因为在 Debian Linux 中它是一个保留名称):
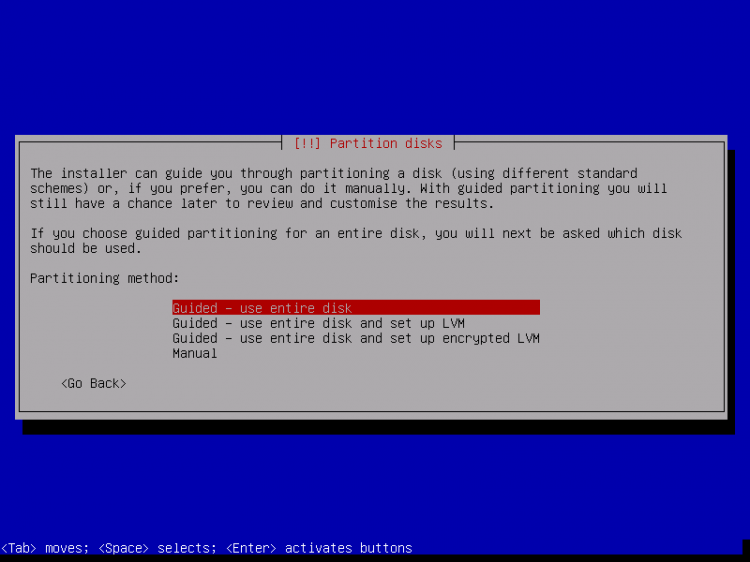
现在你需要对硬盘进行分区。为简单起见,我选择「Guided - use entire disk(引导式——使用整块磁盘)」,这将为 / 文件系统创建一个大分区,并为 swap 创建另一个分区(当然,分区方式完全由你决定——如果你清楚自己在做什么,也可以手动设置分区)。对于 ISPConfig 3 完美服务器之类的托管系统教程,你可能会希望为 / 分配例如 60GB,并创建一个较大的 /var 分区,因为所有网站和邮件数据都存储在 /var 的子目录中。
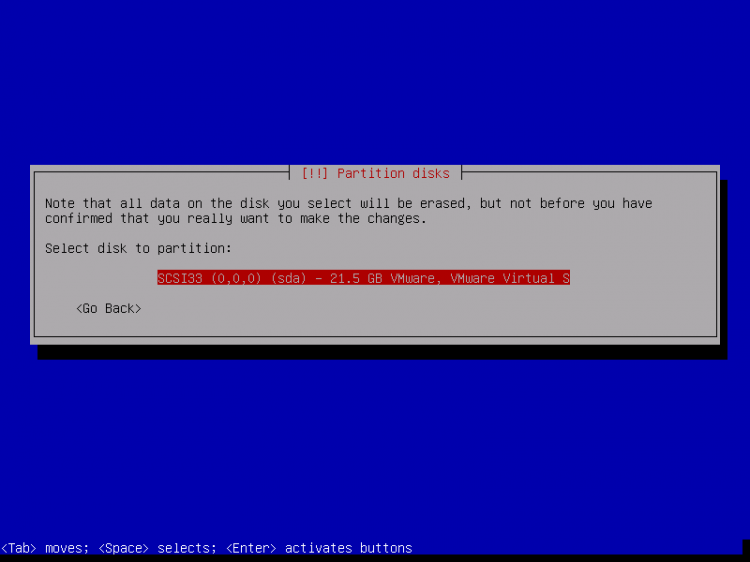
选择你要分区的磁盘:
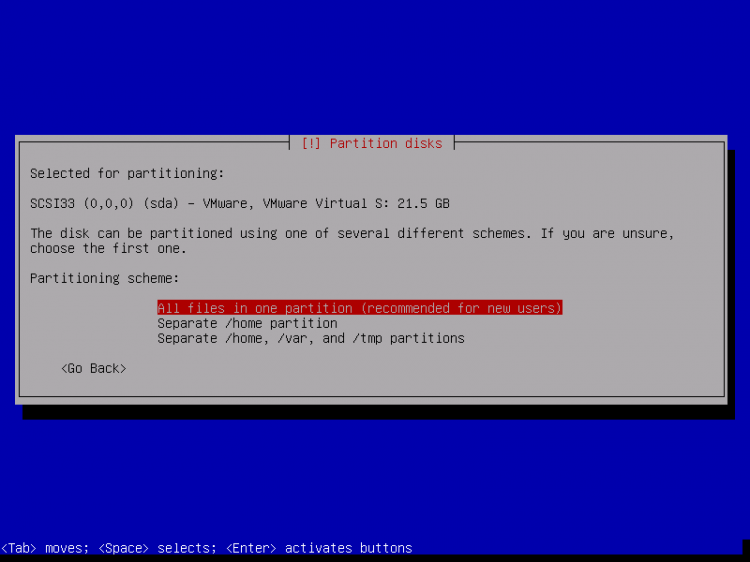
然后选择分区方案。如前所述,为简单起见我选择「All files in one partition(所有文件放在一个分区中,推荐新手使用)」——具体选择什么由你决定:
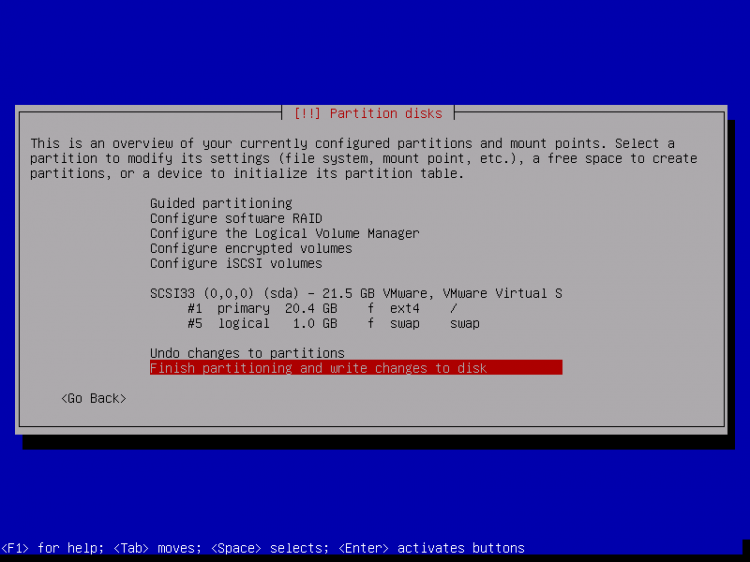
完成后,选择「Finish partitioning and write changes to disk(完成分区并将更改写入磁盘)」:
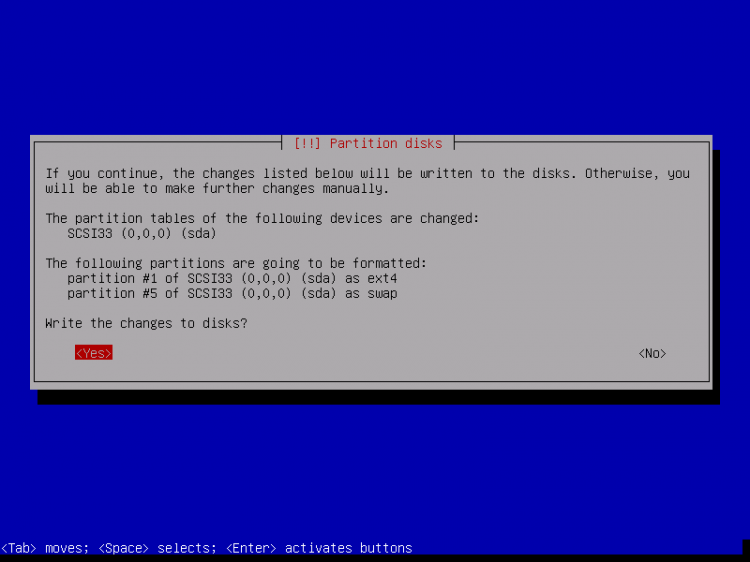
当系统询问「Write changes to disk?(将更改写入磁盘?)」时,选择 Yes:
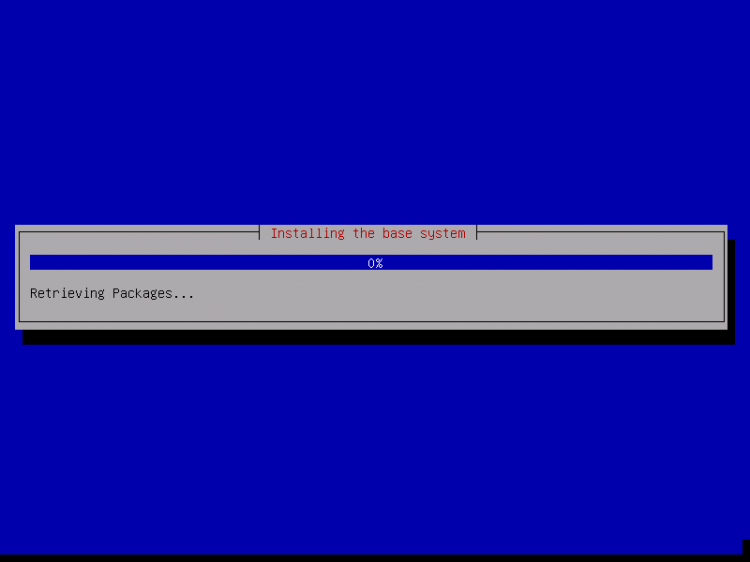
随后,新分区将被创建并格式化。分区创建完成后,基础系统即开始安装:
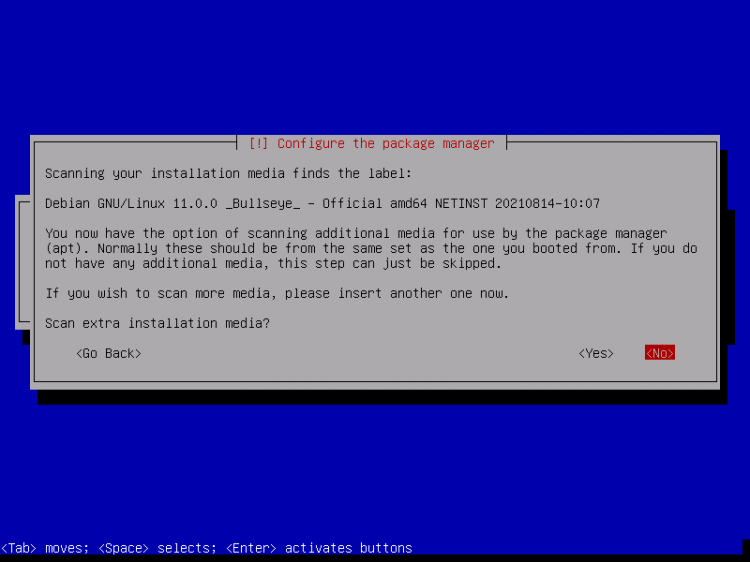
根据你的安装介质不同,可能会弹出以下界面。我将进行基于网络的安装(所有额外的安装包都从 Internet 下载),因此我在此选择不扫描任何额外的安装盘。
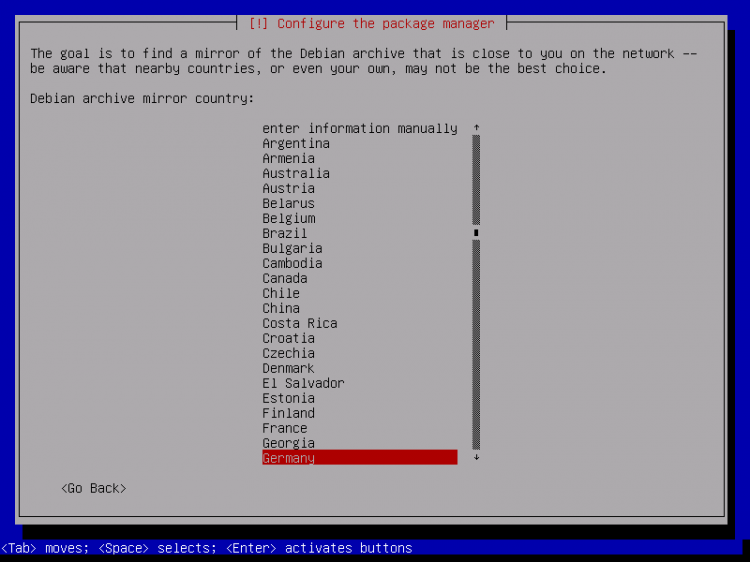
接下来,你必须配置 apt。由于我们使用的 Debian Netinstall 光盘只包含一组最小化的软件包,因此必须使用网络镜像源。选择你要使用的网络镜像源所在的国家(通常为你服务器系统所在的国家):
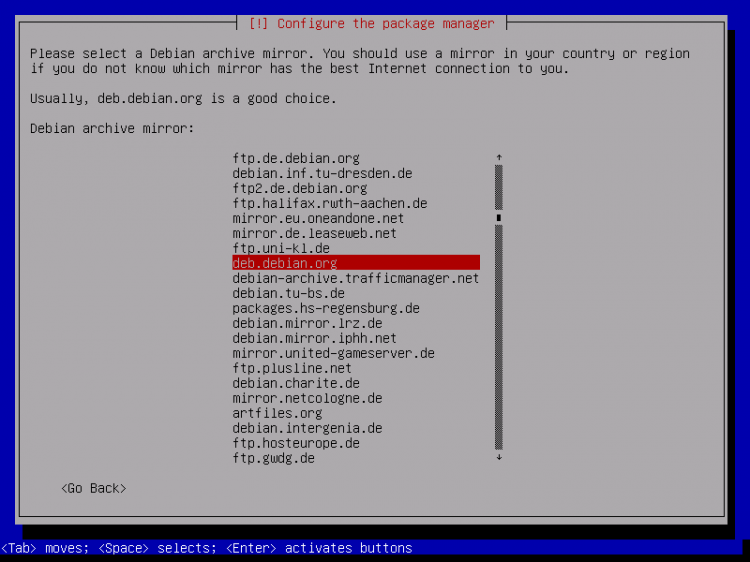
然后选择你希望使用的镜像源(例如 deb.debian.org):
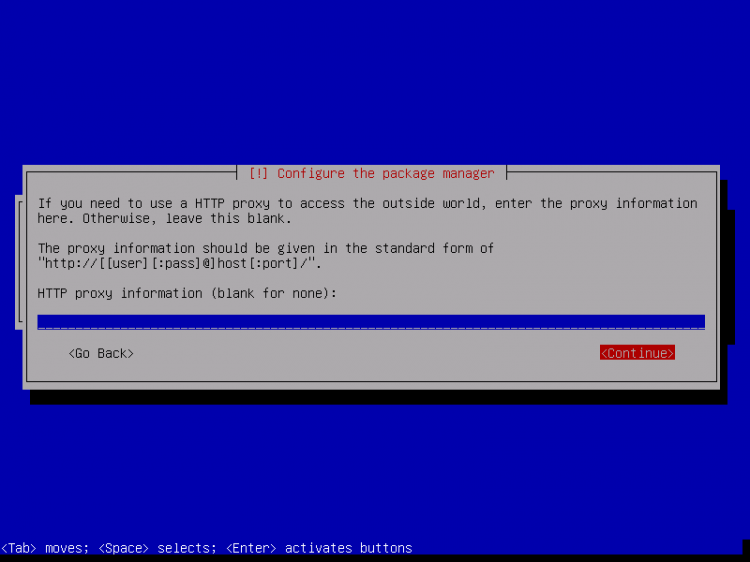
除非你使用 HTTP 代理,否则请将以下字段留空并点击 Continue(继续):
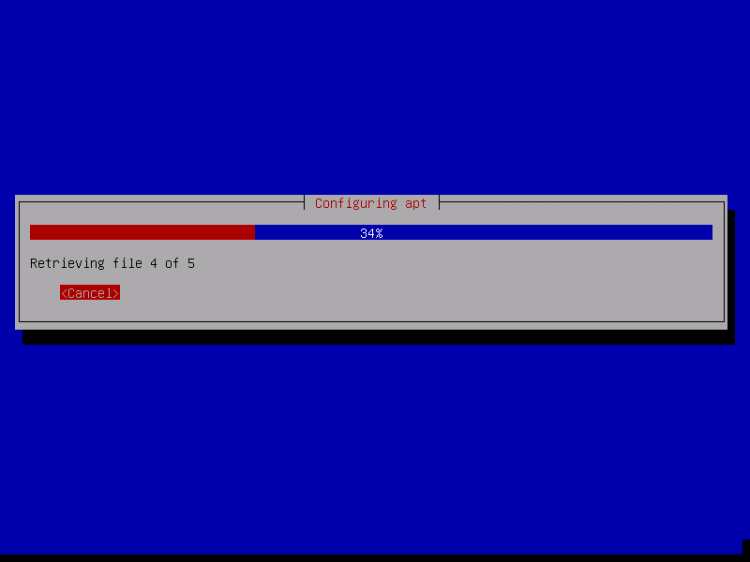
Apt 正在更新其软件包数据库:
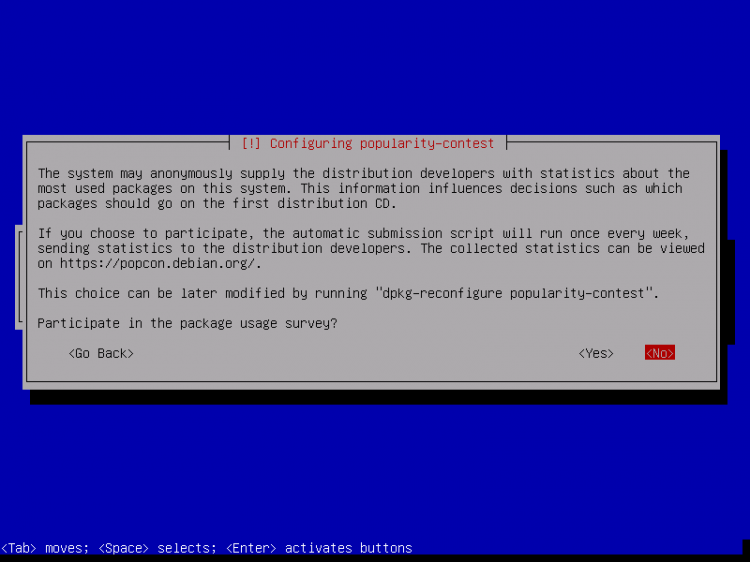
你可以选择 No 跳过软件包使用情况调查:
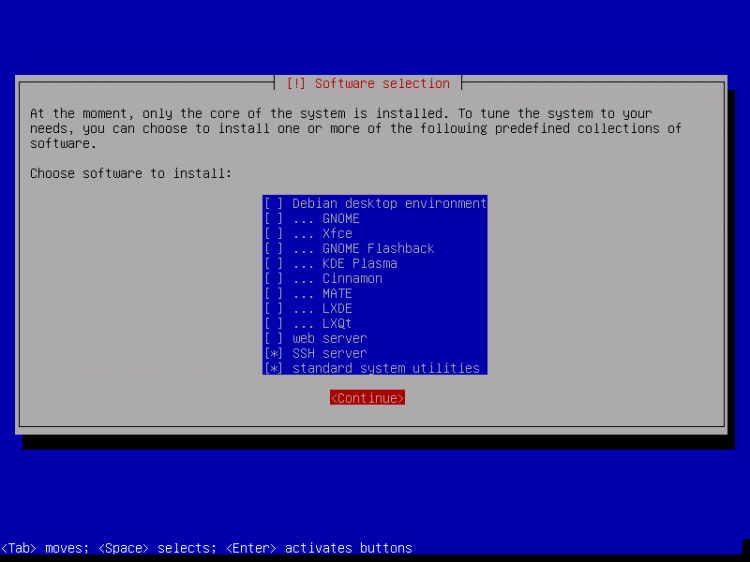
我们选择「Standard system utilities(标准系统工具)」和「SSH server(SSH 服务器)」(这样在安装完成后我就可以立即通过 PuTTY 等 SSH 客户端连接到系统),然后点击 Continue。
有些人可能会认为,不应在最小化服务器上安装标准系统工具。但在我看来,你稍后无论如何都会需要大部分标准工具,因此我会将它们作为基础配置的一部分安装到这台服务器上。
所需的软件包将被下载并安装到系统中:
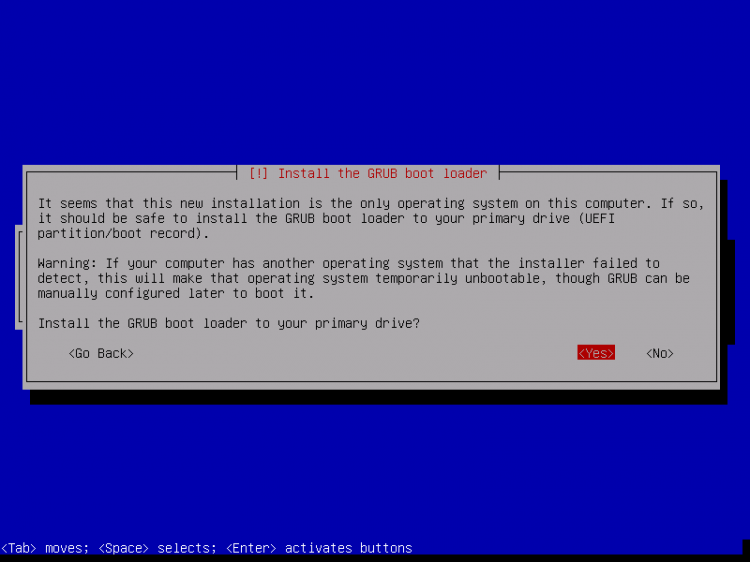
当系统询问「Install the GRUB boot loader to the master boot record?(将 GRUB 引导加载程序安装到主引导记录?)」时,选择 Yes:
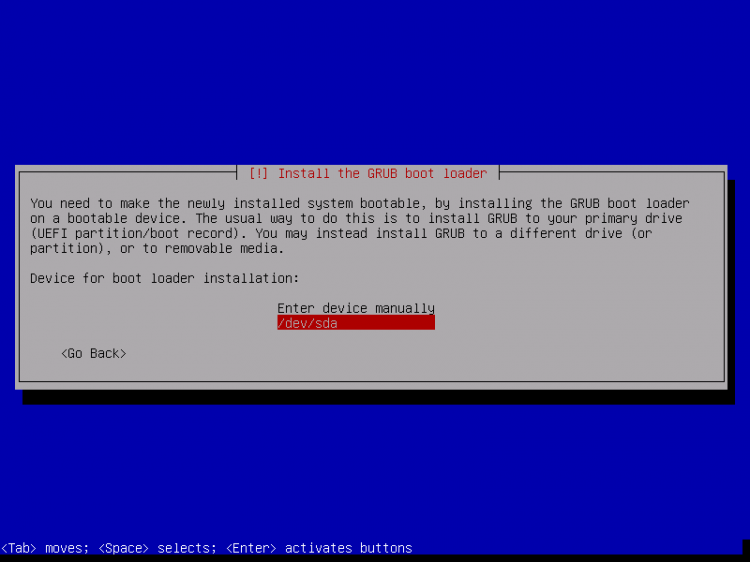
安装程序可能会询问将 Grub 安装到哪个分区。这台服务器只有一块硬盘,因此我在此选择 /dev/sda。
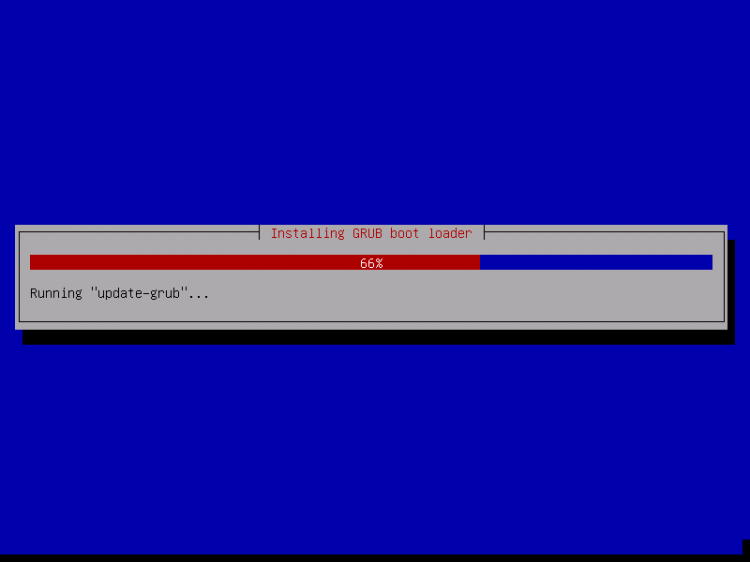
按下回车键,安装程序将安装 Grub 并完成安装。
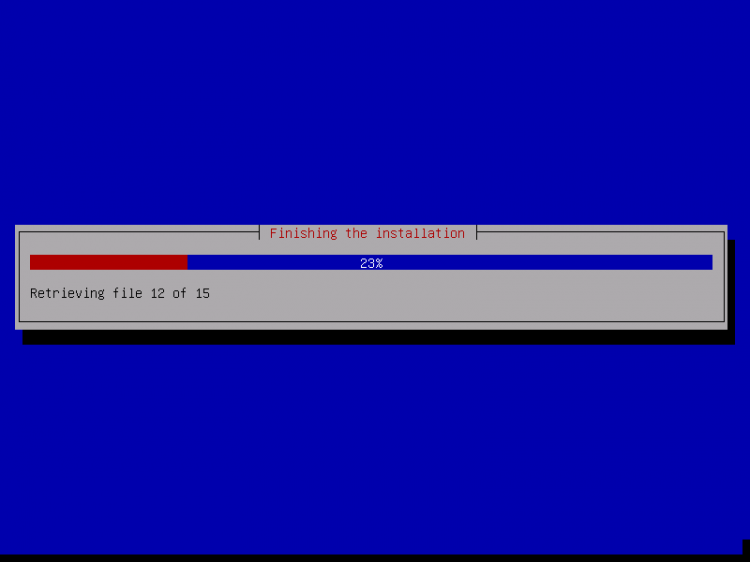
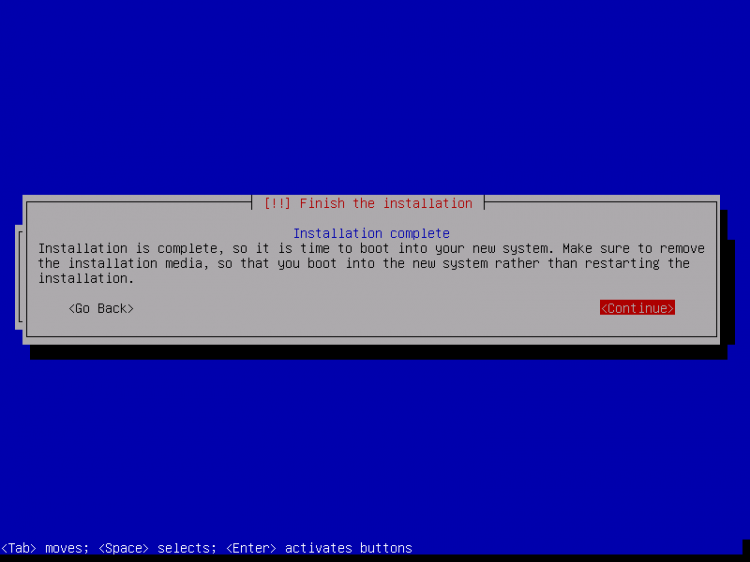
基础系统安装现已完成。从光驱中取出 Debian Netinstall 光盘,并点击 Continue 以重启系统:
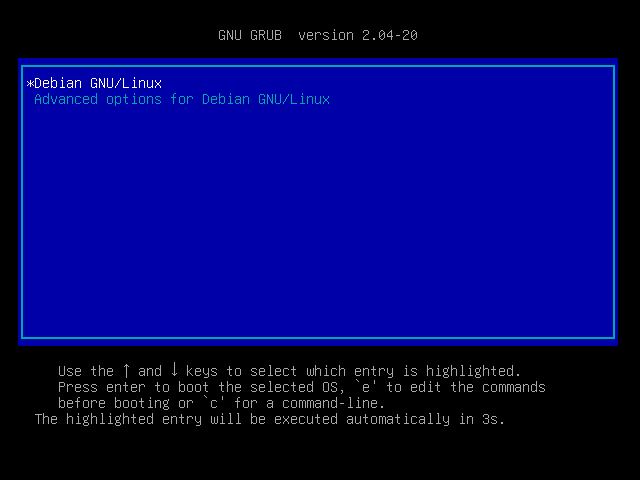
新安装的 Debian 10 服务器的首次启动:首先,你会看到 Grub 引导加载程序的启动界面,按下回车键或等待几秒后,启动过程将自动继续。
几秒钟后,登录提示符应该会出现。
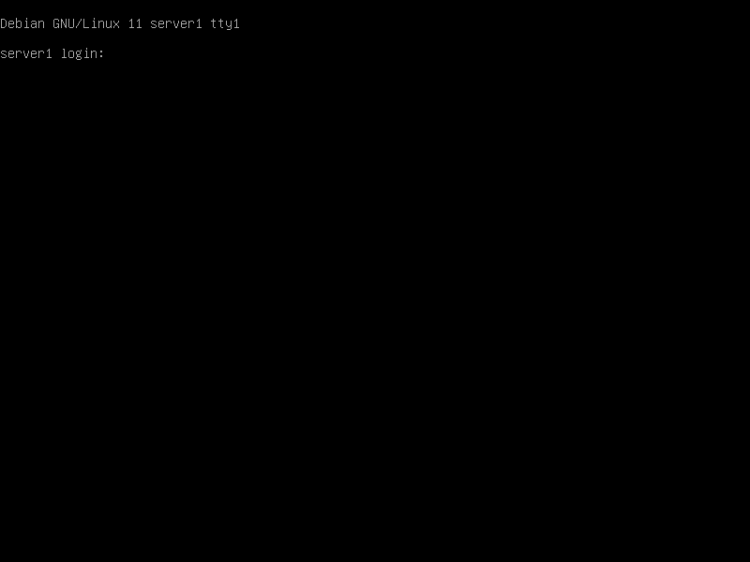
使用用户名「root」和你在安装过程中设置的 root 密码登录。当你通过 SSH 登录时,请使用用户名「administrator」,因为 root 用户已禁用远程登录。然后运行命令「su -」:
su -以成为 root 用户。重要提示:你必须使用带 '-' 的 su 命令,或使用 'su --login',因为这样才能为 root 用户正确初始化 PATH 变量。
进入下一步……
4 安装 SSH 服务器(可选)
如果你在系统安装过程中没有安装 OpenSSH 服务器,现在可以安装:
apt -y install ssh openssh-server从现在起,你可以使用 PuTTY 等 SSH 客户端,从你的工作站连接到你的 Debian Jessie 服务器,并按照本教程的其余步骤操作。
5 安装 shell 编辑器(可选)
我将使用 nano 作为我最喜欢的 shell 文本编辑器。其他人更喜欢 vi,但对初学者来说并不那么容易上手。通过以下命令,我将同时安装这两个编辑器:
apt -y install vim-nox nano(如果你使用其他文本编辑器,例如 joe 或 mc 自带的内置编辑器,则无需执行此操作)。
6 配置网络
你可以通过以下命令获取当前的 IP 地址:
ip a默认情况下,部分网络工具可能不可用。通过以下命令安装软件包:
apt install net-tools由于 Debian 11 安装程序已将我们的系统配置为通过 DHCP 获取网络设置,而服务器应当拥有静态 IP 地址,因此我们现在需要更改该设置。编辑 /etc/network/interfaces 并根据你的需求进行调整(在本示例配置中,我将使用 IP 地址 192.168.0.100)(请注意,我将 allow-hotplug ens33 替换为 auto ens33;否则重启网络不会生效,我们将不得不重启整个系统):
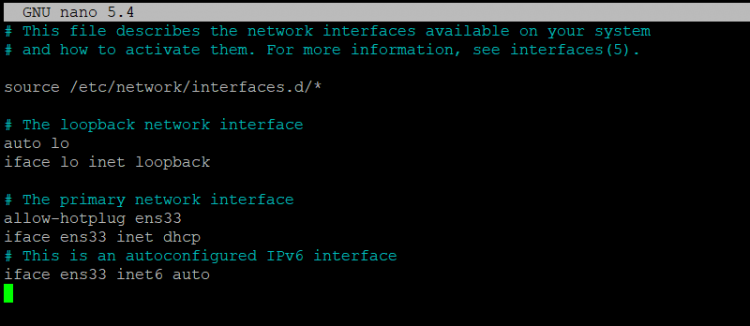
nano /etc/network/interfaces由 apt 安装程序创建的、启用 DHCP 的 interfaces 文件如下:
# This file describes the network interfaces available on your system
# and how to activate them. For more information, see interfaces(5).
source /etc/network/interfaces.d/*
# The loopback network interface
auto lo
iface lo inet loopback
# The primary network interface
allow-hotplug ens33
iface ens33 inet dhcp
# This is an autoconfigured IPv6 interface
iface ens33 inet6 auto
或者参考以下截图:
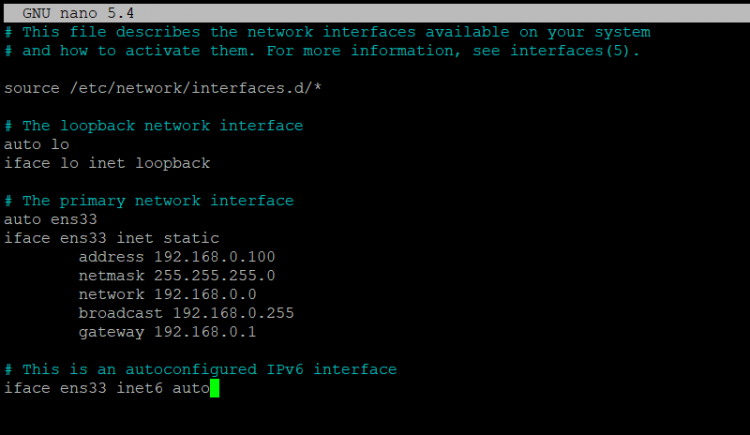
下面是已配置静态 IP 192.168.0.100 的编辑后 interfaces 文件。
# This file describes the network interfaces available on your system
# and how to activate them. For more information, see interfaces(5).
source /etc/network/interfaces.d/*

# The loopback network interface
auto lo
iface lo inet loopback

# The primary network interface
auto ens33
iface ens33 inet static
        address 192.168.0.100
        netmask 255.255.255.0
        network 192.168.0.0
        broadcast 192.168.0.255
        gateway 192.168.0.1
# This is an autoconfigured IPv6 interface
iface ens33 inet6 auto
编辑后的文件应如下所示:
然后重启你的网络:
systemctl restart networking然后编辑 /etc/hosts,使其内容如下:
nano /etc/hosts127.0.0.1 localhost.localdomain localhost 192.168.0.100 server1.example.com server1 # The following lines are desirable for IPv6 capable hosts ::1 localhost ip6-localhost ip6-loopback ff02::1 ip6-allnodes ff02::2 ip6-allrouters
现在编辑主机名,以防你在安装程序中没有选择最终的主机名
nano /etc/hostname/etc/hostname 文件中包含不带域名部分的主机名,因此在我们的示例中仅为「server1」。
然后重启服务器以应用主机名更改:
systemctl reboot再次登录后,运行以下命令:
hostname
hostname -f
以验证新主机名是否已正确设置。输出应如下所示:
root@server1:/home/administrator# hostname
server1
root@server1:/home/administrator# hostname -f
server1.example.com
root@server1:/home/administrator#
7 更新你的 Debian 安装
首先,确保你的 /etc/apt/sources.list 包含 buster/updates 仓库(这可确保你始终获得最新的更新),并且 contrib 和 non-free 仓库已启用。
nano /etc/apt/sources.list# deb cdrom:[Debian GNU/Linux 11.0.0 _Bullseye_ - Official amd64 NETINST 20210814-10:07]/ bullseye main #deb cdrom:[Debian GNU/Linux 11.0.0 _Bullseye_ - Official amd64 NETINST 20210814-10:07]/ bullseye main deb http://deb.debian.org/debian/ bullseye main contrib non-free deb-src http://deb.debian.org/debian/ bullseye main contrib non-free deb http://security.debian.org/debian-security bullseye-security main contrib non-free deb-src http://security.debian.org/debian-security bullseye-security main contrib non-free # bullseye-updates, to get updates before a point release is made; # see https://www.debian.org/doc/manuals/debian-reference/ch02.en.html#_updates_and_backports deb http://deb.debian.org/debian/ bullseye-updates main contrib non-free deb-src http://deb.debian.org/debian/ bullseye-updates main contrib non-free # This system was installed using small removable media # (e.g. netinst, live or single CD). The matching "deb cdrom" # entries were disabled at the end of the installation process. # For information about how to configure apt package sources, # see the sources.list(5) manual.
运行
apt update以更新 apt 软件包数据库,以及
apt upgrade以安装最新的更新(如果有的话)。
8 Debian 11 VMWare 服务器镜像
本教程提供了一个可直接使用的虚拟机镜像,格式为 ovf/ova,兼容 VMWare 和 Virtualbox。该虚拟机镜像使用以下登录信息:
SSH / Shell 登录
用户名:administrator 密码:howtoforge
用户名:root 密码:howtoforge
该虚拟机的 IP 为 192.168.0.100,可在 /etc/network/interfaces 文件中更改。请修改上述所有密码以保护该虚拟机的安全。
9 相关链接
- Debian:http://www.debian.org/