
本教程适用于以下操作系统版本
- Ubuntu 22.04(Jammy Jellyfish)
- Ubuntu 20.04(Focal Fossa)
- Ubuntu 18.04(Bionic Beaver)
本页内容
- 先决条件
- 开始之前
- 安装并配置 MariaDB 数据库
- 在 Ubuntu 22.04 上安装 ERPNext
- 为生产环境配置 ERPNext
- 访问 ERPNext Web 界面
- 使用 Let's Encrypt SSL 保护 ERPNext
- 结语
ERPNext 是一款免费的开源 ERP 软件,被制造商、分销商和服务商广泛使用。它由 Python、JavaScript 和 Frappe Framework 构建。它现代化、易用、免费,专为中小型企业设计,可帮助企业管理者其业务运营的各个方面。全球数千家企业使用它来管理自身的 ERP 流程。它是目前最优秀的 ERP 系统之一,支持制造、分销、零售、贸易、服务、教育、非营利组织等众多领域。
在本教程中,我们将向您展示如何在 Ubuntu 22.04 服务器上安装 ERPNext 软件。
先决条件
- 一台运行 Ubuntu 22.04 的服务器。
- 一个已指向您服务器的有效域名。
- 服务器上已配置 root 密码。
开始之前
首先,您需要在系统上安装一些 Python 依赖项。您可以使用以下命令一次性安装它们:
apt-get install python3-dev libffi-dev git python3-pip python3-testresources libssl-dev wkhtmltopdf gcc g++ make python3.10-venv -y所有 Python 依赖项安装完成后,您需要在服务器上安装 Node.js。
首先,使用以下命令添加 Node.js 软件源:
curl -sL https://deb.nodesource.com/setup_16.x | bash -接下来,使用以下命令安装 Node.js 和 Redis 服务器:
apt-get install nodejs redis-server -y两个软件包安装完成后,运行以下命令安装 Yarn 包:
npm install -g yarn完成后,即可进入下一步。
安装并配置 MariaDB 数据库
默认情况下,MariaDB 在 Ubuntu 22.04 的默认软件源中即可获取。您可以使用以下命令安装它:
apt-get install mariadb-server -y安装完成后,使用以下命令加固 MariaDB 并设置 MariaDB 的 root 密码:
mysql_secure_installation如下方所示回答所有问题,以设置 MariaDB root 密码并加固安装:
Enter current password for root (enter for none):
Set root password? [Y/n] Y
New password:
Re-enter new password:
Remove anonymous users? [Y/n] Y
Disallow root login remotely? [Y/n] Y
Remove test database and access to it? [Y/n] Y
Reload privilege tables now? [Y/n] Y
MariaDB 加固完成后,使用以下命令登录 MariaDB 控制台:
mysql -u root -p接下来,您需要将 MariaDB 的 Innodb fileformat 改为 Barracuda。可以通过编辑文件 /etc/mysql/mariadb.conf.d/50-server.cnf 来实现:
nano /etc/mysql/mariadb.conf.d/50-server.cnf添加或修改以下行:
[mysqld]
innodb-file-format=barracuda
innodb-file-per-table=1
innodb-large-prefix=1
character-set-client-handshake = FALSE
character-set-server = utf8mb4
collation-server = utf8mb4_unicode_ci
保存并关闭文件,然后重启 MariaDB 服务以使更改生效:
systemctl restart mariadb在 Ubuntu 22.04 上安装 ERPNext
首先,使用以下命令创建一个用于运行 ERPNext 的新用户:
useradd -m -s /bin/bash erpnext接下来,使用以下命令为 ERPNext 用户设置密码:
passwd erpnext接下来,使用以下命令将 ERPNext 用户添加到 sudo 组:
usermod -aG sudo erpnext接下来,登录 ERPNext 用户并使用以下命令设置环境变量:
su - erpnext
nano ~/.bashrc
添加以下行:
PATH=$PATH:~/.local/bin/
保存文件,然后使用以下命令使环境变量生效:
source ~/.bashrc接下来,使用以下命令为 ERPNext 创建一个目录:
sudo mkdir /opt/bench接下来,将所有权设置为 erpnext 用户:
sudo chown -R erpnext:erpnext /opt/bench接下来,切换到 /opt/bench 目录并从 GitHub 克隆 bench 仓库:
cd /opt/bench
git clone https://github.com/frappe/bench bench-repo
接下来,使用 pip3 命令安装 bench 仓库:
pip3 install -e bench-repo安装完成后,使用以下命令用 Frappe 框架初始化 bench 目录:
bench init erpnext您应看到如下输出:
? Built js/checkout.min.js
? Built js/dialog.min.js
? Built js/social.min.js
? Built js/web_form.min.js
? Built js/list.min.js
? Built js/chat.js
Browserslist: caniuse-lite is outdated. Please run next command `yarn upgrade caniuse-lite browserslist`
? Built css/frappe-rtl.css
? Built css/printview.css
? Built js/bootstrap-4-web.min.js
? Built js/barcode_scanner.min.js
? Built css/list.min.css
? Built css/report.min.css
? Built frappe/css/email.css
? Built js/frappe-recorder.min.js
? Built js/desk.min.js
? Built css/frappe-chat-web.css
? Built js/frappe-web.min.js
? Built css/form.min.css
? Built css/web_form.css
? Built css/desk.min.css
? Built css/frappe-web-b4.css
? Built js/control.min.js
? Built js/form.min.js
? Built js/data_import_tools.min.js
? Built js/report.min.js
?  Done in 111.35s
Done in 113.33s.
SUCCESS: Bench erpnext initialized
接下来,切换到 erpnext 目录并使用以下命令创建一个新的 ERPNext 站点:
cd /opt/bench/erpnext
bench new-site erp.example.com
系统将提示您输入 MariaDB root 密码和 Administrator 密码,如下所示:
MySQL root password:

Installing frappe...
Updating DocTypes for frappe        : [========================================] 100%
Updating country info               : [========================================] 100%
Set Administrator password:
Re-enter Administrator password:
*** Scheduler is disabled ***
Current Site set to erp.example.com
至此,ERPNext 已安装在您的系统中。
为生产环境配置 ERPNext
接下来,您需要安装 Supervisor 来管理 ERPNext 进程,并将 Nginx 配置为反向代理。
首先,切换为 ERPNext 用户,然后使用以下命令安装 Supervisor 和 Nginx:
su - erpnext
sudo apt-get install supervisor nginx -y
接下来,使用以下命令安装 frappe-bench:
sudo pip3 install frappe-bench接下来,切换到 /opt/bench/erpnext 目录,并使用以下命令为生产环境配置 ERPNext:
cd /opt/bench/erpnext
sudo /home/erpnext/.local/bin/bench setup production erpnext
ERPNext 配置完成后,您应看到如下输出:
PLAY RECAP ************************************************************************************************************************************
localhost                  : ok=8    changed=4    unreachable=0    failed=0    skipped=1    rescued=0    ignored=0

$ sudo systemctl restart supervisor
Port configuration list:

Site erp.example.com assigned port: 80
$ /usr/bin/supervisorctl reread
No config updates to processes
$ /usr/bin/supervisorctl update
$ sudo /usr/sbin/nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
$ sudo systemctl reload nginx
至此,ERPNext 已配合 Nginx 完成生产环境的配置。
访问 ERPNext Web 界面
现在,打开您的网页浏览器并输入网址 http://erp.example.com,您将被重定向到 ERPNext 登录页面:
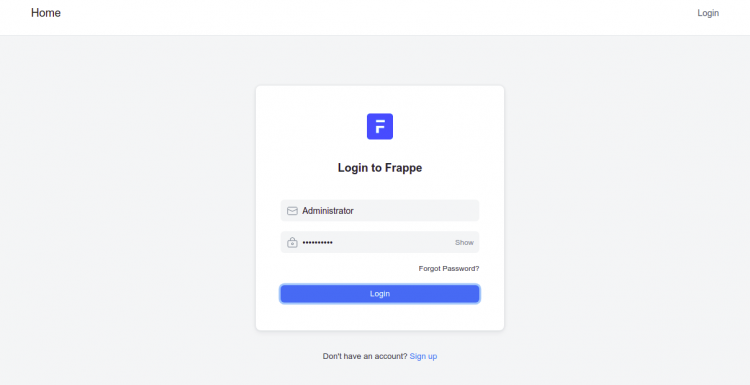
输入用户名 Administrator 以及您之前设置的密码,然后点击“登录”按钮。您应看到如下页面:
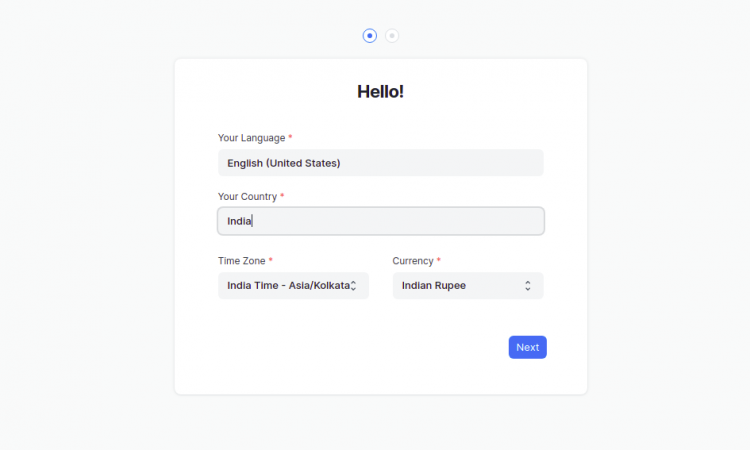
选择您所需的语言、国家/地区、时区和货币,然后点击“下一步”按钮。您应看到如下页面:
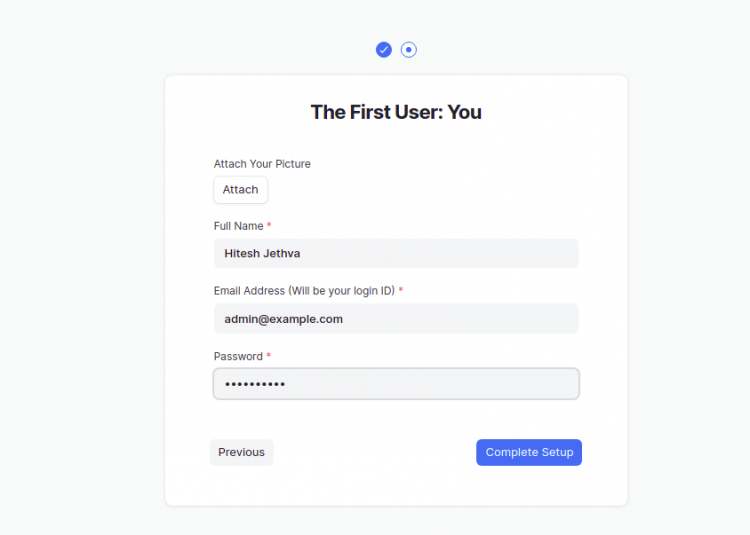
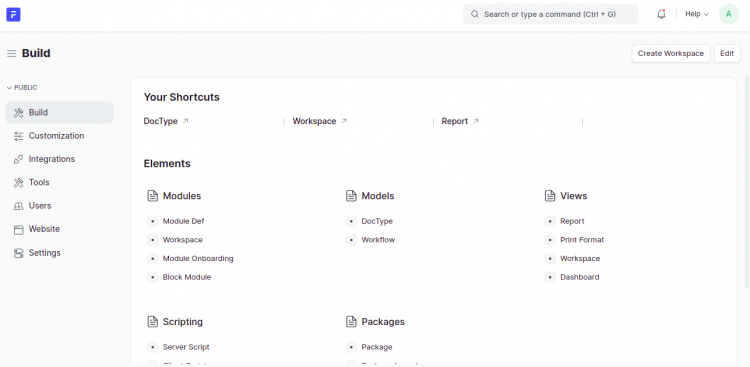
填写您的姓名、电子邮件和密码,然后点击“完成设置”按钮。在接下来的页面中您将看到 ERPNext 仪表板:
使用 Let's Encrypt SSL 保护 ERPNext
首先,您需要安装 Certbot 客户端来安装和管理 Let's Encrypt SSL。您可以使用以下命令安装它:
sudo apt-get install certbot python3-certbot-nginx -y安装完成后,运行以下命令为您的域名安装并配置 Let's Encrypt SSL:
sudo certbot --nginx -d erp.example.com系统将要求您提供电子邮件并接受服务条款,如下所示:
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator nginx, Installer nginx
Enter email address (used for urgent renewal and security notices) (Enter 'c' to
cancel):
[email protected]


- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at
https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf. You must
agree in order to register with the ACME server at
https://acme-v02.api.letsencrypt.org/directory
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(A)gree/(C)ancel: A

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing to share your email address with the Electronic Frontier
Foundation, a founding partner of the Let's Encrypt project and the non-profit
organization that develops Certbot? We'd like to send you email about our work
encrypting the web, EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: Y
Obtaining a new certificate
Performing the following challenges:
http-01 challenge for erp.example.com
Waiting for verification...
Cleaning up challenges
Deploying Certificate to VirtualHost /etc/nginx/conf.d/erpnext.conf
接下来,选择是否将 HTTP 流量重定向到 HTTPS,如下所示:
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
1: No redirect - Make no further changes to the webserver configuration.
2: Redirect - Make all requests redirect to secure HTTPS access. Choose this for
new sites, or if you're confident your site works on HTTPS. You can undo this
change by editing your web server's configuration.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Select the appropriate number [1-2] then [enter] (press 'c' to cancel): 2
输入 2 并按 Enter 键完成该过程。您应看到如下输出:
Redirecting all traffic on port 80 to ssl in /etc/nginx/conf.d/erpnext.conf

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Congratulations! You have successfully enabled https://erp.example.com

You should test your configuration at:
https://www.ssllabs.com/ssltest/analyze.html?d=erp.example.com
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/erp.example.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/erp.example.com/privkey.pem
   Your cert will expire on 2022-09-11. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot again
   with the "certonly" option. To non-interactively renew *all* of
   your certificates, run "certbot renew"
 - Your account credentials have been saved in your Certbot
   configuration directory at /etc/letsencrypt. You should make a
   secure backup of this folder now. This configuration directory will
   also contain certificates and private keys obtained by Certbot so
   making regular backups of this folder is ideal.
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le

 - We were unable to subscribe you the EFF mailing list because your
   e-mail address appears to be invalid. You can try again later by
   visiting https://act.eff.org.
至此,您的 ERPNext 网站已通过 Let's Encrypt SSL 得到保护。您现在可以使用 HTTPS 协议安全地访问您的网站。
结语
恭喜!您已成功在 Ubuntu 22.04 上使用 Nginx 和 Let's Encrypt SSL 安装了 ERPNext。如果您有任何疑问,请随时向我提问。您可以访问 ERPNext 文档页面以获取更多信息。