
本页内容
- 先决条件
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装所需软件包
- 第 3 步 - 安装 Graphite 和 Graphite Web
- 第 4 步 - 安装并配置 PostgreSQL
- 第 5 步 - 配置 Graphite Carbon 和 Web 配置 Carbon 配置 Graphite Web
- 第 6 步 - 配置 Apache
- 第 7 步 - 安装 Nginx
- 第 8 步 - 安装 SSL
- 第 9 步 - 配置 Nginx
- 第 10 步 - 访问并使用 Graphite
- 结论
- 配置 Carbon
- 配置 Graphite Web
Graphite 是一款开源工具,用于跟踪和绘制计算机系统的性能图表。你可以使用它来跟踪网站、应用程序、业务服务和联网服务器的性能。它具有高度的灵活性,可以灵活配置,让你既能获得所跟踪指标的详细呈现,也能掌握其性能和运行状况的整体概览。
Graphite 由多个组件构成:Web 应用程序、一个名为 Carbon 的存储后端,以及一个名为 whisper 的数据库库。在本教程中,你将学习如何在 Ubuntu 22.04 服务器上安装并配置 Graphite。
先决条件
- 一台运行 Ubuntu 22.04 的服务器。
- 一个指向该服务器的完全限定域名(FQDN)。在本教程中,我们将使用 graphite.example.com 域名。
- 一个具有 sudo 权限的非 root 用户。
- uncomplicated Firewall(UFW)已启用并正在运行。
- 确保系统已更新。$ sudo apt update && sudo apt upgrade
- 安装基础工具软件包。其中部分可能已安装。$ sudo apt install wget curl nano unzip -y
一台运行 Ubuntu 22.04 的服务器。
一个指向该服务器的完全限定域名(FQDN)。在本教程中,我们将使用 graphite.example.com 域名。
一个具有 sudo 权限的非 root 用户。
uncomplicated Firewall(UFW)已启用并正在运行。
确保系统已更新。
$ sudo apt update && sudo apt upgrade
安装基础工具软件包。其中部分可能已安装。
$ sudo apt install wget curl nano unzip -y
第 1 步 - 配置防火墙
在安装任何软件包之前,第一步是配置防火墙以允许 HTTP 和 HTTPS 连接。
检查防火墙的状态。
$ sudo ufw status
你应该会看到类似以下的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
允许 HTTP 和 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
再次检查状态以确认。
$ sudo ufw status
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
第 2 步 - 安装所需软件包
我们将使用 PIP(Python 包管理器)安装 Graphite。第一步是安装安装所需的软件包。
$ sudo apt install vim python3-dev python3-pip libcairo2-dev libffi-dev build-essential
第 3 步 - 安装 Graphite 和 Graphite Web
我们将在 /opt/graphite 目录中安装 Graphite。
$ export PYTHONPATH="/opt/graphite/lib/:/opt/graphite/webapp/"
$ sudo pip install --no-binary=:all: https://github.com/graphite-project/whisper/tarball/master
$ sudo pip install --no-binary=:all: https://github.com/graphite-project/carbon/tarball/master
$ sudo pip install --no-binary=:all: https://github.com/graphite-project/graphite-web/tarball/master
第 4 步 - 安装并配置 PostgreSQL
我们将使用 PostgreSQL 官方的 APT 仓库进行安装。运行以下命令以添加 PostgreSQL 的 GPG 密钥。
$ curl https://www.postgresql.org/media/keys/ACCC4CF8.asc | gpg --dearmor | sudo tee /usr/share/keyrings/postgresql-key.gpg >/dev/null
将 APT 仓库添加到你的软件源列表。
$ sudo sh -c 'echo "deb [signed-by=/usr/share/keyrings/postgresql-key.gpg arch=amd64] http://apt.postgresql.org/pub/repos/apt $(lsb_release -cs)-pgdg main" > /etc/apt/sources.list.d/pgdg.list'
更新系统软件仓库。
$ sudo apt update
现在,你可以使用以下命令安装 PostgreSQL 及辅助软件包。
$ sudo apt install postgresql postgresql-contrib libpq-dev
检查 PostgreSQL 服务的状态。
$ sudo systemctl status postgresql
? postgresql.service - PostgreSQL RDBMS
     Loaded: loaded (/lib/systemd/system/postgresql.service; enabled; vendor preset: enabled)
     Active: active (exited) since Tue 2022-09-27 10:09:35 UTC; 4s ago
    Process: 4456 ExecStart=/bin/true (code=exited, status=0/SUCCESS)
   Main PID: 4456 (code=exited, status=0/SUCCESS)
        CPU: 1ms

Sep 27 10:09:35 matrix systemd[1]: Starting PostgreSQL RDBMS...
Sep 27 10:09:35 matrix systemd[1]: Finished PostgreSQL RDBMS.
你可以看到该服务默认已启用并正在运行。
登录到 PostgreSQL shell。
$ sudo -su postgres psql
为 Graphite 创建一个数据库用户。
postgres=# CREATE USER graphite WITH PASSWORD 'your_password';
为 Graphite 创建一个数据库,并将所有权赋予 graphite 用户。
postgres=# CREATE DATABASE graphitedb WITH OWNER graphite;
退出 PostgreSQL shell。
postgres=# \q
第 5 步 - 配置 Graphite Carbon 和 Web
下一步是配置 Graphite Carbon 和 Graphite Web。
配置 Carbon
Carbon 由三个服务组成:
- carbon-cache:接收指标并将其写入磁盘。
- carbon-relay:复制数据。
- carbon-aggregator:运行在 carbon-cache 服务之前,在将指标转发到 Whisper 之前对其进行缓冲。
配置 carbon-cache 是必需的,但 carbon-relay 和 carbon-aggregator 是可选的。
使用示例文件创建 carbon.conf 文件。
$ sudo cp /opt/graphite/conf/carbon.conf.example /opt/graphite/conf/carbon.conf
接下来,创建存储模式(storage schemas)配置。
$ sudo cp /opt/graphite/conf/storage-schemas.conf.example /opt/graphite/conf/storage-schemas.conf
打开存储模式配置文件。
$ sudo nano /opt/graphite/conf/storage-schemas.conf
在其中,你会看到类似如下的条目
[carbon]
pattern = ^carbon\.
retentions = 60:90d
这表示匹配正则表达式 ^carbon\. 的模式应使用 60:90d 的保留策略来保存数据,即
- 指标记录的频次:每 60 秒
- 这些数值的存储时长:90 天
你可以添加自己的条目。以 test 为例,即监控数据点,我们的数据点条目将以字符串 test 开头。此条目应添加在文件底部提到的默认条目之前。
[test]
pattern = ^test\.
retentions = 10s:10m,1m:1h
这将匹配任何以 test 开头的指标。它会以不同的详细程度将数据存储两次。第一个定义(1s:10m)每十秒创建一个数据点,仅将数据存储十分钟。第二个定义每一分钟创建一个数据点,它会收集过去一分钟内的所有数据(六个点,因为前一个定义每十秒创建一个点)并将其聚合以创建该点。此详细级别的数据将存储一小时。
按 Ctrl + X 保存文件,并在提示时输入 Y。
启动 carbon-cache 服务。
$ sudo /opt/graphite/bin/carbon-cache.py start
配置 Graphite Web
下一步是配置 Graphite Web 应用。
为 Graphite 应用生成一个密钥(secret key)。复制显示出来的密钥以备后用。
$ python3 -c 'from django.core.management.utils import get_random_secret_key; print(get_random_secret_key())'
sp%71)6b$%^bc(7xpz1d!)x3(azog01&k^8l02*!y0#)72p07y
创建 Web 应用设置文件。
$ sudo cp /opt/graphite/webapp/graphite/local_settings.py.example /opt/graphite/webapp/graphite/local_settings.py
你需要使用数据库设置为 Graphite Web 应用进行配置。打开 local_settings.py 进行编辑。
$ sudo nano /opt/graphite/webapp/graphite/local_settings.py
取消注释 SECRET_KEY 变量,并为其填入一个随机值。
SECRET_KEY = 'your-secret-key'
取消注释 ALLOWED_HOSTS 变量。
ALLOWED_HOSTS = [ '*' ]
取消注释 TIME_ZONE 变量,并将其设置为合适的值。
TIME_ZONE = 'Asia/Kolkata'
取消注释 USE_REMOTE_USER_AUTHENTICATION 变量,并将其设置为 TRUE,以便远程用户在进行任何数据库更改之前先通过身份验证。
USE_REMOTE_USER_AUTHENTICATION = True
修改数据库设置。
DATABASES = {
    'default': {
        'NAME': 'graphitedb',
        'ENGINE': 'django.db.backends.postgresql_psycopg2',
        'USER': 'graphite',
        'PASSWORD': 'your_password',
        'HOST': '127.0.0.1',
        'PORT': ''
    }
}
按 Ctrl + X 保存文件,并在提示时输入 Y。
安装 Python 的 PostgreSQL 封装器(wrapper)所需的若干依赖。
$ sudo pip install psycopg2-binary
运行以下命令以导入数据库模式(schema)。
$ sudo PYTHONPATH=/opt/graphite/webapp/ django-admin.py migrate --settings=graphite.settings
你将看到如下输出。
Operations to perform:
  Apply all migrations: account, admin, auth, contenttypes, dashboard, events, sessions, tagging, tags, url_shortener
Running migrations:
  Applying contenttypes.0001_initial... OK
  Applying auth.0001_initial... OK
  Applying account.0001_initial... OK
  Applying admin.0001_initial... OK
  Applying admin.0002_logentry_remove_auto_add... OK
  Applying admin.0003_logentry_add_action_flag_choices... OK
  Applying contenttypes.0002_remove_content_type_name... OK
  Applying auth.0002_alter_permission_name_max_length... OK
  Applying auth.0003_alter_user_email_max_length... OK
  Applying auth.0004_alter_user_username_opts... OK
  Applying auth.0005_alter_user_last_login_null... OK
  Applying auth.0006_require_contenttypes_0002... OK
  Applying auth.0007_alter_validators_add_error_messages... OK
  Applying auth.0008_alter_user_username_max_length... OK
  Applying auth.0009_alter_user_last_name_max_length... OK
  Applying auth.0010_alter_group_name_max_length... OK
  Applying auth.0011_update_proxy_permissions... OK
  Applying auth.0012_alter_user_first_name_max_length... OK
  Applying dashboard.0001_initial... OK
  Applying events.0001_initial... OK
  Applying sessions.0001_initial... OK
  Applying tagging.0001_initial... OK
  Applying tagging.0002_on_delete... OK
  Applying tags.0001_initial... OK
  Applying url_shortener.0001_initial... OK
接下来,收集静态文件。
$ sudo PYTHONPATH=/opt/graphite/webapp/ django-admin.py collectstatic --settings=graphite.settings
设置正确的所有权(ownership)设置。
$ sudo chown -R www-data:www-data /opt/graphite/storage/
$ sudo chown -R www-data:www-data /opt/graphite/static/
$ sudo chown -R www-data:www-data /opt/graphite/webapp/
创建一个用于登录的 root 用户。
$ sudo PYTHONPATH=/opt/graphite/webapp/ django-admin.py createsuperuser --settings=graphite.settings
Username (leave blank to use 'root'): navjot
Email address:
[email protected]

Password:
Password (again):
Superuser created successfully.
它会要求你创建一个超级用户(superuser)。该用户稍后将用于连接 Graphite 应用。
第 6 步 - 配置 Apache
Graphite 默认附带 Apache 配置文件。安装 Apache 服务器。
$ sudo apt install apache2 libapache2-mod-wsgi-py3
创建 mod_wsgi 文件。
$ sudo cp /opt/graphite/conf/graphite.wsgi.example /opt/graphite/conf/graphite.wsgi
将 Graphite 的示例配置文件复制到 Apache 的位置。
$ sudo cp /opt/graphite/examples/example-graphite-vhost.conf /etc/apache2/sites-available/graphite.conf
打开 Graphite 配置文件进行编辑。
$ sudo nano /etc/apache2/sites-available/graphite.conf
将第一行的端口号从 80 改为 127.0.0.1:8080。在前面加上 127.0.0.1 可限制其无法通过 Web 访问。
<VirtualHost 127.0.0.1:8080>
添加你的域名。
ServerName graphite.example.com #Replace with your domain
在 Alias /static/ /opt/graphite/static/ 这一行下方添加以下行。
#Add below lines
<Directory /opt/graphite/static/>
     Require all granted
</Directory>
按 Ctrl + X 保存文件,并在提示时输入 Y。
禁用默认的虚拟主机,并启用 Graphite 虚拟主机文件。
$ sudo a2dissite 000-default
$ sudo a2ensite graphite
我们还需要让 Apache 监听 8080 端口并停止监听 80 端口,因为我们将使用 Nginx 作为代理服务器。
打开 /etc/apache2/ports.conf 文件进行编辑。
$ sudo nano /etc/apache2/ports.conf
找到 Listen 80 这一行,并将其替换为以下内容。
Listen 127.0.0.1:8080
按 Ctrl + X 保存文件,并在提示时输入 Y。
重启 Apache 服务器。
$ sudo systemctl restart apache2
要验证 Graphite 是否正常工作且可访问,请运行以下命令。
$ curl 127.0.0.1:8080
你将看到如下输出。
<!DOCTYPE HTML PUBLIC "-//W3C//DTD HTML 4.01 Frameset//EN" "http://www.w3.org/TR/html4/frameset.dtd">
<!-- Copyright 2008 Orbitz WorldWide

Licensed under the Apache License, Version 2.0 (the "License");
you may not use this file except in compliance with the License.
You may obtain a copy of the License at

   http://www.apache.org/licenses/LICENSE-2.0

Unless required by applicable law or agreed to in writing, software
distributed under the License is distributed on an "AS IS" BASIS,
WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
See the License for the specific language governing permissions and
limitations under the License. -->

<html>
  <head>
    <title>Graphite Browser</title>
  </head>


<frameset rows="80,*" frameborder="1" border="1">
  <frame src="/browser/header" name="Header" id='header' scrolling="no" noresize="true" />

    <frame src="/composer?" name="content" id="composerFrame"/>

</frameset>
</html>
这确认它运行正常。
第 7 步 - 安装 Nginx
我们将使用 Nginx 作为 Apache 的代理服务器。这样,我们既能享受安全性和隐蔽性带来的好处,又能继续使用 Graphite 提供的现有配置。
Ubuntu 22.04 自带较旧版本的 Nginx。要安装最新版本,你需要下载官方的 Nginx 仓库。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
| sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
添加 Nginx 稳定版的仓库。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg arch=amd64] \
http://nginx.org/packages/ubuntu `lsb_release -cs` nginx" \
| sudo tee /etc/apt/sources.list.d/nginx.list
更新系统软件仓库。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.22.0
启动 Nginx 服务器。
$ sudo systemctl start nginx
第 8 步 - 安装 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Ubuntu 的仓库安装 Certbot,也可以通过 Snapd 工具获取最新版本。我们将使用 Snapd 版本。
Ubuntu 22.04 默认已安装 Snapd。运行以下命令以确保你的 Snapd 版本是最新的。
$ sudo snap install core
$ sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可以运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
运行以下命令以生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d graphite.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/graphite.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
你会看到 snap.certbot.renew.service 是计划运行的服务之一。
NEXT                        LEFT          LAST                        PASSED   UNIT                           ACTIVATES

.................................................................................................................................
Wed 2022-09-28 00:00:00 UTC 7h left       Tue 2022-09-27 00:00:01 UTC 16h ago  logrotate.timer                logrotate.service
Wed 2022-09-28 02:39:09 UTC 10h left      Tue 2022-09-27 09:42:42 UTC 6h ago   apt-daily.timer                apt-daily.service
Wed 2022-09-28 06:02:00 UTC 13h left      n/a                         n/a      snap.certbot.renew.timer       snap.certbot.renew.service
要检查 SSL 续期是否正常工作,请对流程进行一次试运行(dry run)。
$ sudo certbot renew --dry-run
如果没有看到错误,你就已全部设置完成。你的证书将自动续期。
第 9 步 - 配置 Nginx
打开 /etc/nginx/nginx.conf 文件进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
创建并打开 /etc/nginx/conf.d/uvdesk.conf 文件进行编辑。
$ sudo nano /etc/nginx/conf.d/graphite.conf
在其中粘贴以下代码。
server {
    listen       443 ssl http2;
    listen       [::]:443 ssl http2;
    server_name  graphite.example.com;

    access_log  /var/log/nginx/graphite.access.log;
    error_log   /var/log/nginx/graphite.error.log;

	# SSL
    ssl_certificate      /etc/letsencrypt/live/graphite.example.com/fullchain.pem;
    ssl_certificate_key  /etc/letsencrypt/live/graphite.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/graphite.example.com/chain.pem;
    ssl_session_timeout  5m;
    ssl_session_cache shared:MozSSL:10m;
    ssl_session_tickets off;
    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;
    resolver 8.8.8.8;

    location / {
       proxy_set_header Connection "upgrade";
       proxy_set_header Upgrade $http_upgrade;
       proxy_http_version 1.1;

       proxy_set_header Host $http_host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-NginX-Proxy true;

       proxy_pass http://127.0.0.1:8080;
       proxy_redirect off;
    }
}

# enforce HTTPS
server {
    listen       80;
    listen       [::]:80;
    server_name  graphite.example.com;
    return 301   https://$host$request_uri;
}
完成后按 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
第 10 步 - 访问并使用 Graphite
在你的浏览器中访问 URL https://graphite.example.com,你将看到如下界面。
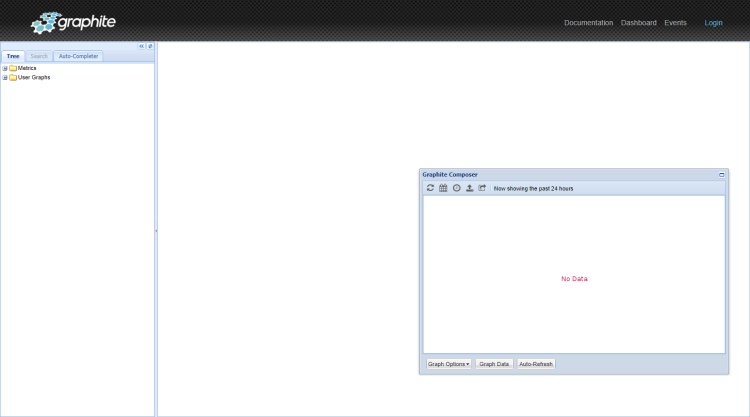
点击右上角的 Login 链接打开登录页面。输入你在第 5 步创建的超级用户凭据,然后按登录按钮继续。
有多种方法可以向 Graphite 提供数据。我们在存储模式(Storage schema)中添加了一个模式匹配器,据此任何以 test 开头的模式都会被记录为我们的模式。让我们使用以下命令添加一些随机数据。
$ echo "test.count 9 `date +%s`" | nc -q0 127.0.0.1 2003;
这会将一个值为 9 的数据指标添加到系统中。让我们通过循环遍历值来添加更多数据。
$ for i in 4 6 8 16 2; do echo "test.count $i `date +%s`" | nc -q0 127.0.0.1 2003; sleep 6; done
返回 Graphite 仪表板,从左侧边栏打开 Metrics >> test >> count。你应该会看到类似如下的内容。
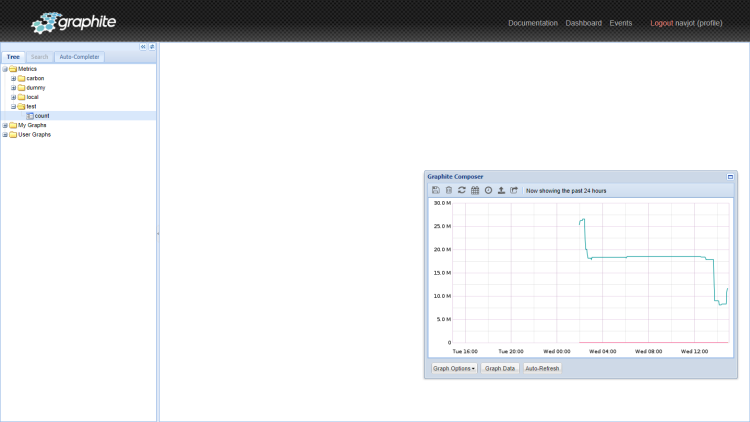
现在你可以开始将其用于监控。你也可以将其与 Grafana 结合使用,以获得高度的可定制性。
结论
至此,我们关于在 Ubuntu 22.04 服务器上安装并配置 Graphite、并将 Nginx 作为代理服务器的教程就结束了。如果你有任何问题,请在下方评论中留言。