
本页内容
- 前置条件
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装 Nginx
- 第 3 步 - 安装 PHP 及扩展
- 第 4 步 - 安装 MySQL
- 第 5 步 - 配置 MySQL
- 第 6 步 - 安装 Composer
- 第 7 步 - 下载并配置 UVDesk
- 第 8 步 - 安装并配置 SSL
- 第 9 步 - 配置 Nginx 和 PHP 配置 PHP-FPM 配置 Nginx
- 第 10 步 - 安装 UVDesk
- 总结
- 配置 PHP-FPM
- 配置 Nginx
UVdesk 是一款面向企业的开源 SaaS 客服系统,用于与客户互动并提供全天候支持。其功能包括工单管理、知识库支持、预设回复,以及基于邮件的自动工单生成。UVdesk 的能力可通过外部模块进行扩展。你可以基于特定触发器自动执行某些操作,从而优化工作流。
在本教程中,你将学习如何使用 Nginx、MySQL 和 PHP 在 Ubuntu 22.04 服务器上安装 UVdesk。
前置条件
- 一台运行 Ubuntu 22.04 的服务器。
- 一个指向该服务器的完全限定域名(FQDN)。在本教程中,我们将使用 uvdesk.example.com 域名。
- 一个具有 sudo 权限的非 root 用户。
- 确保系统已更新。 $ sudo apt update && sudo apt upgrade
- 安装基础工具软件包。其中部分可能已安装。 $ sudo apt install wget curl nano unzip -y
一台运行 Ubuntu 22.04 的服务器。
一个指向该服务器的完全限定域名(FQDN)。在本教程中,我们将使用 uvdesk.example.com 域名。
一个具有 sudo 权限的非 root 用户。
确保系统已更新。
$ sudo apt update && sudo apt upgrade
安装基础工具软件包。其中部分可能已安装。
$ sudo apt install wget curl nano unzip -y
第 1 步 - 配置防火墙
在安装任何软件包之前,第一步是配置防火墙以允许 HTTP 和 HTTPS 连接。
检查防火墙状态。
$ sudo ufw status
你应该会看到类似下面的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
允许 HTTP 和 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
再次检查状态以确认。
$ sudo ufw status
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
第 2 步 - 安装 Nginx
Ubuntu 22.04 自带较旧版本的 Nginx。要安装最新版本,你需要下载官方的 Nginx 软件源。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
| sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
添加 Nginx 稳定版的软件源。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg arch=amd64] \
http://nginx.org/packages/ubuntu `lsb_release -cs` nginx" \
| sudo tee /etc/apt/sources.list.d/nginx.list
更新系统软件源。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.22.0
启动 Nginx 服务器。
$ sudo systemctl start nginx
第 3 步 - 安装 PHP 及扩展
Ubuntu 22.04 默认自带 PHP 8.1。不过 UVdesk 在 PHP 8.0 下运行良好。要安装 PHP 8.0,我们需要使用 Ondrej 的 PHP 软件源。
添加 Ondrej 的 PHP 软件源。
$ sudo add-apt-repository ppa:ondrej/php
更新你的系统软件源列表。
$ sudo apt update
安装 PHP 以及 UVdesk 所需的扩展。
$ sudo apt install php8.0 php8.0-curl php8.0-intl php8.0-gd php8.0-xsl php8.0-mbstring php8.0-zip php8.0-xml php8.0-bz2 php8.0-mysql php8.0-soap php8.0-mysql php8.0-fpm php8.0-gmp php8.0-bcmath php8.0-apcu php8.0-redis php8.0-imagick php8.0-imap php8.0-xdebug php8.0-tidy php8.0-ldap php8.0-opcache php8.0-mailparse
检查已安装的 PHP 版本。
$ php --version
PHP 8.0.23 (cli) (built: Sep 18 2022 10:25:06) ( NTS )
Copyright (c) The PHP Group
Zend Engine v4.0.23, Copyright (c) Zend Technologies
    with Zend OPcache v8.0.23, Copyright (c), by Zend Technologies
    with Xdebug v3.1.5, Copyright (c) 2002-2022, by Derick Rethans
第 4 步 - 安装 MySQL
Ubuntu 22.04 自带最新版本的 MySQL。你可以用一个命令安装它。
$ sudo apt install mysql-server
检查 MySQL 的版本。
$ mysql --version
mysql  Ver 8.0.30-0ubuntu0.22.04.1 for Linux on x86_64 ((Ubuntu))
这一步对于 MySQL 8.0.28 及以上版本是必需的。进入 MySQL Shell。
$ sudo mysql
运行以下命令为你的 root 用户设置密码。请确保密码包含数字、大写字母、小写字母和特殊字符的组合。
mysql> ALTER USER 'root'@'localhost' IDENTIFIED WITH mysql_native_password BY 'YourPassword12!';
退出 Shell。
mysql> exit
运行 MySQL 安全安装脚本。
$ sudo mysql_secure_installation
首先,会要求你输入 root 密码,输入即可。接着会询问是否安装 Validate Password Component(密码验证组件),它会检查 MySQL 中使用的密码强度。按 Y 安装。之后会要求设置密码验证策略的级别,选择 2,因为它是最强的一级。
Securing the MySQL server deployment.

Enter password for user root:

VALIDATE PASSWORD COMPONENT can be used to test passwords
and improve security. It checks the strength of password
and allows the users to set only those passwords which are
secure enough. Would you like to setup VALIDATE PASSWORD component?

Press y|Y for Yes, any other key for No: Y

There are three levels of password validation policy:

LOW    Length >= 8
MEDIUM Length >= 8, numeric, mixed case, and special characters
STRONG Length >= 8, numeric, mixed case, special characters and dictionary                  file

Please enter 0 = LOW, 1 = MEDIUM and 2 = STRONG: 2
Using existing password for root.

Estimated strength of the password: 100
接下来,输入 N 拒绝更改 root 密码。同时,输入 Y 以删除匿名用户、禁止 root 远程登录、删除测试数据库并重载权限表。
Change the password for root ? ((Press y|Y for Yes, any other key for No) : N

 ... skipping.
By default, a MySQL installation has an anonymous user,
allowing anyone to log into MySQL without having to have
a user account created for them. This is intended only for
testing, and to make the installation go a bit smoother.
You should remove them before moving into a production
environment.

Remove anonymous users? (Press y|Y for Yes, any other key for No) : Y
Success.


Normally, root should only be allowed to connect from
'localhost'. This ensures that someone cannot guess at
the root password from the network.

Disallow root login remotely? (Press y|Y for Yes, any other key for No) : Y
Success.

By default, MySQL comes with a database named 'test' that
anyone can access. This is also intended only for testing,
and should be removed before moving into a production
environment.


Remove test database and access to it? (Press y|Y for Yes, any other key for No) : Y
 - Dropping test database...
Success.

 - Removing privileges on test database...
Success.

Reloading the privilege tables will ensure that all changes
made so far will take effect immediately.

Reload privilege tables now? (Press y|Y for Yes, any other key for No) : Y
Success.

All done!
第 5 步 - 配置 MySQL
登录 MySQL Shell。出现提示时输入你的 root 密码。
$ sudo mysql -u root -p
创建一个示例数据库。
mysql> CREATE DATABASE uvdeskdb;
创建一个 SQL 用户账户。
mysql> CREATE USER 'uvdesk'@'localhost' IDENTIFIED BY 'Your_password2';
将该数据库的所有权限授予该用户。
mysql> GRANT ALL PRIVILEGES ON uvdeskdb.* TO 'uvdesk'@'localhost';
刷新用户权限。
mysql> FLUSH PRIVILEGES;
退出 Shell。
mysql> exit
第 6 步 - 安装 Composer
UVdesk 使用 Composer 来管理依赖。运行以下命令下载并安装 Composer。
$ php -r "copy('https://getcomposer.org/installer', 'composer-setup.php');"
$ php -r "if (hash_file('sha384', 'composer-setup.php') === '55ce33d7678c5a611085589f1f3ddf8b3c52d662cd01d4ba75c0ee0459970c2200a51f492d557530c71c15d8dba01eae') { echo 'Installer verified'; } else { echo 'Installer corrupt'; unlink('composer-setup.php'); } echo PHP_EOL;"
$ php composer-setup.php
$ php -r "unlink('composer-setup.php');"
$ sudo mv composer.phar /usr/local/bin/composer
验证 Composer 是否已正确安装。
$ composer -V
Composer version 2.4.2 2022-09-14 16:11:15
第 7 步 - 下载并配置 UVDesk
创建 /var/www 目录。
$ sudo mkdir /var/www
切换到 www 目录。
$ cd /var/www
将 /var/www 文件夹的权限赋予当前登录的系统用户。
$ sudo chown $USER:$USER /var/www/
使用 Composer 安装 UVdesk 的依赖。
$ composer clear-cache
$ composer create-project uvdesk/community-skeleton uvdesk.example.com
安装访问控制列表(acl)工具。
$ sudo apt install acl
为当前登录用户 $USER 和 Nginx 用户 nginx 授予特定目录和文件的权限。
$ sudo setfacl -dR -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/var
$ sudo setfacl -R -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/var
$ sudo setfacl -dR -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/public
$ sudo setfacl -R -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/public
$ sudo setfacl -dR -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/config
$ sudo setfacl -R -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/config
$ sudo setfacl -dR -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/migrations
$ sudo setfacl -R -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/migrations
$ sudo setfacl -m u:nginx:rwX -m u:$USER:rwX /var/www/uvdesk.example.com/.env
第 8 步 - 安装并配置 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Ubuntu 的软件源安装 Certbot,也可以通过 Snapd 工具获取最新版本。我们将使用 Snapd 版本。
Ubuntu 22.04 默认已安装 Snapd。运行以下命令确保你安装的 Snapd 是最新的。
$ sudo snap install core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可以运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
运行以下命令生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d uvdesk.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/uvdesk.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
检查 Certbot 续期调度服务。
$ sudo systemctl list-timers
你会发现 snap.certbot.renew.service 是计划运行的服务之一。
NEXT                        LEFT          LAST                        PASSED      UNIT                      ACTIVATES
Mon 2022-09-19 00:28:48 UTC 13min left    Sun 2022-09-18 23:31:55 UTC 43min ago   fstrim.timer              fstrim.service
Mon 2022-09-19 00:39:00 UTC 23min left    Mon 2022-09-19 00:09:00 UTC 6min ago    phpsessionclean.timer     phpsessionclean.service
Mon 2022-09-19 00:40:00 UTC 24min left    n/a                         n/a         snap.certbot.renew.timer  snap.certbot.renew.service
.......
要检查 SSL 续期是否正常工作,可以对该过程进行一次演练(dry run)。
$ sudo certbot renew --dry-run
如果没有看到任何错误,你就已准备就绪。你的证书将自动续期。
第 9 步 - 配置 Nginx 和 PHP
配置 PHP-FPM
打开文件 /etc/php/8.0/fpm/pool.d/www.conf 。
$ sudo nano /etc/php/8.0/fpm/pool.d/www.conf
我们需要将 PHP 进程的 Unix 用户/组设置为 nginx 。在文件中找到 user=www-data 和 group=www-data 这两行,并将其改为 nginx 。
...
; Unix user/group of processes
; Note: The user is mandatory. If the group is not set, the default user's group
;       will be used.
; RPM: apache user chosen to provide access to the same directories as httpd
user = nginx
; RPM: Keep a group allowed to write in log dir.
group = nginx
...
在文件中找到 listen.owner = www-data 和 listen.group = www-data 这两行,并将其改为 nginx 。
; Set permissions for unix socket, if one is used. In Linux, read/write
; permissions must be set in order to allow connections from a web server. Many
; BSD-derived systems allow connections regardless of permissions. The owner
; and group can be specified either by name or by their numeric IDs.
; Default Values: user and group are set as the running user
;                 mode is set to 0660
listen.owner = nginx
listen.group = nginx
按 Ctrl + X 保存文件,出现提示时输入 Y。
将 PHP-FPM 和 PHP-CLI 的执行时间增加到 60 秒。
$ sudo sed -i 's/max_execution_time = 30/max_execution_time = 60/' /etc/php/8.0/fpm/php.ini
$ sudo sed -i 's/max_execution_time = 30/max_execution_time = 60/' /etc/php/8.0/cli/php.ini
将 PHP-FPM 的内存限制从 128MB 提高到 256MB。
$ sudo sed -i 's/memory_limit = 128M/memory_limit = 256M/' /etc/php/8.0/fpm/php.ini
重启 PHP-FPM 服务。
$ sudo systemctl restart php8.0-fpm
将 PHP 会话目录的属组改为 Nginx。
$ sudo chgrp -R nginx /var/lib/php/session
配置 Nginx
创建并打开文件 /etc/nginx/conf.d/uvdesk.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/uvdesk.conf
在其中粘贴以下代码。
server {
    listen       443 ssl http2;
    listen       [::]:443 ssl http2;
    server_name  uvdesk.example.com;

    access_log  /var/log/nginx/uvdesk.access.log;
    error_log   /var/log/nginx/uvdesk.error.log;

	# SSL
    ssl_certificate      /etc/letsencrypt/live/uvdesk.example.com/fullchain.pem;
    ssl_certificate_key  /etc/letsencrypt/live/uvdesk.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/uvdesk.example.com/chain.pem;
    ssl_session_timeout  5m;
    ssl_session_cache shared:MozSSL:10m;
    ssl_session_tickets off;
    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers on;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;
    resolver 8.8.8.8;

    root /var/www/uvdesk/public;
    index index.php;

    location / {
        try_files $uri $uri/ /index.php?$args;
    }

    # Pass PHP Scripts To FastCGI Server
    location ~ \.php$ {
        fastcgi_split_path_info ^(.+\.php)(.*)$;
        fastcgi_pass unix:/run/php/php8.0-fpm.sock; # Depends On The PHP Version
        fastcgi_index index.php;
        fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
        fastcgi_param PATH_INFO $fastcgi_path_info;
        include fastcgi_params;
        try_files $uri =404;
    }
}

# enforce HTTPS
server {
    listen       80;
    listen       [::]:80;
    server_name  uvdesk.example.com;
    return 301   https://$host$request_uri;
}
注意,Nginx 配置中使用的根目录是 /var/www/uvdesk/public/,而不是 /var/www/uvdesk/ 。
完成后按 Ctrl + X 保存文件,出现提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,出现提示时输入 Y。
验证 Nginx 配置文件的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
第 10 步 - 安装 UVDesk
在浏览器中打开网址 https://uvdesk.example.com,你将看到如下界面。
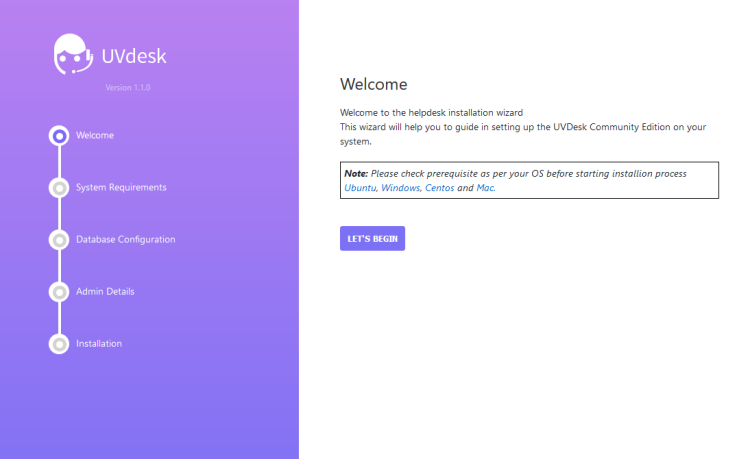
点击“Let's Begin”按钮开始安装过程。安装程序将在下一页检查 PHP 设置和文件权限。
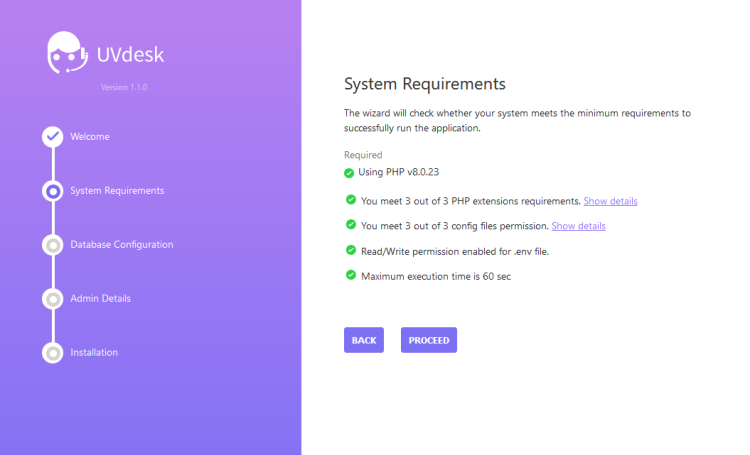
点击“Proceed”继续。下一页会要求你填写数据库详细信息。请按第 4 步中的配置填写。
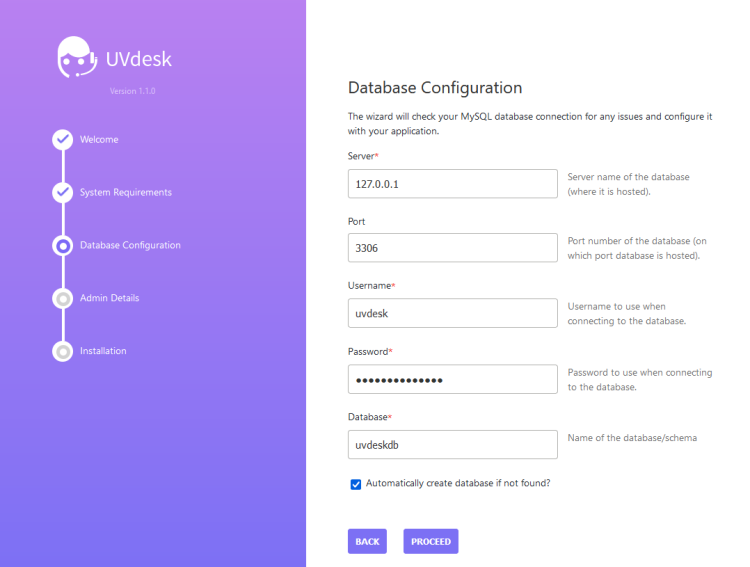
点击“Proceed”继续。接下来会要求你创建一个超级管理员账户,请填写你的信息。
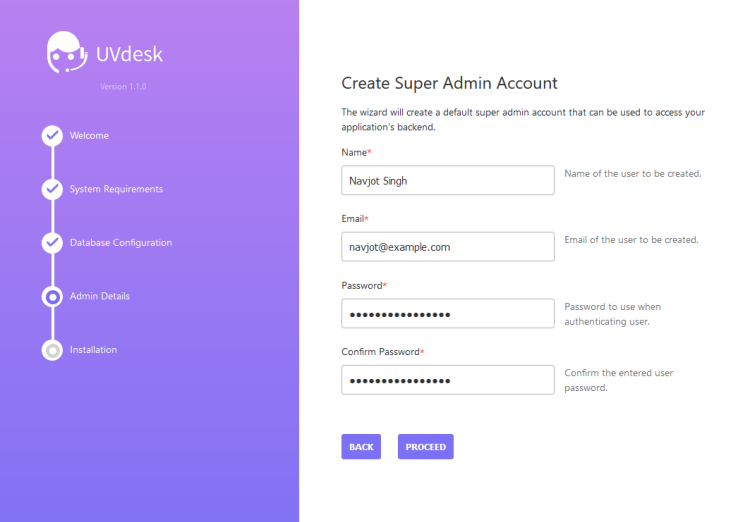
点击“Proceed”继续。接下来会要求你配置网站,为 Member 和 Customer 面板的 URL 前缀命名。这些前缀用于网站的 URL 中。
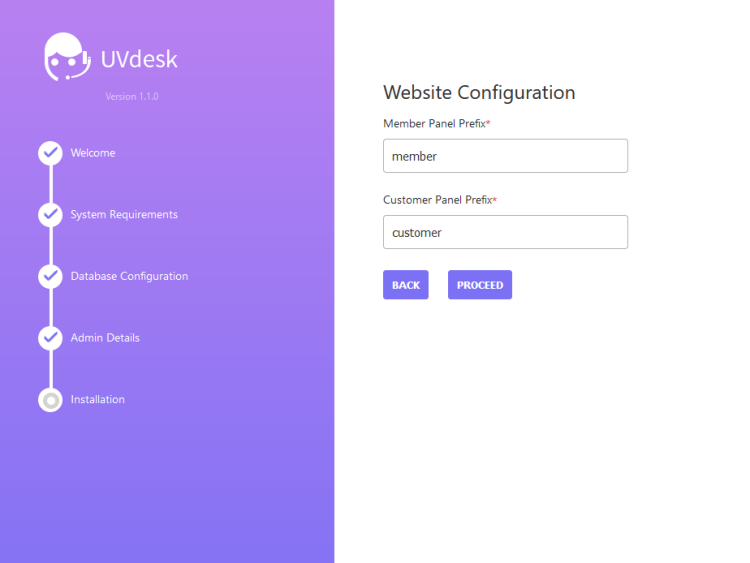
点击“Proceed”继续。你将到达最后的安装页面。
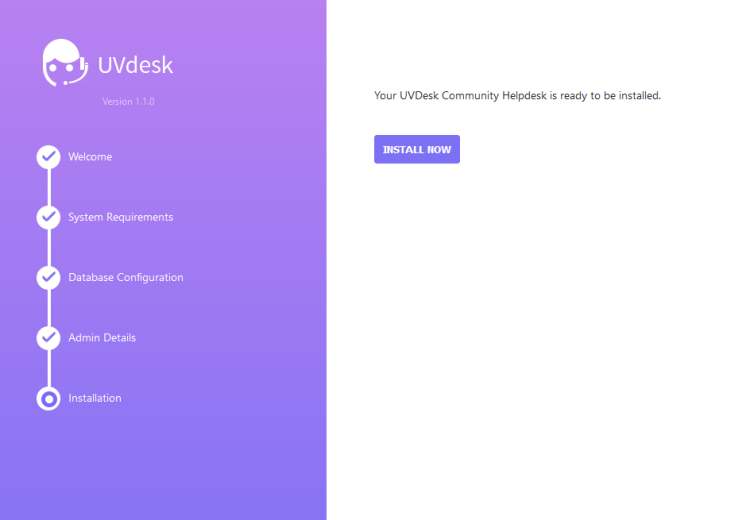
点击“Install Now”开始安装。安装完成后,你将看到如下界面。
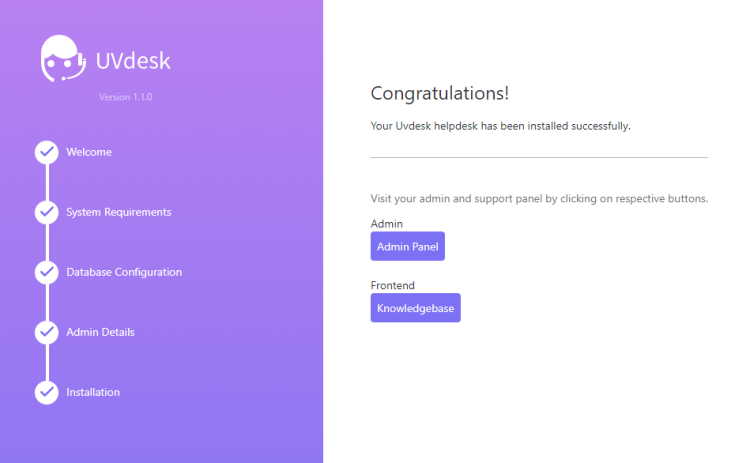
你可以通过给出的链接访问管理面板和前端网站。你的 UVDesk 安装已准备就绪,可以投入使用。
注意:如果安装因 SQL 错误“SQLSTATE[42S02]: Base table or view not found: 1146 Table 'uvdesk.uv_support_role' doesn't exist”而失败,请使用下面列出的命令来修复该问题。
$ cd /var/www/helpdesk.example.com/
$ php bin/console doctrine:migrations:diff
$ php bin/console doctrine:migrations:migrate
$ php bin/console c:c
$ sudo shutdown -r now
总结
你已使用 Nginx、MySQL 和 PHP 在 Ubuntu 22.04 服务器上安装了 UVdesk 客服系统。如果你有任何问题,请在下方评论中留言。