
本页内容
- 先决条件
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Nginx
- 步骤 3 - 安装 Node.js
- 步骤 4 - 安装 MySQL
- 步骤 5 - 安装 Ghost 安装 Ghost-CLI 准备 Ghost 目录 安装 Ghost
- 步骤 6 - 安装 SSL
- 步骤 7 - 配置 Nginx
- 步骤 8 - 配置 SELinux
- 步骤 9 - 运行站点
- 步骤 10 - 完成设置
- 步骤 11 - 配置邮件服务
- 步骤 12 - 更新 Ghost
- 总结
- 安装 Ghost-CLI
- 准备 Ghost 目录
- 安装 Ghost
Ghost 是一个开源博客平台,可帮助你创建外观专业的博客。它于 2013 年作为 WordPress 的替代方案推出,因为后者变得过于复杂。它是用 JavaScript 编写的,并由 Node.js 库提供支持。
本教程将介绍如何在运行 Rocky Linux 9 的服务器上使用 Nginx 和 MySQL 安装 Ghost CMS。我们将使用 Nginx 服务器托管博客,并使用 Let's Encrypt SSL 证书来保护我们的安装。
先决条件
- 一台运行 Rocky Linux 9 的服务器。
- 一个具有 sudo 权限的非 root 用户。
- 一个指向你服务器的完全限定域名(FQDN)。就本教程而言,我们将使用 ghost.example.com 作为域名。
- 确保系统已全面更新。 $ sudo dnf update
- 安装基础工具包。其中一些可能已安装。 $ sudo dnf install wget curl nano unzip yum-utils -y
一台运行 Rocky Linux 9 的服务器。
一个具有 sudo 权限的非 root 用户。
一个指向你服务器的完全限定域名(FQDN)。就本教程而言,我们将使用 ghost.example.com 作为域名。
确保系统已全面更新。
$ sudo dnf update
安装基础工具包。其中一些可能已安装。
$ sudo dnf install wget curl nano unzip yum-utils -y
步骤 1 - 配置防火墙
第一步是配置防火墙。Rocky Linux 使用 Firewalld 防火墙。检查防火墙的状态。
$ sudo firewall-cmd --state
running
防火墙使用不同的区域(zone),public 区域是我们将使用的默认区域。列出防火墙上所有处于活动状态的服务和端口。
$ sudo firewall-cmd --permanent --list-services
它应显示如下输出。
cockpit dhcpv6-client ssh
Wiki.js 需要 HTTP 和 HTTPS 端口才能运行。打开这些端口。
$ sudo firewall-cmd --add-service=http --permanent
$ sudo firewall-cmd --add-service=https --permanent
重新加载防火墙以使更改生效。
$ sudo firewall-cmd --reload
步骤 2 - 安装 Nginx
Rocky Linux 9 自带较旧版本的 Nginx。你需要下载官方 Nginx 仓库以安装最新版本。
创建并打开 /etc/yum.repos.d/nginx.repo 文件,以创建官方的 Nginx 仓库。
$ sudo nano /etc/yum.repos.d/nginx.repo
将以下代码粘贴到其中。
[nginx-stable]
name=nginx stable repo
baseurl=http://nginx.org/packages/centos/$releasever/$basearch/
gpgcheck=1
enabled=1
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true

[nginx-mainline]
name=nginx mainline repo
baseurl=http://nginx.org/packages/mainline/centos/$releasever/$basearch/
gpgcheck=1
enabled=0
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true
按 Ctrl + X 保存文件,并在提示时输入 Y。
安装 Nginx 服务器。
$ sudo dnf install nginx -y
验证安装。
$ nginx -v
nginx version: nginx/1.22.1
启用并启动 Nginx 服务器。
$ sudo systemctl enable nginx --now
检查服务器状态。
$ sudo systemctl status nginx
? nginx.service - nginx - high performance web server
     Loaded: loaded (/usr/lib/systemd/system/nginx.service; enabled; vendor preset: disabled)
     Active: active (running) since Tue 2022-10-25 08:27:47 UTC; 2s ago
       Docs: http://nginx.org/en/docs/
    Process: 1650 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 1651 (nginx)
      Tasks: 2 (limit: 5912)
     Memory: 1.9M
        CPU: 7ms
     CGroup: /system.slice/nginx.service
             ??1651 "nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf"
             ??1652 "nginx: worker process"

Oct 25 08:27:47 ghost.example.com systemd[1]: Starting nginx - high performance web server...
步骤 3 - 安装 Node.js
Ghost 安装程序需要 Nodejs 才能工作。运行以下命令安装 Node 16。
$ curl -fsSL https://rpm.nodesource.com/setup_16.x | sudo bash -
安装 Node。
$ sudo dnf install -y nodejs
验证 Node 安装。
$ node --version
v16.18.0
在撰写本教程时,Node 18 已经发布,并且是 LTS 版本。Ghost 尚未添加对其的支持。请持续关注 Ghost 关于 Node 版本的文档,以获取受支持的最新 Node 版本。当 Ghost 添加对 Node 18 的支持后,请改用以下命令安装 Node 18。
$ curl -fsSL https://rpm.nodesource.com/setup_18.x | sudo bash -
$ sudo dnf install -y nodejs
步骤 4 - 安装 MySQL
Rocky Linux 9 自带最新版本的 MySQL。你可以用一条命令安装它。
$ sudo dnf install mysql-server
检查 MySQL 的版本。
$ mysql --version
mysql  Ver 8.0.30 for Linux on x86_64 (Source distribution)
启用并启动 MySQL 服务。
$ sudo systemctl enable mysqld --now
检查服务状态。
$ sudo systemctl status mysqld
? mysqld.service - MySQL 8.0 database server
     Loaded: loaded (/usr/lib/systemd/system/mysqld.service; enabled; vendor preset: disabled)
     Active: active (running) since Tue 2022-10-25 09:00:26 UTC; 3s ago
    Process: 2920 ExecStartPre=/usr/libexec/mysql-check-socket (code=exited, status=0/SUCCESS)
    Process: 2942 ExecStartPre=/usr/libexec/mysql-prepare-db-dir mysqld.service (code=exited, status=0/SUCCESS)
   Main PID: 3021 (mysqld)
     Status: "Server is operational"
      Tasks: 39 (limit: 5912)
     Memory: 404.4M
        CPU: 4.686s
     CGroup: /system.slice/mysqld.service
             ??3021 /usr/libexec/mysqld --basedir=/usr

Oct 25 09:00:18 ghost.example.com systemd[1]: Starting MySQL 8.0 database server...
Oct 25 09:00:18 ghost.example.com mysql-prepare-db-dir[2942]: Initializing MySQL database
Oct 25 09:00:26 ghost.example.com systemd[1]: Started MySQL 8.0 database server.
默认情况下,你可以使用 Unix 认证登录 MySQL shell。但这样无法运行安全配置向导。因此,对于 MySQL 8.0.28 及以上版本,以下步骤是必要的。进入 MySQL Shell。
$ sudo mysql
运行以下命令为你的 root 用户设置密码。确保密码包含数字、大写字母、小写字母和特殊字符的组合。
mysql> ALTER USER 'root'@'localhost' IDENTIFIED WITH mysql_native_password BY 'YourPassword12!';
退出 shell。这一步的注意事项是,你将无法再使用 Unix 认证登录 MySQL shell。
mysql> exit
运行 MySQL 安全安装脚本。
$ sudo mysql_secure_installation
系统会询问是否安装 Validate Password Component。它会检查 MySQL 中所使用密码的强度。按 Y 安装它。
Securing the MySQL server deployment.

Connecting to MySQL using a blank password.

VALIDATE PASSWORD COMPONENT can be used to test passwords
and improve security. It checks the strength of password
and allows the users to set only those passwords which are
secure enough. Would you like to setup VALIDATE PASSWORD component?

Press y|Y for Yes, any other key for No: Y
接下来,系统会要求你设置密码验证策略的级别。选择 2,因为它是最强的一个。然后系统会要求你创建一个 root 密码。输入符合给定要求的密码。当被问到是否要继续使用该密码时,按 Y 继续。
There are three levels of password validation policy:

LOW    Length >= 8
MEDIUM Length >= 8, numeric, mixed case, and special characters
STRONG Length >= 8, numeric, mixed case, special characters and dictionary                  file

Please enter 0 = LOW, 1 = MEDIUM and 2 = STRONG: 2
Please set the password for root here.

New password:

Re-enter new password:

Estimated strength of the password: 100
Do you wish to continue with the password provided?(Press y|Y for Yes, any other key for No) : Y
最后,按 Y 删除匿名用户、禁止 root 远程登录、删除测试数据库并重新加载权限表。
By default, a MySQL installation has an anonymous user,
allowing anyone to log into MySQL without having to have
a user account created for them. This is intended only for
testing, and to make the installation go a bit smoother.
You should remove them before moving into a production
environment.

Remove anonymous users? (Press y|Y for Yes, any other key for No) : Y
Success.


Normally, root should only be allowed to connect from
'localhost'. This ensures that someone cannot guess at
the root password from the network.

Disallow root login remotely? (Press y|Y for Yes, any other key for No) : Y
Success.

By default, MySQL comes with a database named 'test' that
anyone can access. This is also intended only for testing,
and should be removed before moving into a production
environment.


Remove test database and access to it? (Press y|Y for Yes, any other key for No) : Y
 - Dropping test database...
Success.

 - Removing privileges on test database...
Success.

Reloading the privilege tables will ensure that all changes
made so far will take effect immediately.

Reload privilege tables now? (Press y|Y for Yes, any other key for No) : Y
Success.

All done!
至此,安装并保护 MySQL 的过程完成。
步骤 5 - 安装 Ghost
Ghost 安装包含三个组件——用于安装和管理 Ghost 博客更新的 Ghost-CLI 命令行工具,以及博客软件包本身。
安装 Ghost-CLI
运行以下命令安装 Ghost-CLI 工具。忽略安装过程中收到的任何警告。
$ sudo npm install ghost-cli@latest -g
准备 Ghost 目录
创建 Ghost 根目录。
$ sudo mkdir -p /var/www/html/ghost
将目录的所有权设置为当前用户。
$ sudo chown $USER:$USER /var/www/html/ghost
设置正确的目录权限。
$ sudo chmod 755 /var/www/html/ghost
切换到 Ghost 目录。
$ cd /var/www/html/ghost
安装 Ghost
安装 Ghost 只需一条命令。
$ ghost install
在安装过程中,CLI 工具会提出若干问题来配置博客。
- 在撰写本教程时,Ghost-CLI 除 Ubuntu 外不支持任何其他操作系统。它会询问你是否仍要继续安装。按 Y 继续。
- 博客 URL:输入你完整的博客 URL,并包含 https 协议。( https://ghost.example.com )
- MySQL 主机名:按 Enter 使用默认值 localhost,因为我们的 Ghost 安装与 MySQL 在同一台服务器上。
- MySQL 用户名:输入 root 作为你的 MySQL 用户名。
- MySQL 密码:输入你之前创建的 root 密码。
- Ghost 数据库名称:为你的 Ghost 数据库命名。( ghostdb )
- Sudo 密码:输入你系统的 sudo 密码以执行提权命令。
- 设置 Ghost 的 MySQL 用户?:安装程序会询问是否要为 Ghost 创建一个独立的 MySQL 用户。按 Y 继续。
- 设置 Nginx?:通常,Ghost-CLI 会检测你的 Nginx 安装并自动为你的博客配置。但截至目前,它无法检测到我们的 Nginx 安装。因此,安装程序会自动跳过此步骤。我们将手动配置 Nginx。
- 设置 SSL?:由于跳过了 Nginx 配置,CLI 工具也会跳过 SSL 的设置。
- 设置 systemd?:Ghost 会询问是否要为 Ghost 设置系统服务。按 Y 继续。
- 启动 Ghost?:按 Y 启动你的 Ghost 安装。服务会启动,但我们需要配置 Nginx 和 SSL 才能使其正常工作。
步骤 6 - 安装 SSL
在继续之前,我们需要安装 Certbot 工具以及我们域名的 SSL 证书。
为了安装 Certbot,我们将使用 Snapd 包安装器。Snapd 始终提供最新稳定版的 Certbot,你应该使用它。
Snapd 工具需要 Epel 仓库才能工作。
$ sudo dnf install epel-release -y
我们将使用 Snapd 安装 Certbot。安装 Snapd。
$ sudo dnf install snapd -y
启用并启动 Snap 服务。
$ sudo systemctl enable snapd.socket --now
创建 Snapd 工作所需的链接。
$ sudo ln -s /var/lib/snapd/snap /snap
$ echo 'export PATH=$PATH:/var/lib/snapd/snap/bin' | sudo tee -a /etc/profile.d/snapd.sh
确保你的 snapd 版本是最新的。
$ sudo snap install core
$ sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令,通过创建指向 /usr/bin 目录的符号链接,确保 Certbot 命令可以运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d ghost.example.com
上述命令会将证书下载到你服务器上的 /etc/letsencrypt/live/ghost.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
对流程进行一次试运行(dry run),以检查 SSL 续期是否正常工作。
$ sudo certbot renew --dry-run
如果没有看到错误,说明一切就绪。你的证书将自动续期。
步骤 7 - 配置 Nginx
创建并打开文件 /etc/nginx/conf.d/ghost.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/ghost.conf
将以下代码粘贴到 ghost.conf 文件中。将所有的 ghost.example.com 替换为你自己的域名。
## enforce HTTPS
server {
  listen 80;
  listen [::]:80;
  server_name ghost.example.com;
  return 301 https://$server_name$request_uri;
}

server {
  listen 443 ssl http2;
  listen [::]:443 ssl http2;
  server_name ghost.example.com;

  access_log /var/log/nginx/ghost.access.log;
  error_log /var/log/nginx/ghost.error.log;
  client_max_body_size 20m;

  http2_push_preload on; # Enable HTTP/2 Server Push

  ssl_certificate     /etc/letsencrypt/live/ghost.example.com/fullchain.pem;
  ssl_certificate_key /etc/letsencrypt/live/ghost.example.com/privkey.pem;
  ssl_trusted_certificate /etc/letsencrypt/live/ghost.example.com/chain.pem;
  ssl_session_timeout 1d;

  # Enable TLS versions (TLSv1.3 is required upcoming HTTP/3 QUIC).
  ssl_protocols TLSv1.2 TLSv1.3;

  # Enable TLSv1.3's 0-RTT. Use $ssl_early_data when reverse proxying to
  # prevent replay attacks.
  #
  # @see: https://nginx.org/en/docs/http/ngx_http_ssl_module.html#ssl_early_data
  ssl_early_data on;

  ssl_ciphers 'ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA384';
  ssl_prefer_server_ciphers on;
  ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;
  ssl_session_cache shared:SSL:50m;
  ssl_session_tickets off;

  # OCSP Stapling ---
  # fetch OCSP records from URL in ssl_certificate and cache them
  ssl_stapling on;
  ssl_stapling_verify on;
  ssl_dhparam /etc/ssl/certs/dhparam.pem;

  add_header X-Early-Data $tls1_3_early_data;

  location / {
    proxy_set_header Host $http_host;
    proxy_set_header X-Real-IP $remote_addr;
    proxy_set_header X-Forwarded-Proto https;
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_pass http://localhost:2368;
  }
}

# This block is useful for debugging TLS v1.3. Please feel free to remove this
# and use the `$ssl_early_data` variable exposed by NGINX directly should you
# wish to do so.
map $ssl_early_data $tls1_3_early_data {
  "~." $ssl_early_data;
  default "";
}
上述配置会将所有 HTTP 请求重定向到 HTTPS,并作为 Ghost 服务的代理,通过你的域名提供访问。
按 Ctrl + X 保存文件,并在提示时输入 Y。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
验证你的 Nginx 配置。
$ sudo nginx -t
如果没有看到错误,说明一切正常。重新加载 Nginx 服务器。
$ sudo systemctl reload nginx
步骤 8 - 配置 SELinux
允许 Nginx 连接网络。
$ sudo setsebool -P httpd_can_network_connect 1
步骤 9 - 运行站点
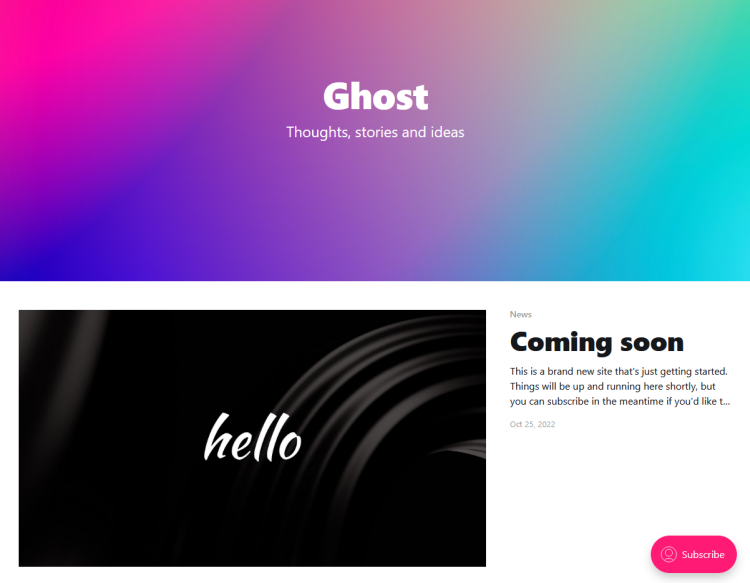
现在,你可以在网页浏览器中打开 https://ghost.example.com 来验证你的安装。你将看到如下页面,表明安装成功。
步骤 10 - 完成设置
要完成 Ghost 博客的设置,请在浏览器中访问 https://ghost.example.com/ghost。博客域名末尾额外的 /ghost 会将你重定向到 Ghost 的管理面板,由于你是首次访问,此处会进入设置页面。
你需要创建管理员账户并选择一个博客标题。
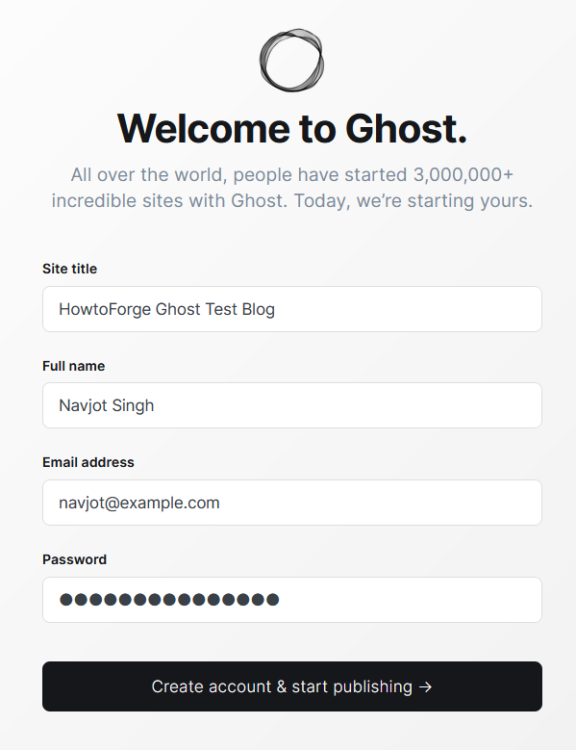
输入你的详细信息,然后点击“Create account & start publishing”(创建账户并开始发布)按钮继续。
接下来,你会进入如下界面,在这里你可以选择撰写第一篇文章、自定义站点以及导入成员等操作。
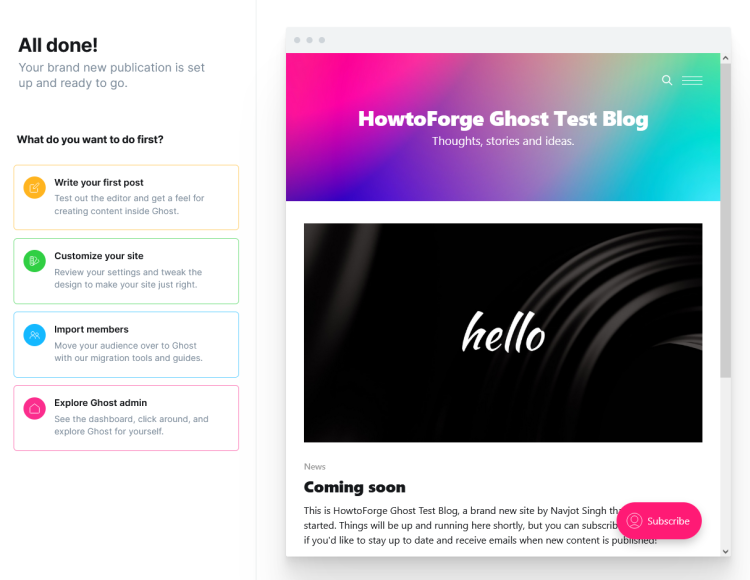
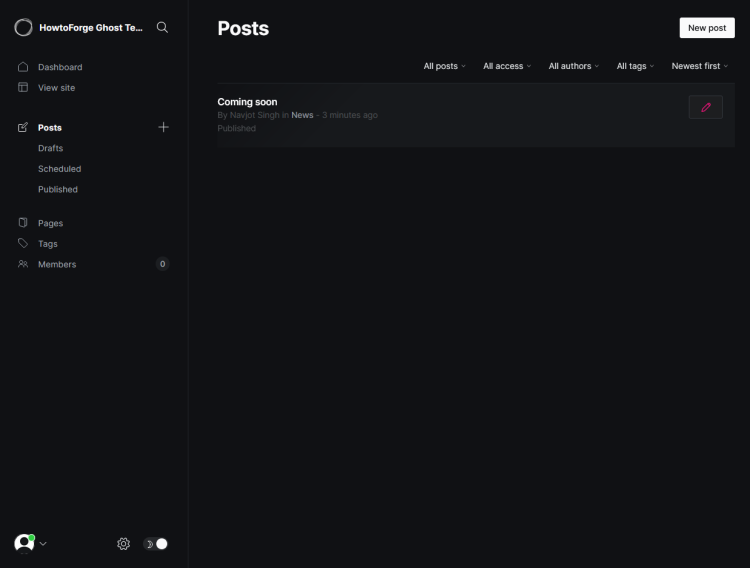
我们将选择 Explore Ghost admin 直接探索并进入仪表盘。设置结束时,你将看到 Ghost 的管理面板。
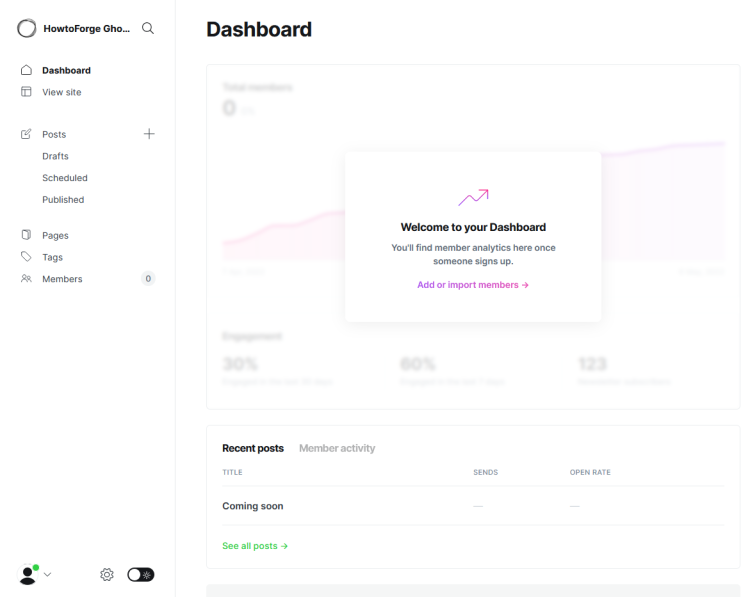
如果你想切换到深色模式,可以点击设置页面底部设置齿轮按钮旁边的开关切换。
切换到 Posts(文章)页面,你会看到一篇默认文章。你可以取消发布或删除它,然后开始发帖。
)
步骤 11 - 配置邮件服务
Ghost 不仅是一个博客平台,也是一个新闻通讯管理器。对于日常运营,你可以使用任何事务性邮件服务与 Ghost 配合发送邮件。但如果你想通过 Ghost 发送新闻通讯,官方唯一支持的大批量邮件服务是 Mailgun。你也可以使用其他新闻通讯服务,但为此你需要使用 Ghost 的 Zapier 集成功能。
让我们先配置一个用于事务性邮件的 SMTP 服务。为此,请打开文件 /var/www/html/ghost/config.production.json 进行编辑。
$ nano /var/www/html/ghost/config.production.json
找到以下行。
 "mail": {
    "transport": "Direct"
  },
用以下代码替换它们。
"mail": {
    "from": "'Acme Support'
[email protected]
",
    "transport": "SMTP",
    "options": {
        "host": "YOUR-SES-SERVER-NAME",
        "port": 465,
        "service": "SES",
        "auth": {
            "user": "YOUR-SES-SMTP-ACCESS-KEY-ID",
            "pass": "YOUR-SES-SMTP-SECRET-ACCESS-KEY"
        }
    }
},
这里我们使用 Amazon SES 邮件服务,因为它非常便宜,并且如果你使用他们的 EC2 服务,则可终身免费。
如果你想使用 Mailgun 的新闻通讯服务,请改用以下代码。
"mail": {
  "from": "'Acme Support'
[email protected]
",
  "transport": "SMTP",
  "options": {
    "service": "Mailgun",
    "host": "smtp.mailgun.org",
    "port": 587,
    "secure": true,
    "auth": {
      "user": "
[email protected]
",
      "pass": "1234567890"
    }
  }
},
按 Ctrl + X 保存文件,并在提示时输入 Y。
完成后,重启 Ghost 应用程序以使更改生效。
$ ghost restart
要配置新闻通讯设置,请访问 Settings >> Email newsletter(设置 >> 邮件新闻通讯)部分。
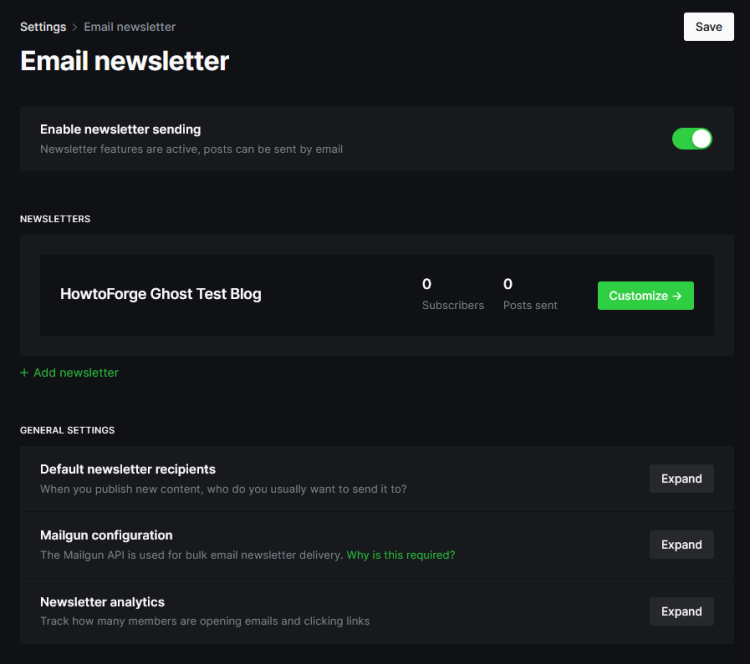
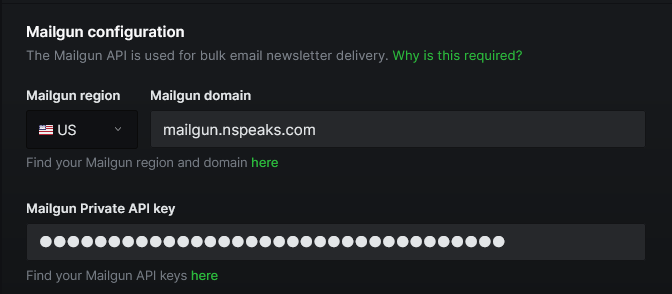
点击 Mailgun 配置链接将其展开。
填写你的 Mailgun Region(区域)、domain(域名)和 API key(API 密钥)。
点击右上角的 Save(保存)按钮以保存设置。
要测试新闻通讯发送,请打开任意文章,打开其设置并点击 Email newsletter(邮件新闻通讯)选项。接下来,发送一封测试邮件以检查是否正常工作。如果没有出现任何错误,说明你的新闻通讯发送功能正常。
步骤 12 - 更新 Ghost
Ghost 更新有两种类型——小版本更新(Minor updates)和大版本更新(Major updates)。
首先,如果要运行小版本更新,请先做一次完整备份。
$ cd /var/www/html/ghost
$ ghost backup
运行更新命令以执行小版本更新。
$ ghost update
要执行大版本更新,你应该遵循 Ghost 官方提供的详细更新指南。根据你当前所处的版本以及想要更新到的大版本,具体步骤会有所不同。
总结
至此,我们关于如何在你的 Rocky Linux 9 服务器上使用 Nginx 搭建 Ghost CMS 的教程就结束了。如果你有任何问题或反馈,请在下方评论中分享。