
本页内容
- 准备工作
- 步骤 1 - 配置防火墙
- 步骤 2 - 安装 Docker 和 Docker Compose
- 步骤 3 - 创建 Docker Compose 配置
- 步骤 4 - 启动 Jellyfin
- 步骤 5 - 安装 Nginx
- 步骤 6 - 安装 SSL
- 步骤 7 - 配置 Nginx
- 步骤 8 - 访问并配置 Jellyfin
- 步骤 9 - 升级 Jellyfin
- 结语
Jellyfin 是一款免费的开源媒体服务器,可让你串流播放能够随时随地访问的内容。它支持电影、电视节目、音乐以及直播电视/DVR。Jellyfin 服务器可部署在 Windows、Linux 或 macOS 上,并通过公网 URL 使用浏览器和移动应用从不同设备即时访问其内容。只要这些媒体设备连接到互联网或同一网络,它甚至还能在其他电脑、电视或手机上串流这些文件。它提供了诸多功能,包括:支持 DLNA、无播放限制、自动从 TheTVDB、TheMovieDB 和 Rotten Tomatoes 获取元数据、自动录制、支持硬件加速等等。
在 Emby 转向专有授权模式后,Jellyfin 是 Emby 媒体服务器的一个分支(fork)。
在本教程中,你将学习如何在 Rocky Linux 9 服务器上使用 Docker 安装 Jellyfin 媒体服务器。
准备工作
- 一台运行 Rocky Linux 9 的服务器,至少配备 2 个 CPU 核心和 4GB 内存。根据需要升级服务器配置。
- 一个具有 sudo 权限的非 root 用户。
- 一个指向你服务器的完全限定域名(FQDN)。本教程中我们将使用 jellyfin.example.com 作为域名。
- 确保系统已更新。 $ sudo dnf update
- 安装基础工具包。其中部分可能已安装。 $ sudo dnf install wget curl nano unzip yum-utils -y
一台运行 Rocky Linux 9 的服务器,至少配备 2 个 CPU 核心和 4GB 内存。根据需要升级服务器配置。
一个具有 sudo 权限的非 root 用户。
一个指向你服务器的完全限定域名(FQDN)。本教程中我们将使用 jellyfin.example.com 作为域名。
确保系统已更新。
$ sudo dnf update
安装基础工具包。其中部分可能已安装。
$ sudo dnf install wget curl nano unzip yum-utils -y
步骤 1 - 配置防火墙
第一步是配置防火墙。Rocky Linux 使用 Firewalld 防火墙。检查防火墙状态。
$ sudo firewall-cmd --state
running
防火墙使用不同的区域(zone),我们将使用默认的公共区域(public zone)。列出防火墙上处于活动状态的所有服务和端口。
$ sudo firewall-cmd --permanent --list-services
它应显示以下输出。
cockpit dhcpv6-client ssh
Jellyfin 需要 HTTP 和 HTTPS 端口才能正常工作。开放这些端口。
$ sudo firewall-cmd --permanent --add-service=http
$ sudo firewall-cmd --permanent --add-service=https
添加伪装(masquerade),因为该应用会与其他实例通信。
$ sudo firewall-cmd --permanent --add-masquerade
重新加载防火墙以使更改生效。
$ sudo firewall-cmd --reload
步骤 2 - 安装 Docker 和 Docker Compose
Rocky Linux 自带较旧版本的 Docker。要安装最新版本,首先安装官方的 Docker 仓库。
$ sudo yum-config-manager \
    --add-repo \
    https://download.docker.com/linux/centos/docker-ce.repo
安装最新版本的 Docker。
$ sudo dnf install docker-ce docker-ce-cli containerd.io
尝试安装 Docker 时你可能会遇到以下错误。
ror:
 Problem: problem with installed package buildah-1:1.26.2-1.el9_0.x86_64
  - package buildah-1:1.26.2-1.el9_0.x86_64 requires runc >= 1.0.0-26, but none of the providers can be installed
  - package containerd.io-1.6.9-3.1.el9.x86_64 conflicts with runc provided by runc-4:1.1.3-2.el9_0.x86_64
  - package containerd.io-1.6.9-3.1.el9.x86_64 obsoletes runc provided by runc-4:1.1.3-2.el9_0.x86_64
  - cannot install the best candidate for the job
如果出现上述错误,请使用以下命令。
$ sudo dnf install docker-ce docker-ce-cli containerd.io docker-compose-plugin --allowerasing
启用并运行 Docker 守护进程。
$ sudo systemctl enable docker --now
验证它是否正在运行。
? docker.service - Docker Application Container Engine
     Loaded: loaded (/usr/lib/systemd/system/docker.service; enabled; vendor preset: disabled)
     Active: active (running) since Sat 2022-11-12 00:19:44 UTC; 6s ago
TriggeredBy: ? docker.socket
       Docs: https://docs.docker.com
   Main PID: 99263 (dockerd)
      Tasks: 8
     Memory: 28.1M
        CPU: 210ms
     CGroup: /system.slice/docker.service
             ??99263 /usr/bin/dockerd -H fd:// --containerd=/run/containerd/containerd.sock
默认情况下,Docker 需要 root 权限。如果你想避免每次运行 docker 命令时都使用 sudo,请将你的用户名加入到 docker 组。
$ sudo usermod -aG docker $(whoami)
你需要注销服务器并以同一用户重新登录以使该更改生效,或者使用以下命令。
$ su - ${USER}
确认你的用户已加入 Docker 组。
$ groups
navjot wheel docker
步骤 3 - 创建 Docker Compose 配置
创建用于 Jellyfin Docker 配置的目录。
$ mkdir ~/jellyfin
切换到该目录。
$ cd ~/jellyfin
创建并打开 Docker Compose 文件进行编辑。
$ nano docker-compose.yml
在其中粘贴以下代码。
version: '3.8'
services:
  jellyfin:
    image: jellyfin/jellyfin
    container_name: jellyfin
    user: 1000:1000
    volumes:
      - ./config:/config
      - ./cache:/cache
      - ./media:/media
      - ./media2:/media2:ro
    restart: 'unless-stopped'
    ports:
      - 8096:8096
    # Optional - alternative address used for autodiscovery
    environment:
      - JELLYFIN_PublishedServerUrl=http://jellyfin.example.com
按 Ctrl + X 保存文件,并在提示时输入 Y。
上述 docker 文件会从 Docker Hub 仓库拉取最新版本的 Jellyfin 服务器。该镜像的用户和组 ID 都设置为 1000。你可以根据系统用户的 ID 进行修改以获得正确的权限。我们挂载了用于缓存、配置和媒体文件的目录。容器的重启策略设置为 unless-stopped,这意味着除非手动停止,否则它会持续运行。Jellyfin 默认运行在 8096 端口,我们已将该端口暴露给宿主机,供后续 Nginx 使用。我们还设置了一个指定 Jellyfin 公网 URL 的环境变量。
为缓存和配置目录创建目录,然后在 compose 文件中将它们挂载为持久化卷。我们还在文件中挂载了两个媒体目录。你可以根据需要创建任意数量的媒体目录。media2 目录以只读方式挂载。
步骤 4 - 启动 Jellyfin
使用以下命令验证 Docker Compose 配置。
$ docker compose config
你将收到类似的输出,确认配置有效。
name: jellyfin
services:
  jellyfin:
    container_name: jellyfin
    environment:
      JELLYFIN_PublishedServerUrl: http://jellyfin.nspeaks.xyz
    image: jellyfin/jellyfin
    network_mode: host
    restart: unless-stopped
    user: 1000:1000
    volumes:
    - type: bind
      source: /home/navjot/jellyfin/config
      target: /config
      bind:
        create_host_path: true
    - type: bind
      source: /home/navjot/jellyfin/cache
      target: /cache
      bind:
        create_host_path: true
    - type: bind
      source: /home/navjot/jellyfin/media
      target: /media
      bind:
        create_host_path: true
    - type: bind
      source: /home/navjot/jellyfin/media2
      target: /media2
      read_only: true
      bind:
        create_host_path: true
启动 Jellyfin 容器。
$ docker compose up -d
步骤 5 - 安装 Nginx
Rocky Linux 自带较旧版本的 Nginx。你需要下载官方的 Nginx 仓库以安装最新版本。
创建并打开 /etc/yum.repos.d/nginx.repo 文件以创建官方的 Nginx 仓库。
$ sudo nano /etc/yum.repos.d/nginx.repo
在其中粘贴以下代码。
[nginx-stable]
name=nginx stable repo
baseurl=http://nginx.org/packages/centos/$releasever/$basearch/
gpgcheck=1
enabled=1
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true

[nginx-mainline]
name=nginx mainline repo
baseurl=http://nginx.org/packages/mainline/centos/$releasever/$basearch/
gpgcheck=1
enabled=0
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true
按 Ctrl + X 保存文件,并在提示时输入 Y。
安装 Nginx 服务器。
$ sudo dnf install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.22.1
启用并启动 Nginx 服务器。
$ sudo systemctl enable nginx --now
检查服务器状态。
$ sudo systemctl status nginx
? nginx.service - nginx - high performance web server
     Loaded: loaded (/usr/lib/systemd/system/nginx.service; enabled; vendor preset: disabled)
     Active: active (running) since Sun 2022-11-13 13:49:55 UTC; 1s ago
       Docs: http://nginx.org/en/docs/
    Process: 230797 ExecStart=/usr/sbin/nginx -c /etc/nginx/nginx.conf (code=exited, status=0/SUCCESS)
   Main PID: 230798 (nginx)
      Tasks: 3 (limit: 12355)
     Memory: 2.8M
        CPU: 13ms
     CGroup: /system.slice/nginx.service
             ??230798 "nginx: master process /usr/sbin/nginx -c /etc/nginx/nginx.conf"
             ??230799 "nginx: worker process"
             ??230800 "nginx: worker process"
步骤 6 - 安装 SSL
Certbot 工具使用 Let's Encrypt API 生成 SSL 证书。它需要 EPEL 仓库才能工作。
$ sudo dnf install epel-release
我们将使用 Snapd 来安装 Certbot。安装 Snapd。
$ sudo dnf install snapd
启用并启动 Snap 服务。
$ sudo systemctl enable snapd --now
安装 Snap core 包。
$ sudo snap install core
$ sudo snap refresh core
为 Snapd 创建必要链接使其正常工作。
$ sudo ln -s /var/lib/snapd/snap /snap
$ echo 'export PATH=$PATH:/var/lib/snapd/snap/bin' | sudo tee -a /etc/profile.d/snapd.sh
执行以下命令以安装 Certbot。
$ sudo snap install --classic certbot
通过创建指向其可执行文件的符号链接来启用 Certbot。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d jellyfin.example.com
上述命令会将证书下载到你服务器上的 /etc/letsencrypt/live/jellyfin.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
要检查 SSL 续期是否正常工作,可以对该流程进行一次演练(dry run)。
$ sudo certbot renew --dry-run
如果没有看到错误,说明一切就绪。你的证书将自动续期。
步骤 7 - 配置 Nginx
打开 /etc/nginx/nginx.conf 文件进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 保存文件,并在提示时输入 Y。
创建并打开 /etc/nginx/conf.d/jellyfin.conf 文件进行编辑。
$ sudo nano /etc/nginx/conf.d/jellyfin.conf
在其中粘贴以下代码。
## Censor sensitive information in logs
log_format stripsecrets '$remote_addr $host - $remote_user [$time_local] '
                    '"$secretfilter" $status $body_bytes_sent '
                    '$request_length $request_time $upstream_response_time '
                    '"$http_referer" "$http_user_agent"';

map $request $secretfilter {
    ~*^(?<prefix1>.*[\?&]api_key=)([^&]*)(?<suffix1>.*)$  "${prefix1}***$suffix1";
    default                                               $request;
}

# Cache video streams
# Set in-memory cache-metadata size in keys_zone, size of video caching and how many days a cached object should persist
proxy_cache_path  /var/cache/nginx/jellyfin-videos levels=1:2 keys_zone=jellyfin-videos:100m inactive=90d max_size=35000m;
map $request_uri $h264Level { ~(h264-level=)(.+?)& $2; }
map $request_uri $h264Profile { ~(h264-profile=)(.+?)& $2; }

# Cache images
proxy_cache_path /var/cache/nginx/jellyfin levels=1:2 keys_zone=jellyfin:100m max_size=15g inactive=30d use_temp_path=off;

limit_conn_zone $binary_remote_addr zone=addr:10m;

server {
  listen 80;
  listen [::]:80;
  server_name jellyfin.example.com;
  location / { return 301 https://$host$request_uri; }
}

server {
   listen 443 ssl http2;
   listen [::]:443 ssl http2;
   server_name jellyfin.example.com;

   ## The default `client_max_body_size` is 1M, this might not be enough for some posters, etc.
   client_max_body_size 20M;

   # use a variable to store the upstream proxy
   # in this example we are using a hostname which is resolved via DNS
   # (if you aren't using DNS remove the resolver line and change the variable to point to an IP address e.g `set $jellyfin 127.0.0.1`)
   set $jellyfin jellyfin;
   resolver 127.0.0.1 valid=30;

   access_log  /var/log/nginx/jellyfin.access.log stripsecrets;
   error_log   /var/log/nginx/jellyfin.error.log;

   http2_push_preload on; # Enable HTTP/2 Server Push

   ssl_certificate /etc/letsencrypt/live/jellyfin.example.com/fullchain.pem;
   ssl_certificate_key /etc/letsencrypt/live/jellyfin.example.com/privkey.pem;
   ssl_trusted_certificate /etc/letsencrypt/live/jellyfin.example.com/chain.pem;
   ssl_session_timeout 1d;

   # Enable TLS versions (TLSv1.3 is required upcoming HTTP/3 QUIC).
   ssl_protocols TLSv1.2 TLSv1.3;

   # Enable TLSv1.3's 0-RTT. Use $ssl_early_data when reverse proxying to
   # prevent replay attacks.
   #
   # @see: https://nginx.org/en/docs/http/ngx_http_ssl_module.html#ssl_early_data
   ssl_early_data on;

   ssl_ciphers 'ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA384';
   ssl_prefer_server_ciphers on;
   ssl_session_cache shared:SSL:10m;
   ssl_session_tickets off;

   keepalive_timeout    70;
   sendfile             on;
   client_max_body_size 80m;

   # OCSP Stapling ---
   # fetch OCSP records from URL in ssl_certificate and cache them
   ssl_stapling on;
   ssl_stapling_verify on;
   ssl_dhparam /etc/ssl/certs/dhparam.pem;

   # Content Security Policy
   # See: https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP
   # Enforces https content and restricts JS/CSS to origin
   # External Javascript (such as cast_sender.js for Chromecast) must be whitelisted.
   # NOTE: The default CSP headers may cause issues with the webOS app
   add_header Content-Security-Policy "default-src https: data: blob: http://image.tmdb.org; style-src 'self' 'unsafe-inline'; script-src 'self' 'unsafe-inline' https://www.gstatic.com/cv/js/sender/v1/cast_sender.js https://www.gstatic.com/eureka/clank/95/cast_sender.js https://www.gstatic.com/eureka/clank/96/cast_sender.js https://www.gstatic.com/eureka/clank/97/cast_sender.js https://www.youtube.com blob:; worker-src 'self' blob:; connect-src 'self'; object-src 'none'; frame-ancestors 'self'";

   # Security / XSS Mitigation Headers
   # NOTE: X-Frame-Options may cause issues with the webOS app
   add_header X-Frame-Options "SAMEORIGIN";
   add_header X-XSS-Protection "1; mode=block";
   add_header X-Content-Type-Options "nosniff";
   add_header X-Early-Data $tls1_3_early_data;

   location = / {
       return 302 http://$host/web/;
       return 302 https://$host/web/;
   }

   location / {
       # Proxy main Jellyfin traffic
       proxy_pass http://$jellyfin:8096;
       proxy_set_header Host $host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-Forwarded-Protocol $scheme;
       proxy_set_header X-Forwarded-Host $http_host;
       proxy_buffering off;
  }

  # location block for /web - This is purely for aesthetics so /web/#!/ works instead of having to go to /web/index.html/#!/
   location = /web/ {
       # Proxy main Jellyfin traffic
       proxy_pass http://$jellyfin:8096/web/index.html;
       proxy_set_header Host $host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-Forwarded-Protocol $scheme;
       proxy_set_header X-Forwarded-Host $http_host;
   }

   location /socket {
       # Proxy Jellyfin Websockets traffic
       proxy_pass http://$jellyfin:8096;
       proxy_http_version 1.1;
       proxy_set_header Upgrade $http_upgrade;
       proxy_set_header Connection "upgrade";
       proxy_set_header Host $host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-Forwarded-Protocol $scheme;
       proxy_set_header X-Forwarded-Host $http_host;
   }

   # Cache video streams
   location ~* ^/Videos/(.*)/(?!live)
   {
       # Set size of a slice (this amount will be always requested from the backend by nginx)
       # Higher value means more latency, lower more overhead
       # This size is independent of the size clients/browsers can request
       slice 2m;

       proxy_cache jellyfin-videos;
       proxy_cache_valid 200 206 301 302 30d;
       proxy_ignore_headers Expires Cache-Control Set-Cookie X-Accel-Expires;
       proxy_cache_use_stale error timeout invalid_header updating http_500 http_502 http_503 http_504;
       proxy_connect_timeout 15s;
       proxy_http_version 1.1;
       proxy_set_header Connection "";
       # Transmit slice range to the backend
       proxy_set_header Range $slice_range;

       # This saves bandwidth between the proxy and jellyfin, as a file is only downloaded one time instead of multiple times when multiple clients want to at the same time
       # The first client will trigger the download, the other clients will have to wait until the slice is cached
       # Esp. practical during SyncPlay
       proxy_cache_lock on;
       proxy_cache_lock_age 60s;

       proxy_pass http://$jellyfin:8096;
       proxy_cache_key "jellyvideo$uri?MediaSourceId=$arg_MediaSourceId&VideoCodec=$arg_VideoCodec&AudioCodec=$arg_AudioCodec&AudioStreamIndex=$arg_AudioStreamIndex&VideoBitrate=$arg_VideoBitrate&AudioBitrate=$arg_AudioBitrate&SubtitleMethod=$arg_SubtitleMethod&TranscodingMaxAudioChannels=$arg_TranscodingMaxAudioChannels&RequireAvc=$arg_RequireAvc&SegmentContainer=$arg_SegmentContainer&MinSegments=$arg_MinSegments&BreakOnNonKeyFrames=$arg_BreakOnNonKeyFrames&h264-profile=$h264Profile&h264-level=$h264Level&slicerange=$slice_range";

       # add_header X-Cache-Status $upstream_cache_status; # This is only for debugging cache
   }

   # Cache images
   location ~ /Items/(.*)/Images {
       proxy_pass http://127.0.0.1:8096;
       proxy_set_header Host $host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-Forwarded-Protocol $scheme;
       proxy_set_header X-Forwarded-Host $http_host;

       proxy_cache jellyfin;
       proxy_cache_revalidate on;
       proxy_cache_lock on;
       # add_header X-Cache-Status $upstream_cache_status; # This is only to check if cache is working
   }

   # Downloads limit (inside server block)
   location ~ /Items/(.*)/Download$ {
       proxy_pass http://127.0.0.1:8096;
       proxy_set_header Host $host;
       proxy_set_header X-Real-IP $remote_addr;
       proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
       proxy_set_header X-Forwarded-Proto $scheme;
       proxy_set_header X-Forwarded-Protocol $scheme;
       proxy_set_header X-Forwarded-Host $http_host;

       limit_rate 1700k; # Speed limit (here is on kb/s)
       limit_conn addr 3; # Number of simultaneous downloads per IP
       limit_conn_status 460; # Custom error handling
       # proxy_buffering on; # Be sure buffering is on (it is by default on nginx), otherwise limits won't work
   }

}

# This block is useful for debugging TLS v1.3. Please feel free to remove this
# and use the `$ssl_early_data` variable exposed by NGINX directly should you
# wish to do so.
map $ssl_early_data $tls1_3_early_data {
  "~." $ssl_early_data;
  default "";
}
完成后,按 Ctrl + X 保存文件,并在提示时输入 Y。
验证 Nginx 配置文件的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
配置 SELinux 以允许网络连接。
$ sudo setsebool -P httpd_can_network_connect 1
重启 Nginx 服务器。
$ sudo systemctl restart nginx
如果你遇到以下错误,那很可能是由 SELinux 限制导致的。
nginx: [emerg] open() "/var/run/nginx.pid" failed (13: Permission denied)
要修复该错误,请运行以下命令。
$ sudo ausearch -c 'nginx' --raw | audit2allow -M my-nginx
$ sudo semodule -X 300 -i my-nginx.pp
再次启动 Nginx 服务。
$ sudo systemctl start nginx
步骤 8 - 访问并配置 Jellyfin
访问 URL https://jellyfin.example.com,你将看到以下界面。
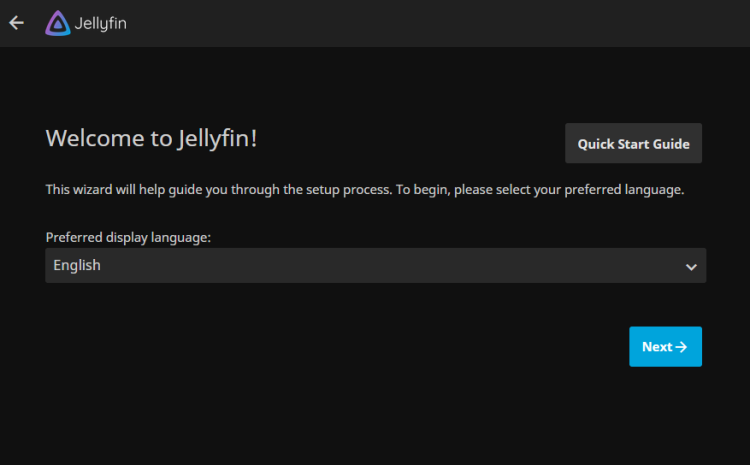
选择显示语言,然后点击 Next(下一步)按钮继续。
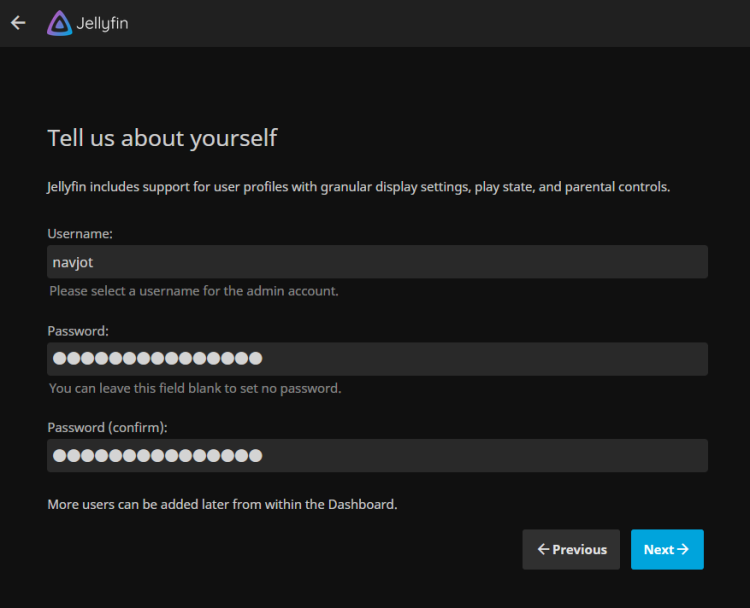
输入你的用户详情并点击 Next(下一步)按钮继续。点击 Add Media Library(添加媒体库)来添加媒体库。我们将添加一个用于电影的媒体库。
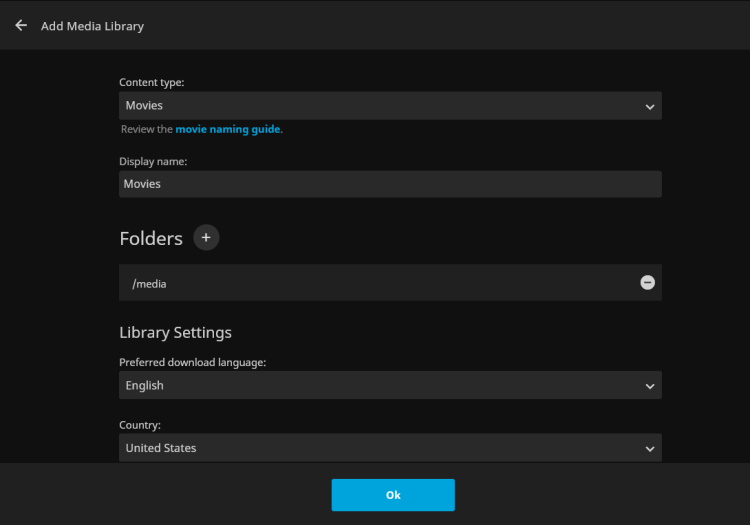
填写所有选项,并点击 Folders(文件夹)选项旁的加号来选择你的媒体库文件夹。向下滚动并填写所需的选项。点击 Ok(确定)按钮完成媒体库的添加。你将返回媒体库设置页面。
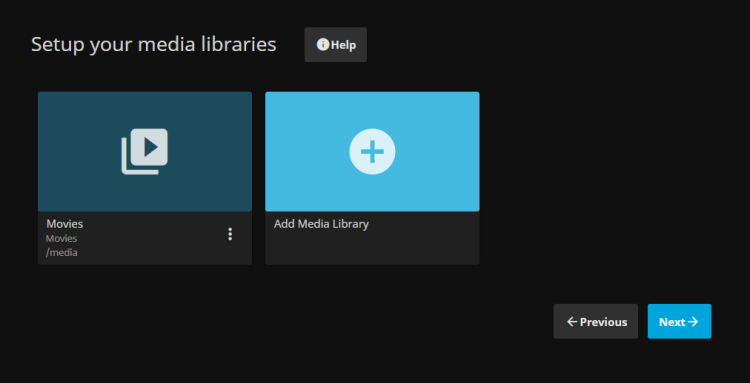
点击 Next(下一步)按钮继续。
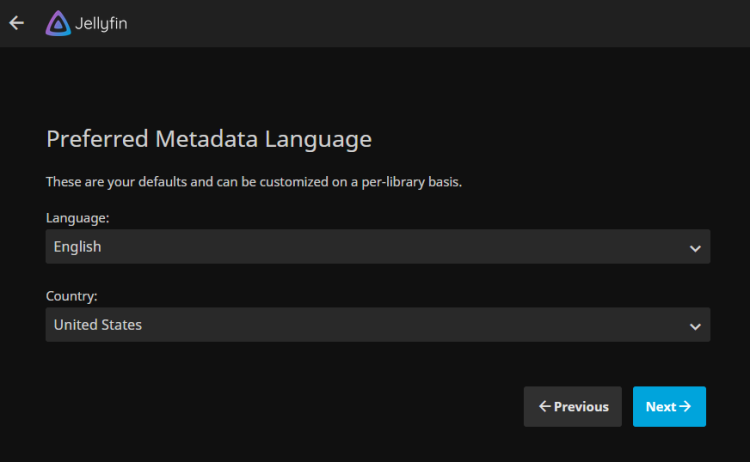
为你的媒体元数据选择语言和国家/地区,然后点击 Next(下一步)按钮继续。
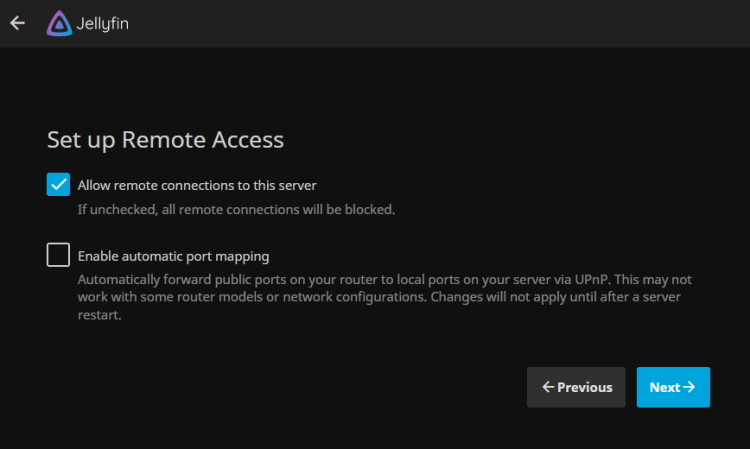
确保已勾选 Allow remote connections(允许远程连接)选项。如果你想使用端口映射,也请一并启用。完成后点击 Next(下一步)按钮。
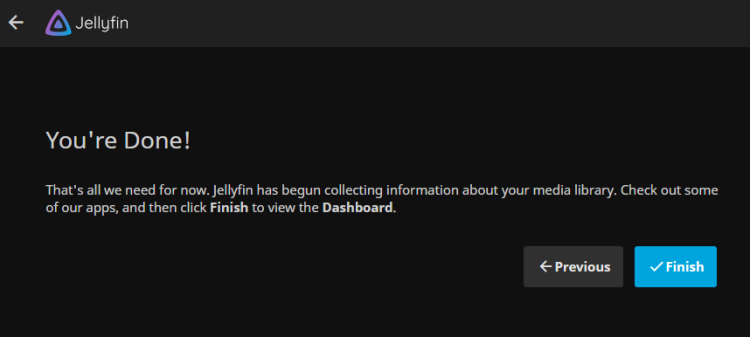
设置已完成。点击 Finish(完成)按钮进入 Jellyfin 登录页面。
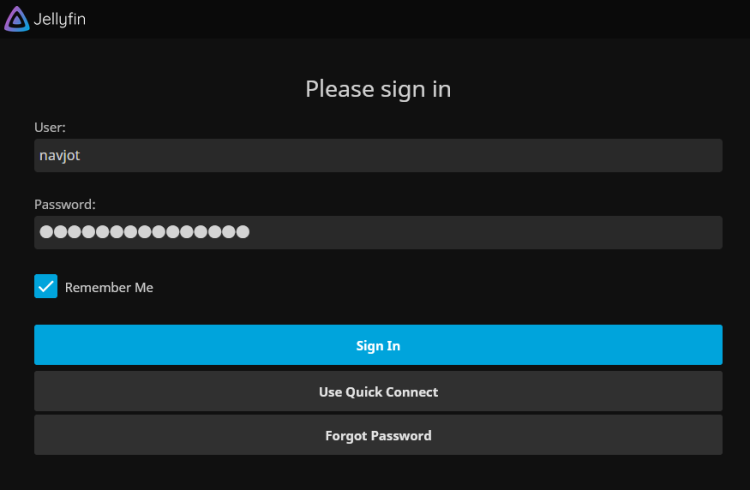
输入之前创建的用户详情,然后点击 Sign in(登录)按钮进入仪表盘。
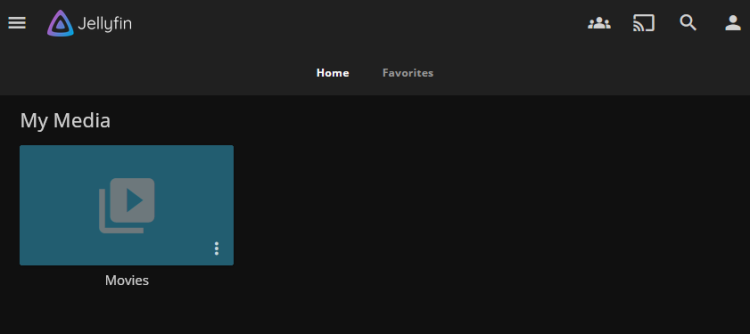
现在你可以开始使用 Jellyfin 播放你的内容了。
步骤 9 - 升级 Jellyfin
升级 Jellyfin 很简单,只需几个步骤。首先切换到该目录。
$ cd ~/jellyfin
停止 Jellyfin 容器。
$ docker compose down --remove-orphans
拉取 Jellyfin 的最新容器镜像。
$ docker compose pull
如果需要,可对 docker-compose.yml 进行任何修改。
启动 Jellyfin 容器。
$ docker compose up -d
结语
至此,本教程关于在 Rocky Linux 9 服务器上使用 Docker 安装 Jellyfin 媒体服务器的内容就结束了。如果你有任何问题,请在下方评论区留言。