
本教程适用于以下操作系统版本
- Ubuntu 22.04 (Jammy Jellyfish)
- Ubuntu 18.04 (Bionic Beaver)
本页内容
- 前提条件
- 准备工作
- 在 Ubuntu 22.04 上安装 Jitsi Meet
- 生成 Let's Encrypt 证书
- 配置 Jitsi Meet
- 重启 Jitsi 服务
- 配置 UFW 防火墙
- 访问 Jitsi Meet
- 总结
Jitsi 是一款免费且开源的聊天、电话和视频会议工具。它是 Skype、Zoom 和 Microsoft Teams 等其他工具的绝佳替代品。你无需注册或安装任何软件即可使用 Jitsi,可直接通过 Web 浏览器访问它。Jitsi 允许你使用 SIP 或 XMPP 协议进行免费通话、聊天、发送文件或共享屏幕。如果你正在寻找一款开源的视频会议和通话工具,那么 Jitsi 是你的最佳选择。
在本文中,我们将向你展示如何在 Ubuntu 22.04 服务器上安装 Jitsi Meet。
前提条件
- 一台运行 Ubuntu 22.04 且至少配备 4GB 内存的服务器。
- 一个指向你服务器 IP 的有效域名。
- 服务器上已配置 root 密码。
准备工作
在开始之前,你需要将所有软件包更新到最新版本。可以运行以下命令来更新它们:
apt-get update -y所有软件包更新完成后,你还需要在服务器上安装一些必需的依赖项。可以运行以下命令一次性安装它们:
apt-get install wget curl gnupg2 apt-transport-https -y所有软件包安装完成后,即可进入下一步。
在 Ubuntu 22.04 上安装 Jitsi Meet
默认情况下,Ubuntu 默认仓库中不包含 Jitsi Meet 软件。因此你需要将其官方仓库添加到 APT。
首先,使用以下命令将 Jitsi 仓库添加到 APT:
echo 'deb https://download.jitsi.org stable/' >> /etc/apt/sources.list.d/jitsi-stable.list接下来,使用以下命令下载并添加 Jitsi GPG 密钥:
wget -qO - https://download.jitsi.org/jitsi-key.gpg.key | apt-key add -接下来,使用以下命令更新仓库并安装 Jitsi Meet:
apt-get update -y
apt-get install jitsi-meet -y
在安装过程中,系统会要求你提供系统的完全限定主机名,如下所示:
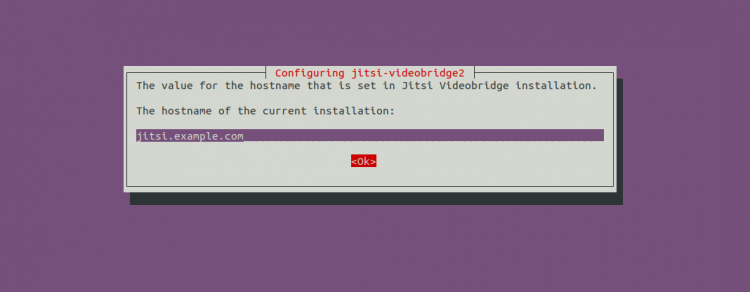
输入你的系统主机名并点击 Ok 按钮。随后系统会询问是否安装 SSL 证书:

选择「Generate a new Self-signed certificate」并按 Ok 按钮以完成安装。
生成 Let's Encrypt 证书
对于生产环境,不建议使用自签名 SSL 证书。因此你需要为 Jitsi 安装 Let's Encrypt SSL 证书。
可以使用以下命令安装 Let's Encrypt SSL 证书:
/usr/share/jitsi-meet/scripts/install-letsencrypt-cert.sh系统会要求你输入邮箱地址以安装 Let's Encrypt SSL 证书:
-------------------------------------------------------------------------
This script will:
- Need a working DNS record pointing to this machine(for domain jitsi.example.com)
- Download certbot-auto from https://dl.eff.org to /usr/local/sbin
- Install additional dependencies in order to request Let’s Encrypt certificate
- If running with jetty serving web content, will stop Jitsi Videobridge
- Configure and reload nginx or apache2, whichever is used
- Configure the coturn server to use Let's Encrypt certificate and add required deploy hooks
- Add command in weekly cron job to renew certificates regularly

You need to agree to the ACME server's Subscriber Agreement (https://letsencrypt.org/documents/LE-SA-v1.1.1-August-1-2016.pdf)
by providing an email address for important account notifications
Enter your email and press [ENTER]:
[email protected]


Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator webroot, Installer None
Obtaining a new certificate
Performing the following challenges:
http-01 challenge for jitsi.example.com
Using the webroot path /usr/share/jitsi-meet for all unmatched domains.
Waiting for verification...
Cleaning up challenges
Running deploy-hook command: /etc/letsencrypt/renewal-hooks/deploy/0000-coturn-certbot-deploy.sh
Output from deploy-hook command 0000-coturn-certbot-deploy.sh:
Configuring turnserver


IMPORTANT NOTES:
- Congratulations! Your certificate and chain have been saved at:
/etc/letsencrypt/live/jitsi.example.com/fullchain.pem
Your key file has been saved at:
/etc/letsencrypt/live/jitsi.example.com/privkey.pem
Your cert will expire on 2022-09-27. To obtain a new or tweaked
version of this certificate in the future, simply run certbot
again. To non-interactively renew *all* of your certificates, run
"certbot renew"
- Your account credentials have been saved in your Certbot
configuration directory at /etc/letsencrypt. You should make a
secure backup of this folder now. This configuration directory will
also contain certificates and private keys obtained by Certbot so
making regular backups of this folder is ideal.
- If you like Certbot, please consider supporting our work by:

Donating to ISRG / Let's Encrypt: https://letsencrypt.org/donate
Donating to EFF: https://eff.org/donate-le
配置 Jitsi Meet
接下来,你需要编辑 Jitsi Meet 配置文件,将其配置为仅允许已注册用户创建会议室。
nano /etc/prosody/conf.avail/jitsi.example.com.cfg.lua修改以下几行:
authentication = "anonymous"
authentication = "internal_plain"
VirtualHost "guest.jitsi.example.com"
authentication = "anonymous"
c2s_require_encryption = false
保存并关闭该文件,然后打开另一个配置文件:
nano /etc/jitsi/meet/jitsi.example.com-config.js添加以下一行:
anonymousdomain: 'guest.jitsi.example.com',
接下来,使用以下命令创建 SIP 配置文件:
nano /etc/jitsi/jicofo/sip-communicator.properties添加以下一行:
org.jitsi.jicofo.auth.URL=XMPP:jitsi.example.com
保存并关闭该文件,然后使用以下命令为 Jitsi 创建用户:
prosodyctl register user jitsi.example.com password重启 Jitsi 服务
接下来,你需要重启所有 Jitsi 服务以使配置更改生效。可以使用以下命令完成:
systemctl restart prosody.service jicofo.service jitsi-videobridge2.service现在,使用以下命令检查 Prosody 服务的状态:
systemctl status prosody.service你应该会看到以下输出:
? prosody.service - Prosody XMPP Server
     Loaded: loaded (/lib/systemd/system/prosody.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2022-06-25 16:15:58 UTC; 5s ago
       Docs: https://prosody.im/doc
   Main PID: 62561 (lua5.2)
      Tasks: 1 (limit: 4579)
     Memory: 9.3M
        CPU: 475ms
     CGroup: /system.slice/prosody.service
             ??62561 lua5.2 /usr/bin/prosody -F

Jun 25 16:15:58 ubuntu2204 systemd[1]: Started Prosody XMPP Server.
要检查 Jicofo 服务的状态,请运行以下命令:
systemctl status jicofo.service你应该会看到以下输出:
? jicofo.service - LSB: Jitsi conference Focus
     Loaded: loaded (/etc/init.d/jicofo; generated)
     Active: active (running) since Sat 2022-06-25 16:15:58 UTC; 22s ago
       Docs: man:systemd-sysv-generator(8)
    Process: 62534 ExecStart=/etc/init.d/jicofo start (code=exited, status=0/SUCCESS)
      Tasks: 35 (limit: 4579)
     Memory: 177.4M
        CPU: 8.700s
     CGroup: /system.slice/jicofo.service
             ??62540 java -Xmx3072m -XX:+HeapDumpOnOutOfMemoryError -XX:HeapDumpPath=/tmp -Djdk.tls.ephemeralDHKeySize=2048 -Dconfig.file=/et>

Jun 25 16:15:58 ubuntu2204 systemd[1]: Starting LSB: Jitsi conference Focus...
Jun 25 16:15:58 ubuntu2204 jicofo[62534]: Starting jicofo: jicofo started.
Jun 25 16:15:58 ubuntu2204 systemd[1]: Started LSB: Jitsi conference Focus.
要检查 Jitsi videobridge2 服务,请运行以下命令:
systemctl status jitsi-videobridge2.service你应该会看到以下输出:
? jitsi-videobridge2.service - Jitsi Videobridge
     Loaded: loaded (/lib/systemd/system/jitsi-videobridge2.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2022-06-25 16:15:58 UTC; 35s ago
    Process: 62564 ExecStartPost=/bin/bash -c echo $MAINPID > /var/run/jitsi-videobridge/jitsi-videobridge.pid (code=exited, status=0/SUCCESS)
   Main PID: 62563 (java)
      Tasks: 48 (limit: 65000)
     Memory: 171.4M
        CPU: 9.877s
     CGroup: /system.slice/jitsi-videobridge2.service
             ??62563 java -Xmx3072m -XX:+UseG1GC -XX:+HeapDumpOnOutOfMemoryError -XX:HeapDumpPath=/tmp -Djdk.tls.ephemeralDHKeySize=2048 -Dco>

Jun 25 16:15:58 ubuntu2204 systemd[1]: Starting Jitsi Videobridge...
Jun 25 16:15:58 ubuntu2204 systemd[1]: Started Jitsi Videobridge.
配置 UFW 防火墙
接下来,你需要通过防火墙放行所有 Jitsi 端口,以便能够从远程机器访问它。可以通过 UFW 放行这些端口,如下所示:
ufw allow 80/tcp
ufw allow 443/tcp
ufw allow 4443/tcp
ufw allow 10000/udp
ufw allow 22/tcp
ufw enable
也可以使用以下命令检查防火墙规则:
ufw statusUFW 防火墙配置完成后,即可进入下一步。
访问 Jitsi Meet
至此,Jitsi Meet 已在你的 Ubuntu 22.04 服务器上安装并配置完成。现在可以通过 URL https://jitsi.example.com 访问其 Web 界面。你应该会看到 Jitsi Meet 的会议室创建页面:
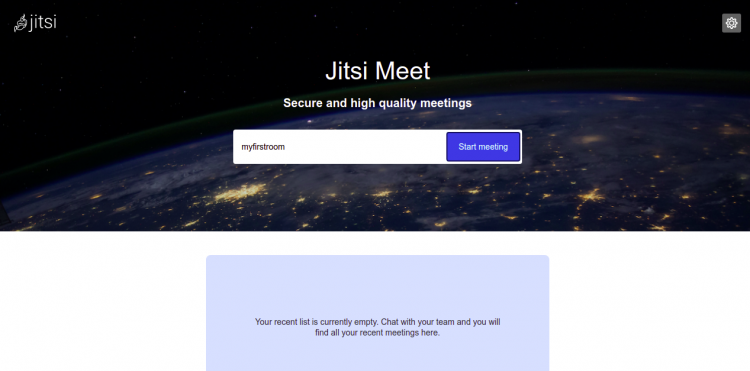
现在可以输入你的会议室名称并开始使用 Jitsi。
总结
恭喜!你已在 Ubuntu 22.04 服务器上成功安装了带有 Let's Encrypt SSL 证书的 Jitsi Meet。现在可以通过 Web 浏览器或移动应用访问 Jitsi,并与其他用户开始通话。