
本页内容
- 先决条件
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装并配置 PostgreSQL
- 第 3 步 - 安装并配置 Redis
- 第 4 步 - 下载 NetBox
- 第 5 步 - 配置 NetBox
- 第 6 步 - 安装 NetBox
- 第 7 步 - 配置 Gunicorn 并创建服务文件
- 第 8 步 - 安装 Nginx
- 第 9 步 - 安装 SSL
- 第 10 步 - 配置 Nginx
- 第 11 步 - 升级 NetBox
- 结语
NetBox 是一个开源的 IP 地址管理(IPAM)和数据中心基础设施管理(DCIM)Web 应用程序,用于管理和记录计算机网络及 IP 地址。它由 DigitalOcean 的网络工程团队最初构想。它是使用 Django Python 框架编写的,并使用 PostgreSQL 数据库进行数据存储。它还使用 Redis 数据库来缓存查询。
本教程将教你如何在 Ubuntu 22.04 服务器上安装 NetBox 工具,并将 Nginx 用作反向代理服务器。
先决条件
- 运行 Ubuntu 22.04 的服务器。
- 具有 sudo 权限的非 root 用户。
- 一个完全限定域名(FQDN),例如 netbox.example.com 。
- 确保所有内容都已更新。 $ sudo apt update $ sudo apt upgrade
- 你的系统需要的一些软件包。 $ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y 其中部分软件包可能已在你的系统上安装。
运行 Ubuntu 22.04 的服务器。
具有 sudo 权限的非 root 用户。
一个完全限定域名(FQDN),例如 netbox.example.com 。
确保所有内容都已更新。
$ sudo apt update
$ sudo apt upgrade
你的系统需要的一些软件包。
$ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y
其中部分软件包可能已在你的系统上安装。
第 1 步 - 配置防火墙
第一步是配置防火墙。Ubuntu 默认附带了 ufw(Uncomplicated Firewall,简单防火墙)。
检查防火墙是否正在运行。
$ sudo ufw status
你应该会得到如下输出。
Status: inactive
允许 SSH 端口,以便防火墙在启用时不会中断当前连接。
$ sudo ufw allow OpenSSH
同时允许 HTTP 和 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
启用防火墙
$ sudo ufw enable
Command may disrupt existing ssh connections. Proceed with operation (y|n)? y
Firewall is active and enabled on system startup
再次检查防火墙的状态。
$ sudo ufw status
你应该会看到类似的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
第 2 步 - 安装并配置 PostgreSQL
NetBox 可与 PostgreSQL 11 及更高版本配合使用。Ubuntu 22.04 默认附带 PostgreSQL 14。在本教程中我们将使用 PostgreSQL 15。
运行以下命令以添加 PostgreSQL 的 GPG 密钥。
$ curl https://www.postgresql.org/media/keys/ACCC4CF8.asc | gpg --dearmor | sudo tee /usr/share/keyrings/postgresql-key.gpg >/dev/null
将 APT 仓库添加到你的软件源列表中。
$ sudo sh -c 'echo "deb [signed-by=/usr/share/keyrings/postgresql-key.gpg arch=amd64] http://apt.postgresql.org/pub/repos/apt $(lsb_release -cs)-pgdg main" > /etc/apt/sources.list.d/pgdg.list'
更新系统仓库。
$ sudo apt update
现在,你可以使用以下命令安装 PostgreSQL。
$ sudo apt install postgresql postgresql-contrib
postgresql-contrib 软件包包含一些额外的实用工具。
检查 PostgreSQL 服务的状态。
$ sudo systemctl status postgresql
? postgresql.service - PostgreSQL RDBMS
     Loaded: loaded (/lib/systemd/system/postgresql.service; enabled; vendor preset: enabled)
     Active: active (exited) since Tue 2022-11-27 9:10:35 UTC; 5s ago
    Process: 30544 ExecStart=/bin/true (code=exited, status=0/SUCCESS)
   Main PID: 30544 (code=exited, status=0/SUCCESS)
        CPU: 2ms

Dec 27 9:10:35 netbox systemd[1]: Starting PostgreSQL RDBMS...
Dec 27 9:10:35 netbox systemd[1]: Finished PostgreSQL RDBMS.
你可以看到该服务默认已启用并正在运行。
启动 PostgreSQL 命令行。
$ sudo -i -u postgres psql
创建 NetBox 数据库。
postgres=# CREATE DATABASE netbox;
创建 NetBox 用户并选择一个强密码。
postgres-# CREATE USER netbox WITH PASSWORD 'Your_Password';
将数据库的所有者更改为 NetBox 用户。
postgres-# ALTER DATABASE netbox OWNER TO netbox;
退出命令行。
postgres-# \q
验证你的凭据是否有效。
$ psql --username netbox --password --host localhost netbox
Password for user netbox:
psql (15.1 (Ubuntu 15.1-1.pgdg22.04+1))
SSL connection (protocol: TLSv1.3, cipher: TLS_AES_256_GCM_SHA384, bits: 256, compression: off)
Type "help" for help.

netbox=>
通过输入 \q 退出命令行。
第 3 步 - 安装并配置 Redis
Ubuntu 自带 Redis 6.0.16。在本教程中,我们将从官方仓库安装最新版本。
导入官方的 Redis GPG 密钥。
$ curl -fsSL https://packages.redis.io/gpg | sudo gpg --dearmor -o /usr/share/keyrings/redis-archive-keyring.gpg
将 APT 仓库添加到你的软件源列表中。
echo "deb [signed-by=/usr/share/keyrings/redis-archive-keyring.gpg] https://packages.redis.io/deb $(lsb_release -cs) main" | sudo tee /etc/apt/sources.list.d/redis.list
更新系统仓库列表。
$ sudo apt update
执行以下命令以安装 Redis 服务器。
$ sudo apt install redis
确认 Redis 版本。
$ redis-server -v
Redis server v=7.0.7 sha=00000000:0 malloc=jemalloc-5.2.1 bits=64 build=2260280010e18db8
让我们使用以下命令验证服务连接。
$ redis-cli
你将被切换到 Redis 命令行。
第一步是为 Redis 默认用户设置密码。将 Your_Redis_Password 替换为你自行选择的强密码。
127.0.0.1:6379> acl setuser default >Your_Redis_Password
测试 Redis 身份验证。
127.0.0.1:6379> AUTH Your_Redis_Password
OK
Ping 该服务。
127.0.0.1:6379> ping
PONG
通过输入 exit 退出该服务。
第 4 步 - 下载 NetBox
NetBox 需要 Python Django 才能运行。安装 NetBox 的第一步是安装所需的 Python 软件包。运行以下命令以安装所需的 Python 软件包。
$ sudo apt install -y python3 python3-pip python3-venv python3-dev build-essential libxml2-dev libxslt1-dev libffi-dev libpq-dev libssl-dev zlib1g-dev
检查 Python 版本。
$ python3 -V
Python 3.10.6
为 NetBox 安装创建基础目录。
$ sudo mkdir -p /opt/netbox/
切换到该目录。
$ cd /opt/netbox
将 NetBox 的 GitHub 仓库的 master 分支克隆到当前目录。
$ sudo git clone -b master --depth 1 https://github.com/netbox-community/netbox.git .
--depth 1 标志仅获取仓库中最近的一次提交。如果你想下载完整的提交历史,可以省略该标志。
从 releases 页面查看 NetBox 的最新版本,并使用 Git 检出该版本。在撰写本教程时,3.4.1 是最新的可用版本。
$ git config --global --add safe.directory /opt/netbox
$ sudo git checkout v3.4.1
在检出之前,你需要将该目录添加到 Git 的安全目录列表中。这是较新版本 Git 中提供的一项新的安全特性。
下一步是为 NetBox 创建一个系统用户和组。
$ sudo adduser --system --group netbox
授予该用户对 NetBox 的 media 目录的权限。
$ sudo chown --recursive netbox /opt/netbox/netbox/media/
第 5 步 - 配置 NetBox
切换到 NetBox 配置目录。
$ cd /opt/netbox/netbox/netbox/
复制示例配置文件以创建实际配置文件。
$ sudo cp configuration_example.py configuration.py
在进行配置之前,我们需要为 NetBox 创建一个密钥。请记下该密钥,因为我们需要在配置中使用它。
$ python3 ../generate_secret_key.py
dSSWi$Ar2cVvu1)V!B82sY1tJAQK9r)vzM8ReQRF7@C^+$=1+(
打开配置文件进行编辑。
$ sudo nano configuration.py
找到 ALLOWED_HOSTS 变量并按如下方式设置其值。该变量保存着可通过其访问此服务器的有效主机名和 IP 地址的列表。
ALLOWED_HOSTS = ['netbox.example.com', '<yourserverIP>']
下一步是编辑数据库详细信息。按如下方式配置数据库详细信息。
DATABASE = {
    'NAME': 'netbox',              # Database name
    'USER': 'netbox',              # PostgreSQL username
    'PASSWORD': 'Your_Password',   # PostgreSQL password
    'HOST': 'localhost',           # Database server
    'PORT': '',                    # Database port (leave blank for default)
    'CONN_MAX_AGE': 300,           # Max database connection age
}
按图示配置 Redis。输入你在第 3 步中设置的 Redis 密码。
REDIS = {
    'tasks': {
        'HOST': 'localhost',
        'PORT': 6379,
        # Comment out `HOST` and `PORT` lines and uncomment the following if using Redis Sentinel
        # 'SENTINELS': [('mysentinel.redis.example.com', 6379)],
        # 'SENTINEL_SERVICE': 'netbox',
        'PASSWORD': 'Your_Redis_Password',
        'DATABASE': 0,
        'SSL': False,
        # Set this to True to skip TLS certificate verification
        # This can expose the connection to attacks, be careful
        # 'INSECURE_SKIP_TLS_VERIFY': False,
    },
    'caching': {
        'HOST': 'localhost',
        'PORT': 6379,
        # Comment out `HOST` and `PORT` lines and uncomment the following if using Redis Sentinel
        # 'SENTINELS': [('mysentinel.redis.example.com', 6379)],
        # 'SENTINEL_SERVICE': 'netbox',
        'PASSWORD': 'Your_Redis_Password',
        'DATABASE': 1,
        'SSL': False,
        # Set this to True to skip TLS certificate verification
        # This can expose the connection to attacks, be careful
        # 'INSECURE_SKIP_TLS_VERIFY': False,
    }
}
将该密钥的值添加到变量中。
SECRET_KEY = 'dSSWi$Ar2cVvu1)V!B82sY1tJAQK9r)vzM8ReQRF7@C^+$=1+('
默认情况下,NetBox 使用本地文件系统来存储上传的文件。你可以通过安装 django-storages 库将文件存储在远程文件系统上。运行以下命令将 django-storages 软件包添加到 NetBox 的 requirements.txt 中,随后将在后续步骤中安装它。我们还需要配置存储参数。取消注释配置文件中的存储部分,并按如下方式进行。
STORAGE_BACKEND = 'storages.backends.s3boto3.S3Boto3Storage'
STORAGE_CONFIG = {
    'AWS_ACCESS_KEY_ID': 'Key ID',
    'AWS_SECRET_ACCESS_KEY': 'Secret',
    'AWS_STORAGE_BUCKET_NAME': 'netbox',
    'AWS_S3_REGION_NAME': 'eu-west-1',
}
也支持其他存储类型,包括 FTP、SFTP、Dropbox 以及其他 S3 提供商。要了解如何配置它们,你可以阅读 django-storages 帮助页面。
按 Ctrl + X 并在提示时输入 Y 保存文件。
第 6 步 - 安装 NetBox
运行 NetBox 升级脚本。
$ sudo /opt/netbox/upgrade.sh
升级脚本执行以下任务。
- 创建一个 Python 虚拟环境
- 安装所有必需的 Python 软件包
- 运行数据库模式迁移
- 在本地构建文档(用于离线使用)
- 在磁盘上聚合静态资源文件
激活由升级脚本创建的虚拟环境。
$ source /opt/netbox/venv/bin/activate
下一步是创建一个超级用户以访问 NetBox。但首先,切换到所需目录。
(venv) $ cd /opt/netbox/netbox
创建超级用户。
(venv) $ python3 manage.py createsuperuser
你将得到如下输出。
Username (leave blank to use 'navjot'):
Email address:
[email protected]

Password:
Password (again):
Superuser created successfully.
NetBox 包含一个 housekeeping 管理命令,用于处理周期性清理任务,例如清除旧的会话和已过期的变更记录。你可以手动运行该命令,或使用 cron 定期运行它。NetBox 提供了一个 shell 脚本来运行 housekeeping 任务。运行以下命令以在 Cron 每日目录中为该脚本创建软链接。这将确保该命令每天运行。
(venv) $ sudo ln -s /opt/netbox/contrib/netbox-housekeeping.sh /etc/cron.daily/netbox-housekeeping
最后一步是测试 NetBox 应用程序是否正常工作。但首先,我们需要为测试打开 8000 端口。不过你可以使用任何端口。
(venv) $ sudo ufw allow 8000
启动 NetBox 的开发实例。
(venv) $ python3 manage.py runserver 0.0.0.0:8000 --insecure
如果成功,你将得到如下输出。
Performing system checks...

System check identified no issues (0 silenced).
December 27, 2022 - 09:27:37
Django version 4.1.4, using settings 'netbox.settings'
Starting development server at http://0.0.0.0:8000/
Quit the server with CONTROL-C.
你应该能够通过 URL http://
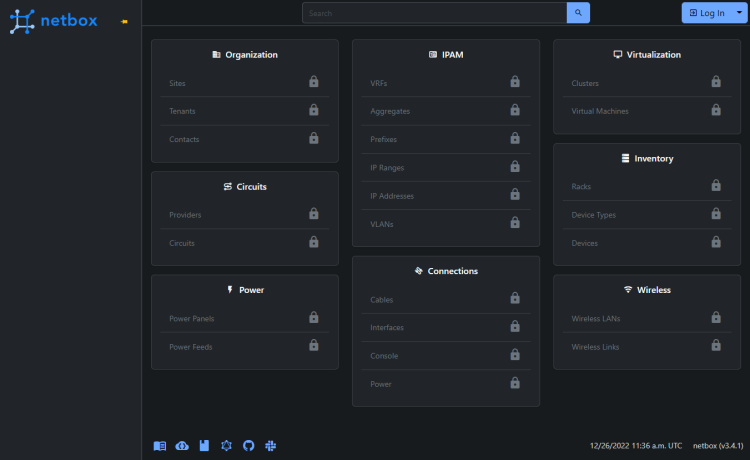
点击 Log In 按钮打开登录页面,并输入之前创建的超级用户凭据。
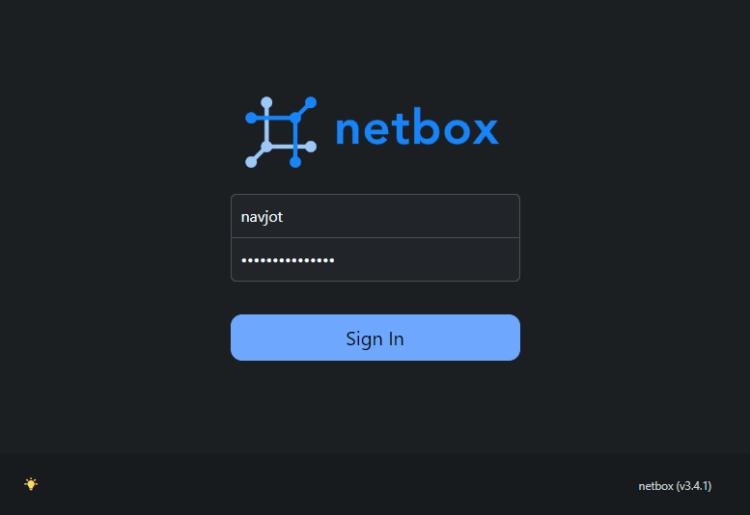
你将被带回 NetBox 仪表板。
按 Ctrl + C 键停止服务器。停用 Python 虚拟环境。
(venv) $ deactivate
第 7 步 - 配置 Gunicorn 并创建服务文件
NetBox 作为 WSGI 应用程序运行在 HTTP 服务器之后。NetBox 会自动安装 Gunicorn 服务器。在此步骤中,我们将配置 Gunicorn 并为 NetBox 创建一个服务文件,以便它可以在后台运行并在系统重启后保持运行。
NetBox 附带一个默认的 Gunicorn 配置文件。创建它的副本。
$ sudo cp /opt/netbox/contrib/gunicorn.py /opt/netbox/gunicorn.py
默认配置应该足以满足我们的需求。根据你的需要,你可以编辑该文件以更改主机名、端口号,或通过更改线程、worker 和请求数量来进行性能优化。
下一步是将 NetBox 和 Gunicorn 的服务文件都复制到 /etc/systemd/system 目录。
$ sudo cp -v /opt/netbox/contrib/*.service /etc/systemd/system/
重新加载服务守护进程。
$ sudo systemctl daemon-reload
启动并启用 netbox 和 netbox-rq 服务。
$ sudo systemctl start netbox netbox-rq
$ sudo systemctl enable netbox netbox-rq
检查 WSGI 服务的状态。
$ sudo systemctl status netbox
你将得到类似的输出。
? netbox.service - NetBox WSGI Service
     Loaded: loaded (/etc/systemd/system/netbox.service; enabled; vendor preset: enabled)
     Active: active (running) since Tue 2022-12-27 09:28:23 UTC; 17s ago
       Docs: https://docs.netbox.dev/
   Main PID: 4180 (gunicorn)
      Tasks: 6 (limit: 1030)
     Memory: 357.9M
        CPU: 7.747s
     CGroup: /system.slice/netbox.service
             ??4180 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi
             ??4181 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi
             ??4182 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi
             ??4183 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi
             ??4184 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi
             ??4185 /opt/netbox/venv/bin/python3 /opt/netbox/venv/bin/gunicorn --pid /var/tmp/netbox.pid --pythonpath /opt/netbox/netbox --config /opt/netbox/gunicorn.py netbox.wsgi

Dec 27 09:28:23 netbox systemd[1]: Started NetBox WSGI Service.
Dec 27 09:28:24 netbox gunicorn[4180]: [2022-12-27 09:28:24 +0000] [4180] [INFO] Starting gunicorn 20.1.0
Dec 27 09:28:24 netbox gunicorn[4180]: [2022-12-27 09:28:24 +0000] [4180] [INFO] Listening at: http://127.0.0.1:8001 (4180)
Dec 27 09:28:24 netbox gunicorn[4180]: [2022-12-27 09:28:24 +0000] [4180] [INFO] Using worker: gthread
Dec 27 09:28:24 netbox gunicorn[4181]: [2022-12-27 09:28:24 +0000] [4181] [INFO] Booting worker with pid: 4181
Dec 27 09:28:24 netbox gunicorn[4182]: [2022-12-27 09:28:24 +0000] [4182] [INFO] Booting worker with pid: 4182
Dec 27 09:28:24 netbox gunicorn[4183]: [2022-12-27 09:28:24 +0000] [4183] [INFO] Booting worker with pid: 4183
Dec 27 09:28:24 netbox gunicorn[4184]: [2022-12-27 09:28:24 +0000] [4184] [INFO] Booting worker with pid: 4184
Dec 27 09:28:24 netbox gunicorn[4185]: [2022-12-27 09:28:24 +0000] [4185] [INFO] Booting worker with pid: 4185
如你所见,Gunicorn 默认监听 8001 端口。在将 Nginx 配置为反向代理服务器时,此信息将很有用。
第 8 步 - 安装 Nginx
Ubuntu 22.04 自带较旧版本的 Nginx。要安装最新版本,你需要下载官方的 Nginx 仓库。
导入 Nginx 的签名密钥。
$ curl https://nginx.org/keys/nginx_signing.key | gpg --dearmor \
	| sudo tee /usr/share/keyrings/nginx-archive-keyring.gpg >/dev/null
为 Nginx 的稳定版本添加仓库。
$ echo "deb [signed-by=/usr/share/keyrings/nginx-archive-keyring.gpg arch=amd64] \
http://nginx.org/packages/ubuntu `lsb_release -cs` nginx" \
    | sudo tee /etc/apt/sources.list.d/nginx.list
更新系统仓库。
$ sudo apt update
安装 Nginx。
$ sudo apt install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.22.1
启动 Nginx 服务器。
$ sudo systemctl start nginx
第 9 步 - 安装 SSL
我们需要安装 Certbot 来生成 SSL 证书。你可以使用 Ubuntu 的仓库安装 Certbot,也可以使用 Snapd 工具获取最新版本。我们将使用 Snapd 版本。
Ubuntu 22.04 默认安装了 Snapd。运行以下命令以确保你的 Snapd 版本是最新的。请确保你的 Snapd 版本是最新的。
$ sudo snap install core
$ sudo snap refresh core
安装 Certbot。
$ sudo snap install --classic certbot
使用以下命令创建指向 /usr/bin 目录的符号链接,以确保 Certbot 命令可以运行。
$ sudo ln -s /snap/bin/certbot /usr/bin/certbot
运行以下命令以生成 SSL 证书。
$ sudo certbot certonly --nginx --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d netbox.example.com
上述命令会将证书下载到服务器上的 /etc/letsencrypt/live/netbox.example.com 目录。
生成 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
要检查 SSL 续期是否正常工作,请对该过程进行一次演练(dry run)。
$ sudo certbot renew --dry-run
如果你没有看到任何错误,则说明一切就绪。你的证书将自动续期。
第 10 步 - 配置 Nginx
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 并在提示时输入 Y 保存文件。
创建并打开文件 /etc/nginx/conf.d/netbox.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/netbox.conf
在其中粘贴以下代码。
server {
  # Redirect any http requests to https
  listen         80;
  listen         [::]:80;
  server_name    netbox.example.com;
  return 301     https://$host$request_uri;
}

server {
  listen                    443 ssl http2;
  listen                    [::]:443 ssl http2;
  server_name               netbox.example.com;

  access_log                /var/log/nginx/netbox.access.log;
  error_log                 /var/log/nginx/netbox.error.log;

  # TLS configuration
  ssl_certificate           /etc/letsencrypt/live/netbox.example.com/fullchain.pem;
  ssl_certificate_key       /etc/letsencrypt/live/netbox.example.com/privkey.pem;
  ssl_trusted_certificate   /etc/letsencrypt/live/netbox.example.com/chain.pem;
  ssl_protocols             TLSv1.2 TLSv1.3;

  ssl_ciphers 'ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA384';
  ssl_prefer_server_ciphers on;
  ssl_session_cache         shared:SSL:50m;
  ssl_session_timeout       1d;

  # OCSP Stapling ---
  # fetch OCSP records from URL in ssl_certificate and cache them
  ssl_stapling on;
  ssl_stapling_verify on;
  ssl_dhparam /etc/ssl/certs/dhparam.pem;

  client_max_body_size 25m;

  # Proxy everything over to the netbox server
  location /static/ {
    alias /opt/netbox/netbox/static/;
  }

  location / {
    proxy_set_header        X-Real-IP $remote_addr;
    proxy_set_header        X-Forwarded-Proto $scheme;
    proxy_set_header	    X-Forwarded-Host $http_host;
    proxy_pass              http://127.0.0.1:8001;
  }
}
完成后按 Ctrl + X 并在提示时输入 Y 保存文件。
验证 Nginx 配置文件语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx 服务。
$ sudo systemctl restart nginx
你现在可以通过 URL https://netbox.example.com 访问 NetBox 仪表板。
第 11 步 - 升级 NetBox
升级 NetBox 非常简单。这些步骤包括检出 Git 仓库的 master 分支、拉取最新提交,然后检出新的稳定版本。
切换到 NetBox 目录。
$ cd /opt/netbox
检出 master 分支。
$ sudo git checkout master
从仓库拉取最新的提交。
$ sudo git pull origin master
检出新版本。如果 3.4.2 是较新的版本,你可以检出该版本。
$ sudo git checkout v3.4.2
运行升级脚本。
$ sudo ./upgrade.sh
对于升级过程,该脚本执行以下功能。
- 销毁并重建 Python 虚拟环境
- 安装所有必需的 Python 软件包(列于 requirements.txt 中)
- 从 local_requirements.txt 安装任何额外的软件包
- 应用该版本中包含的任何数据库迁移
- 在本地构建文档(用于离线使用)
- 收集所有由 HTTP 服务提供的静态文件
- 从数据库中删除过时的内容类型
- 从数据库中删除所有已过期的用户会话
重启 Gunicorn 和 NetBox 服务。
$ sudo systemctl restart netbox netbox-rq
结语
至此,我们关于在 Ubuntu 22.04 服务器上安装 NetBox 网络文档与管理工具,并将 Nginx 用作反向代理服务器的教程就结束了。如果你有任何问题,请在下方评论中发布。