
本页内容
- 准备工作
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装 Docker 和 Docker Compose
- 第 3 步 - 为 Drupal 创建 Docker Compose 文件(MySQL、Drupal、Nginx、Certbot 服务)
- 第 4 步 - 创建 Nginx 配置
- 第 5 步 - 生成 SSL 证书
- 第 6 步 - 为 SSL 配置 Nginx
- 第 7 步 - 启动 Drupal 网页安装向导
- 第 8 步 - 配置 Drupal
- 第 9 步 - 备份 Drupal
- 第 10 步 - 升级 Drupal
- 总结
- MySQL Docker 服务
- Drupal 服务
- Nginx 服务
- Certbot 服务
Drupal 是一个用 PHP 编写的开源内容管理系统(CMS)。全球许多组织都用它来搭建博客、政府网站、企业站点等。它提供了日益丰富的功能与模块来扩展自身能力,让你能够创建任何想要的网站。
本教程将教你如何在 Ubuntu 22.04 服务器上通过 Docker 安装 Drupal。Drupal 兼容 PHP 8.2 与 MySQL,自第 9 版起也支持 PostgreSQL,但存在一些缺陷,因此我们本教程将坚持使用 MySQL。我们将借助 Docker Compose 将 Drupal 与 Nginx 及 Certbot 集成,以安全的 HTTPS 协议对外提供 Drupal 网站服务。
准备工作
- 一台运行 Ubuntu 22.04 的服务器;小型社区至少需要 1GB 内存,托管较大的社区则建议使用至少 2GB 或更大内存的服务器。
- 一个具有 sudo 权限的非 root 用户。
- 一个指向你服务器的完全限定域名(FQDN)。本教程中我们将使用 example.com 作为域名。
- 确保系统已更新。$ sudo apt update
- 安装基础工具包。其中部分可能已安装。$ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y
一台运行 Ubuntu 22.04 的服务器;小型社区至少需要 1GB 内存,托管较大的社区则建议使用至少 2GB 或更大内存的服务器。
一个具有 sudo 权限的非 root 用户。
一个指向你服务器的完全限定域名(FQDN)。本教程中我们将使用 example.com 作为域名。
确保系统已更新。
$ sudo apt update
安装基础工具包。其中部分可能已安装。
$ sudo apt install wget curl nano software-properties-common dirmngr apt-transport-https gnupg gnupg2 ca-certificates lsb-release ubuntu-keyring unzip -y
第 1 步 - 配置防火墙
第一步是配置防火墙。Ubuntu 默认自带 ufw(Uncomplicated Firewall,简易防火墙)。
检查防火墙是否正在运行。
$ sudo ufw status
你应该会看到如下输出。
Status: inactive
放行 SSH 端口,以免启用防火墙时中断当前连接。
$ sudo ufw allow OpenSSH
同时放行 HTTP 与 HTTPS 端口。
$ sudo ufw allow http
$ sudo ufw allow https
启用防火墙
$ sudo ufw enable
Command may disrupt existing ssh connections. Proceed with operation (y|n)? y
Firewall is active and enabled on system startup
再次检查防火墙状态。
$ sudo ufw status
你应该会看到类似的输出。
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
80/tcp                     ALLOW       Anywhere
443                        ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
80/tcp (v6)                ALLOW       Anywhere (v6)
443 (v6)                   ALLOW       Anywhere (v6)
第 2 步 - 安装 Docker 和 Docker Compose
Ubuntu 22.04 自带较旧版本的 Docker。要安装最新版本,首先导入 Docker 的 GPG 密钥。
$ curl -fsSL https://download.docker.com/linux/ubuntu/gpg | sudo gpg --dearmor -o /etc/apt/keyrings/docker.gpg
创建 Docker 仓库文件。
$ echo \
  "deb [arch=$(dpkg --print-architecture) signed-by=/etc/apt/keyrings/docker.gpg] https://download.docker.com/linux/ubuntu \
  $(lsb_release -cs) stable" | sudo tee /etc/apt/sources.list.d/docker.list > /dev/null
更新系统软件源列表。
$ sudo apt update
安装最新版本的 Docker。
$ sudo apt install docker-ce docker-ce-cli containerd.io docker-compose-plugin
验证其是否正在运行。
$ sudo systemctl status docker
? docker.service - Docker Application Container Engine
     Loaded: loaded (/lib/systemd/system/docker.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2023-01-14 10:41:35 UTC; 2min 1s ago
TriggeredBy: ? docker.socket
       Docs: https://docs.docker.com
   Main PID: 2054 (dockerd)
      Tasks: 52
     Memory: 22.5M
        CPU: 248ms
     CGroup: /system.slice/docker.service
             ??  2054 /usr/bin/dockerd -H fd:// --containerd=/run/containerd/containerd.sock
默认情况下,Docker 需要 root 权限。若想避免每次运行 docker 命令都使用 sudo,可将你的用户名加入 docker 组。
$ sudo usermod -aG docker $(whoami)
你需要注销服务器再以同一用户重新登录才能使改动生效,或者执行以下命令。
$ su - ${USER}
确认你的用户已加入 Docker 组。
$ groups
navjot wheel docker
第 3 步 - 为 Drupal 创建 Docker Compose 文件
创建 Drupal 目录。
$ mkdir ~/drupal
切换到该目录。
$ cd ~/drupal
创建并打开 docker-compose.yml 文件进行编辑。
$ nano docker-compose.yml
将以下代码粘贴进去。
services:
  mysql:
    image: mysql:8.0
    container_name: mysql
    restart: unless-stopped
    env_file: .env
    volumes:
      - db-data:/var/lib/mysql
    networks:
      - internal

  drupal:
    image: drupal:10-fpm-alpine
    container_name: drupal
    depends_on:
      - mysql
    restart: unless-stopped
    networks:
      - internal
      - external
    volumes:
      - drupal-data:/var/www/html

  webserver:
    image: nginx:1.22.1-alpine
    container_name: webserver
    depends_on:
      - drupal
    restart: unless-stopped
    ports:
      - 80:80
    volumes:
      - drupal-data:/var/www/html
      - ./nginx-conf:/etc/nginx/conf.d
      - certbot-etc:/etc/letsencrypt
    networks:
      - external

  certbot:
    depends_on:
      - webserver
    image: certbot/certbot
    container_name: certbot
    volumes:
      - certbot-etc:/etc/letsencrypt
      - drupal-data:/var/www/html
    command: certonly --webroot --webroot-path=/var/www/html --email sammy@your_domain --agree-tos --no-eff-email --staging -d example.com -d www.example.com

networks:
  external:
    driver: bridge
  internal:
    driver: bridge

volumes:
  drupal-data:
  db-data:
  certbot-etc:
按 Ctrl + X 保存文件,并在提示时输入 Y。
下面我们逐一讲解上述文件中定义的各个服务。
MySQL Docker 服务
这里我们从 Docker Hub 拉取最新的 mysql:8.0 镜像。我们使用 8.x 版本而非 latest 标签,这样可以确保使用经过测试、与 Drupal 兼容的稳定版 MySQL。我们为容器设置了名称,便于用 Docker 命令停止、启动以及查看日志。除非手动停止,该容器会持续运行。我们定义了一个 .env 文件,稍后将填入 MySQL 凭据。我们还把名为 db-data 的卷挂载到容器内的 /var/lib/mysql 目录。MySQL 服务将使用内部网络与 drupal 通信。
Drupal 服务
我们使用 Drupal 10 Alpine 镜像。Alpine 版 Docker 镜像体积更小,且该镜像内置 PHP-FPM 来处理 PHP。它将与 Nginx 协同提供网站服务。depends_on 选项让 Drupal 连接 MySQL 服务,并确保 Drupal 容器始终在 MySQL 容器之后启动。Drupal 使用内部网络与 MySQL 通信,并使用外部网络向其他容器暴露自身。我们还为 Drupal 创建了一个命名卷,指向容器内的 /var/www/html 目录。
Nginx 服务
我们为 Nginx 使用 Alpine 镜像,它将主机的 80 端口暴露出来。我们使用两个命名卷:一个用于 Drupal 的公开目录,另一个用于存储 Let's Encrypt 的 SSL 证书。第三个卷以绑定挂载方式指向主机上的 Nginx 配置目录(稍后定义)。Nginx 还连接到外部 Docker 网络以使 Drupal 站点正常工作。
Certbot 服务
最后,我们拉取 Certbot 镜像来安装 SSL 证书。它与 Nginx 服务共享卷,用于存储证书和 webroot 定义。我们还在容器内加入了一条创建时运行的命令,该命令使用 --staging 标志首次获取测试证书。证书验证需要 Nginx,但缺少证书时 Nginx 无法启动,因此我们先用 --staging 创建临时证书来启动 Nginx,随后再生成正式证书。
第 4 步 - 创建 Nginx 配置
创建 Nginx 配置目录。
$ mkdir nginx-conf
创建并打开 Nginx 配置文件。
$ nano nginx-conf/drupal.conf
将以下代码粘贴进去。
server {
    listen 80;
    listen [::]:80;

    server_name drupal.example.com;

    index index.php index.html index.htm;

    root /var/www/html;

    location ~ /.well-known/acme-challenge {
        allow all;
        root /var/www/html;
    }

    location / {
        try_files $uri $uri/ /index.php$is_args$args;
    }

    rewrite ^/core/authorize.php/core/authorize.php(.*)$ /core/authorize.php$1;

    location ~ \.php$ {
        try_files $uri =404;
        fastcgi_split_path_info ^(.+\.php)(/.+)$;
        fastcgi_pass drupal:9000;
        fastcgi_index index.php;
        include fastcgi_params;
        fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
        fastcgi_param PATH_INFO $fastcgi_path_info;
    }

    location ~ /\.ht {
        deny all;
    }

    location = /favicon.ico {
        log_not_found off; access_log off;
    }
    location = /robots.txt {
        log_not_found off; access_log off; allow all;
    }
    location ~* \.(css|gif|ico|jpeg|jpg|js|png)$ {
        expires max;
        log_not_found off;
    }
}
按 Ctrl + X 保存文件,并在提示时输入 Y。
在该文件中,我们将添加一个 server 块,包含服务器名与文档根目录的指令,以及若干 location 块,用于引导 Certbot 客户端的证书请求、PHP 处理和静态资源请求。目前 Nginx 仅监听 80 端口,以便 Certbot 能在 /var/www/html/.well-known/acme-challenge 目录放入临时文件来验证 DNS 并申请临时证书。这样我们就能配合 webroot 插件使用 Certbot。
第 5 步 - 生成 SSL 证书
为生成 SSL 证书,我们先启动容器。正确的临时证书将出现在 Nginx 容器内的 /etc/letsencrypt/live 目录中。
$ docker compose up -d
检查各服务的状态。
$ docker compose ps
NAME                IMAGE                  COMMAND                  SERVICE             CREATED             STATUS                     PORTS
certbot             certbot/certbot        "certbot certonly --…"   certbot             6 minutes ago       Exited (1) 5 minutes ago
drupal              drupal:10-fpm-alpine   "docker-php-entrypoi…"   drupal              6 minutes ago       Up 6 minutes               9000/tcp
mysql               mysql:8.0              "docker-entrypoint.s…"   mysql               6 minutes ago       Up 6 minutes               3306/tcp, 33060/tcp
webserver           nginx:1.22.1-alpine    "/docker-entrypoint.…"   webserver           6 minutes ago       Up 6 minutes               0.0.0.0:80->80/tcp, :::80->80/tcp
Certbot 容器在生成证书后会成功退出。检查 Nginx 容器中证书所在的路径。
$ docker compose exec webserver ls -la /etc/letsencrypt/live
你将看到如下输出。
total 16
drwx------    3 root     root          4096 Jan 17 09:15 .
drwxr-xr-x    9 root     root          4096 Jan 17 09:15 ..
-rw-r--r--    1 root     root           740 Jan 17 09:15 README
drwxr-xr-x    2 root     root          4096 Jan 17 09:15 drupal.example.com
这证明一切成功。下一步是生成正式证书。
打开 docker-compose.yml 文件进行编辑。
$ nano docker-compose.yml
将 Certbot 服务段中的 --staging 标志替换为 --force-renewal 标志。这会让 Certbot 为你的域名申请新证书。之所以使用续订标志,是因为此后将用它来续期证书。
  certbot:
    depends_on:
      - webserver
    image: certbot/certbot
    container_name: certbot
    volumes:
      - certbot-etc:/etc/letsencrypt
      - drupal-data:/var/www/html
    command: certonly --webroot --webroot-path=/var/www/html --email
[email protected]
 --agree-tos --no-eff-email --staple-ocsp --force-renewal -d drupal.example.com
按 Ctrl + X 保存文件,并在提示时输入 Y。
再次运行 docker compose up 命令以重建 Certbot 容器。--no-deps 标志告知 Certbot 跳过启动 webserver 容器,因为它已在运行。
$ docker compose up --force-recreate --no-deps certbot
你将看到如下输出。
[+] Running 1/0
 ? Container certbot  Recreated                                                                                                                                                                             0.1s
Attaching to certbot
certbot  | Saving debug log to /var/log/letsencrypt/letsencrypt.log
certbot  | Account registered.
certbot  | Renewing an existing certificate for drupal.example.com
certbot  |
certbot  | Successfully received certificate.
certbot  | Certificate is saved at: /etc/letsencrypt/live/drupal.example.com/fullchain.pem
certbot  | Key is saved at:         /etc/letsencrypt/live/drupal.example.com/privkey.pem
certbot  | This certificate expires on 2023-04-17.
certbot  | These files will be updated when the certificate renews.
certbot  | NEXT STEPS:
certbot  | - The certificate will need to be renewed before it expires. Certbot can automatically renew the certificate in the background, but you may need to take steps to enable that functionality. See https://certbot.org/renewal-setup for instructions.
certbot  |
certbot  | - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
certbot  | If you like Certbot, please consider supporting our work by:
certbot  |  * Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
certbot  |  * Donating to EFF:                    https://eff.org/donate-le
certbot  | - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
certbot exited with code 0
第 6 步 - 为 SSL 配置 Nginx
证书已生效后,我们需要配置 Nginx 来提供证书并将 HTTP 请求重定向到 HTTPS。
停止 Nginx 服务。
$ docker stop webserver
新建一个用于 SSL 配置的 Nginx 文件并打开编辑。
$ nano nginx-conf/drupal-ssl.conf
将以下代码粘贴进去。
server {
    listen 80;
    listen [::]:80;

    server_name drupal.example.com;

    location ~ /.well-known/acme-challenge {
        allow all;
        root /var/www/html;
    }

    location / {
        rewrite ^ https://$host$request_uri? permanent;
    }
}
server {
    listen 443 ssl http2;
    listen [::]:443 ssl http2;
    server_name drupal.example.com;

    index index.php index.html index.htm;

    root /var/www/html;

    server_tokens off;

    ssl_certificate /etc/letsencrypt/live/drupal.example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/drupal.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/drupal.example.com/chain.pem;
    ssl_session_timeout 1d;
    ssl_session_cache shared:SSL:10m;
    ssl_session_tickets off;
    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
    ssl_prefer_server_ciphers off;
    ssl_ecdh_curve secp384r1;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;

    # OCSP stapling
    ssl_stapling on;
    ssl_stapling_verify on;
    resolver 8.8.8.8 8.8.4.4 valid=300s;
    resolver_timeout 5s;

    add_header X-Frame-Options "SAMEORIGIN" always;
    add_header X-XSS-Protection "1; mode=block" always;
    add_header X-Content-Type-Options "nosniff" always;
    add_header Referrer-Policy "no-referrer-when-downgrade" always;
    add_header Content-Security-Policy "default-src * data: 'unsafe-eval' 'unsafe-inline'" always;

    location / {
        try_files $uri $uri/ /index.php$is_args$args;
    }

    rewrite ^/core/authorize.php/core/authorize.php(.*)$ /core/authorize.php$1;

    location ~ \.php$ {
        try_files $uri =404;
        fastcgi_split_path_info ^(.+\.php)(/.+)$;
        fastcgi_pass drupal:9000;
        fastcgi_index index.php;
        include fastcgi_params;
        fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
        fastcgi_param PATH_INFO $fastcgi_path_info;
    }

    location ~ /\.ht {
        deny all;
    }

    location = /favicon.ico {
        log_not_found off; access_log off;
    }
    location = /robots.txt {
        log_not_found off; access_log off; allow all;
    }
    location ~* \.(css|gif|ico|jpeg|jpg|js|png)$ {
        expires max;
        log_not_found off;
    }
}
按 Ctrl + X 保存文件,并在提示时输入 Y。
HTTP 块指定了 Certbot 的 webroot 插件路径,并将任何 HTTP 请求重定向到 HTTPS。
下一步是确保 Nginx 容器监听 443 端口。打开 docker-compose.yml 文件进行编辑。
$ nano docker-compose.yml
在文件的 Nginx 段中,按如下方式修改以暴露 443 端口并启用 SSL。
  webserver:
    image: nginx:1.22.1-alpine
    container_name: webserver
    depends_on:
      - drupal
    restart: unless-stopped
    ports:
      - 80:80
      - 443:443
    volumes:
      - drupal-data:/var/www/html
      - ./nginx-conf:/etc/nginx/conf.d
      - certbot-etc:/etc/letsencrypt
      - /etc/ssl/certs/dhparam.pem:/etc/ssl/certs/dhparam.pem
    networks:
      - external
按 Ctrl + X 保存文件,并在提示时输入 Y。
既然已为 Nginx 启用并添加 SSL 配置,你可以删除旧的 HTTP 配置文件。
$ rm nginx-conf/drupal.conf
重启 Nginx 之前,我们需要生成前面已在配置中引用的 Diffie-Hellman 组证书。
$ sudo openssl dhparam -dsaparam -out /etc/ssl/certs/dhparam.pem 4096
重建 Nginx 容器。
$ docker compose up -d --force-recreate --no-deps webserver
检查容器状态。
$ docker compose ps
NAME                IMAGE                  COMMAND                  SERVICE             CREATED             STATUS                   PORTS
certbot             certbot/certbot        "certbot certonly --…"   certbot             3 hours ago         Exited (0) 3 hours ago
drupal              drupal:10-fpm-alpine   "docker-php-entrypoi…"   drupal              3 hours ago         Up 3 hours               9000/tcp
mysql               mysql:8.0              "docker-entrypoint.s…"   mysql               3 hours ago         Up 3 hours               3306/tcp, 33060/tcp
webserver           nginx:1.22.1-alpine    "/docker-entrypoint.…"   webserver           15 seconds ago      Up 13 seconds            0.0.0.0:80->80/tcp, :::80->80/tcp, 0.0.0.0:443->443/tcp, :::443->443/tcp
第 7 步 - 启动 Drupal 网页安装向导
现在可以启动 Drupal 网页安装向导了。在浏览器中打开网址 https://drupal.example.com,你将看到如下界面。
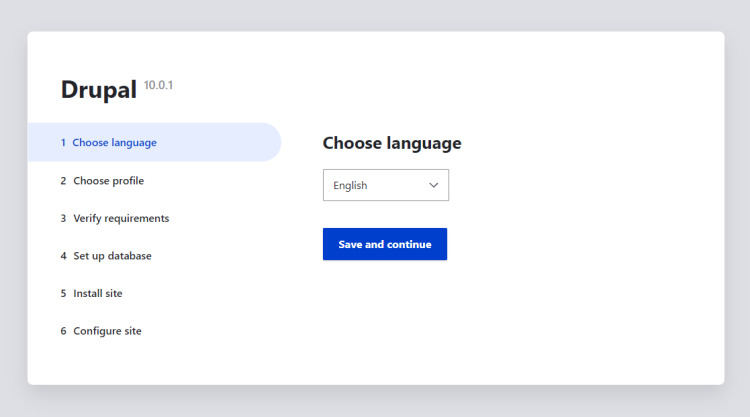
点击“Save and continue”(保存并继续)按钮,进入安装配置档页面。
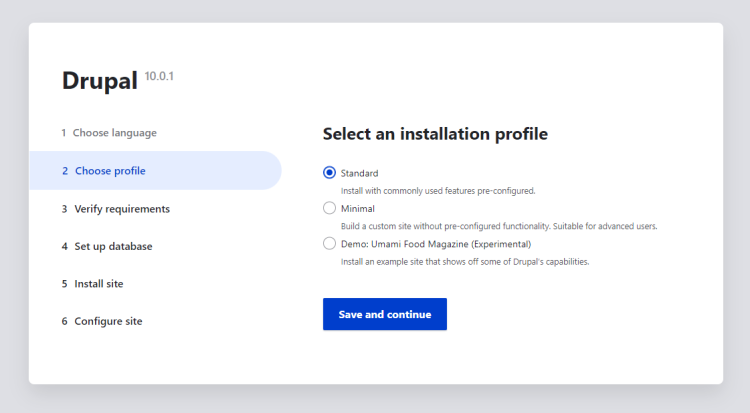
我们选择 Standard(标准)配置档。点击“Save and continue”按钮,进入数据库配置页面。
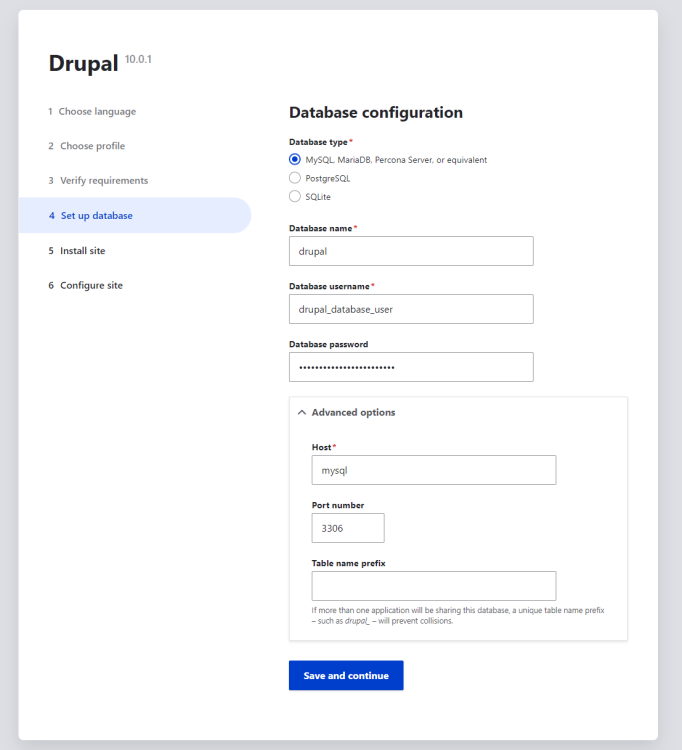
填入我们在环境文件中使用的数据库凭据,展开 Advanced options(高级选项)部分,并将 mysql 作为数据库主机。这与 Docker compose 文件中 Drupal 需要连接的 MySQL 服务名称一致。
点击“Save and continue”按钮继续。Drupal 将开始安装默认模块与主题。
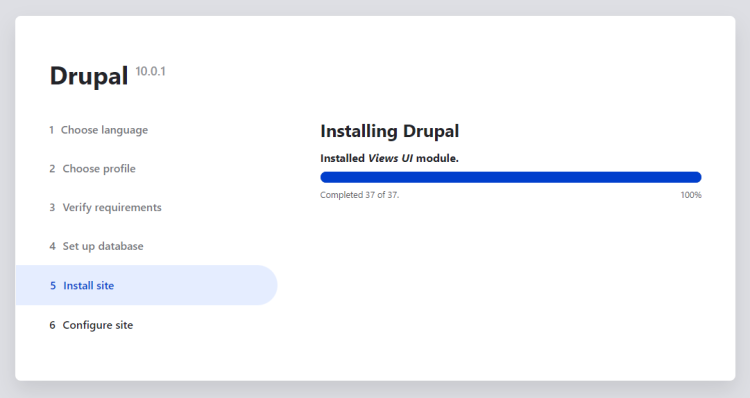
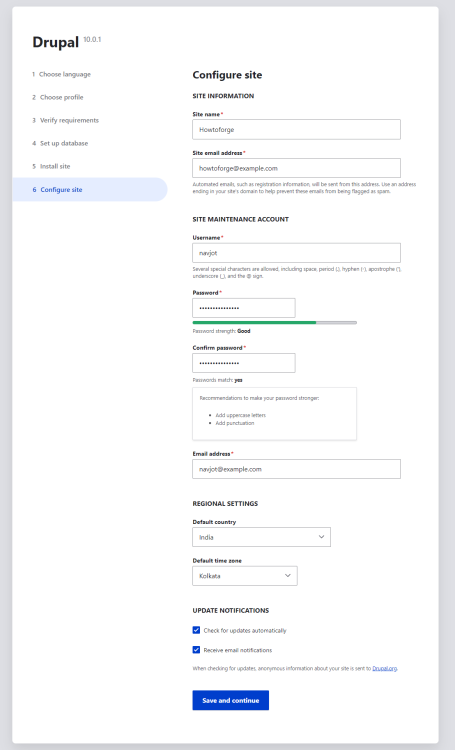
接下来会进入 Drupal 配置页面。填写站点名称、邮箱、用户名、密码以及区域设置,完成后点击“Save and continue”按钮。
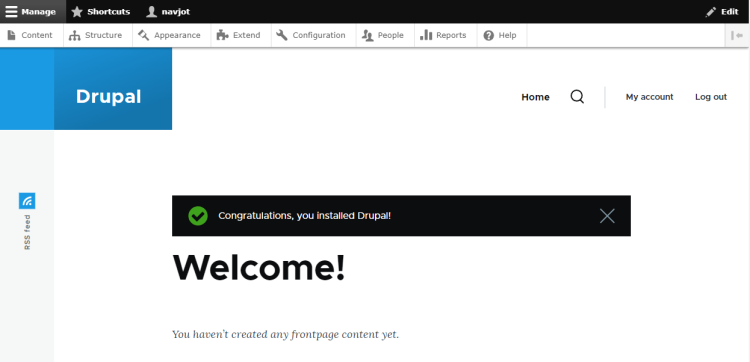
最后你将进入 Drupal 仪表盘,可以开始使用 Drupal 搭建你的网站了。
第 8 步 - 配置 Drupal
这一步是可选的,但有助于提升 Drupal 性能。首先要设置 MySQL 的事务隔离级别。MySQL、MariaDB 及同类数据库的默认事务隔离级别为 “REPEATABLE READ”。在 Drupal 下该设置可能引发表死锁,导致站点变得极慢或完全无响应。Drupal 站点推荐的事务隔离级别为 ‘READ COMMITTED’。
登录到 MySQL 容器的 shell。
$ docker exec -it mysql bash
使用 root 用户打开 MySQL shell。
bash-4.4# mysql -u root -p
Enter password:
运行以下命令全局修改事务隔离级别。
mysql> SET GLOBAL TRANSACTION ISOLATION LEVEL READ COMMITTED;
连续输入两次 exit 退出 MySQL shell 与容器。
下一步是将你的域名设为受信任主机,以防范 HTTP HOST 头攻击。为此,需要编辑 Drupal 容器内的 /var/www/html/sites/default/settings.php 文件。由于 Drupal 文件使用了命名卷,推荐的修改方式是先把文件从容器复制到主机,编辑后再复制回容器。对于 Drupal 安装中任何需要修改的文件,都可以采用这种方式。
将配置文件从容器复制到主机。
$ docker cp drupal:/var/www/html/sites/default/settings.php settings.php
该文件处于只读模式,为其添加写入权限。
$ chmod+w settings.php
打开文件进行编辑。
$ nano settings.php
在文件中找到如下段落。
#$settings['trusted_host_patterns'] = [
#  '^www\.example\.com$',
#];
去掉井号注释符,并按如下方式添加你的 Drupal 域名。
$settings['trusted_host_patterns'] = [
  '^drupal\.example\.com$',
];
按 Ctrl + X 保存文件,并在提示时输入 Y。
再次移除写入权限。
$ chmod -w settings.php
将文件复制回容器内。
$ docker cp settings.php drupal:/var/www/html/sites/default
第 9 步 - 备份 Drupal
我们将使用命令行备份 Drupal 数据库。切换到 Drupal 目录。
$ cd ~/drupal
创建备份目录。
$ mkdir backup-data
使用以下命令备份 Drupal 数据库,系统会要求输入 MySQL root 密码。
$ docker compose exec mysql sh -c "exec mysqldump drupal -uroot -p" | tee backup-data/data_`date +%d-%m-%Y"_"%H_%M_%S`.sql >/dev/null
Enter password: root_password
上述命令会在 ~/drupal/backup-data 目录中生成 SQL 备份。
查看目录内容。
$ ls -al backup-data
total 6716
drwxrwxr-x 2 navjot navjot    4096 Jan 19 13:59 .
drwxrwxr-x 4 navjot navjot    4096 Jan 19 13:35 ..
-rw-rw-r-- 1 navjot navjot 6868325 Jan 19 13:37 data_19-01-2023_13_36_58.sql
你可以看到数据库已备份到该目录。可以使用 phpMyAdmin 工具或以下命令恢复该数据库。
$ docker compose exec mysql sh -c "exec mysql -uroot -p" < backup-data/data_19-01-2023_13_36_58.sql
你可以创建定时任务(cron job)来定期备份数据库。
在 /etc/cron.daily 目录中创建备份脚本并打开编辑。
$ sudo nano /etc/cron.daily/drupalbackup.sh
将以下代码粘贴进去。
#!/bin/bash
cd /home/navjot/drupal/
/usr/bin/docker compose exec mysql sh -c "exec mysqldump drupal -uroot -p" | tee backup-data/data_`date +%d-%m-%Y"_"%H_%M_%S`.sql >/dev/null
按 Ctrl + X 保存文件,并在提示时输入 Y。
赋予脚本可执行权限。
$ sudo chmod +x /etc/cron.daily/drupalbackup.sh
现在你的数据库将每天自动备份。
第 10 步 - 升级 Drupal
升级 Drupal 的第一步是使用示例 9 中的命令备份 Drupal 数据库。
然后切换到该目录。
$ cd ~/drupal
停止容器。
$ docker compose down
拉取最新的容器镜像。
$ docker compose pull drupal:10-fpm-alpine
若要升级到下一个主版本,你需要相应调整镜像名称,并查阅 Drupal 的发行说明以确认是否存在兼容问题。
如有需要,可在 docker-compose.yml 中做相应修改。其余镜像可通过更改其在 Docker compose 文件中的定义来更新。
重启 Drupal 容器,这也会拉取其他软件包次版本的最新镜像。
$ docker compose up -d
总结
至此,本教程在 Ubuntu 22.04 服务器上通过 Docker 安装 Drupal 的内容就结束了。如果你有任何疑问,请在下方评论区留言。