
本页内容
- 前提条件
- 第 1 步 - 配置防火墙
- 第 2 步 - 安装 Docker
- 第 3 步 - 安装 Docker Compose
- 第 4 步 - 创建 Koel App Key
- 第 5 步 - 创建 Koel Environment File
- 第 6 步 - 创建 Koel Docker Compose File
- 第 7 步 - 启动 Koel Container 首次初始化 Koel 更改管理员密码
- 第 8 步 - 安装 SSL
- 第 9 步 - 安装 Nginx
- 第 10 步 - 访问 Koel
- 第 11 步 - 导入音乐
- 第 12 步 - 更新 Koel
- 结论
- 首次初始化 Koel
- 更改管理员密码
Koel 是一个基于 Web 的音频流媒体服务,使用 Laravel PHP 框架编写。它允许你流式播放个人音乐收藏,并从世界任何地方访问。它支持多种媒体格式,包括 AAC、OGG、WMA、FLAC 和 APE。
在本教程中,你将学习如何使用 Docker 在 Rocky Linux 8 机器上安装 Koel Music Streaming Server。
前提条件
- 一台运行 Rocky Linux 8.5 的服务器。
- 一个具有 sudo 权限的非 root 用户。
- 更新所有内容。$ sudo dnf update
- 安装必要的软件包。$ sudo dnf install yum-utils nano curl
- 一个指向服务器的自定义域名,如 koel.example.com 。
一台运行 Rocky Linux 8.5 的服务器。
一个具有 sudo 权限的非 root 用户。
更新所有内容。
$ sudo dnf update
安装必要的软件包。
$ sudo dnf install yum-utils nano curl
一个指向服务器的自定义域名,如 koel.example.com 。
第 1 步 - 配置防火墙
第一步是配置防火墙。Rocky Linux 使用 Firewalld Firewall。检查防火墙的状态。
$ sudo firewall-cmd --state
running
防火墙使用不同的区域,public 区域是我们将使用的默认区域。列出防火墙上所有启用的服务和端口。
$ sudo firewall-cmd --permanent --list-services
它应显示以下输出。
cockpit dhcpv6-client ssh
允许 HTTP 和 HTTPS 端口。
$ sudo firewall-cmd --permanent --add-service=http
$ sudo firewall-cmd --permanent --add-service=https
重新检查防火墙的状态。
$ sudo firewall-cmd --permanent --list-services
你应该会看到类似的输出。
cockpit dhcpv6-client http https ssh
重新加载防火墙以使更改生效。
$ sudo firewall-cmd --reload
第 2 步 - 安装 Docker
Rocky Linux 自带较旧版本的 Docker。要安装最新版本,首先要安装官方 Docker repository。
$ sudo yum-config-manager \
    --add-repo \
    https://download.docker.com/linux/centos/docker-ce.repo
安装最新版本的 Docker。
$ sudo dnf install docker-ce docker-ce-cli containerd.io
启用并运行 Docker daemon。
$ sudo systemctl enable docker --now
验证它正在运行。
? docker.service - Docker Application Container Engine
   Loaded: loaded (/usr/lib/systemd/system/docker.service; enabled; vendor preset: disabled)
   Active: active (running) since Sat 2022-04-02 13:26:08 UTC; 2s ago
     Docs: https://docs.docker.com
 Main PID: 21152 (dockerd)
    Tasks: 7
   Memory: 30.9M
   CGroup: /system.slice/docker.service
           ??21152 /usr/bin/dockerd -H fd:// --containerd=/run/containerd/containerd.sock
...
默认情况下,Docker 需要 root 权限。如果你想避免每次运行 docker 命令时都使用 sudo,请将你的用户名添加到 docker group。
$ sudo usermod -aG docker $(whoami)
你需要退出服务器并以同一用户重新登录,以使此更改生效。
第 3 步 - 安装 Docker Compose
下载 Docker Compose 的最新稳定版本。
$ sudo curl -L "https://github.com/docker/compose/releases/download/1.29.2/docker-compose-$(uname -s)-$(uname -m)" -o /usr/local/bin/docker-compose
为 Docker Compose 二进制文件赋予可执行权限。
$ sudo chmod +x /usr/local/bin/docker-compose
测试安装。
$ docker-compose --version
docker-compose version 1.29.2, build 5becea4c
安装 Docker-compose Bash Completion 脚本。
$ sudo curl \
    -L https://raw.githubusercontent.com/docker/compose/1.29.2/contrib/completion/bash/docker-compose \
    -o /etc/bash_completion.d/docker-compose
重新加载你的 profile 设置以使 bash-completion 生效。
$ source ~/.bashrc
第 4 步 - 创建 Koel App Key
我们将通过短暂运行容器来生成 Koel 的 App key。运行以下命令来启动容器并访问其 shell。
$ docker run -it --rm phanan/koel bash
进入容器后,运行以下命令生成 application key。
$ php artisan key:generate --force
输出带有新生成 app key 的修改后的 environment file。
$ cat .env
APP_KEY=base64:fjtO7aVHHKWfk4DThKqf1nci6o2DuMkNd90TKX6Gj+4=
复制 key 值并退出容器 shell。
$ exit
第 5 步 - 创建 Koel Environment File
为 Koel 创建一个目录。
$ mkdir ~/koel
切换到该目录。
$ cd ~/koel
创建 music 目录。
$ mkdir music
创建并打开 .env 文件。
$ nano .env
在其中粘贴以下代码。
APP_NAME=Koel

# A random 32-char string. You can leave this empty if use php artisan koel:init.
APP_KEY=base64:fjtO7aVHHKWfk4DThKqf1nci6o2DuMkNd90TKX6Gj+4=

# The ABSOLUTE path to your media. This value can always be changed later via the web interface.
MEDIA_PATH=/music

APP_ENV=production
APP_DEBUG=true
APP_URL=https://koel.example.com

# The maximum scan time, in seconds. Increase this if you have a huge library.
# Note: This setting doesn't have effect when scanning via koel:sync.
APP_MAX_SCAN_TIME=600

# The memory limit, in MB, used by the scanning process.
# For example, if you want to set a memory limit of 2048MB, enter "2048" (without
# quotes) here.
MEMORY_LIMIT=512

# The streaming method.
# Can be either 'php' (default), 'x-sendfile', or 'x-accel-redirect'
# See https://docs.koel.dev/#streaming-music for more information.
# Note: This setting doesn't have effect if the media needs transcoding (e.g. FLAC).
STREAMING_METHOD=x-sendfile

# If you want Koel to integrate with Last.fm, set the API details here.
# See https://docs.koel.dev/3rd-party.html#last-fm for more information
LASTFM_API_KEY=
LASTFM_API_SECRET=

# If you want to use Amazon S3 with Koel, fill the info here and follow the
# installation guide at https://docs.koel.dev/aws-s3.html
AWS_ACCESS_KEY_ID=
AWS_SECRET_ACCESS_KEY=
AWS_REGION=

# If you want Koel to integrate with YouTube, set the API key here.
# See https://docs.koel.dev/3rd-party.html#youtube for more information.
YOUTUBE_API_KEY=

# You can also configure Koel to use a CDN to serve the media files.
# This url must be mapped to the home URL of your Koel's installation.
# No trailing slash, please.
CDN_URL=

# The bit rate of the output mp3 stream. Higher value results in better quality,
# but slower streaming and more bandwidth.
OUTPUT_BIT_RATE=128

# Whether to allow song downloading.
# Note that if you're downloading more than one song, Koel will zip them up
# using PHP's ZipArchive. So if the module isn't available in the current
# environment, such a download will (silently) fail.
ALLOW_DOWNLOAD=true

# If this is set to true, the query to get artist, album, and song information will be cached.
# This can give a boost to Koel's boot time, especially if your library is huge.
# However, the cache deserialization process can be memory sensitive, so if you encounter
# errors, try setting this to false.
CACHE_MEDIA=true

# Koel attempts to detect if your website use HTTPS and generates secure URLs accordingly.
# If this attempts for any reason, you can force it by setting this value to true.
FORCE_HTTPS=true

# The variables below are Laravel-specific.
# You can change them if you know what you're doing. Otherwise, just leave them as-is.
APP_LOG_LEVEL=debug
BROADCAST_DRIVER=log
CACHE_DRIVER=file
SESSION_DRIVER=file
QUEUE_DRIVER=sync
按 Ctrl + X 并在提示时输入 Y 来保存文件。
上面的大多数设置都一目了然。需要配置以下设置才能使其正常工作。将上一步生成的 app key 填入 APP_KEY 变量。在 APP_URL 下输入你的域名,并根据服务器的资源以 MB 为单位设置 memory limit。我们已将 streaming method 设置为 x-sendfile,因为 Koel 的 docker image 使用 Apache 并预先配置了它。FORCE_HTTPS 设置被设为 true,因为我们将使用 Nginx 作为 load balancer,并结合 Let's Encrypt SSL 将 Koel 提供给 Web。如果你想与 Koel 一起使用其他服务,请配置它们。
第 6 步 - 创建 Koel Docker Compose File
创建并打开文件 docker-compose.yml 进行编辑。
$ nano docker-compose.yml
在其中粘贴以下代码。
version: '3.3'

services:
  koel:
    image: phanan/koel
    container_name: koel
    depends_on:
      - koeldb
    restart: unless-stopped
    ports:
      - 8080:80
    environment:
      - DB_CONNECTION=mysql
      - DB_HOST=koeldb
      - DB_USERNAME=koel
      - DB_PASSWORD=koelpassword
      - DB_DATABASE=koel
    volumes:
      - ./music:/music
      - ./.env:/var/www/html/.env
      - covers:/var/www/html/public/img/covers
      - search_index:/var/www/html/storage/search-indexes

  koeldb:
    image: mysql/mysql-server:8.0
    restart: unless-stopped
    volumes:
      - db:/var/lib/mysql
    environment:
      - MYSQL_ROOT_PASSWORD=rootpassword
      - MYSQL_DATABASE=koel
      - MYSQL_USER=koel
      - MYSQL_PASSWORD=koelpassword

volumes:
  db:
    driver: local
  covers:
    driver: local
  search_index:
    driver: local
按 Ctrl + X 并在提示时输入 Y 来保存文件。
上面的文件基于 Koel 和 MySQL 的 docker images 启动 containers。它将 Koel 暴露到你机器上的 8080 端口。music 和 environment file 被挂载到 container 上各自对应的位置。music covers 和 search index 的目录,连同 MySQL data,都作为 local volumes 挂载。为变量 MYSQL_ROOT_PASSWORD 、 MYSQL_PASSWORD 选择一个强密码,并使这些值与上面文件中 Koel container 的变量匹配。要将 Koel container 与 database container 链接,请确保 DB_HOST 和 depends_on 变量以 Database container 的 service name 命名。
第 7 步 - 启动 Koel Container
使用以下命令启动 Koel Container。
$ docker-compose up -d
首次初始化 Koel
登录到 Koel Container shell。下面命令中的 koel 指的是通过上面 Docker compose 文件中的 container_name 变量设置的容器名称。如果你没有设置容器名称,则必须先找到该容器的名称,并在以下命令中使用它。
$ docker exec --user www-data -it koel bash
运行以下命令创建 administrator account 并初始化 database。
$ php artisan koel:init --no-assets
更改管理员密码
Koel 会创建一个具有以下 credentials 的默认 administrator account。
email:
[email protected]

password: KoelIsCool
你可以在 container shell 内使用以下命令更改 administrator account 的密码。
$ php artisan koel:admin:change-password
退出容器 shell。
$ exit
第 8 步 - 安装 SSL
要使用 Let's Encrypt 安装 SSL certificate,我们需要安装 Certbot 工具。
首先,你需要下载并安装 EPEL repository。
$ sudo dnf install epel-release
运行以下命令安装 Certbot。
$ sudo dnf install certbot
生成 SSL certificate。
$ sudo certbot certonly --standalone --agree-tos --no-eff-email --staple-ocsp --preferred-challenges http -m
[email protected]
 -d koel.example.com
上面的命令会将一个 certificate 下载到服务器上的 /etc/letsencrypt/live/koel.example.com 目录。
生成 Diffie-Hellman group certificate。
$ sudo openssl dhparam -out /etc/ssl/certs/dhparam.pem 4096
为 Let's Encrypt 自动续期创建一个 challenge web root 目录。
$ sudo mkdir -p /var/lib/letsencrypt
创建一个 Cron Job 来续期 SSL。它将每天运行以检查 certificate 并在需要时续期。为此,首先创建文件 /etc/cron.daily/certbot-renew 并打开进行编辑。
$ sudo nano /etc/cron.daily/certbot-renew
粘贴以下代码。
#!/bin/sh
certbot renew --cert-name koel.example.com --webroot -w /var/lib/letsencrypt/ --post-hook "systemctl reload nginx"
按 Ctrl + X 并在提示时输入 Y 来保存文件。
更改该任务文件的权限以使其可执行。
$ sudo chmod +x /etc/cron.daily/certbot-renew
第 9 步 - 安装 Nginx
我们将安装最新版本的 Nginx。创建并打开文件 /etc/yum.repos.d/nginx.repo 进行编辑。
$ sudo nano /etc/yum.repos.d/nginx.repo
在其中粘贴以下几行。
[nginx-stable]
name=nginx stable repo
baseurl=http://nginx.org/packages/centos/$releasever/$basearch/
gpgcheck=1
enabled=1
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true

[nginx-mainline]
name=nginx mainline repo
baseurl=http://nginx.org/packages/mainline/centos/$releasever/$basearch/
gpgcheck=1
enabled=0
gpgkey=https://nginx.org/keys/nginx_signing.key
module_hotfixes=true
按 Ctrl + X 并在提示时输入 Y 来保存文件。
安装 Nginx。
$ sudo dnf install nginx
验证安装。
$ nginx -v
nginx version: nginx/1.20.2
启用并启动 Nginx service。
$ sudo systemctl enable nginx --now
创建并打开文件 /etc/nginx/conf.d/koel.conf 进行编辑。
$ sudo nano /etc/nginx/conf.d/koel.conf
在其中粘贴以下代码。
# Redirect all non-encrypted to encrypted
server {
    listen 80;
    listen [::]:80;
    server_name koel.example.com;
    return 301 https://$host$request_uri;
}

server {
    listen 443 ssl http2;
    listen [::]:443 ssl http2;

    server_name koel.example.com;

    ssl_certificate     /etc/letsencrypt/live/koel.example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/koel.example.com/privkey.pem;
    ssl_trusted_certificate /etc/letsencrypt/live/koel.example.com/chain.pem;
    ssl_session_timeout 1d;
    ssl_session_cache shared:MozSSL:10m;
    ssl_session_tickets off;
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_dhparam /etc/ssl/certs/dhparam.pem;

    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;

    access_log /var/log/nginx/koel.example.com.access.log main;
    error_log  /var/log/nginx/koel.example.com.error.log;

    location / {
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header X-Forwarded-Port $server_port;
        proxy_set_header X-Forwarded-Host $host;
        client_max_body_size 400M;
    	proxy_pass  http://localhost:8080;
    	proxy_http_version 1.1;
        proxy_set_header Host $host;
    }
}
完成后,按 Ctrl + X 并在提示时输入 Y 来保存文件。上面的配置允许 Nginx 充当 proxy server 并绑定到 localhost 上的 8080 端口。
打开文件 /etc/nginx/nginx.conf 进行编辑。
$ sudo nano /etc/nginx/nginx.conf
在 include /etc/nginx/conf.d/*.conf; 这一行之前添加以下行。
server_names_hash_bucket_size 64;
按 Ctrl + X 并在提示时输入 Y 来保存文件。
验证 Nginx configuration file 的语法。
$ sudo nginx -t
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
重启 Nginx service 以启用新配置。
$ sudo systemctl restart nginx
第 10 步 - 访问 Koel
你可以在浏览器中访问 URL https://koel.example.com 来访问 Koel。你将看到以下登录界面。
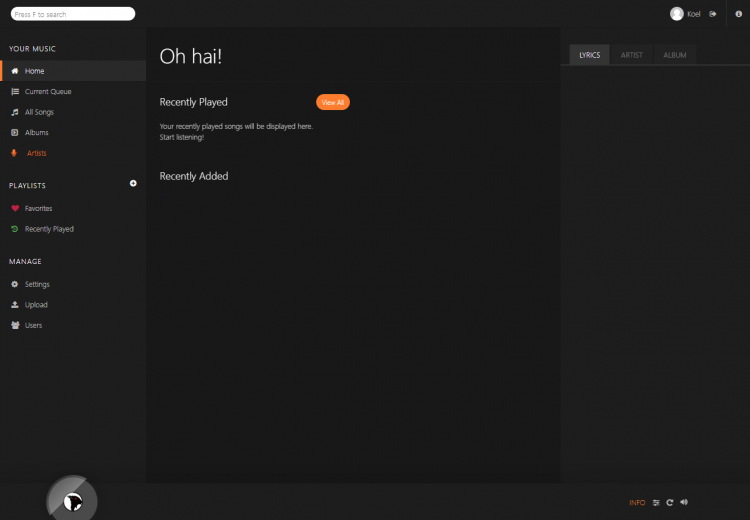
输入 [email protected] 作为你的用户名,以及你在登录前设置的密码。成功登录后将出现以下 dashboard。
第 11 步 - 导入音乐
将要导入的 music files 复制到系统的 ~/koel/music 文件夹。你可以使用 scp 命令将文件从本地 PC 导入到服务器。
$ scp test.mp3 user@<yourserverIP>:/home/user/koel/music
将文件复制到 ~/koel/music 文件夹后,运行以下命令将音乐导入 Koel。
$ docker exec --user www-data koel php artisan koel:sync
音乐将显示在 Koel 的 web interface 中,你可以开始播放。
Koel 的 web interface 还允许你直接上传歌曲。
第 12 步 - 更新 Koel
切换到 Koel 目录。
$ cd ~/koel
拉取最新的 Koel Docker image。
$ docker-compose pull
关闭容器。
$ docker-compose down --remove-orphans
使用更新后的 images 启动容器。
$ docker-compose up -d
验证 Docker containers。
$ docker ps
结论
关于使用 Docker 在 Rocky Linux 服务器上安装 Koel Music Streaming Service 的教程到此结束。如果你有任何问题,请在下面的评论中发表。