
本教程适用于以下操作系统版本
- Ubuntu 24.04 (Noble Numbat)
- Ubuntu 22.04 (Jammy Jellyfish)
- Ubuntu 20.04 (Focal Fossa)
本页内容
- 准备工作
- 开始之前
- 安装 Java JDK
- 安装并配置 Elasticsearch
- 安装 MongoDB 服务器
- 安装并配置 Graylog
- 将 Nginx 配置为 Graylog 的反向代理
- 访问 Graylog Web 界面
- 结语
Graylog 是一款免费的开源日志监控工具,用于捕获、存储并实现对 TB 级机器数据的实时分析。它专为现代日志分析而设计,让用户能够快速、轻松地从数据中挖掘价值并更快地采取行动。它还提供告警与日志历史检索系统,使用 ElasticSearch 作为主索引数据库,并使用 MongoDB 存储元信息。它帮助你以简单、可读的格式监控、搜索并分析大量数据。
在本教程中,我们将向你展示如何在 Ubuntu 22.04 服务器上安装 Graylog。
准备工作
- 一台运行 Ubuntu 22.04、内存至少为 4GB 的服务器
- 服务器上已配置 root 密码。
开始之前
首先,你需要将系统软件包更新到最新版本。你可以使用以下命令将它们全部更新:
apt update -y
apt upgrade
更新完所有软件包后,你还需要在服务器上安装一些依赖项。你可以使用以下命令将它们全部安装:
apt install apt-transport-https gnupg2 uuid-runtime pwgen curl dirmngr -y一旦所有必需的依赖项都已安装完毕,你就可以进入下一步。
安装 Java JDK
Graylog 要求服务器上已安装 Java。如果尚未安装,你可以使用以下命令进行安装:
apt install openjdk-11-jre-headless -yJava 安装完成后,你可以通过运行以下命令来验证已安装的 Java 版本:
java -version你应该会看到以下输出:
openjdk version "11.0.16" 2022-07-19
OpenJDK Runtime Environment (build 11.0.16+8-post-Ubuntu-0ubuntu122.04)
OpenJDK 64-Bit Server VM (build 11.0.16+8-post-Ubuntu-0ubuntu122.04, mixed mode, sharing)
完成后,你可以进入下一步。
安装并配置 Elasticsearch
Graylog 使用 Elasticsearch 来存储来自外部资源的日志。因此你需要在系统中安装 Elasticsearch。
默认情况下,Elasticsearch 软件包在 Ubuntu 默认仓库中不可用。因此你需要将 Elasticsearch 仓库添加到你的系统中。
首先,使用以下命令下载并添加 Elasticsearch 的 GPG 密钥:
wget -qO - https://artifacts.elastic.co/GPG-KEY-elasticsearch | apt-key add -接下来,使用以下命令添加 Elasticsearch 仓库:
echo "deb https://artifacts.elastic.co/packages/oss-7.x/apt stable main" | sudo tee -a /etc/apt/sources.list.d/elastic-7.x.list接下来,使用以下命令更新仓库并安装 Elasticsearch:
apt update -y
apt install elasticsearch-oss -y
安装完 Elasticsearch 后,你需要编辑 Elasticsearch 配置文件并定义集群名称。你可以使用以下命令完成:
nano /etc/elasticsearch/elasticsearch.yml将你的集群名称定义为 Graylog,并添加如下所示的另一行:
cluster.name: graylog
action.auto_create_index: false
完成后保存并关闭文件。然后,使用以下命令启动 Elasticsearch 服务并使其在开机时自动启动:
systemctl daemon-reload
systemctl start elasticsearch
systemctl enable elasticsearch
你也可以使用该以下命令验证 Elasticsearch 服务的状态:
systemctl status elasticsearch你应该会看到以下输出:
? elasticsearch.service - Elasticsearch
     Loaded: loaded (/lib/systemd/system/elasticsearch.service; disabled; vendor preset: enabled)
     Active: active (running) since Sun 2022-09-25 07:05:27 UTC; 21s ago
       Docs: https://www.elastic.co
   Main PID: 74226 (java)
      Tasks: 48 (limit: 4579)
     Memory: 1.2G
        CPU: 22.739s
     CGroup: /system.slice/elasticsearch.service
             ??74226 /usr/share/elasticsearch/jdk/bin/java -Xshare:auto -Des.networkaddress.cache.ttl=60 -Des.networkaddress.cache.negative.t>

Sep 25 07:05:11 ubuntu2204 systemd[1]: Starting Elasticsearch...
Sep 25 07:05:27 ubuntu2204 systemd[1]: Started Elasticsearch.
现在,使用以下命令验证 Elasticsearch 的响应:
curl -X GET http://localhost:9200你应该会看到以下输出:
{
  "name" : "ubuntu2204",
  "cluster_name" : "graylog",
  "cluster_uuid" : "6IWBEBx_THa2Gzqb7a1LTQ",
  "version" : {
    "number" : "7.10.2",
    "build_flavor" : "oss",
    "build_type" : "deb",
    "build_hash" : "747e1cc71def077253878a59143c1f785afa92b9",
    "build_date" : "2021-01-13T00:42:12.435326Z",
    "build_snapshot" : false,
    "lucene_version" : "8.7.0",
    "minimum_wire_compatibility_version" : "6.8.0",
    "minimum_index_compatibility_version" : "6.0.0-beta1"
  },
  "tagline" : "You Know, for Search"
}
安装 MongoDB 服务器
Graylog 使用 MongoDB 作为数据库。因此你需要将 MongoDB 数据库安装到你的服务器上。默认情况下,Ubuntu 默认仓库中不包含 MongoDB 软件包。因此你需要将 MongoDB 官方仓库添加到你的系统中:
你可以使用以下命令添加它:
wget -qO - https://www.mongodb.org/static/pgp/server-4.4.asc | apt-key add -
echo "deb [ arch=amd64,arm64 ] https://repo.mongodb.org/apt/ubuntu focal/mongodb-org/4.4 multiverse" | tee /etc/apt/sources.list.d/mongodb-org-4.4.list
仓库添加完成后,使用以下命令更新仓库缓存并安装 Graylog:
apt update -y
apt install -y mongodb-org
MongoDB 安装完成后,使用以下命令启动 MongoDB 服务并使其在系统重启时自动启动:
systemctl enable --now mongod你也可以使用该以下命令检查 MongoDB 的状态:
systemctl status mongod你应该在以下输出中看到 MongoDB 的状态:
? mongod.service - MongoDB Database Server
     Loaded: loaded (/lib/systemd/system/mongod.service; enabled; vendor preset: enabled)
     Active: active (running) since Sun 2022-09-25 07:20:35 UTC; 8s ago
       Docs: https://docs.mongodb.org/manual
   Main PID: 77018 (mongod)
     Memory: 60.0M
        CPU: 936ms
     CGroup: /system.slice/mongod.service
             ??77018 /usr/bin/mongod --config /etc/mongod.conf

Sep 25 07:20:35 ubuntu2204 systemd[1]: Started MongoDB Database Server.
完成后,你可以进入下一步。
安装并配置 Graylog
默认情况下,Graylog 软件包在 Ubuntu 默认仓库中不可用。因此你需要将 Graylog 仓库安装到你的服务器上。
你可以使用以下命令下载 Graylog 仓库软件包:
wget https://packages.graylog2.org/repo/packages/graylog-4.3-repository_latest.deb下载完成后,使用以下命令安装下载的软件包:
dpkg -i graylog-4.3-repository_latest.deb接下来,使用以下命令更新仓库并安装 Graylog 服务器:
apt update -y
apt install graylog-server -y
安装完 Graylog 服务器后,你需要生成一个密钥来保护用户密码。你可以使用以下命令生成它:
pwgen -N 1 -s 96你应该会看到以下输出:
d1fDH1NEOMgb3nxbFYY3eVpqzjOprwgPgFuGh2F0flDdZglJP2CxENV4WEeW8iqZXsjDEZgMob3oBvQYm62RXxoc33hKTPJa
接下来,你还需要为 Graylog 管理员用户生成一个安全密码。你需要使用此密码登录 Graylog Web 界面。你可以使用以下命令生成它:
echo -n "Enter Password: " && head -1你应该会看到以下输出:
Enter Password: yourpassword
e472e1436cbe87774c1bc75d0a646d67e506bea1dff8701fd41f34bca33e1419
现在,编辑 Graylog 主配置文件并定义两个密码:
nano /etc/graylog/server/server.conf粘贴你上面生成的两个密码,如下所示:
password_secret = Wv4VQWCAA9sRbL7pxPeY7tb9lSo50esEWgNXxXHypx0Og3CezMmQLdF2QzQdRSIXmNXKINjRvZpPTrvZv4k4NlJrFYTfOc3c
root_password_sha2 = e472e1436cbe87774c1bc75d0a646d67e506bea1dff8701fd41f34bca33e1419
接下来,你还需要按如下所示为你的服务器定义一个绑定地址:
http_bind_address = 127.0.0.1:9000
完成后保存并关闭文件,然后使用以下命令启动 Graylog 服务并使其在系统重启时自动启动:
systemctl daemon-reload
systemctl start graylog-server
systemctl enable graylog-server
接下来,你可以使用以下命令验证 Graylog 服务器的状态:
systemctl status graylog-server你应该会看到以下输出:
? graylog-server.service - Graylog server
     Loaded: loaded (/lib/systemd/system/graylog-server.service; disabled; vendor preset: enabled)
     Active: active (running) since Sun 2022-09-25 07:25:13 UTC; 10s ago
       Docs: http://docs.graylog.org/
   Main PID: 78082 (graylog-server)
      Tasks: 44 (limit: 4579)
     Memory: 539.4M
        CPU: 18.488s
     CGroup: /system.slice/graylog-server.service
             ??78082 /bin/sh /usr/share/graylog-server/bin/graylog-server
             ??78119 /usr/bin/java -Xms1g -Xmx1g -XX:NewRatio=1 -server -XX:+ResizeTLAB -XX:-OmitStackTraceInFastThrow -Djdk.tls.acknowledgeC>

Sep 25 07:25:13 ubuntu2204 systemd[1]: Started Graylog server.
Sep 25 07:25:13 ubuntu2204 graylog-server[78119]: OpenJDK 64-Bit Server VM warning: Option UseConcMarkSweepGC was deprecated in version 9.0 a>
Sep 25 07:25:14 ubuntu2204 graylog-server[78119]: WARNING: sun.reflect.Reflection.getCallerClass is not supported. This will impact performan>
Sep 25 07:25:17 ubuntu2204 graylog-server[78119]: WARNING: An illegal reflective access operation has occurred
Sep 25 07:25:17 ubuntu2204 graylog-server[78119]: WARNING: Illegal reflective access by retrofit2.Platform (file:/usr/share/graylog-server/gr>
Sep 25 07:25:17 ubuntu2204 graylog-server[78119]: WARNING: Please consider reporting this to the maintainers of retrofit2.Platform
Sep 25 07:25:17 ubuntu2204 graylog-server[78119]: WARNING: Use --illegal-access=warn to enable warnings of further illegal reflective access >
Sep 25 07:25:17 ubuntu2204 graylog-server[78119]: WARNING: All illegal access operations will be denied in a future release
你也可以使用该以下命令查看 Graylog 服务器的日志:
tail -f /var/log/graylog-server/server.logGraylog 服务器成功启动后,你应该会看到以下输出:
2022-09-25T07:25:40.117Z INFO  [ServerBootstrap] Services started, startup times in ms: {FailureHandlingService [RUNNING]=73, GeoIpDbFileChangeMonitorService [RUNNING]=88, PrometheusExporter [RUNNING]=88, OutputSetupService [RUNNING]=89, JobSchedulerService [RUNNING]=89, InputSetupService [RUNNING]=90, BufferSynchronizerService [RUNNING]=91, LocalKafkaMessageQueueReader [RUNNING]=92, LocalKafkaMessageQueueWriter [RUNNING]=92, GracefulShutdownService [RUNNING]=93, MongoDBProcessingStatusRecorderService [RUNNING]=93, UserSessionTerminationService [RUNNING]=101, StreamCacheService [RUNNING]=133, LocalKafkaJournal [RUNNING]=134, UrlWhitelistService [RUNNING]=134, ConfigurationEtagService [RUNNING]=137, EtagService [RUNNING]=139, PeriodicalsService [RUNNING]=174, LookupTableService [RUNNING]=203, JerseyService [RUNNING]=4076}
2022-09-25T07:25:40.133Z INFO  [ServerBootstrap] Graylog server up and running.
此时,Graylog 服务器已启动并在 9000 端口上监听。你可以使用以下命令进行检查:
ss -antpl | grep 9000你应该会看到以下输出:
LISTEN 0 4096 [::ffff:127.0.0.1]:9000 *:* users:(("java",pid=78119,fd=56))
将 Nginx 配置为 Graylog 的反向代理
接下来,你需要安装并配置 Nginx 作为反向代理,以便在 80 端口上访问 Graylog 服务器。
首先,使用以下命令安装 Nginx 服务器:
apt install nginx -y安装完 Nginx 服务器后,使用以下命令创建一个新的 Nginx 虚拟主机配置文件:
nano /etc/nginx/sites-available/graylog.conf添加以下行:
server {
    listen 80;
    server_name graylog.example.org;

location /
    {
      proxy_set_header Host $http_host;
      proxy_set_header X-Forwarded-Host $host;
      proxy_set_header X-Forwarded-Server $host;
      proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
      proxy_set_header X-Graylog-Server-URL http://$server_name/;
      proxy_pass       http://208.117.84.72:9000;
    }

}
完成后保存并关闭文件。然后,使用以下命令检查 Nginx 是否存在语法错误:
nginx -t你应该会看到以下输出:
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
接下来,使用以下命令启用 Nginx 虚拟主机配置文件:
ln -s /etc/nginx/sites-available/graylog.conf /etc/nginx/sites-enabled/接下来,删除 Nginx 默认的虚拟主机文件:
rm -rf /etc/nginx/sites-enabled/default最后,重启 Nginx 服务以使更改生效:
systemctl restart nginx接下来,使用以下命令验证 Graylog 的状态:
systemctl status nginx你应该会看到以下输出:
? nginx.service - A high performance web server and a reverse proxy server
     Loaded: loaded (/lib/systemd/system/nginx.service; enabled; vendor preset: enabled)
     Active: active (running) since Sun 2022-09-25 07:30:45 UTC; 8s ago
       Docs: man:nginx(8)
    Process: 78980 ExecStartPre=/usr/sbin/nginx -t -q -g daemon on; master_process on; (code=exited, status=0/SUCCESS)
    Process: 78981 ExecStart=/usr/sbin/nginx -g daemon on; master_process on; (code=exited, status=0/SUCCESS)
   Main PID: 78982 (nginx)
      Tasks: 3 (limit: 4579)
     Memory: 3.3M
        CPU: 49ms
     CGroup: /system.slice/nginx.service
             ??78982 "nginx: master process /usr/sbin/nginx -g daemon on; master_process on;"
             ??78983 "nginx: worker process" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" ""
             ??78984 "nginx: worker process" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" "" ""

Sep 25 07:30:45 ubuntu2204 systemd[1]: Starting A high performance web server and a reverse proxy server...
Sep 25 07:30:45 ubuntu2204 systemd[1]: Started A high performance web server and a reverse proxy server.
访问 Graylog Web 界面
现在,打开你的网页浏览器并输入 URL http://graylog.example.com。你将跳转到 Graylog 登录页面,如下所示:
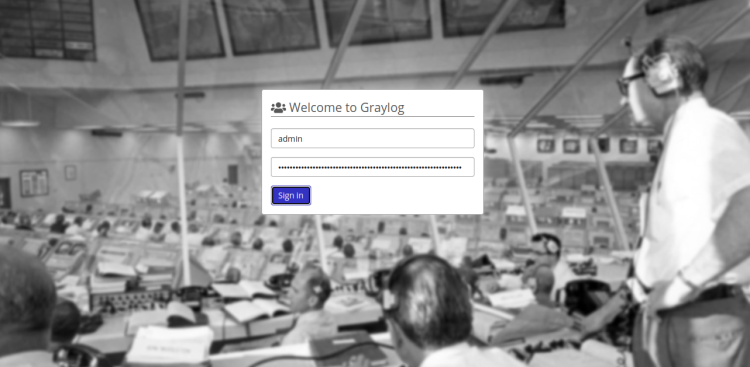
输入你的管理员用户名和密码,然后点击 Login 按钮。你应该在接下来的页面上看到 Graylog 仪表盘:
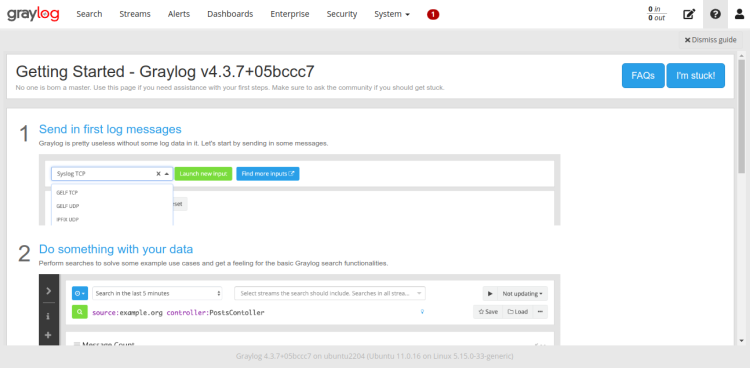
结语
恭喜!你已成功在 Ubuntu 22.04 上安装并配置了以 Nginx 作为反向代理的 Graylog 服务器。你现在可以探索 Graylog,并创建一个输入来接收来自外部来源的 Rsyslog 日志。如果你有任何疑问,请随时向我提问。