
本教程适用于以下 OS 版本
- Debian 11 (Bullseye)
- Debian 8 (Jessie)
- Debian 7 (Wheezy)
- Debian 6 (Squeeze)
- Debian 5 (Lenny)
- Debian 4 (Etch)
本页内容
- 前提条件
- 安装 Lighttpd
- 安装 PHP 和 PHP-FPM
- 为 PHP-FPM 配置 Lighttpd
- 创建 Lighttpd 虚拟主机
- 使用 Let's Encrypt 保护 Lighttpd
- 结论
Lighttpd 是一款简单、快速且安全的 Web 服务器。它体积非常小,不需要大量内存和 CPU 占用,这使其成为托管各类应用程序的最佳服务器之一。它专为关键任务环境而设计。它可以在单台服务器上并行处理多达 10,000 个连接。它提供了许多功能,包括 URL-Rewriting、Output-Compression、event mechanism、FastCGI、SCGI、Auth 等。
在本教程中,我们将向你展示如何在 Debian 11 上安装带有 PHP 和 Let's Encrypt SSL 的 Lighttpd。
前提条件
- 一台运行 Debian 11 的服务器。
- 一个指向服务器 IP 的有效域名。
- 服务器上已配置 root 密码。
安装 Lighttpd
默认情况下,Lighttpd 软件包包含在 Debian 11 官方仓库中。你可以通过运行以下命令来安装它:
apt-get install lighttpd -y安装 Lighttpd 后,启动 Lighttpd 服务并设置其在系统重启时自动启动:
systemctl start lighttpd
systemctl enable lighttpd
你也可以使用以下命令检查 Lighttpd 的状态:
systemctl status lighttpd你将看到以下输出:
? lighttpd.service - Lighttpd Daemon
     Loaded: loaded (/lib/systemd/system/lighttpd.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2022-02-12 07:01:06 UTC; 12s ago
    Process: 4663 ExecStartPre=/usr/sbin/lighttpd -tt -f /etc/lighttpd/lighttpd.conf (code=exited, status=0/SUCCESS)
   Main PID: 4668 (lighttpd)
      Tasks: 1 (limit: 2341)
     Memory: 932.0K
        CPU: 226ms
     CGroup: /system.slice/lighttpd.service
             ??4668 /usr/sbin/lighttpd -D -f /etc/lighttpd/lighttpd.conf

Feb 12 07:01:06 debian11 systemd[1]: Starting Lighttpd Daemon...
Feb 12 07:01:06 debian11 systemd[1]: Started Lighttpd Daemon.
现在,打开你的 Web 浏览器,使用 URL http://your-server-ip 访问 Lighttpd 网页。你将在下面的屏幕上看到 Lighttpd 测试页面:
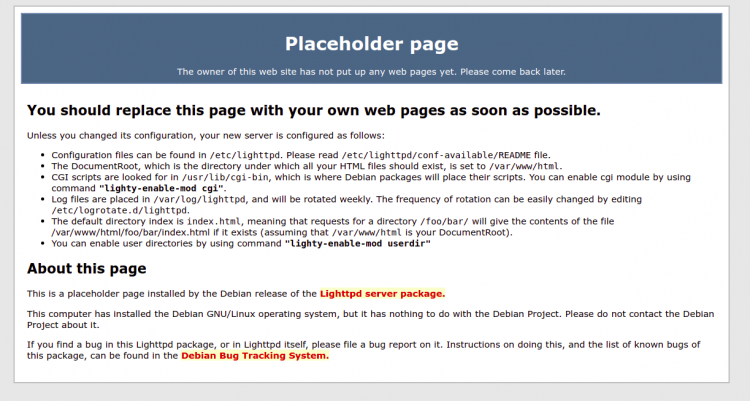
完成后,你可以继续下一步。
安装 PHP 和 PHP-FPM
接下来,运行以下命令将 PHP 和 PHP-FPM 软件包安装到你的系统中。
apt-get install php php-cgi php-fpm php-mysql -y安装完成后,编辑 php.ini 文件并将 cgi.fix_pathinfo 设置为 1
nano /etc/php/7.4/fpm/php.ini修改以下行:
cgi.fix_pathinfo=1
完成后保存并关闭文件。
为了让 Lighttpd 与 PHP-FPM 协同工作,你需要替换默认的 PHP-CGI 配置和 PHP-FPM socket:
首先,编辑 PHP-FPM 配置文件:
nano /etc/php/7.4/fpm/pool.d/www.conf找到以下行:
listen = /run/php/php7.4-fpm.sock
并将其替换为以下行:
listen = 127.0.0.1:9000
保存并关闭文件,然后重启 PHP-FPM 以应用更改:
systemctl restart php7.4-fpm你也可以使用以下命令检查 PHP-FPM 的状态:
systemctl status php7.4-fpm你将看到以下输出:
? php7.4-fpm.service - The PHP 7.4 FastCGI Process Manager
     Loaded: loaded (/lib/systemd/system/php7.4-fpm.service; enabled; vendor preset: enabled)
     Active: active (running) since Sat 2022-02-12 07:04:35 UTC; 1min 7s ago
       Docs: man:php-fpm7.4(8)
    Process: 15141 ExecStartPost=/usr/lib/php/php-fpm-socket-helper install /run/php/php-fpm.sock /etc/php/7.4/fpm/pool.d/www.conf 74 (code=e>
   Main PID: 15138 (php-fpm7.4)
     Status: "Processes active: 0, idle: 2, Requests: 0, slow: 0, Traffic: 0req/sec"
      Tasks: 3 (limit: 2341)
     Memory: 8.8M
        CPU: 54ms
     CGroup: /system.slice/php7.4-fpm.service
             ??15138 php-fpm: master process (/etc/php/7.4/fpm/php-fpm.conf)
             ??15139 php-fpm: pool www
             ??15140 php-fpm: pool www

Feb 12 07:04:35 debian11 systemd[1]: Starting The PHP 7.4 FastCGI Process Manager...
Feb 12 07:04:35 debian11 systemd[1]: Started The PHP 7.4 FastCGI Process Manager.
完成后,你可以继续下一步。
为 PHP-FPM 配置 Lighttpd
接下来,你需要编辑 Lighttpd 配置文件并使用 Fast CGI 对其进行修改:
nano /etc/lighttpd/conf-available/15-fastcgi-php.conf找到以下行:
"bin-path" => "/usr/bin/php-cgi",
"socket" => "/var/run/lighttpd/php.socket",
并将它们替换为以下行:
"host" => "127.0.0.1",
"port" => "9000",
保存并关闭文件,然后使用以下命令启用 Fast CGI 模块:
lighty-enable-mod fastcgi
lighty-enable-mod fastcgi-php
最后,重启 Lighttpd 服务以应用更改:
systemctl restart lighttpd创建 Lighttpd 虚拟主机
Lighttpd 还允许你使用虚拟主机托管多个网站。让我们创建一个新的虚拟主机配置文件,用于托管一个名为 test.example.com 的网站。
nano /etc/lighttpd/conf-available/test.conf添加以下行:
$HTTP["host"] == "test.example.com" {
    server.document-root = "/var/www/html/"
    server.errorlog      = "/var/log/lighttpd/example.com-error.log"
}
保存并关闭文件,然后使用以下命令激活虚拟主机:
ln -s /etc/lighttpd/conf-available/test.conf /etc/lighttpd/conf-enabled/接下来,创建一个 index.php 文件:
nano /var/www/html/index.php添加以下行:
<?php
phpinfo();
?>
保存并关闭文件,然后使用以下命令设置适当的权限和所有权:
chown -R www-data:www-data /var/www/html/
chmod -R 755 /var/www/html
接下来,重启 Lighttpd 服务以应用更改:
systemctl restart lighttpd现在,打开你的 Web 浏览器,使用 URL http://test.example.com 验证你的网站。你将在下面的屏幕上看到 PHP 测试页面:
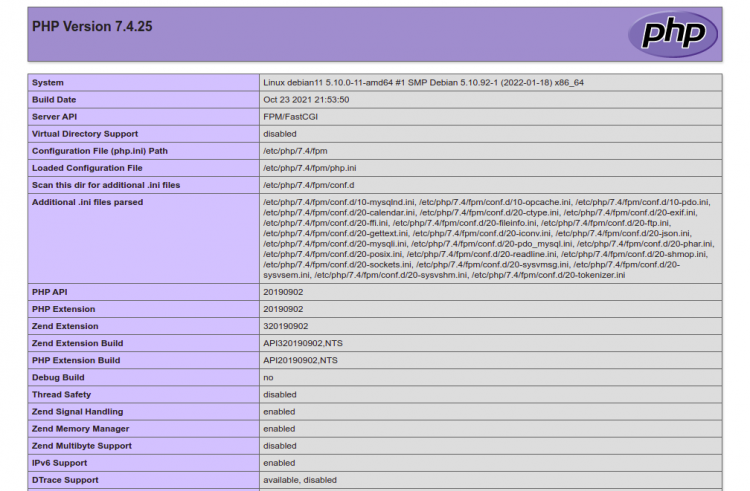
使用 Let's Encrypt 保护 Lighttpd
Lighttpd 还允许你使用 Let's Encrypt SSL 保护网站。为此,首先使用以下命令安装 Certbot 客户端:
apt-get install certbot -y接下来,运行以下命令为你的网站下载 Let's Encrypt SSL:
certbot certonly --webroot -w /var/www/html/ -d test.example.com系统将要求你提供电子邮件地址并接受许可条款,如下所示:
Saving debug log to /var/log/letsencrypt/letsencrypt.log
Plugins selected: Authenticator webroot, Installer None
Enter email address (used for urgent renewal and security notices) (Enter 'c' to
cancel):
[email protected]


- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please read the Terms of Service at
https://letsencrypt.org/documents/LE-SA-v1.2-November-15-2017.pdf. You must
agree in order to register with the ACME server at
https://acme-v02.api.letsencrypt.org/directory
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(A)gree/(C)ancel: A

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Would you be willing to share your email address with the Electronic Frontier
Foundation, a founding partner of the Let's Encrypt project and the non-profit
organization that develops Certbot? We'd like to send you email about our work
encrypting the web, EFF news, campaigns, and ways to support digital freedom.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
(Y)es/(N)o: Y
Once the certificates are downloaded successfully, you should see the following output:

IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/test.example.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/test.example.com/privkey.pem
   Your cert will expire on 2022-05-11. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot
   again. To non-interactively renew *all* of your certificates, run
   "certbot renew"
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le
接下来,你需要将证书和私钥合并到一个文件中。你可以使用以下命令完成:
cat /etc/letsencrypt/live/test.example.com/cert.pem /etc/letsencrypt/live/test.example.com/privkey.pem > /etc/letsencrypt/live/test.example.com/web.pem接下来,你需要编辑 Lighttpd 虚拟主机文件并定义 Let's Encrypt SSL 证书路径。
你可以使用以下命令完成:
nano /etc/lighttpd/conf-enabled/test.conf按如下所示修改文件:
$HTTP["host"] == "test.example.com" {
    server.document-root = "/var/www/html/"
}

$SERVER["socket"] == ":443" {
ssl.engine = "enable"
ssl.pemfile = "/etc/letsencrypt/live/test.example.com/web.pem"
ssl.ca-file = "/etc/letsencrypt/live/test.example.com/chain.pem"
server.name = "test.example.com"
server.document-root = "/var/www/html/"
server.errorlog = "/var/log/lighttpd/example.com_error.log"
accesslog.filename = "/var/log/lighttpd/example.com_access.log"
}

$HTTP["scheme"] == "http" {
$HTTP["host"] == "test.example.com" {
url.redirect = ("/.*" => "https://test.example.com$0")
}
}
保存并关闭文件。然后重启 Lighttpd 服务以应用配置更改:
systemctl restart lighttpd你现在可以使用 URL https://test.example.com 安全地访问你的网站。
结论
恭喜!你已成功在 Debian 11 上安装了带有 PHP 和 Let's Encrypt SSL 的 Lighttpd。你现在可以开始使用 Lighttpd Web 服务器部署你的网站。如有任何问题,欢迎随时向我提问。